
CVE-2026-1357
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
educationexploitationpenetration-testing+3
sahmsec/cve-2026-1357Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
 atiilla/cve-2026-27876
Grafana SQL Expressions Arbitrary File Write to RCE
 kentox493/cve-2026-46300_fragnesia
Linux kernel local privilege escalation exploit with automated prerequisite audit for CVE-2026-46300, validating patch status, XFRM ESP-in-TCP…
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 adityabhatt3010/cve-2025-53770-sharepoint-zero-day-variant-exploited-for-full-rce
A critical zero-auth RCE vulnerability in SharePoint (CVE-2025-53770), now exploited in the wild, building directly on the spoofing flaw…
 jakabakos/cve-2024-27348-apache-hugegraph-rce
Python exploit and detection script for CVE-2024-27348, a remote code execution vulnerability in Apache HugeGraph Server via the Gremlin traversal…
 surajraghuvanshi/paloaltorcedetectionandexploit
Detecion for the vulnerability CVE-2017-15944
 h4rk3nz0/exploits
A selection of rebuilt and from scratch exploits, scripts and ideas that can be used in red-teaming scenarios.
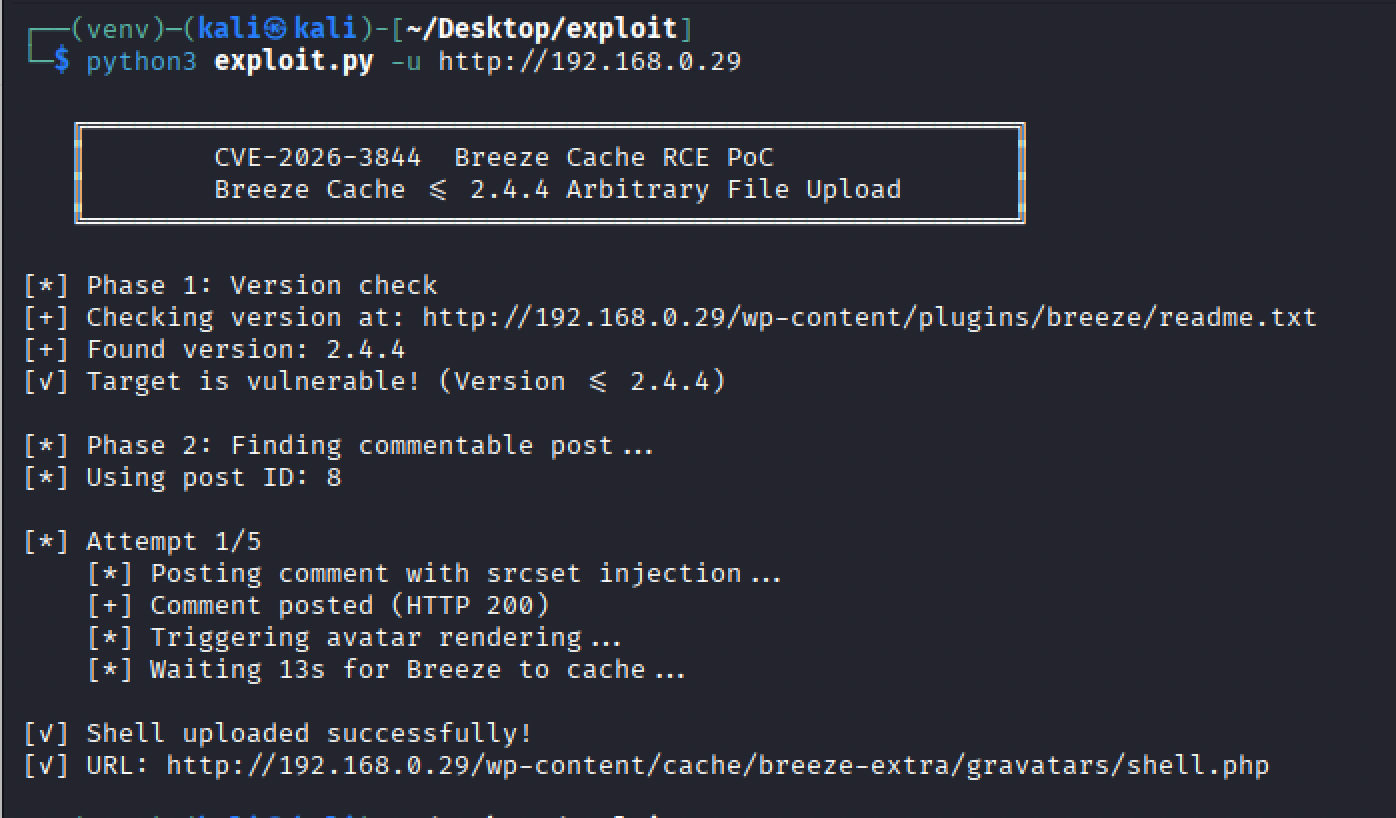 halilkirazkaya/cve-2026-3844
Exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to RCE in Breeze Cache WordPress plugin. Includes lab setup, usage, and…
 magicpipersec/wps-cve-2022-24934
PoC exploit server for CVE-2022-24934 that delivers a malicious payload via a fake WPS Update Server, targeting the wpsupdate.exe process for…
 boredchilada/clickfix-simulator-2025
A lightweight, self-hosted simulation tool for "ClickFix" (ClearFake) social engineering training. Safely simulates clipboard-injection attacks with…
 attarwahyup/netscaler-cve-2026-8451
Exploit code for CVE-2026-8451 targeting Citrix Netscaler, providing proof-of-concept for the vulnerability.
 s-vx/cve-2026-47668
PoC exploit for unauthenticated remote code execution in DBGate via the /runners/start endpoint, with blind RCE mode and container-based testing…
 revoltsecurities/cve-2024-4358
An Vulnerability detection and Exploitation tool for CVE-2024-4358
 haidv35/cve-2021-21972
Exploit for CVE-2021-21972 targeting VMware vCenter Server, enabling remote code execution via the vSphere Client.
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…