
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
101 results
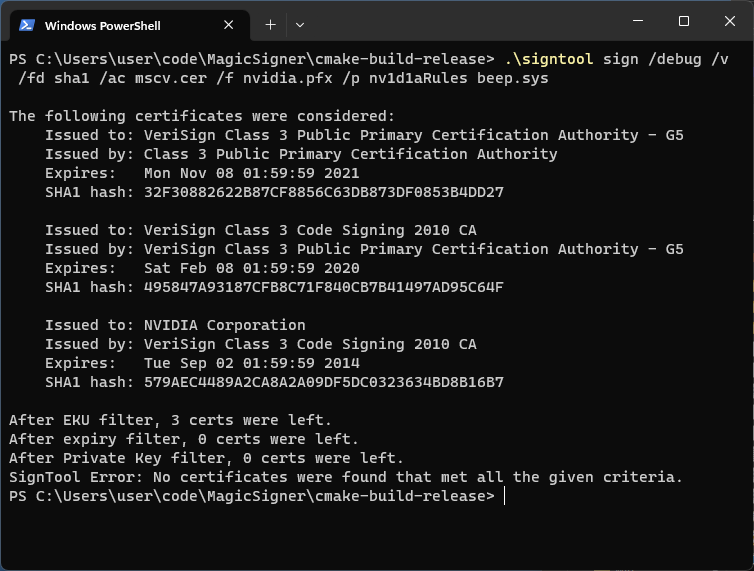
MagicSigner preview

MagicSigner

GitHubnamazso/magicsigner

Signtool for expired certificates

adversarial-attackauthentication-authorizationdefensive-tools+2
5243 years ago
CVE-2021-1675-LPE-EXP preview

CVE-2021-1675-LPE-EXP

GitHubevilashz/cve-2021-1675-lpe-exp

PrintNightmare , Local Privilege Escalation of CVE-2021-1675 or CVE-2021-34527
binary-exploitationexploitationprivilege-escalation+2
565 years ago
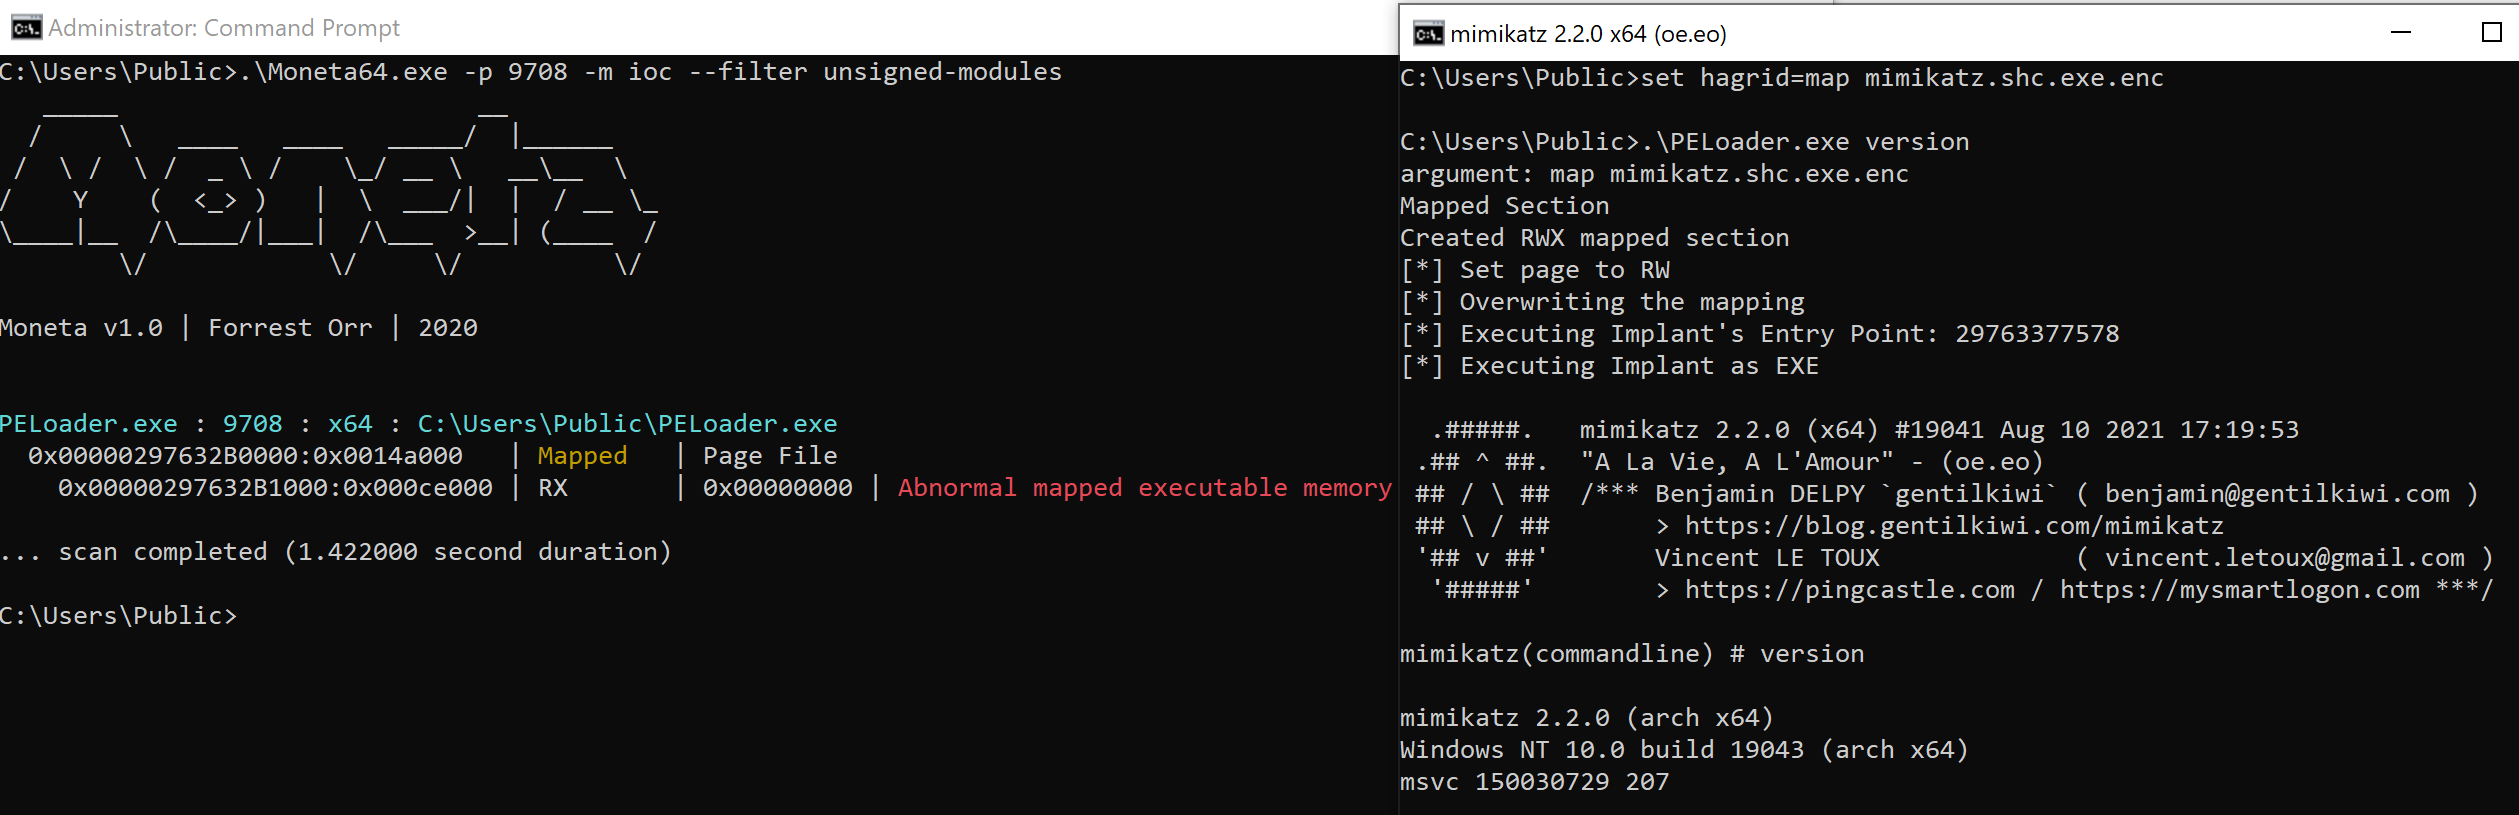
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques

binary-analysisexploitationmalware-analysis+4
4554 years ago
LdrLockLiberator preview

LdrLockLiberator

GitHubelliotkillick/ldrlockliberator

For when DLLMain is the only way
exploitationpayload-developmentpersistence-mechanisms+2
4352 years ago
C2-Tool-Collection preview

C2-Tool-Collection

GitHuboutflanknl/c2-tool-collection

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

command-and-controlexploit-frameworksinformation-gathering+8
1.4k3 years ago
Cooolis-ms preview

Cooolis-ms

GitHubrvn0xsy/cooolis-ms

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…

command-and-controlexploit-frameworksids-ips-evasion+7
9282 years ago
DLLPasswordFilterImplant preview

DLLPasswordFilterImplant

GitHubgosecure/dllpasswordfilterimplant

DLL Password Filter Implant with Exfiltration Capabilities
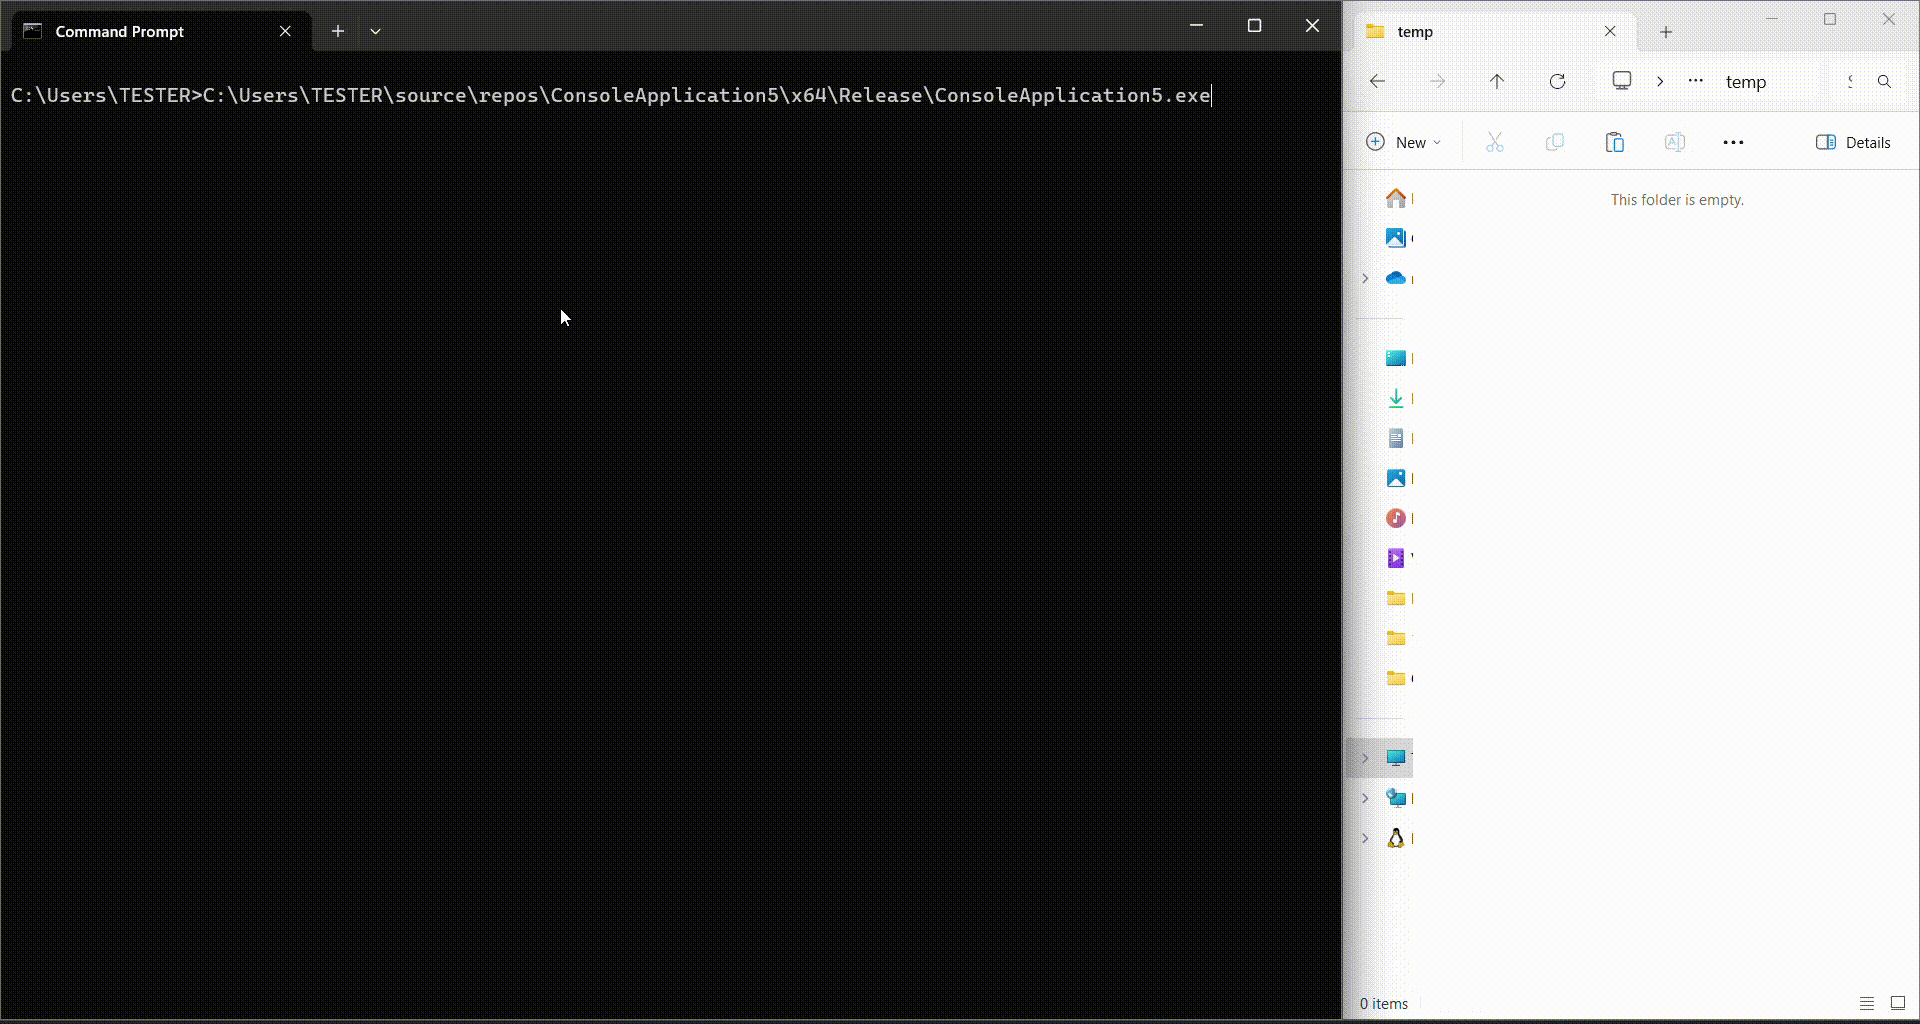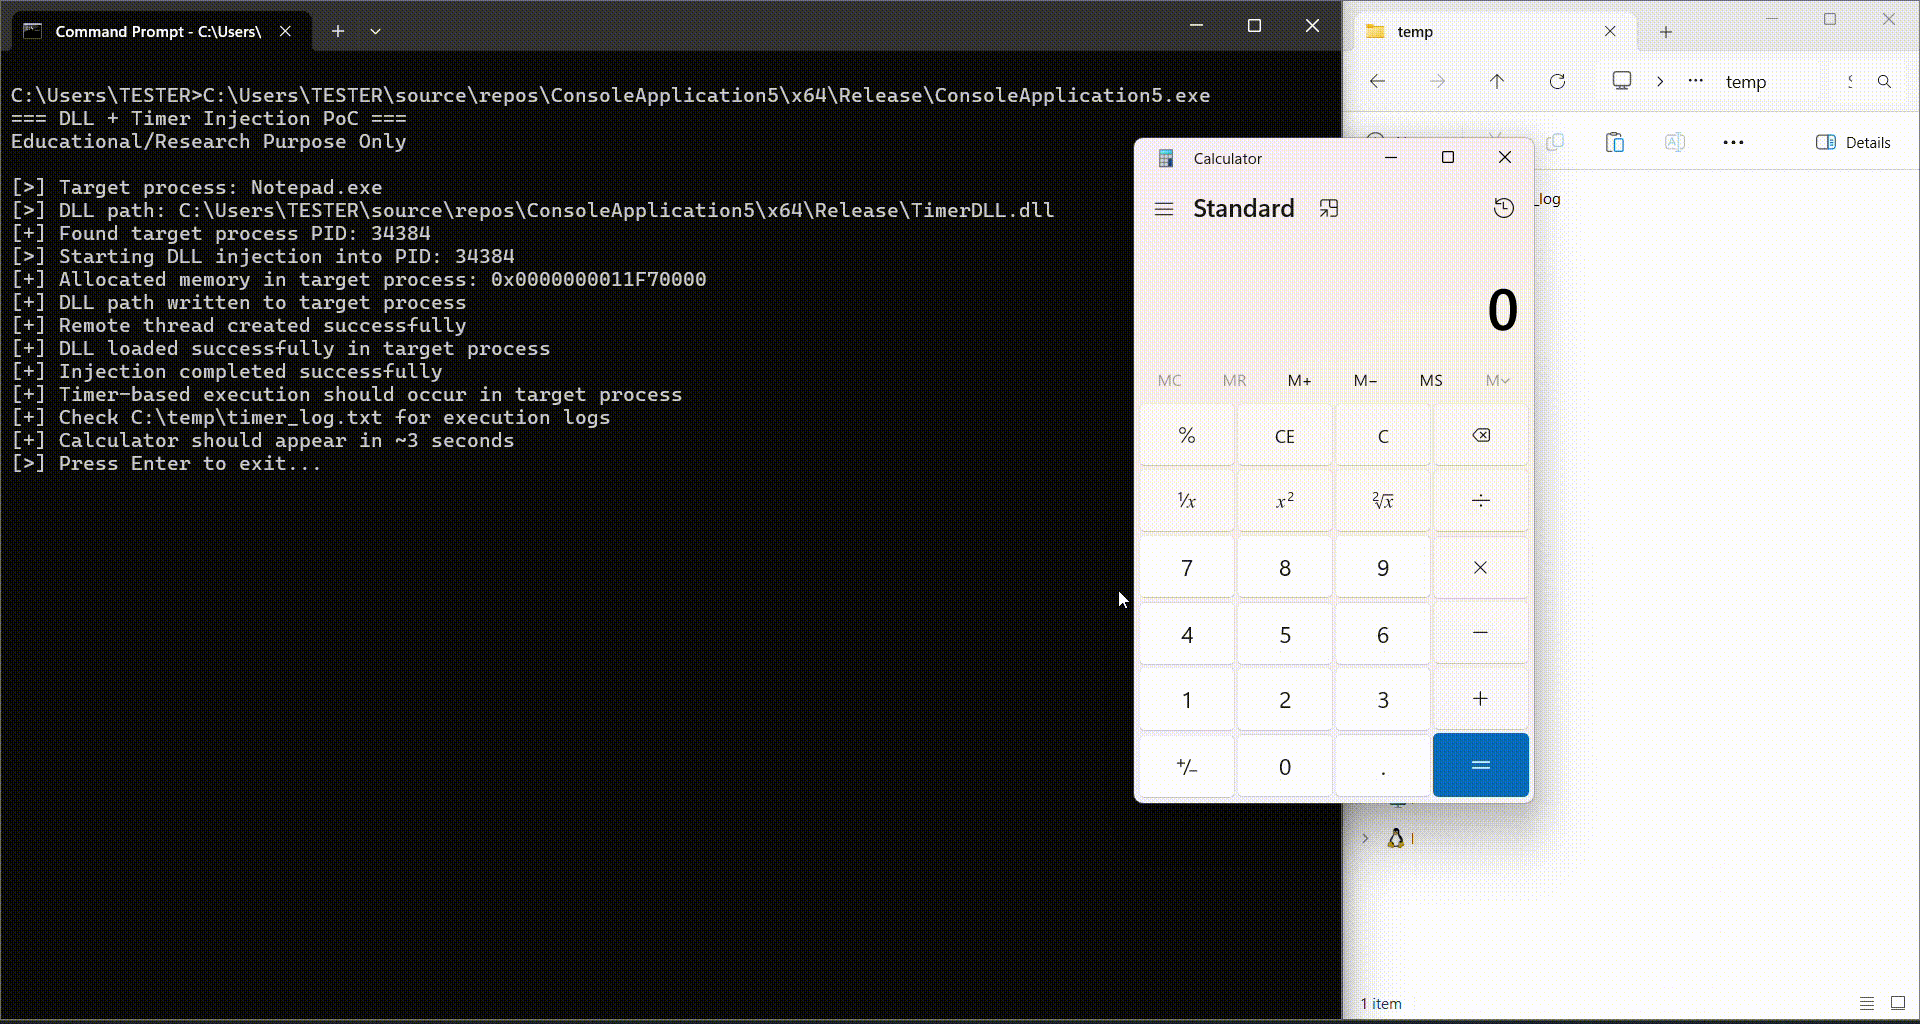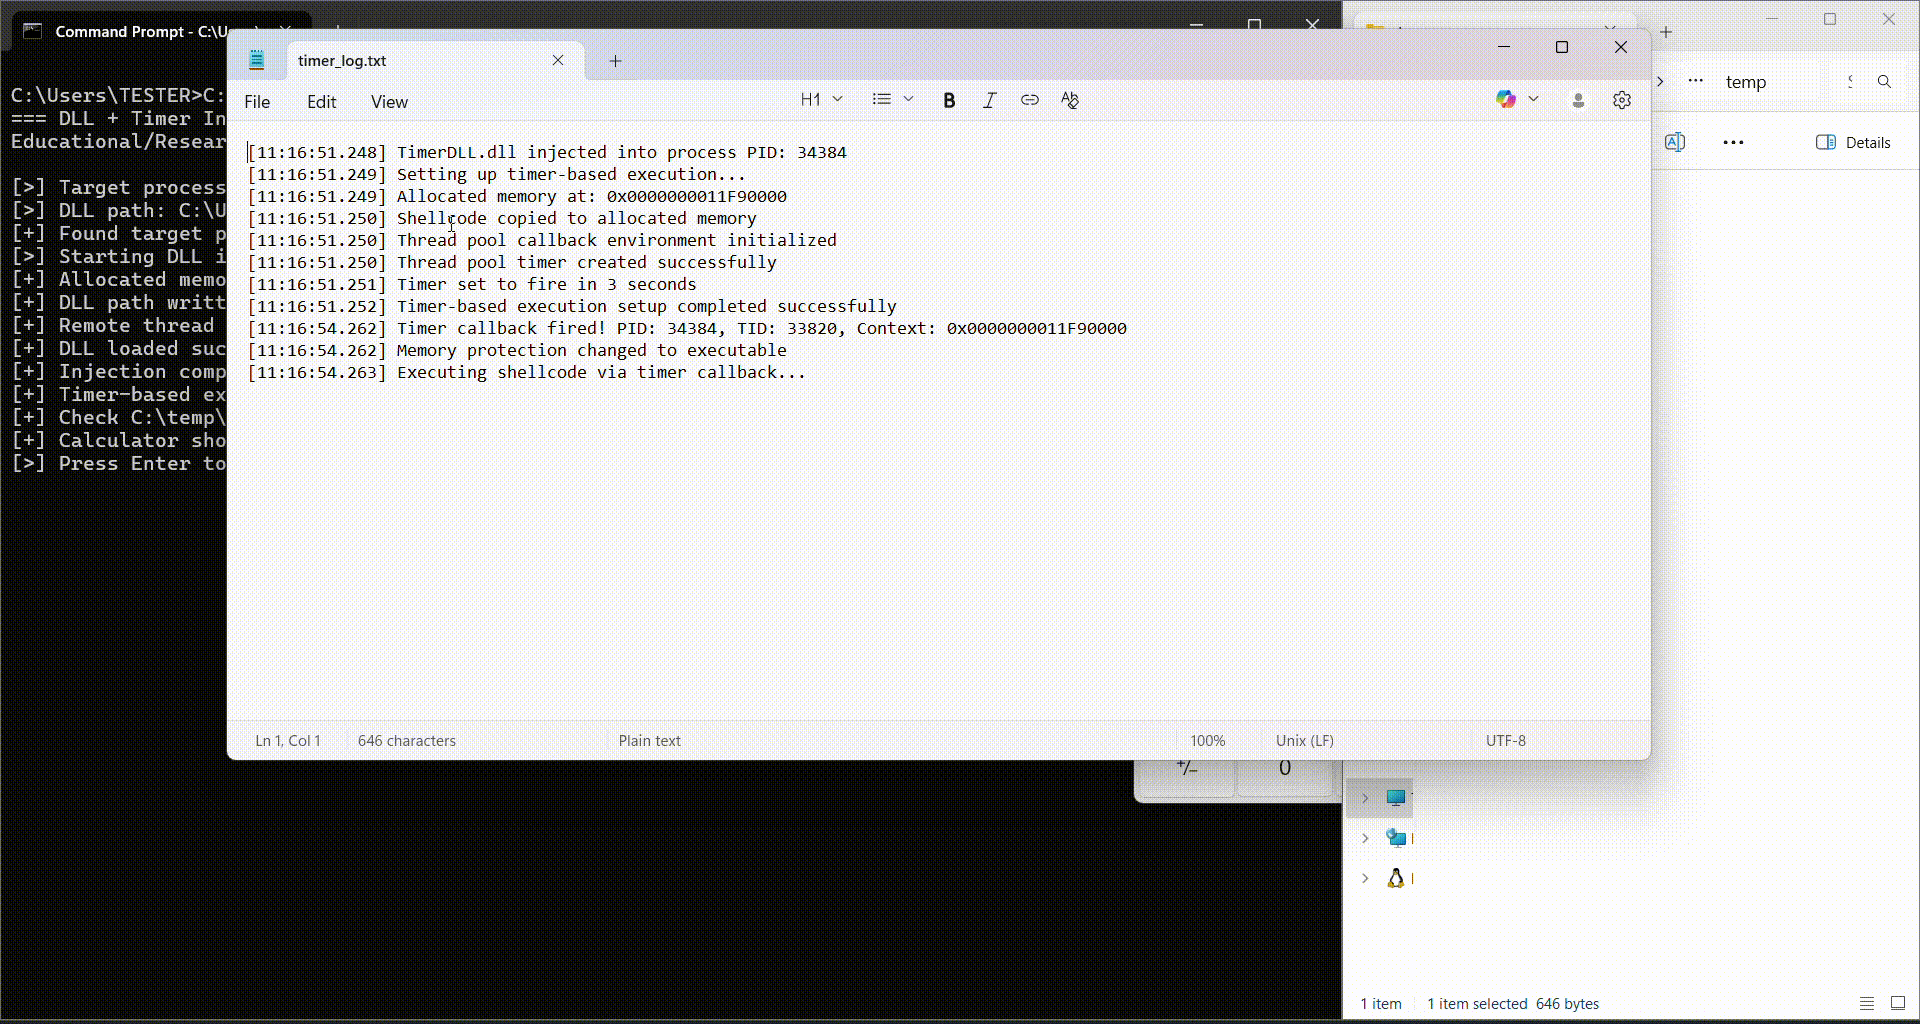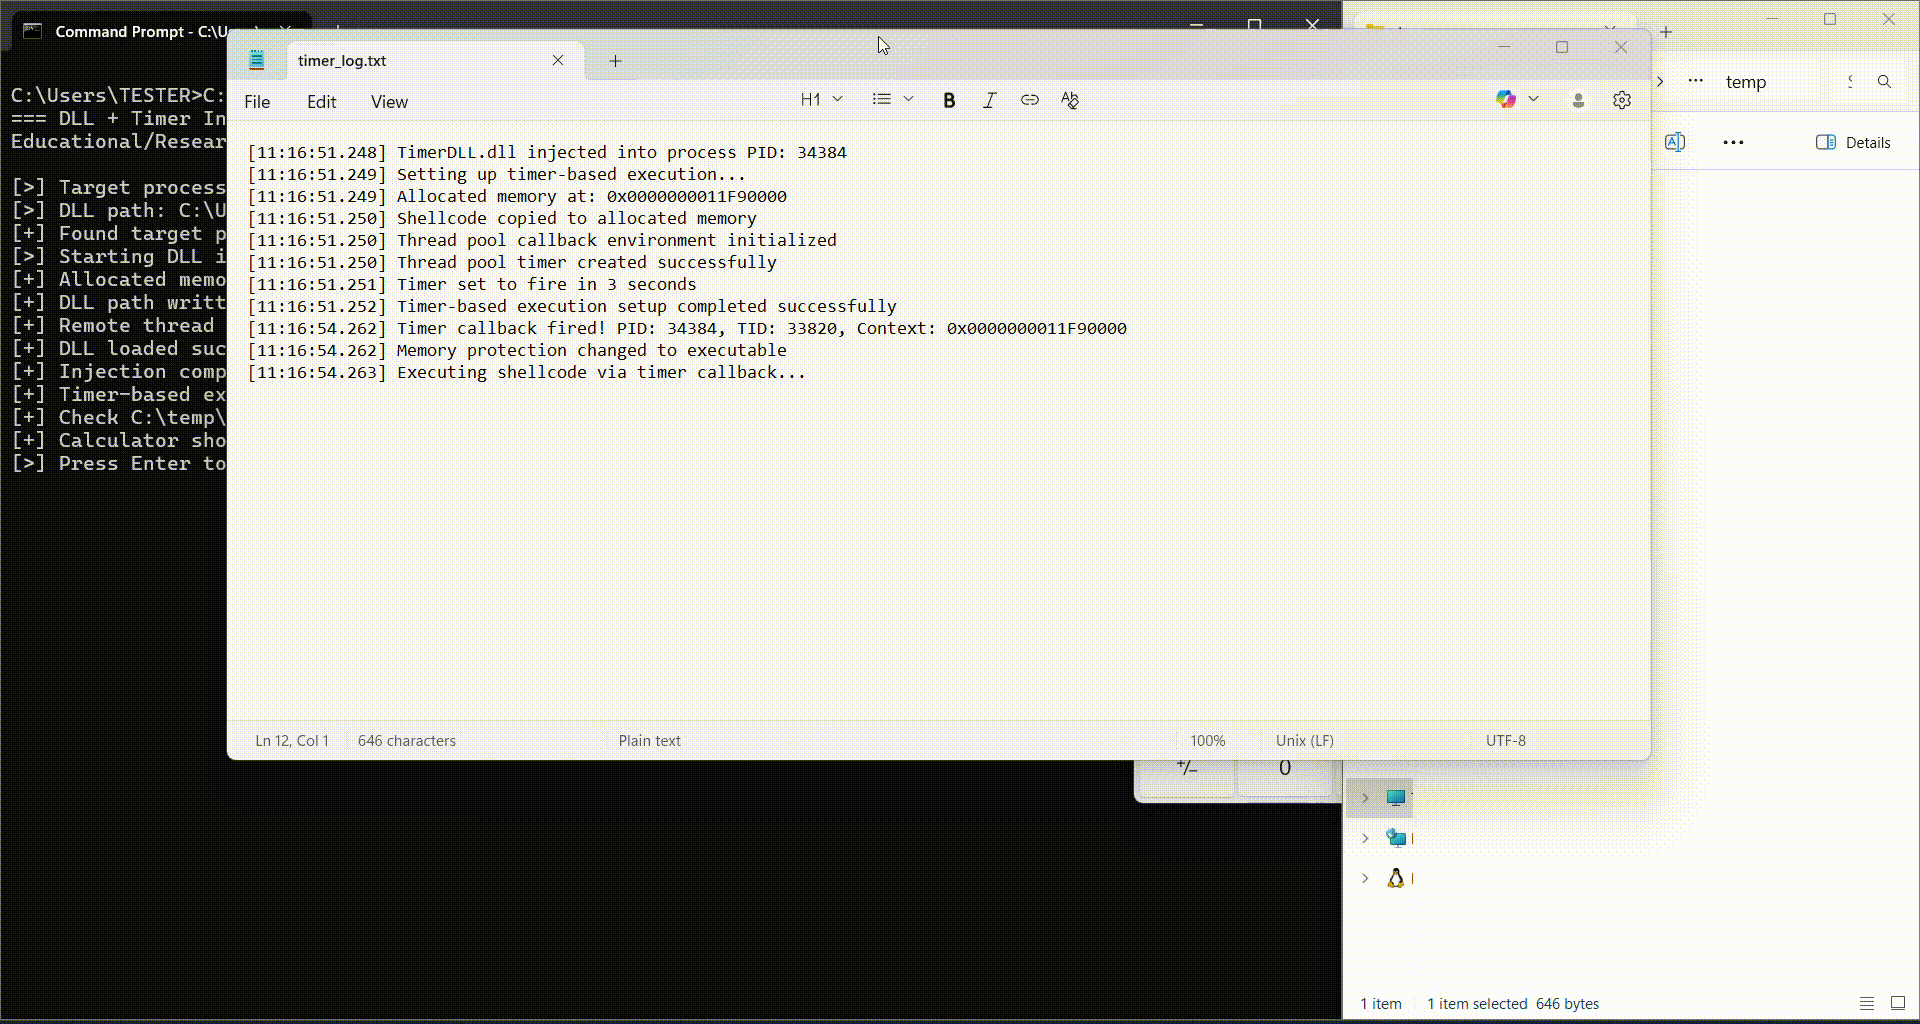
data-exfiltrationpenetration-testingpersistence-mechanisms+2
1366 years ago
Remote-DLL-Injection-with-Timer-based-Shellcode-Execution preview

Remote-DLL-Injection-with-Timer-based-Shellcode-Execution

GitHubandreisss/remote-dll-injection-with-timer-based-shellcode-execution

Remote DLL Injection with Timer-based Shellcode Execution
educationexploitationpayload-development+3
2161 year ago
OneDriveUpdaterSideloading preview

OneDriveUpdaterSideloading

GitHubchoisg/onedriveupdatersideloading

Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

adversarial-attackpayload-developmentred-teaming+1
1014 years ago
freeMetsrvLoader preview

freeMetsrvLoader

GitHubattl4s/freemetsrvloader

freeBokuLoader fork which targets and frees Metsrv's initial reflective DLL package

command-and-controlpayload-developmentpost-exploitation+1
353 years ago
TrollDump preview

TrollDump

GitHubcybersectroll/trolldump

Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…

payload-developmentpost-exploitationprivilege-escalation+1
842 years ago
Previous123456Next