

stratus-red-team
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
adversarial-attackcloud-infrastructure-securitycloud-security+5
2.4k
datadog/stratus-red-team:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 convisolabs/cve-2024-43044-jenkins
Exploit for the vulnerability CVE-2024-43044 in Jenkins
 crystallen1/cve-2025-27636-demo
Demonstrates Apache Camel CVE-2025-27636 with Docker-based reproduction of header injection attacks, including bean method injection and command…
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
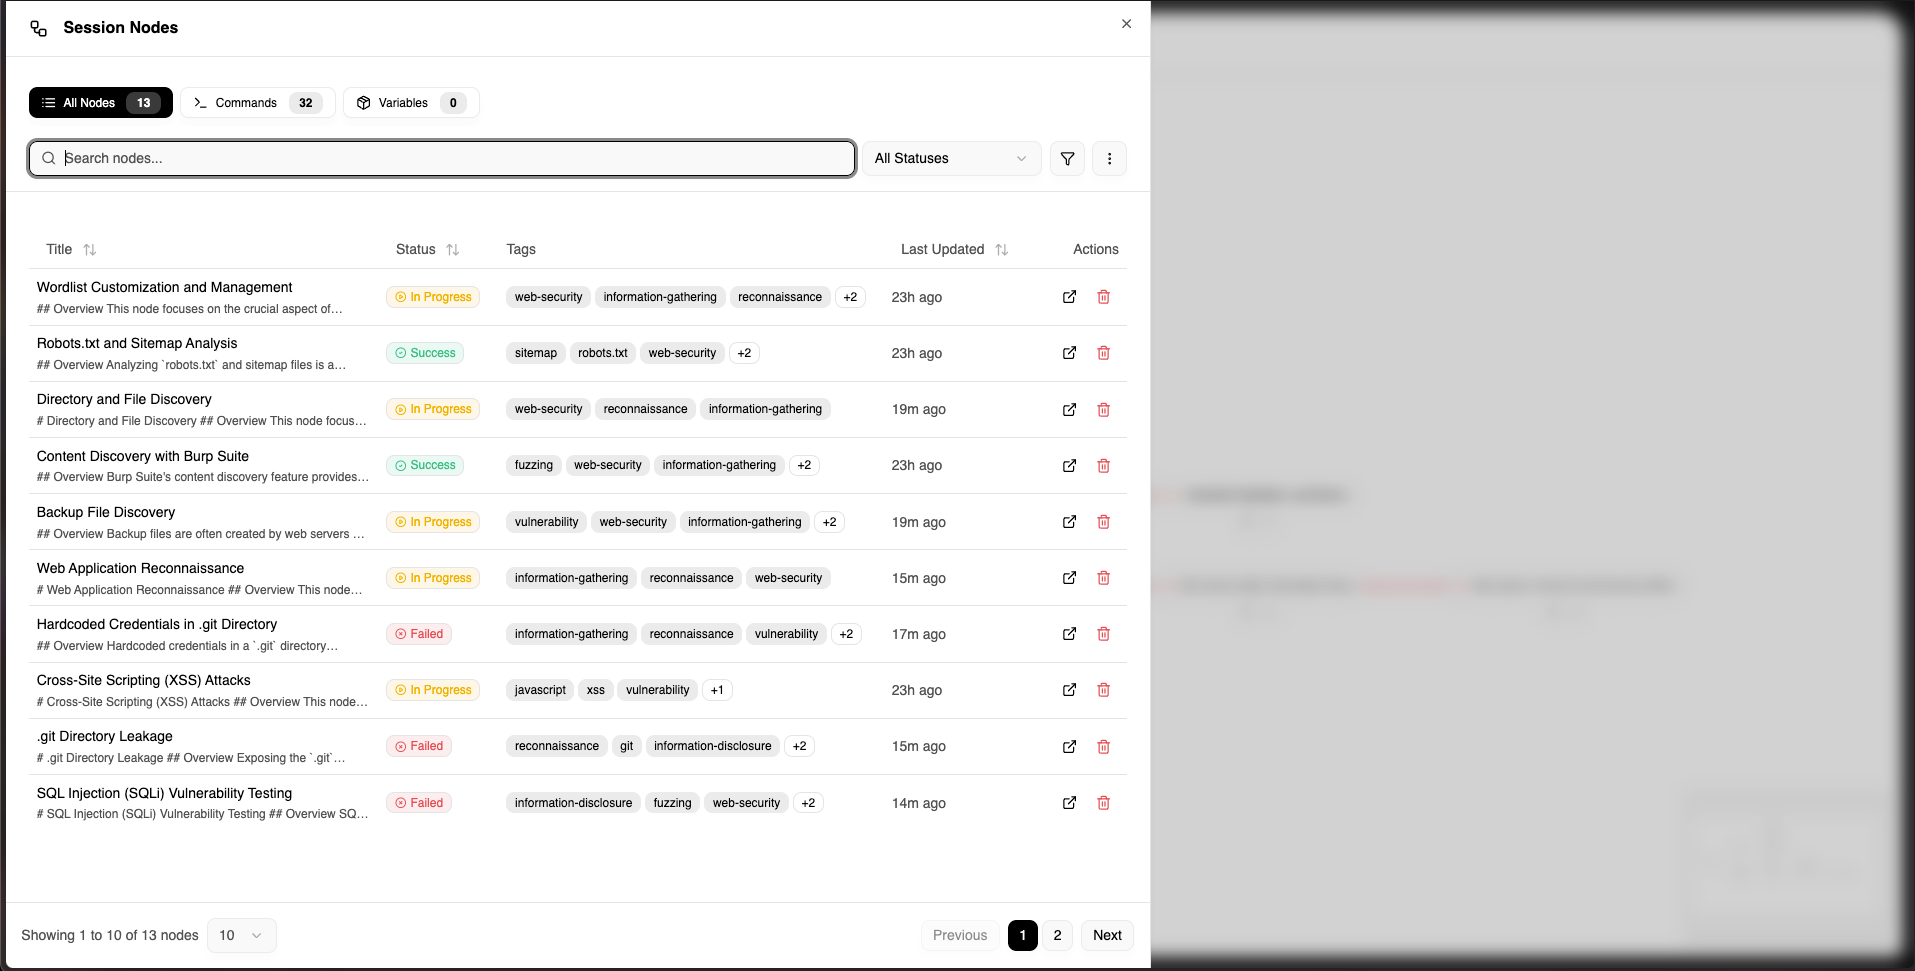 rb-x/pwnflow
A visual methodology tracking platform tailored for offensive security assessments
 joaovicdev/exploit-cve-2026-9198
Proof-of-concept exploit for CVE-2026-9198, an unauthenticated RCE in IBM Langflow OSS, chaining auto_login and validate/code endpoints. Includes a…
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 learner202649/cve-2026-42271-poc
The code for personally reproducing the corresponding vulnerability
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 0xballpoint/load
Lord Of Active Directory - automatic vulnerable active directory on AWS
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 opsxcq/docker-tor-hiddenservice-nginx
Easily setup a hidden service inside the Tor network