
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
CVE-2024-51793 preview

CVE-2024-51793

GitHub0axz-tools/cve-2024-51793

Exploits CVE-2024-51793 unauthenticated arbitrary file upload in WordPress Computer Repair Shop plugin, scans target lists, uploads PHP webshells,…
exploitationpayload-developmentpenetration-testing+3
1 year ago
CVE-2025-49113 preview

CVE-2025-49113

GitHubleakforge/cve-2025-49113

Roundcube ≤ 1.6.10 Post-Auth RCE via PHP Object Deserialization
exploitationpayload-developmentpenetration-testing+3
1 year ago
CVE-2025-49113 preview

CVE-2025-49113

GitHubmooder1/cve-2025-49113

Roundcube Webmail post-auth RCE via PHP object deserialization (CVE-2025-49113)
exploitationpayload-developmentpenetration-testing+3
6 months ago
CVE-2023-26326_Buddyform_exploit preview

CVE-2023-26326_Buddyform_exploit

GitHubmesudmammad1/cve-2023-26326_buddyform_exploit

Python exploit for CVE-2023-26326 (WordPress BuddyForms) chained with CVE-2024-2961 to achieve unauthenticated remote code execution via php://filter…
exploitationpayload-developmentpenetration-testing+3
1 year ago
CVE-2019-9978-Social-Warfare-WordPress-Plugin-RCE preview

CVE-2019-9978-Social-Warfare-WordPress-Plugin-RCE

GitHubhousma/cve-2019-9978-social-warfare-wordpress-plugin-rce

The `swp_debug` parameter in `admin-post.php` allows remote attackers to include external files containing malicious PHP code, which are evaluated on…
educationexploitationpayload-generation+5
1 year ago
php-reverse-shell preview

php-reverse-shell

GitHubh3x0v3rl0rd/php-reverse-shell

PHP reverse shell script for establishing a remote TCP connection, enabling command execution on a target web server.
penetration-testingpost-exploitationred-teaming+2
5 years ago
PolyDrop preview

PolyDrop

GitHubmalwaresupportgroup/polydrop

A BYOSI (Bring-Your-Own-Script-Interpreter) Rapid Payload Deployment Toolkit
command-and-controldefensive-toolseducation+5
1262 years ago
Roundcube-CVE-2025-49113 preview

Roundcube-CVE-2025-49113

GitHubbiitts/roundcube-cve-2025-49113

Proof-of-concept to CVE-2025-49113
exploitationpayload-developmentpenetration-testing+3
61 year ago
CVE-2021-44967 preview

CVE-2021-44967

GitHubgodylockz/cve-2021-44967

Proof-of-concept exploit for CVE-2021-44967 enabling remote code execution in LimeSurvey 5.2.4 via malicious plugin upload, with reverse shell…
exploitationpayload-developmentpenetration-testing+3
11 month ago
CVE-2023-47400 preview

CVE-2023-47400

GitHublucasvanhaaren/cve-2023-47400

Proof of Concept for the CVE-2023-47400
exploitationpayload-developmentpenetration-testing+3
22 years ago
CVE-2026-15282 preview

CVE-2026-15282

GitHubshinthink/cve-2026-15282

Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
educationexploitationpayload-generation+5
3 months ago
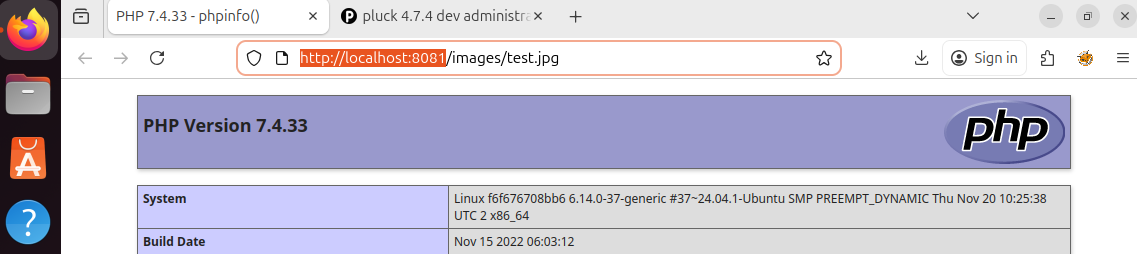
CVE-2018-11736 preview

CVE-2018-11736

GitHubpurgemebaby/cve-2018-11736

PoC exploit for CVE-2018-11736 affecting Pluck CMS versions prior to 4.7.7-dev2 with a File Upload Vulnerability
exploitationpayload-developmentpenetration-testing+3
17 months ago
CVE-2024-4577 preview

CVE-2024-4577

GitHubcharis3306/cve-2024-4577

Python-based exploit for CVE-2024-4577, a PHP-CGI remote code execution vulnerability on Windows platforms with Best-Fit character conversion bypass.
exploitationpenetration-testingred-teaming+2
2 years ago
DAws preview

DAws

GitHubdotcppfile/daws

Advanced Web Shell

ids-ips-evasionpayload-generationpenetration-testing+6
5789 years ago
Zero-Day-Legacy preview

Zero-Day-Legacy

GitHubayham-megdadi/zero-day-legacy

A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…

ctfeducationlabs-practice+6
23 months ago
Previous1234Next