
mongobleed-scanner
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
database-securityexploitationinformation-gathering+3
pedrocruz2202/mongobleed-scanner🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 charlesjson/cve-2023-20198
Python-based exploit tool for CVE-2023-20198 targeting Cisco IOS XE routers. Provides automated exploitation and post-exploitation capabilities for…
 wa6n3r/cve-2024-3400
Multi-threaded exploit tool for CVE-2024-3400 in Palo Alto PAN-OS with automated artifact download and detailed logging for confirmed RCE.
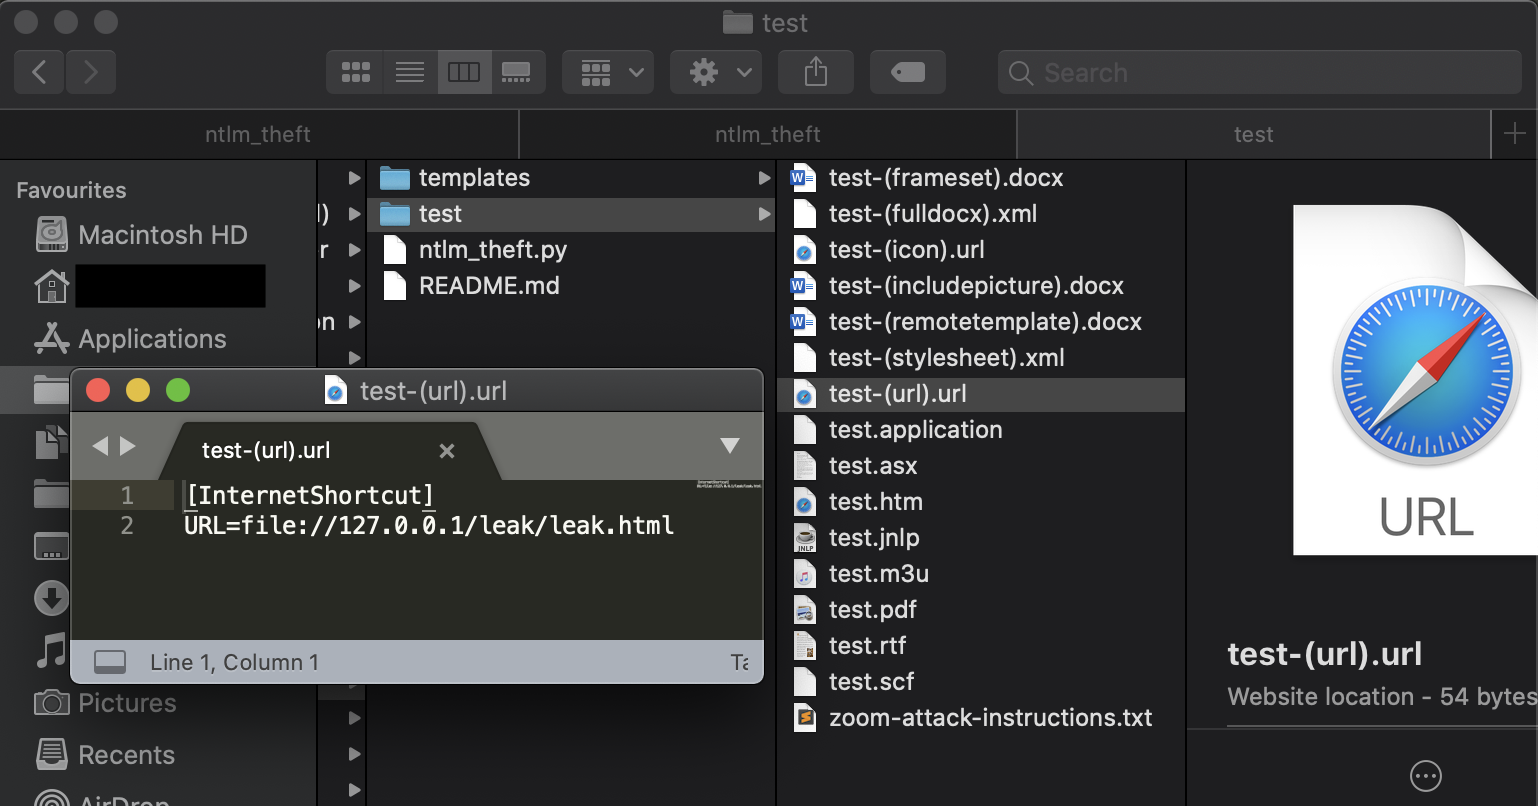 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
 voidsshadows/hikvision-city-hunter
This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…
 pinecone-wifi/pinecone
Modular WLAN auditing framework for red teams with deauthentication, rogue AP, and WPA handshake capture modules. Features a Metasploit-like CLI for…
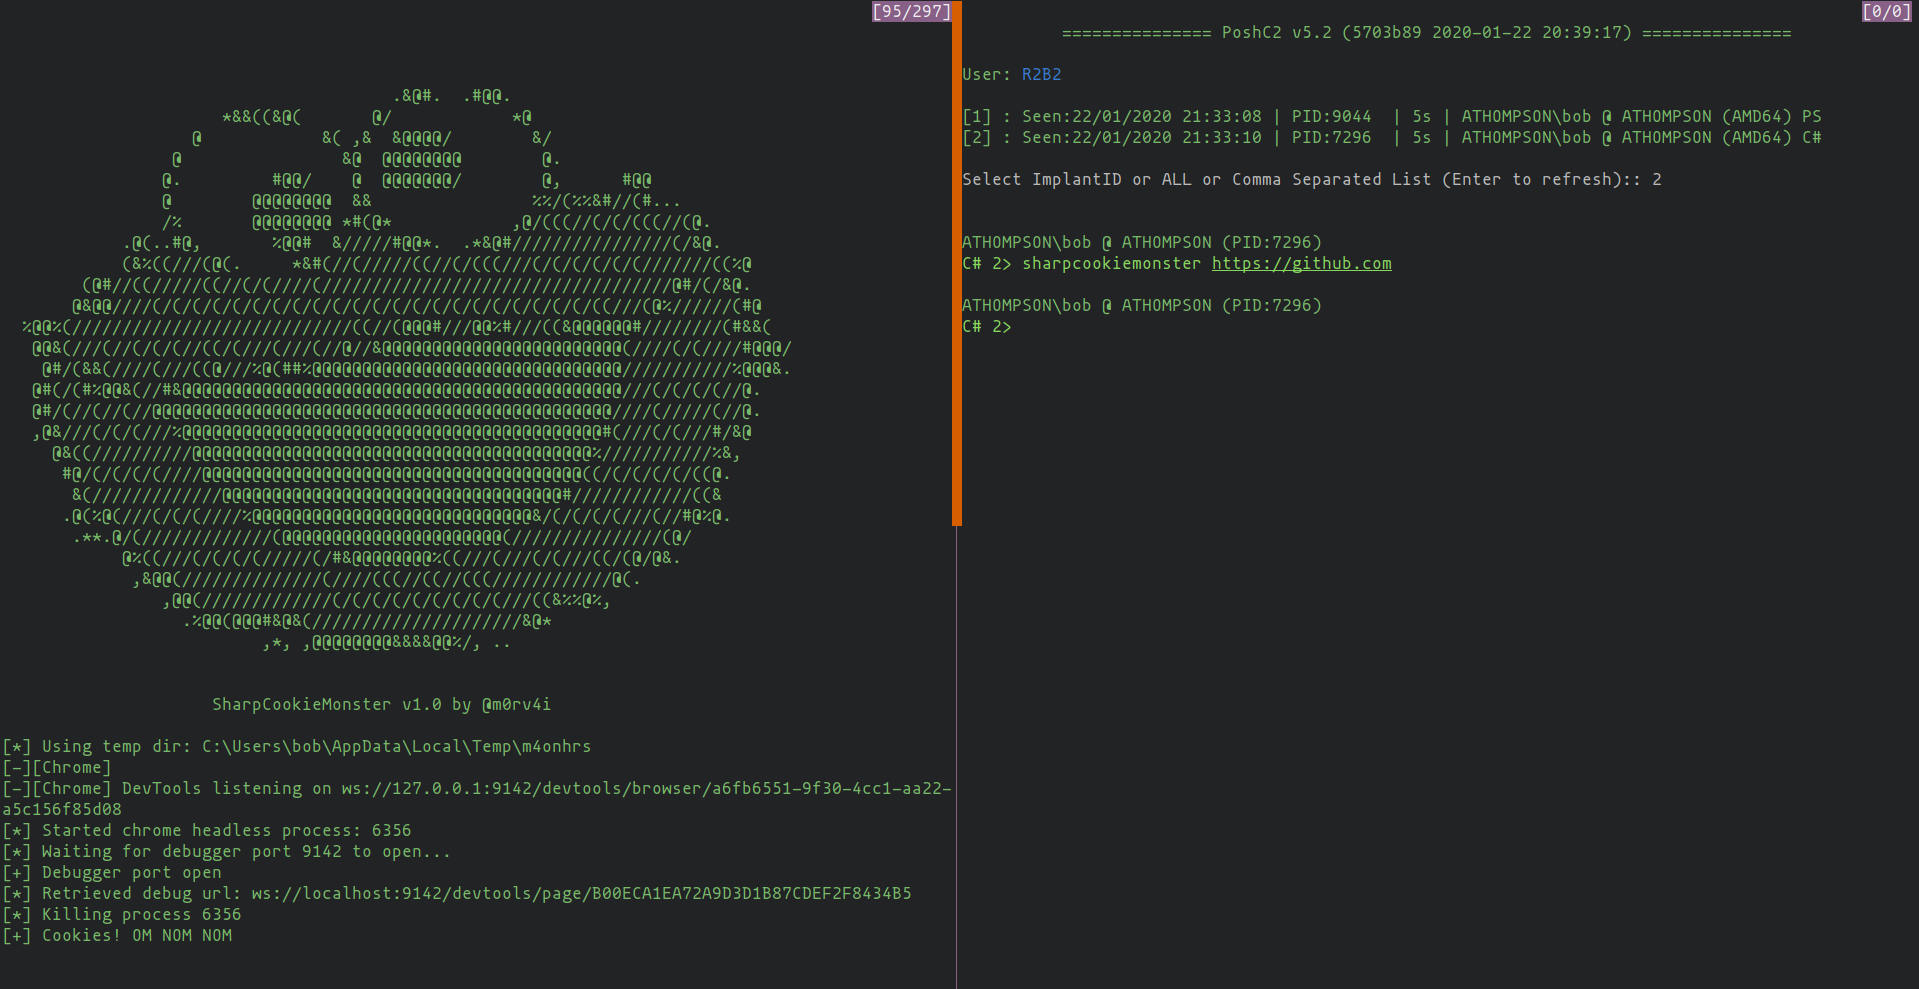 riskydissonance/sharpcookiemonster
C# tool to dump all cookies from Chrome/Edge browsers, including httpOnly and secure flags, for session hijacking and post-exploitation credential…
 stiffies/airscout
A nice tool that automates network hash capturing and has a nice GUI. Read README.md for more information and NEVER use this without explicit…
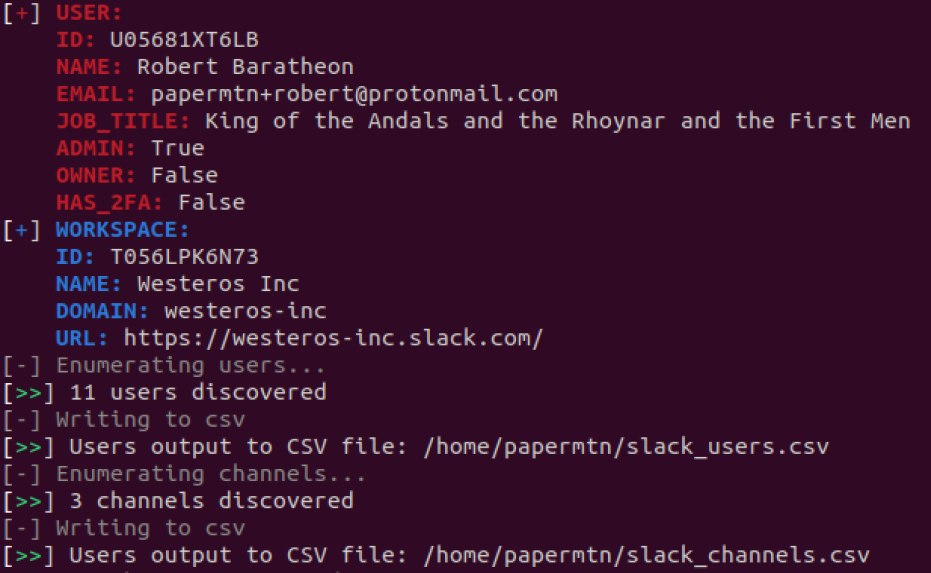 papermtn/slack-watchman
Slack enumeration and exposed secrets detection tool
 xmcyber/machound
Extends BloodHound to collect and ingest Active Directory relationships from macOS hosts, including logged-in users, admin groups, SSH/VNC/AppleEvent…
 darabium/couchdb-exploit
Exploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 pwndexter/sharpedrchecker
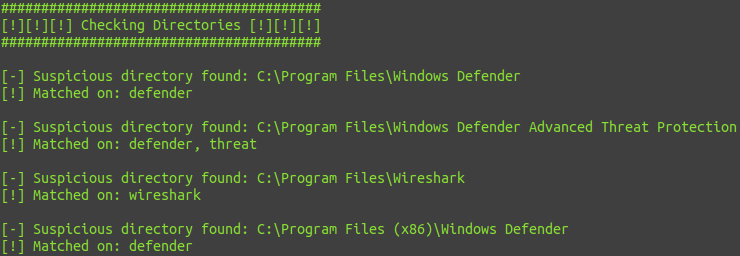
C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).