
CVE-2026-73570
 gabrielunknown/cve-2026-73570
Zimbra SNMP Notification OS Command Injection — Unauthenticated RCE via SMTP exploit (Poc)
exploitationpenetration-testingred-teaming+3
4
gabrielunknown/cve-2026-73570Zimbra SNMP Notification OS Command Injection — Unauthenticated RCE via SMTP exploit (Poc)
 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 exdev994/cve-2026-90817
Python PoC for CVE-2026-90817, an unauthenticated REDCap RCE via survey passthrough routing and file-path injection, with a Docker lab and…
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
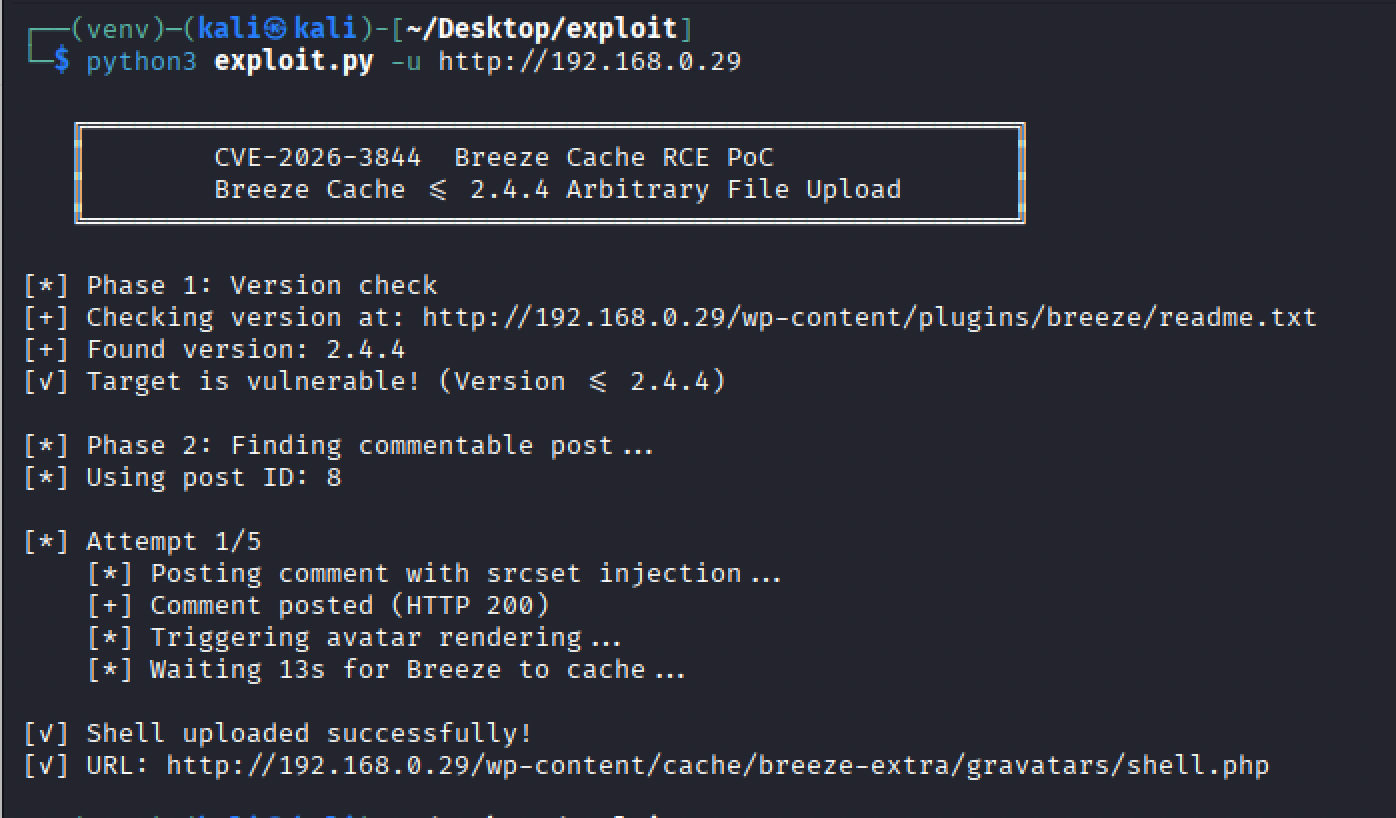 halilkirazkaya/cve-2026-3844
Exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to RCE in Breeze Cache WordPress plugin. Includes lab setup, usage, and…
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 razureink/cve-2024-49113-ldap_nightmare_reproduction
Reproduction of cve-2024-49113-ldap_nightmare_reproduction
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 usmansec/-cve-2021-4034
Controlled proof-of-concept assessment and exploitation report for CVE-2021-4034 (PwnKit) local privilege escalation in pkexec/polkit, with forensic…
 nxploited/cve-2025-15030
User Profile Builder < 3.15.2 - Unauthenticated Arbitrary Password Reset
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 d3vn0mi/cve-2025-60787-poc
Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config