
CVE-2022-3368
 wh04m1001/cve-2022-3368
Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
binary-exploitationexploitationpenetration-testing+3
29
wh04m1001/cve-2022-3368Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
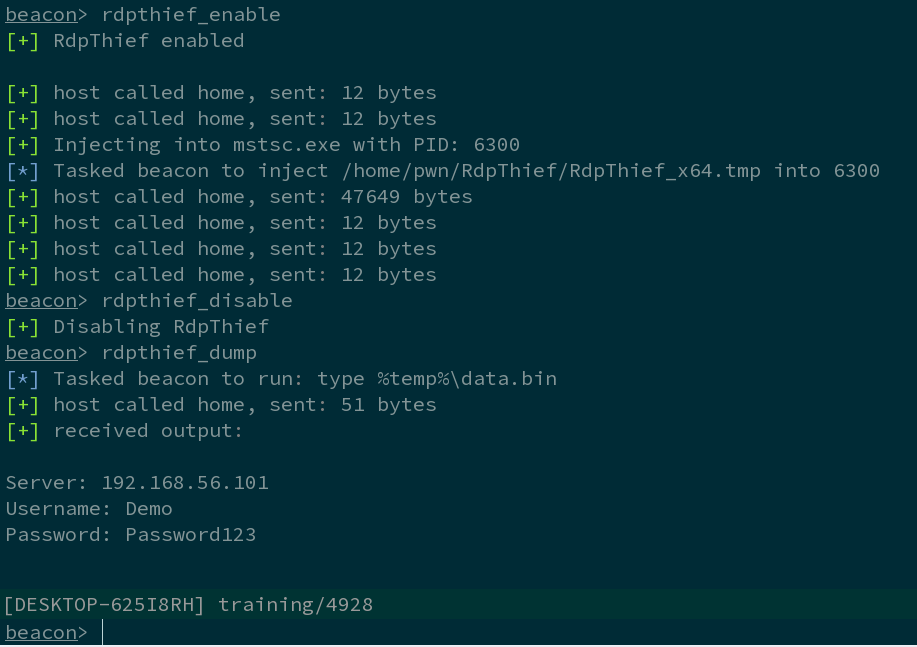 0x09al/rdpthief
Extracting Clear Text Passwords from mstsc.exe using API Hooking.
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 s12cybersecurity/rdpcredentialstealer
Windows implant that steals RDP credentials via API hooking (Detours) and DLL injection, capturing usernames and passwords to a file for red-team…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 enkomio/alanframework
A C2 post-exploitation framework
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 trailer2/cod-mw-warzone-2---cve-2023-38821
DLL Planting in the CoD MW Warzone 2 - CVE-2023-38821
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 dorkerdevil/cve-2026-89282
Proof-of-concept for CVE-2026-89282: proxy DLL search-order hijack in Apache Lounge Windows installs that yields SYSTEM privilege escalation on…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 knight0x07/bumblecrypt
A Bumblebee-inspired Crypter
 malwaretech/uacelevator
Passive UAC elevation using dll infection
 egebalci/amber
Reflective PE packer.
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.