
RustHound-CE
 g0h4n/rusthound-ce
Active Directory data ingestor for BloodHound Community Edition written in Rust. 🦀
information-gatheringpenetration-testingreconnaissance+1
g0h4n/rusthound-ceActive Directory data ingestor for BloodHound Community Edition written in Rust. 🦀
 nh-red-team/rusthound
Active Directory data ingestor for BloodHound Legacy written in Rust. 🦀
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 mverschu/adwsdomaindump
Active Directory information dumper via ADWS for evasion purposes.
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 javelinnetworks/honeypotbuster
PowerShell module for red teams to detect honeypots, honeytokens, and deception techniques in Active Directory environments, including fake accounts,…
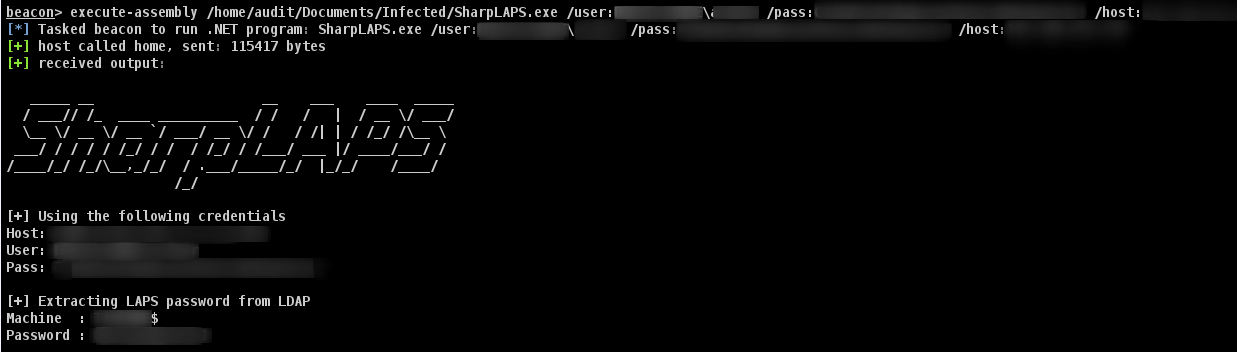 swisskyrepo/sharplaps
C# tool to retrieve LAPS passwords from Active Directory via LDAP, designed for in-memory execution within Cobalt Strike sessions using…
 hunniccyber/sharpsniper
Find specific users in active directory via their username and logon IP address
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 ccob/gssapi-abuse
A tool for enumerating potential hosts that are open to GSSAPI abuse within Active Directory networks
 xmcyber/machound
Extends BloodHound to collect and ingest Active Directory relationships from macOS hosts, including logged-in users, admin groups, SSH/VNC/AppleEvent…
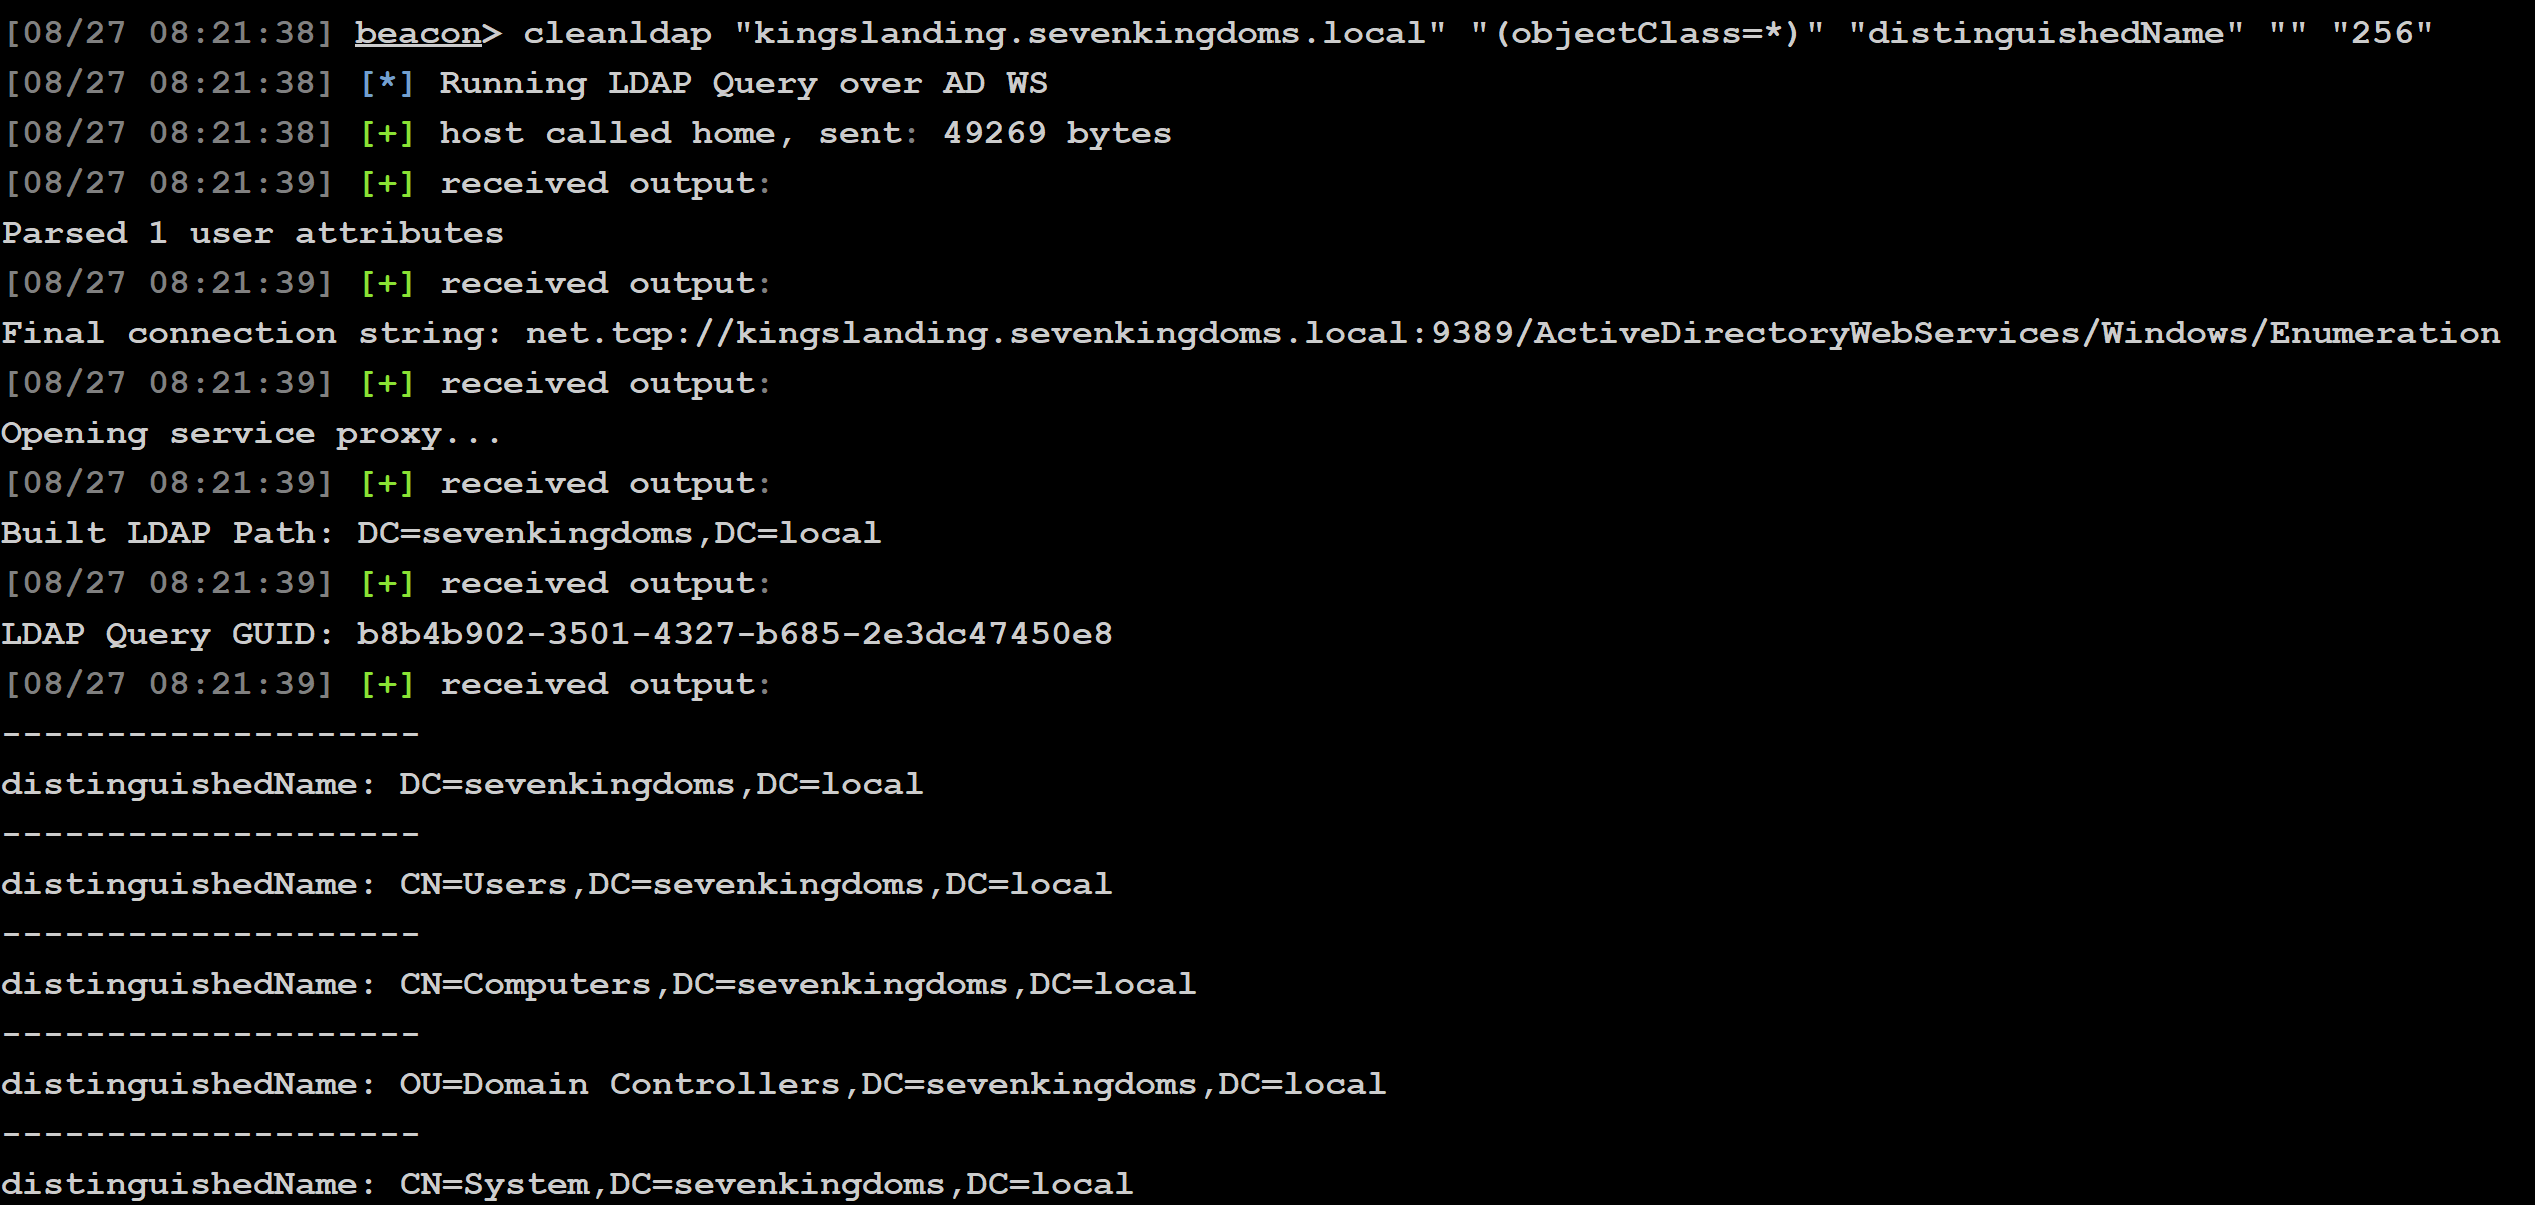 mandiant/cleanldap
Stealthy LDAP query BOF for Active Directory reconnaissance via AD WS, enabling attribute enumeration and data collection for red team operations.
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 mitchmoser/lacheck
Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
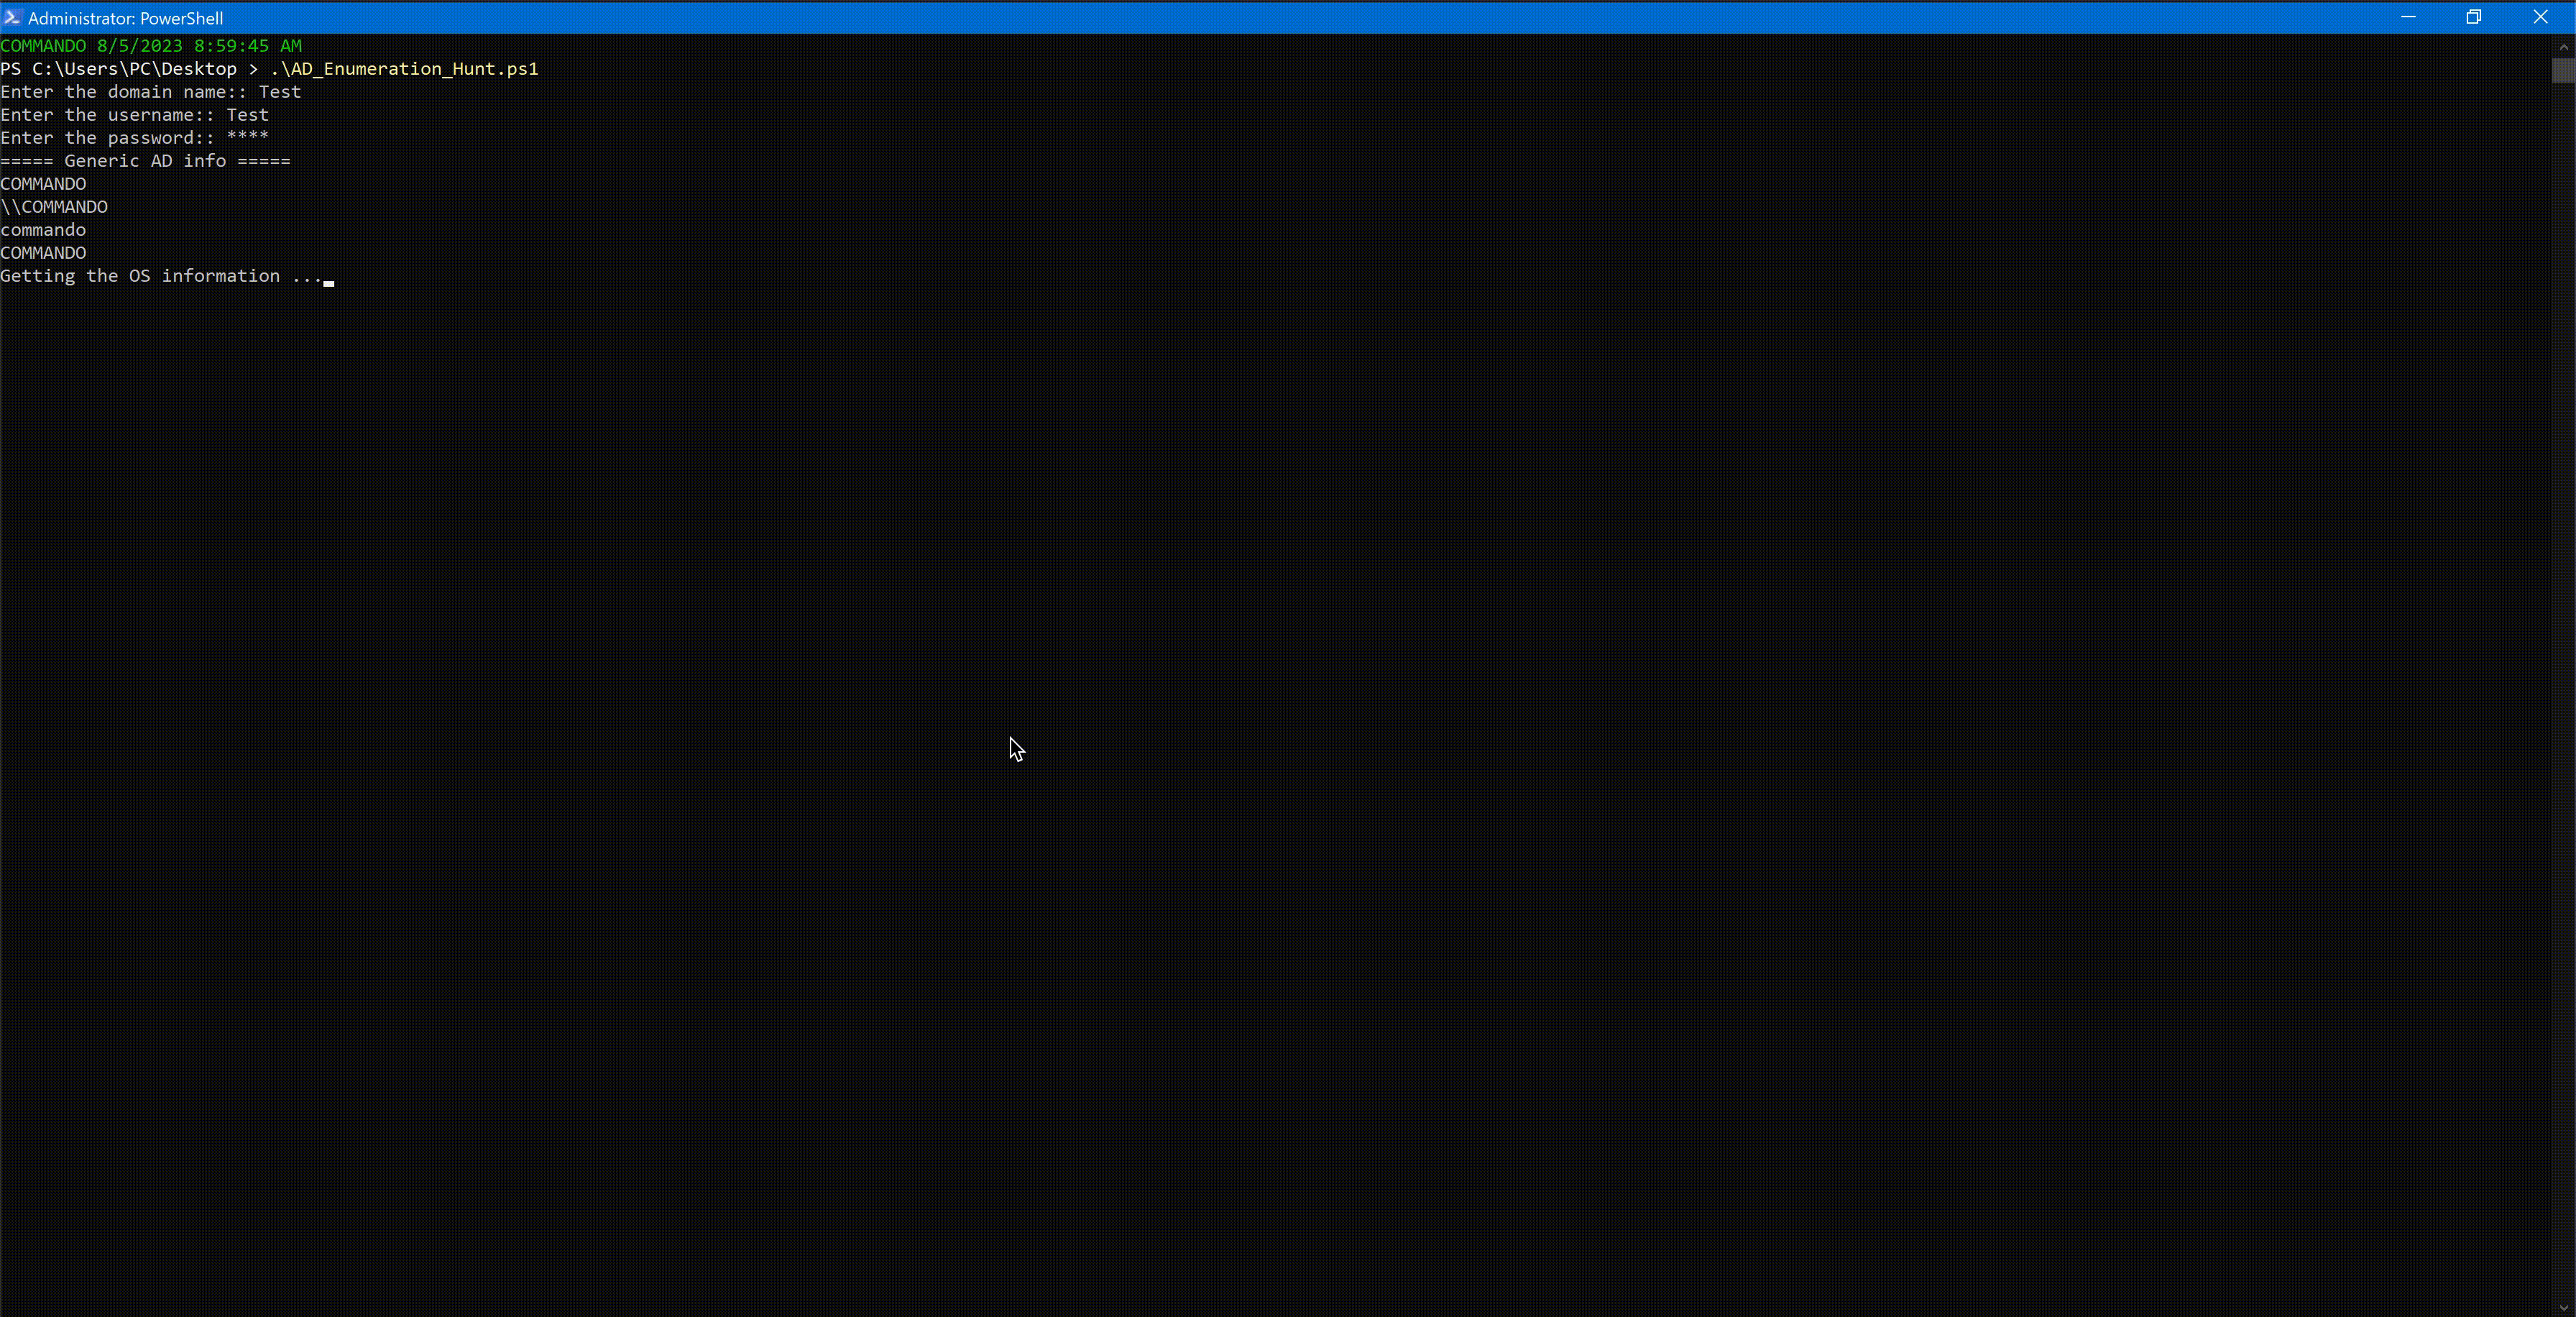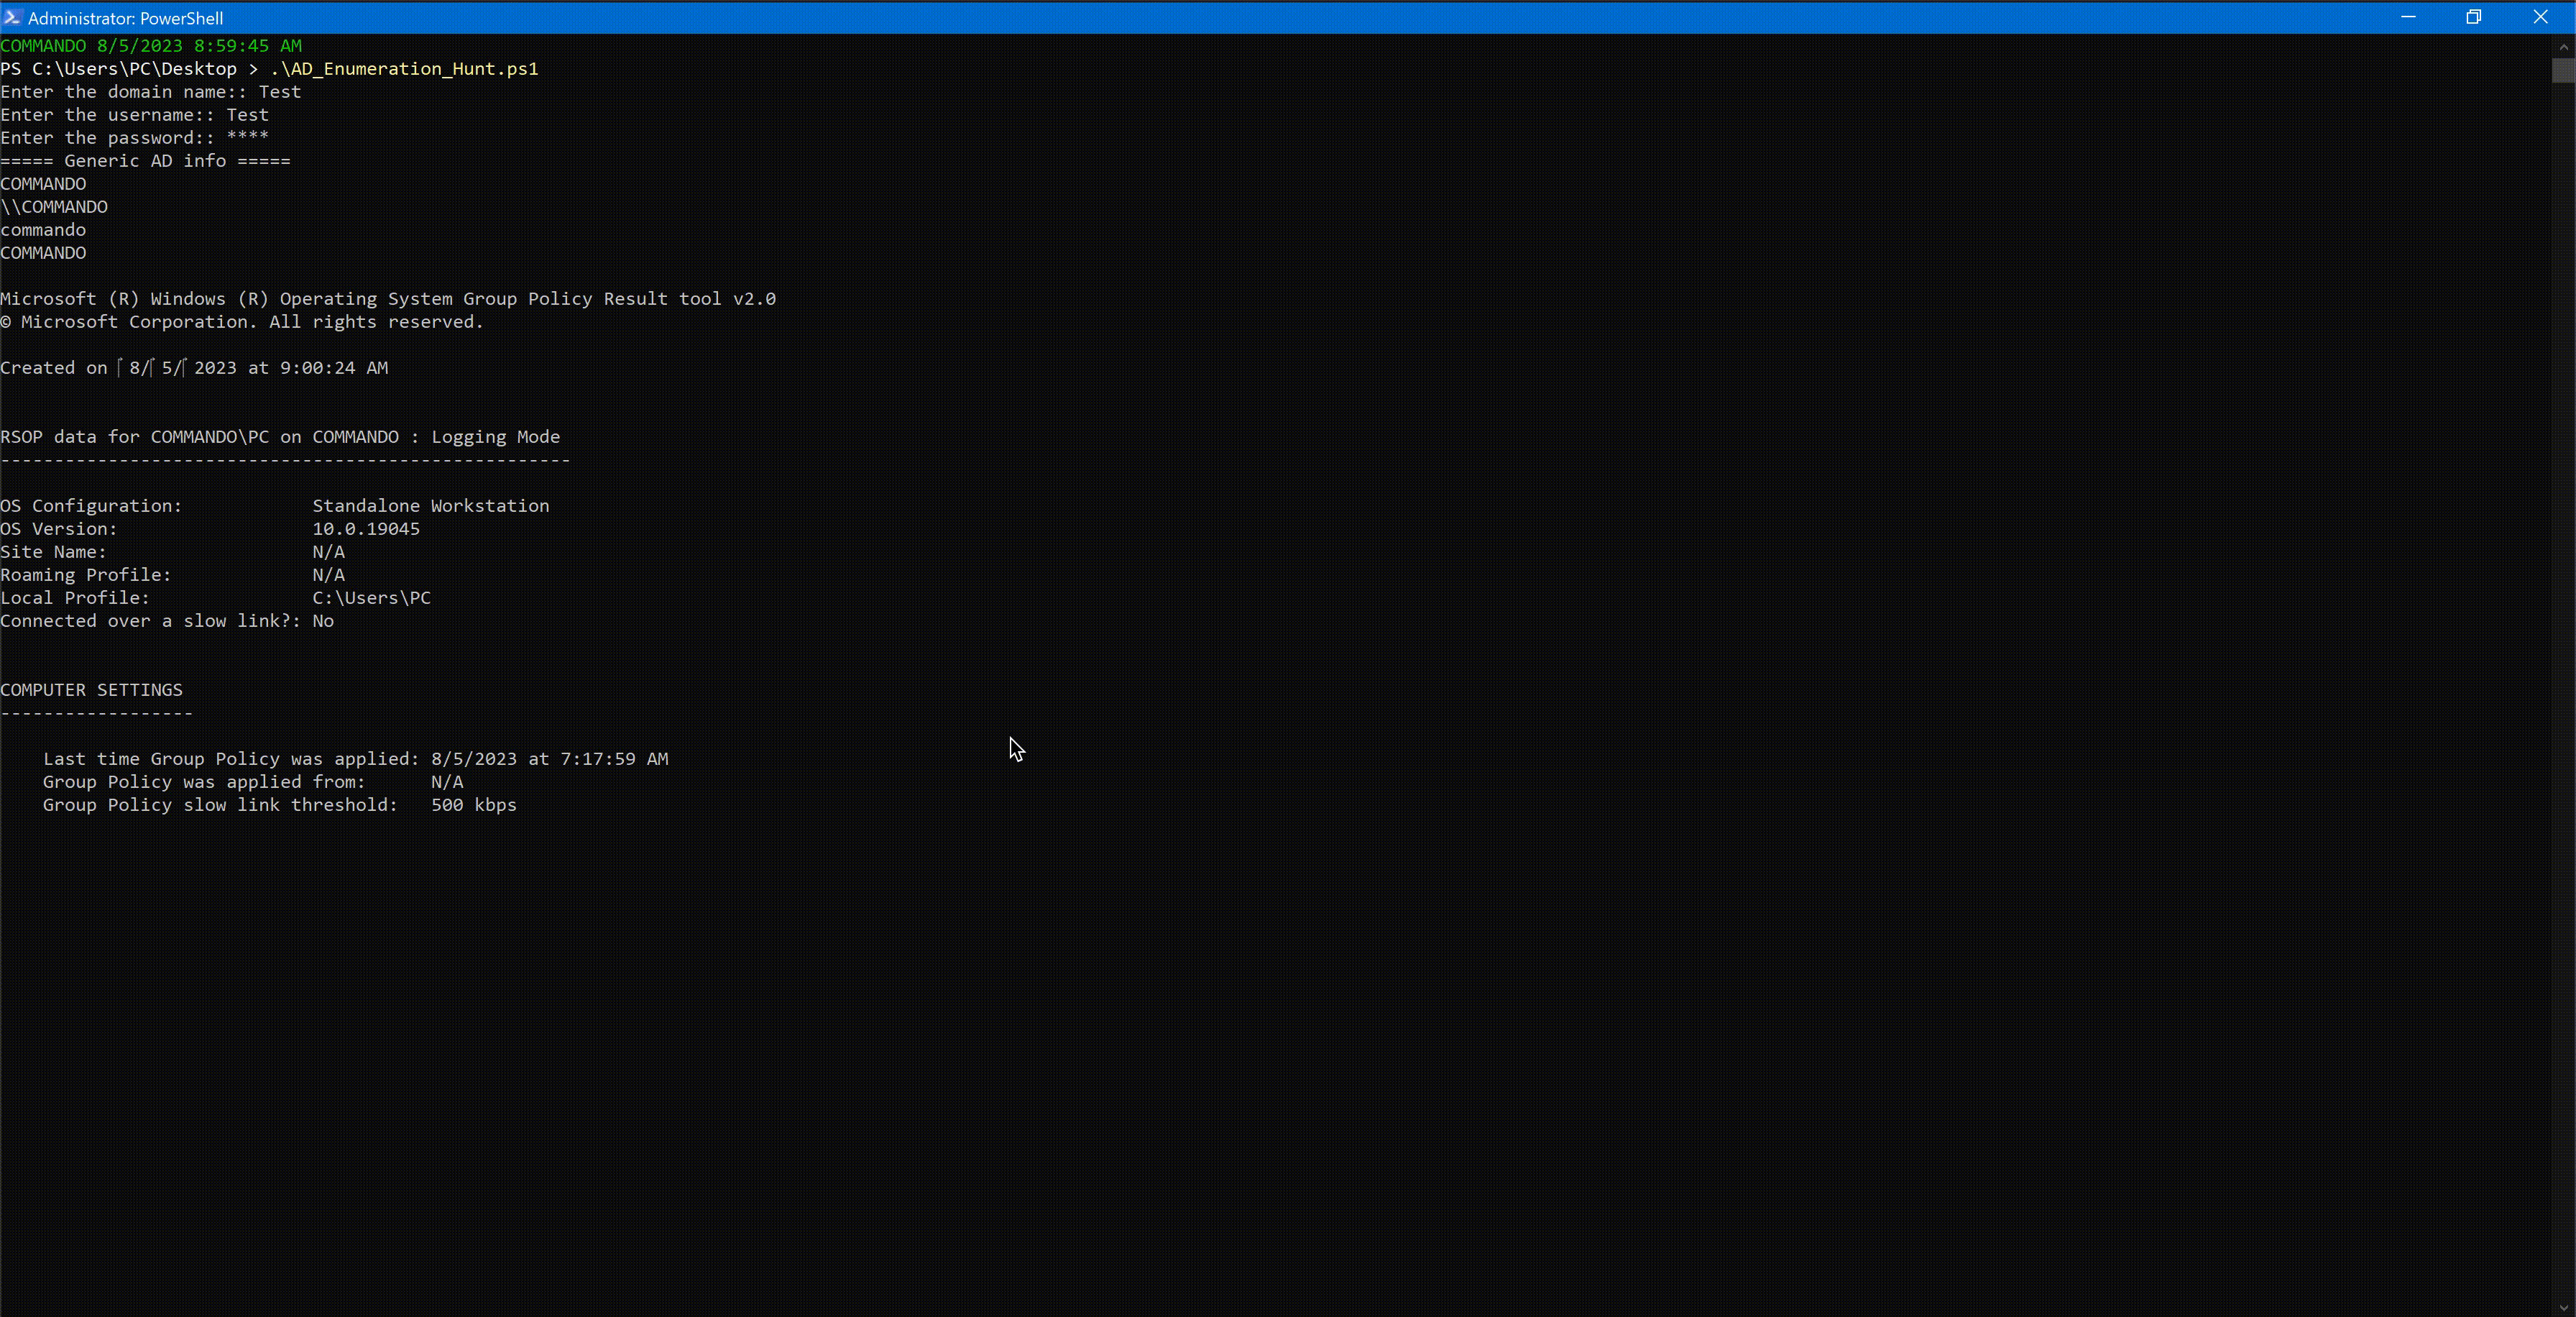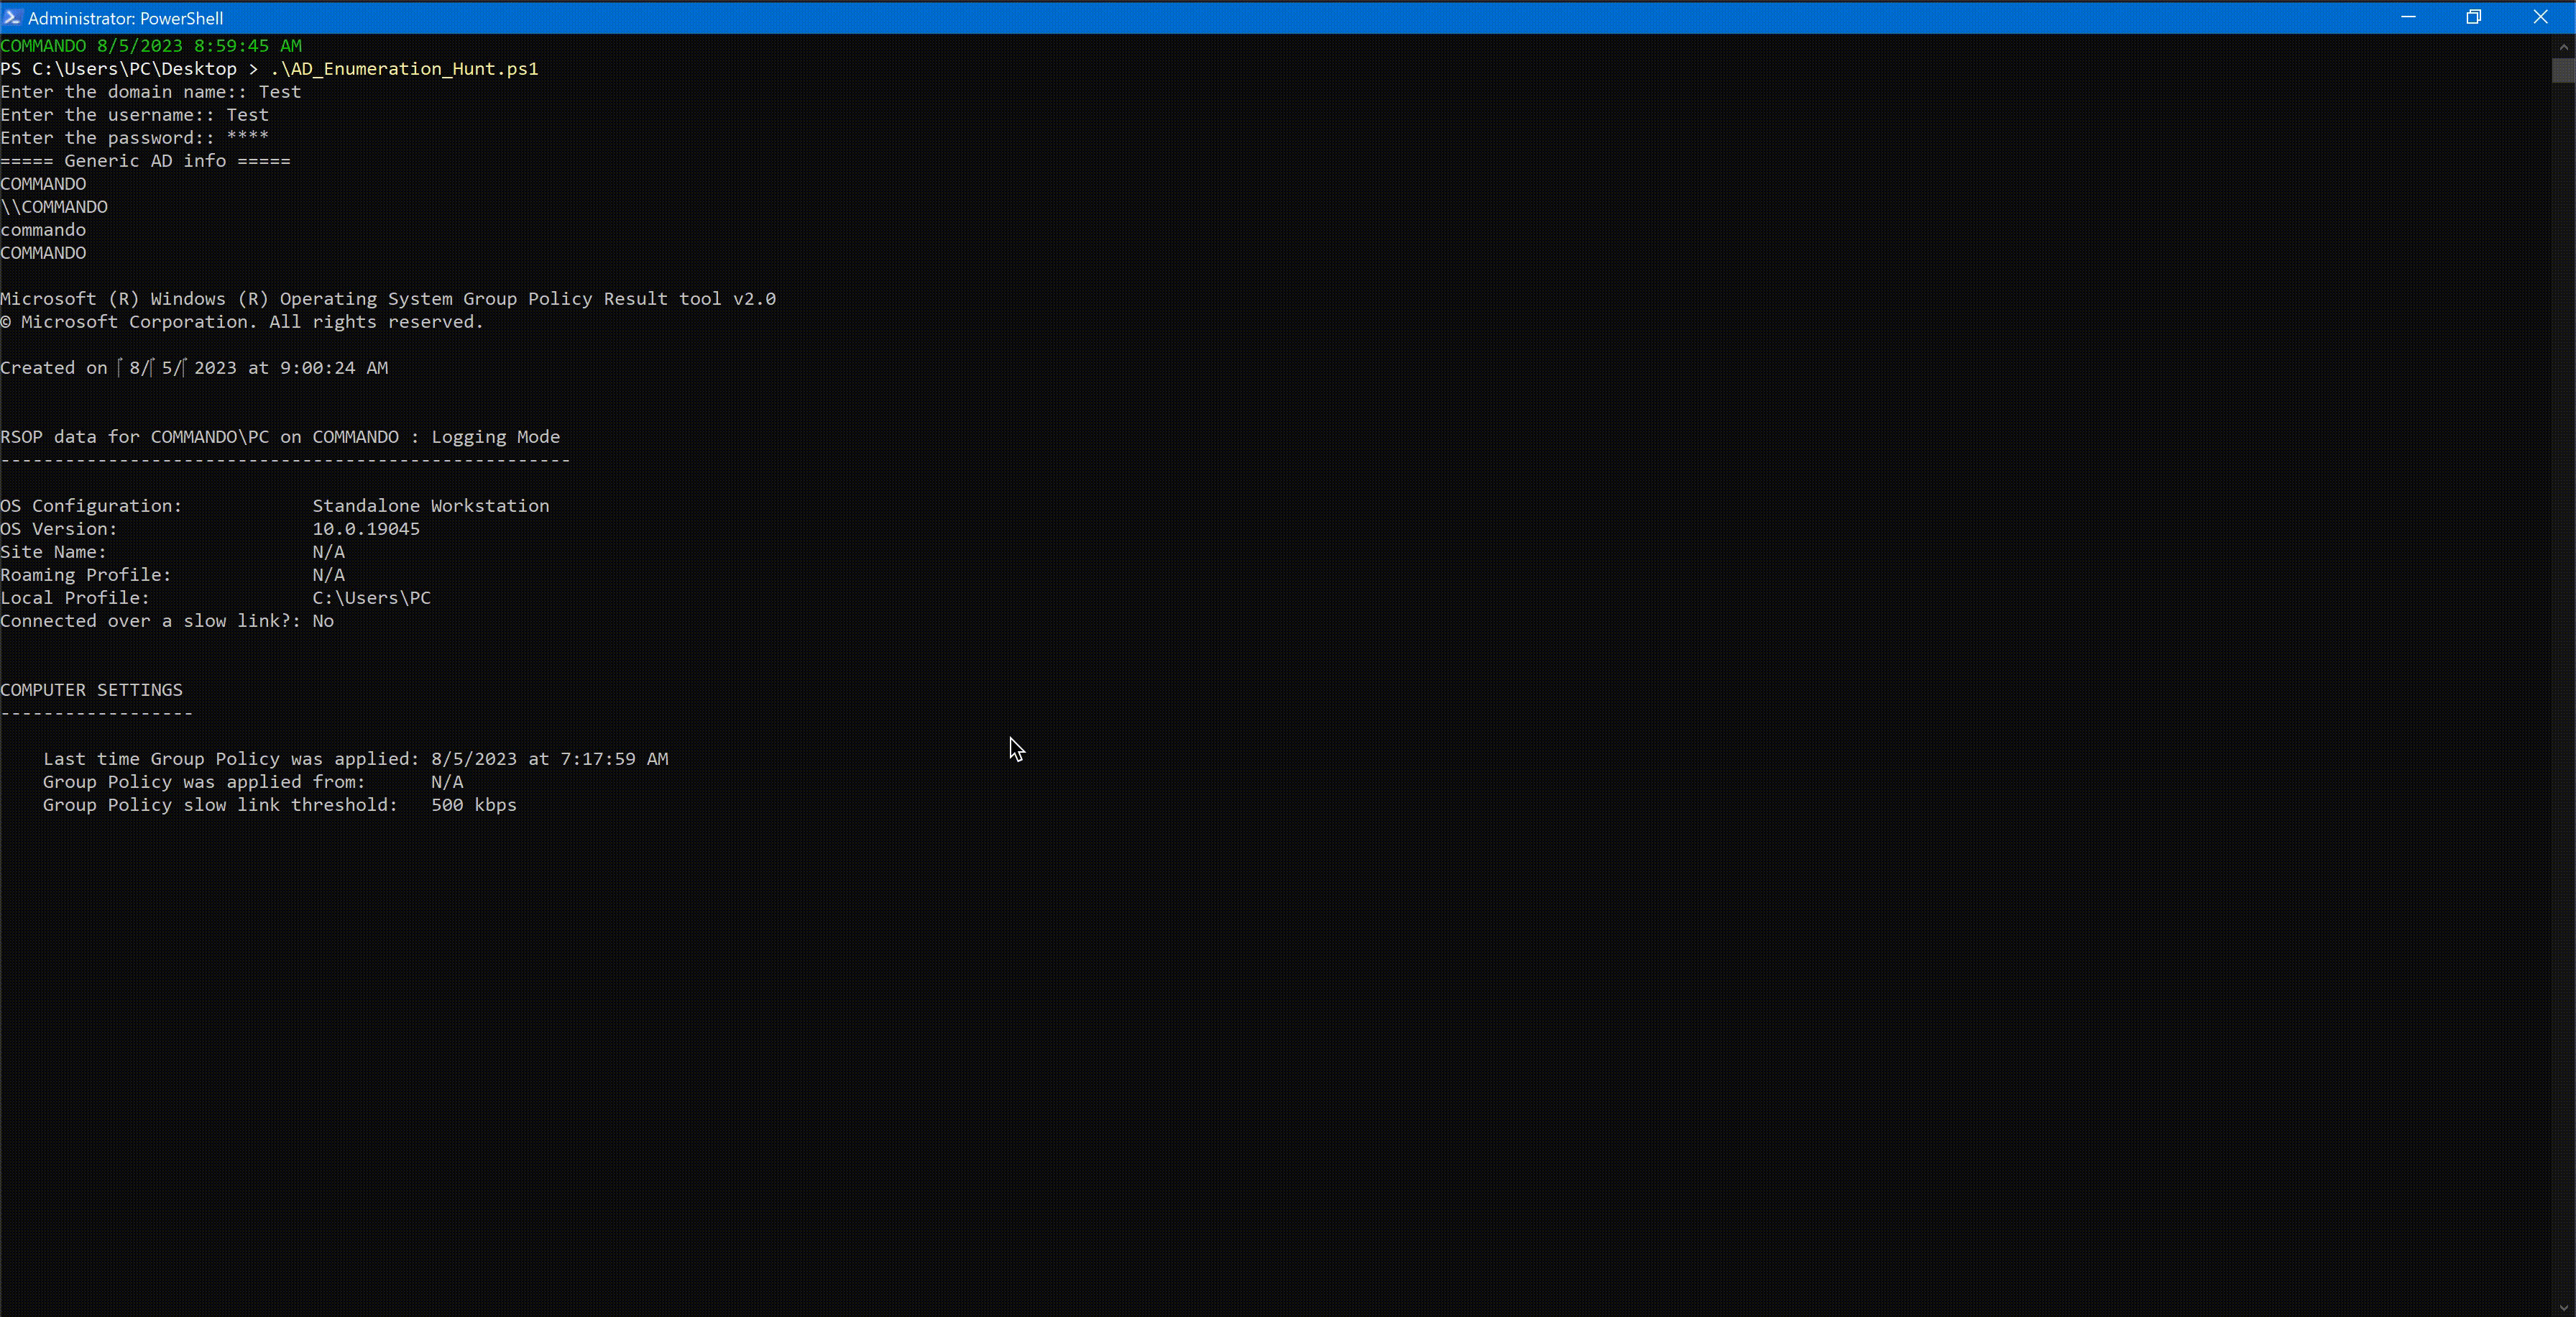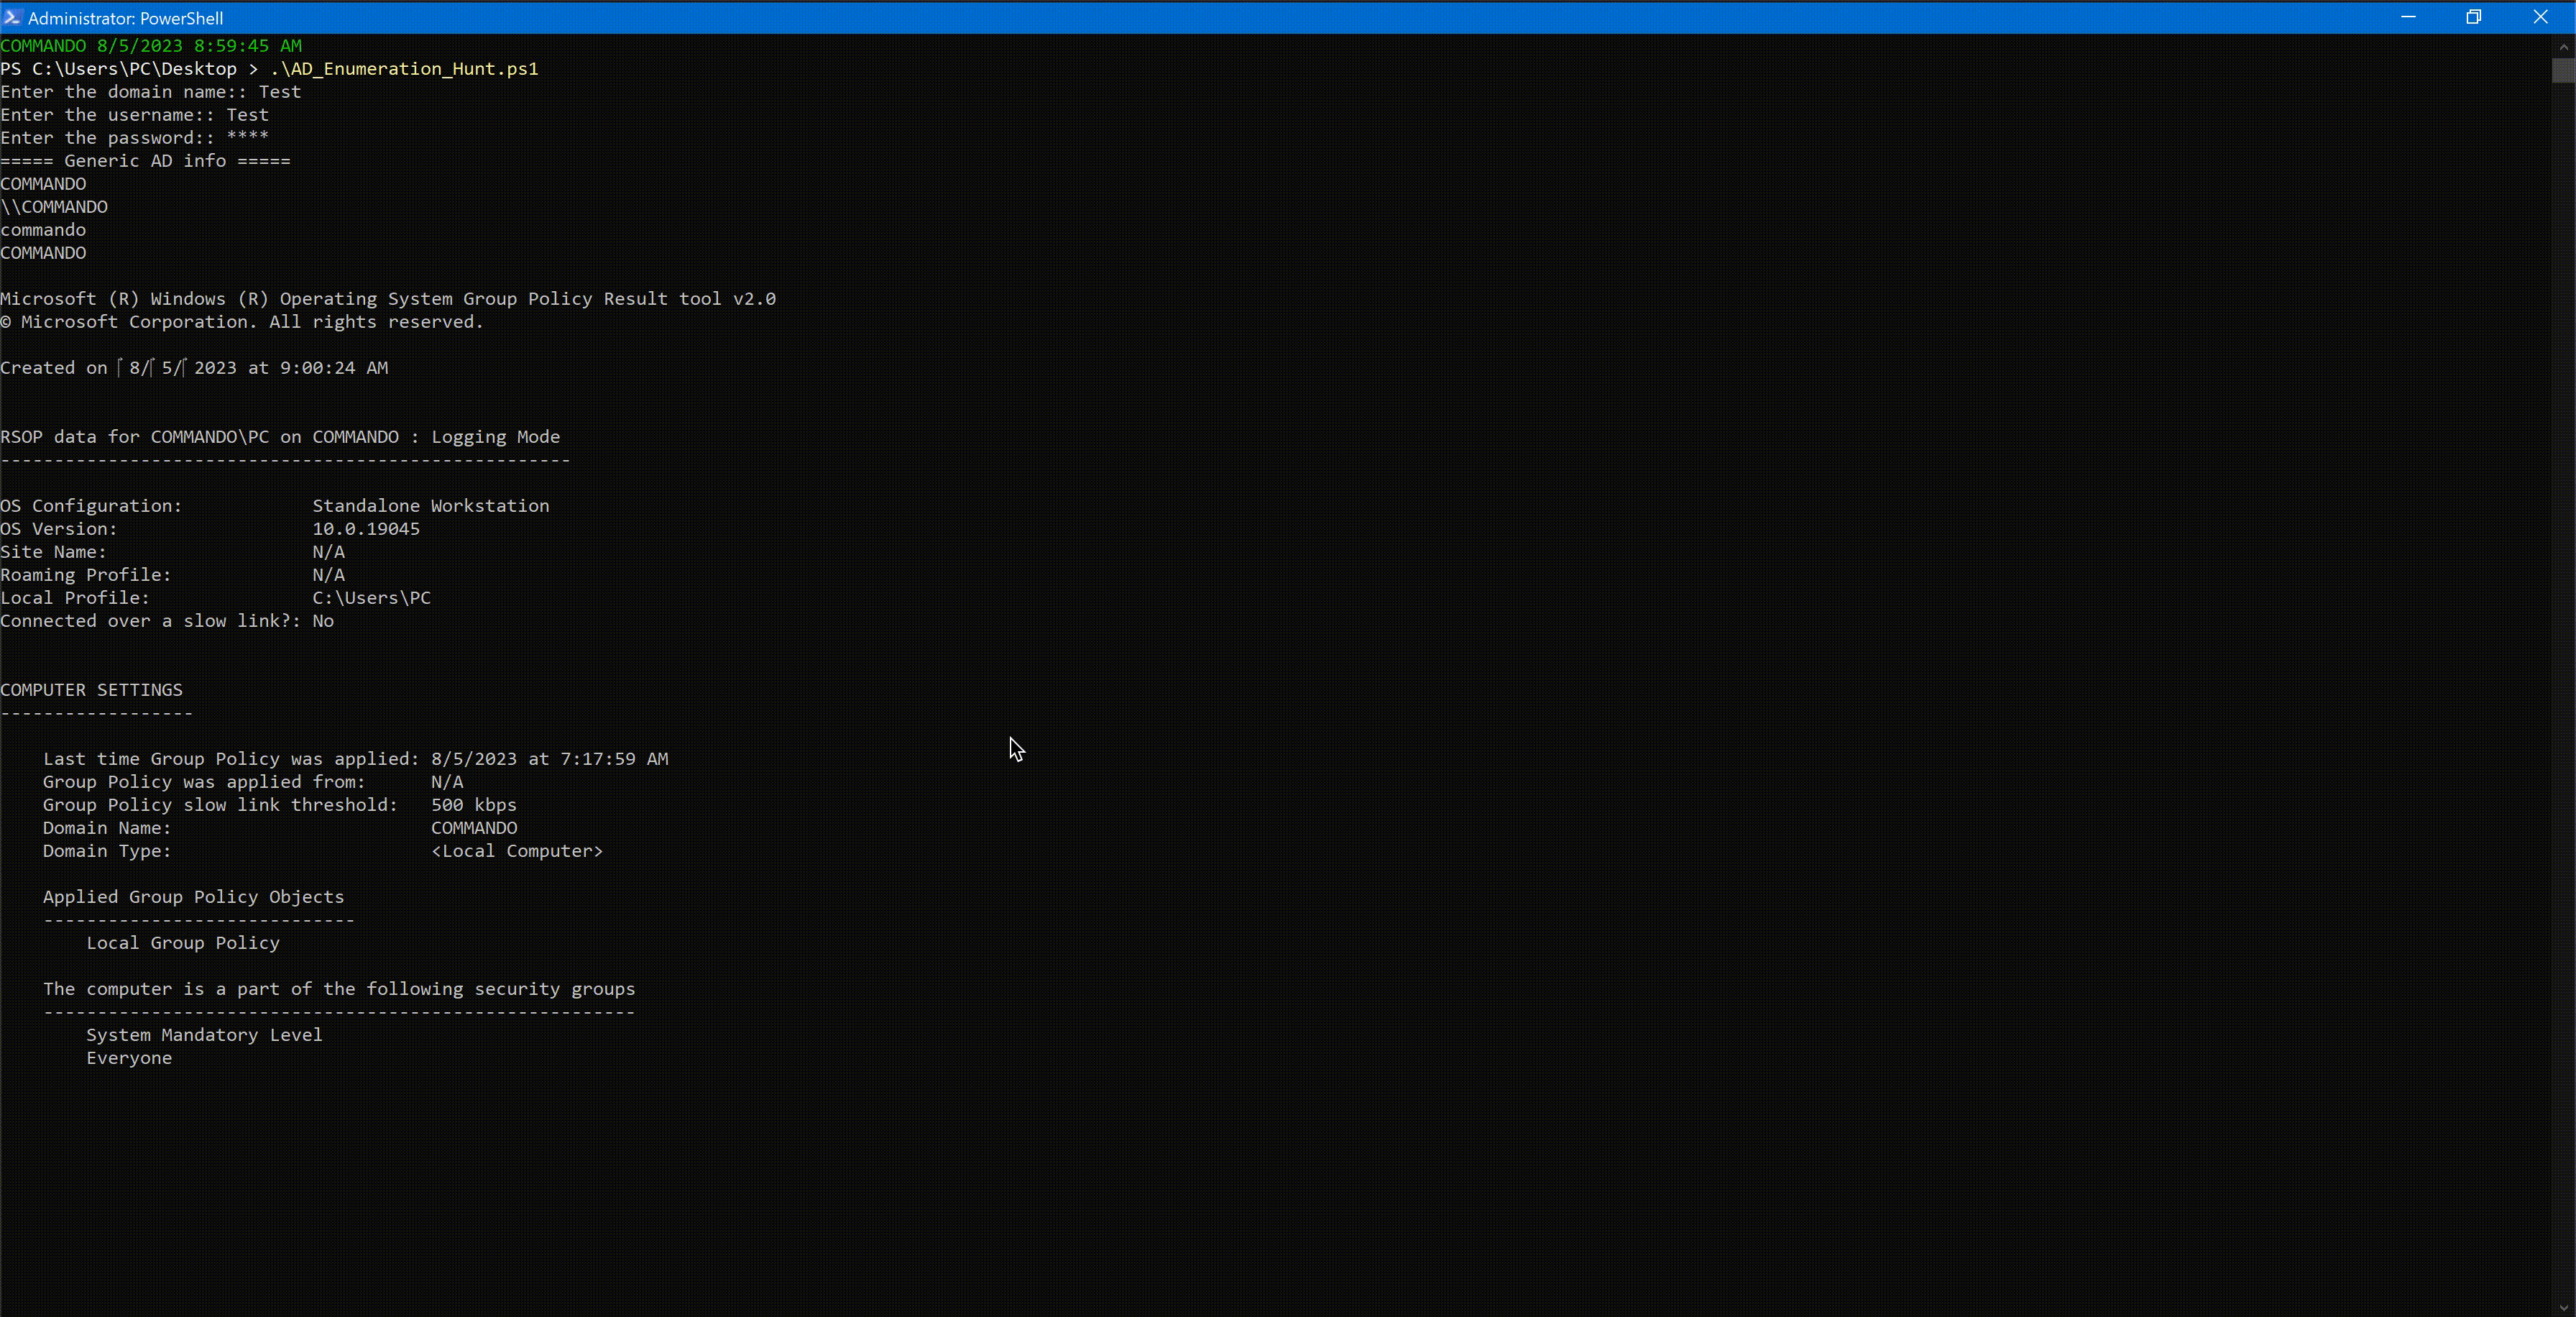 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
 crypt0p3g/adnullenum
One-pass anonymous Active Directory enumeration over SAMR and LSARPC — null session, no credentials, with structured reusable output.
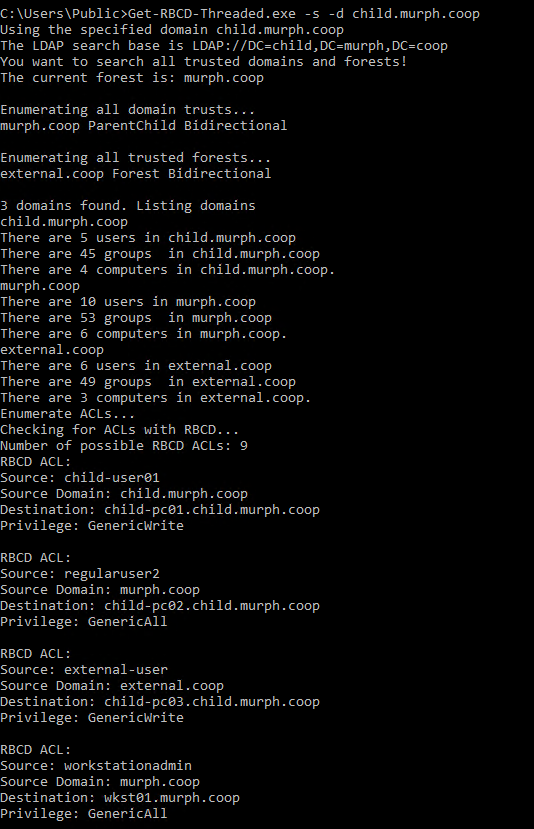 fatrodzianko/get-rbcd-threaded
Tool to discover Resource-Based Constrained Delegation attack paths in Active Directory environments