DDoS-Purple-Teaming-Offensive-Multi-Vector-7-Tier-Defensive-Holistic-Blueprint-

Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…

Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…

Authenticated remote code execution exploit for FusionPBX versions <= 4.5.10, leveraging the PHP-Editor function to inject a payload and gain a shell…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…

Proof-of-concept exploit for CVE-2026-20131, a pre-authentication RCE in Cisco Catalyst SD-WAN Controller and Manager, enabling admin access and…

Proof-of-concept exploit for CVE-2026-26215, an unauthenticated remote code execution vulnerability in manga-image-translator via unsafe pickle…

Proof-of-concept exploit for CVE-2025-66478, demonstrating remote code execution in Next.js via crafted multipart requests with prototype pollution.

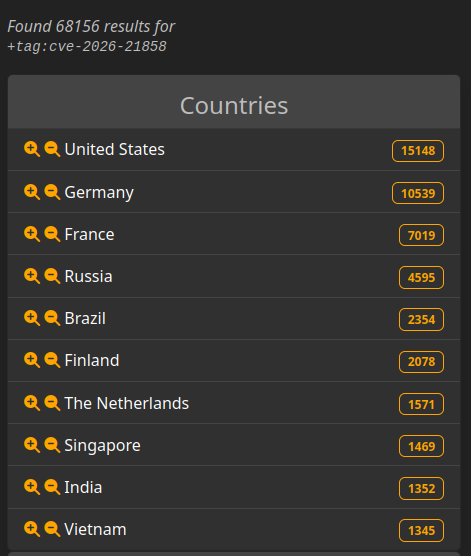
Exploit for CVE-2026-21858, a critical unauthenticated content-type parsing flaw in n8n allowing arbitrary file read, credential theft, and remote…

Technical audit and reproduction of CVE-2026-21858, an n8n RCE chain exploiting Content-Type confusion for arbitrary file read, session forgery, and…

Proof-of-concept exploit for unauthenticated remote code execution in Hyland OnBase Timer Service via .NET Remoting BinaryFormatter deserialization,…

Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow 1.8.1 via the build_public_tmp endpoint, enabling Python code injection through…

Unified Security Research Tool

Automated exploit chain for n8n combining arbitrary file read, admin token forgery, and sandbox bypass to achieve unauthenticated remote code…

This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…

Python exploit for CVE-2026-21627, an unauthenticated arbitrary PHP file inclusion in Joomla's Novarain Framework, enabling file upload, delete, and…

Self-contained exploit for CVE-2021-4034 - Pkexec Local Privilege Escalation

Proof of Concept for Authenticated RCE in Crafty Controller

Next.js RSC RCE vulnerability scanner with multiple scan modes, WAF bypass, interactive shell, and batch scanning for authorized penetration testing.