
ESP32Marauder
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
bluetooth-securitydefensive-toolsembedded-systems-security+6
12.9k
justcallmekoko/esp32marauderA suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
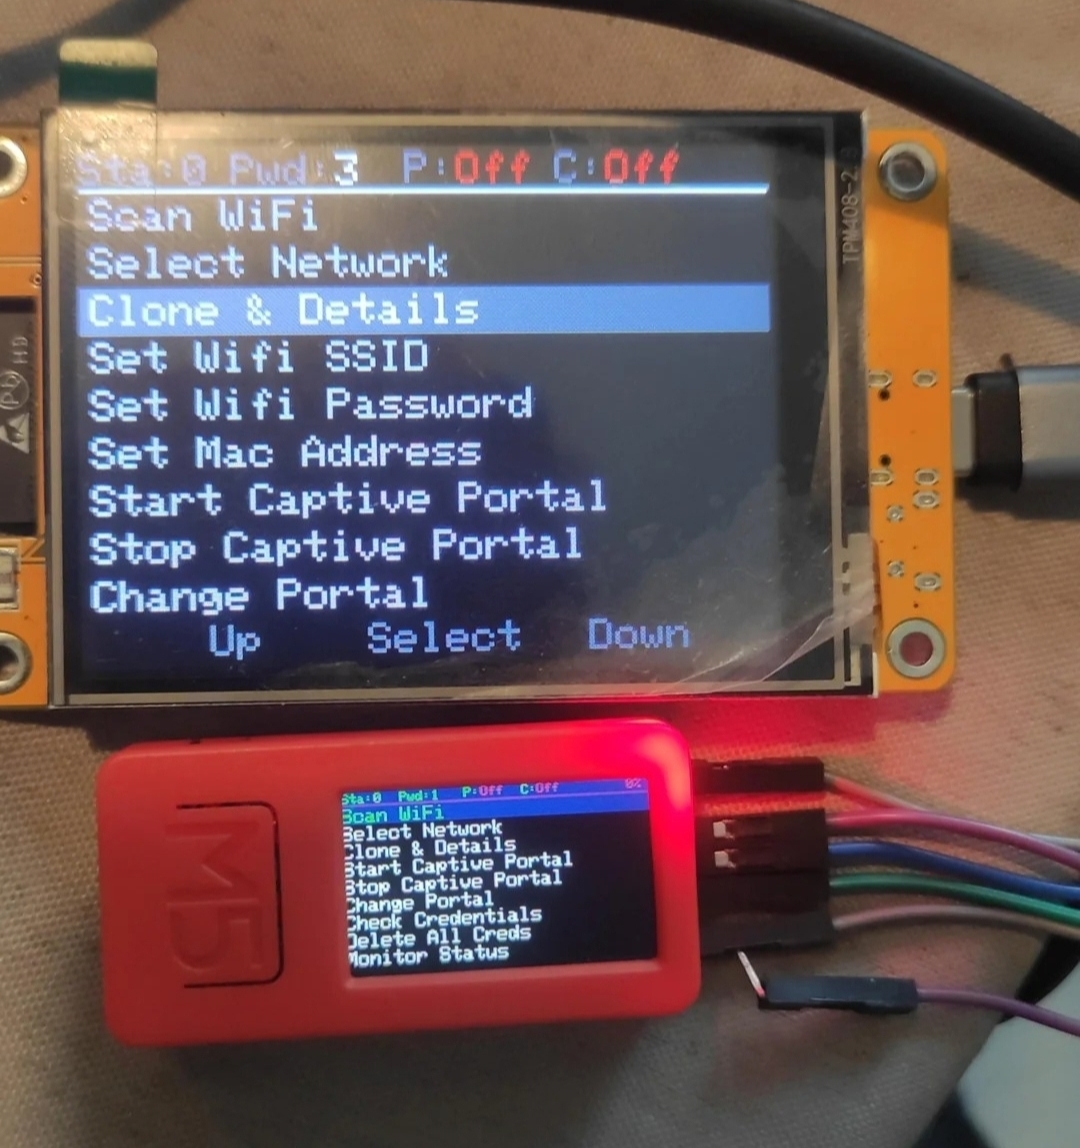 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
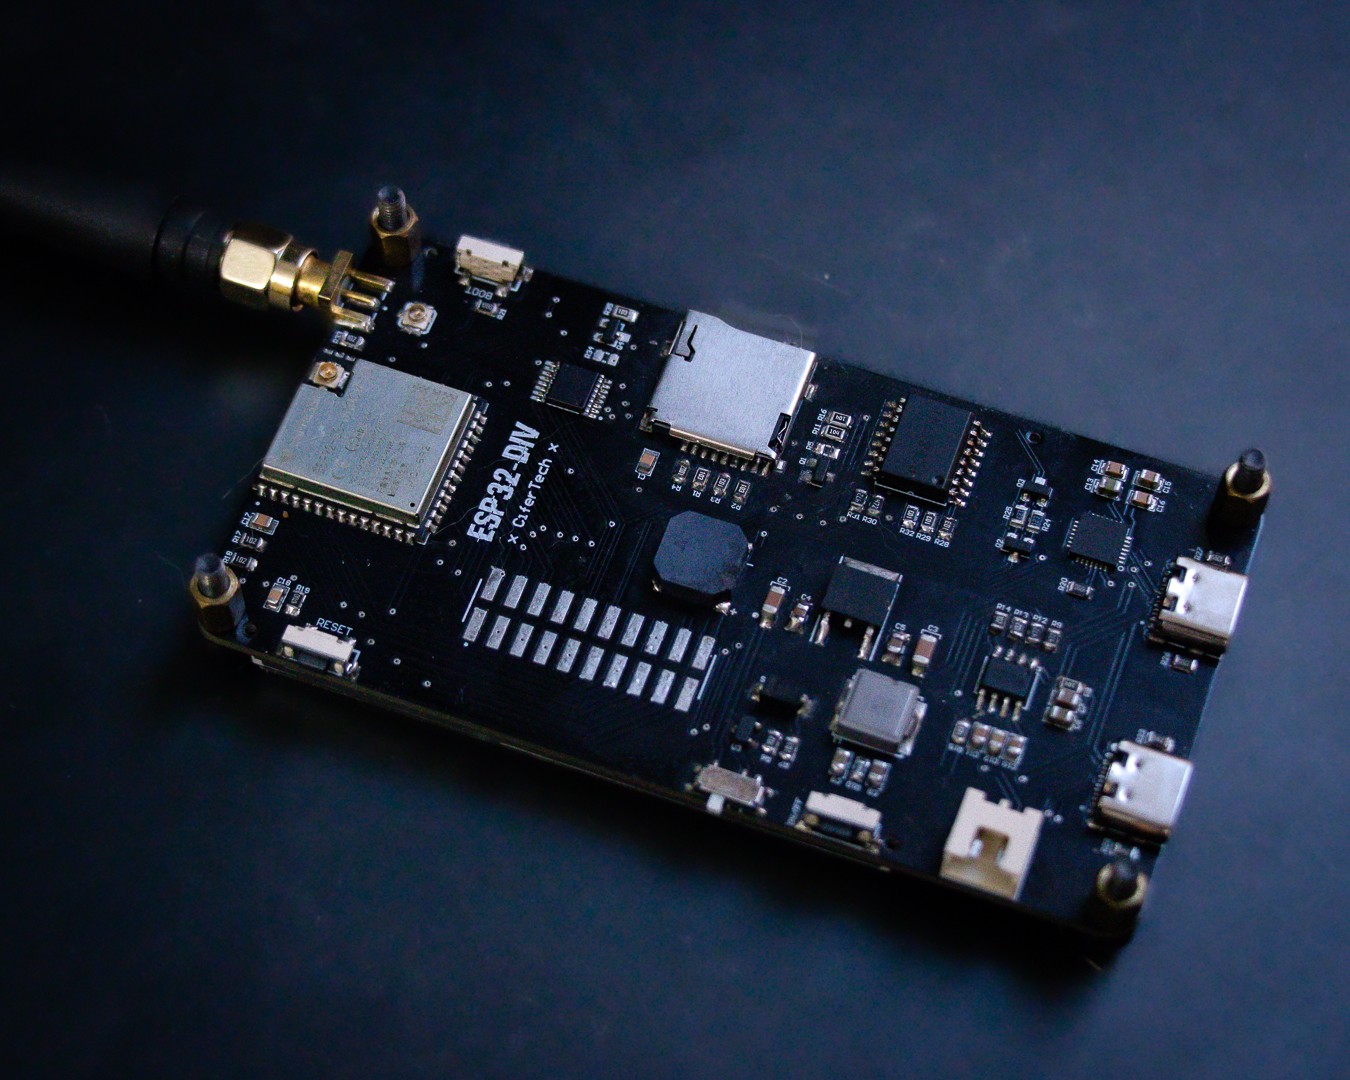 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
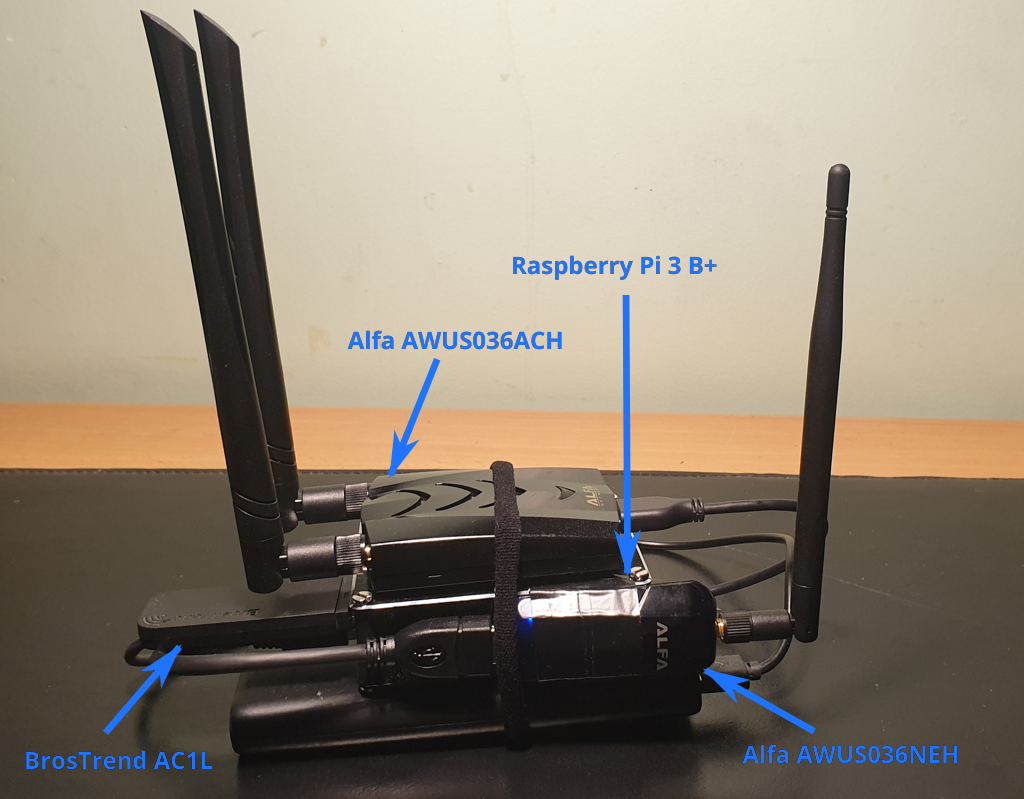 koutto/pi-pwnbox-rogueap
Homemade Pwnbox :rocket: / Rogue AP :satellite: based on Raspberry Pi — WiFi Hacking Cheatsheets + MindMap :bulb:
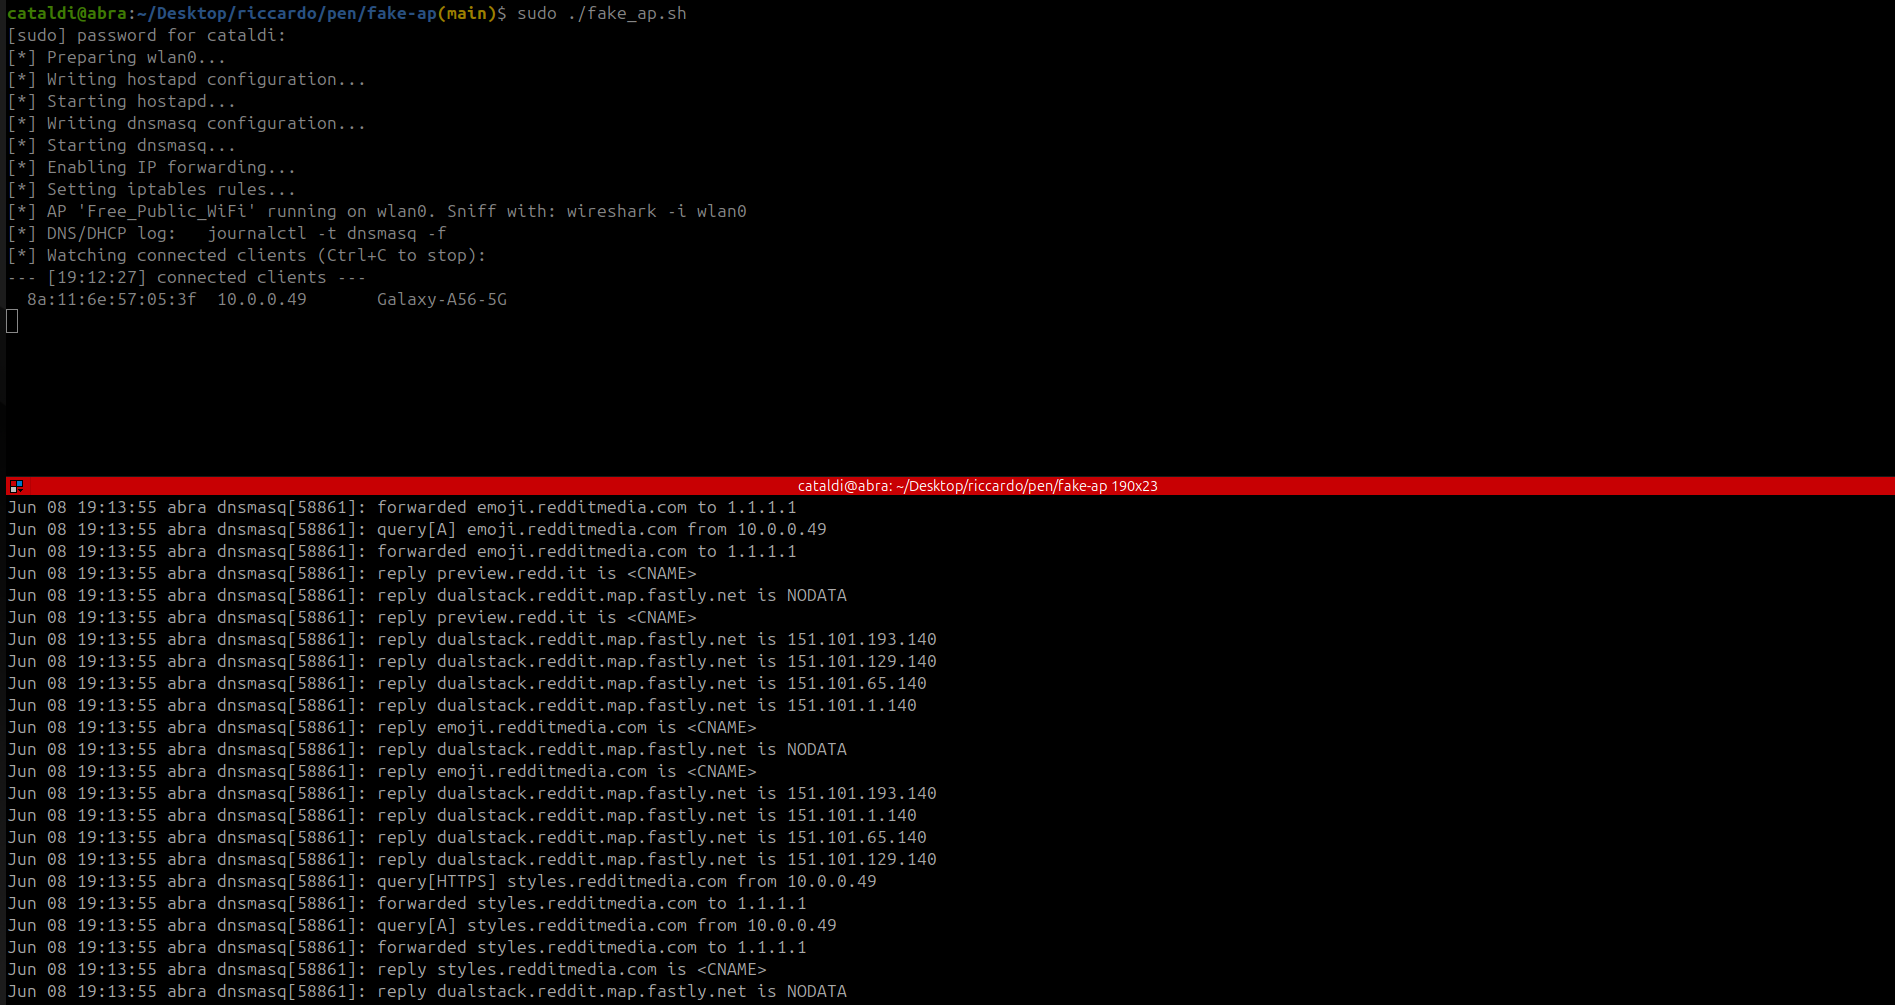 riccardocataldi/access-point
Rogue open Wi-Fi AP for controlled traffic capture using hostapd, dnsmasq, and iptables NAT. Enables real-time client monitoring, DNS/DHCP logging,…
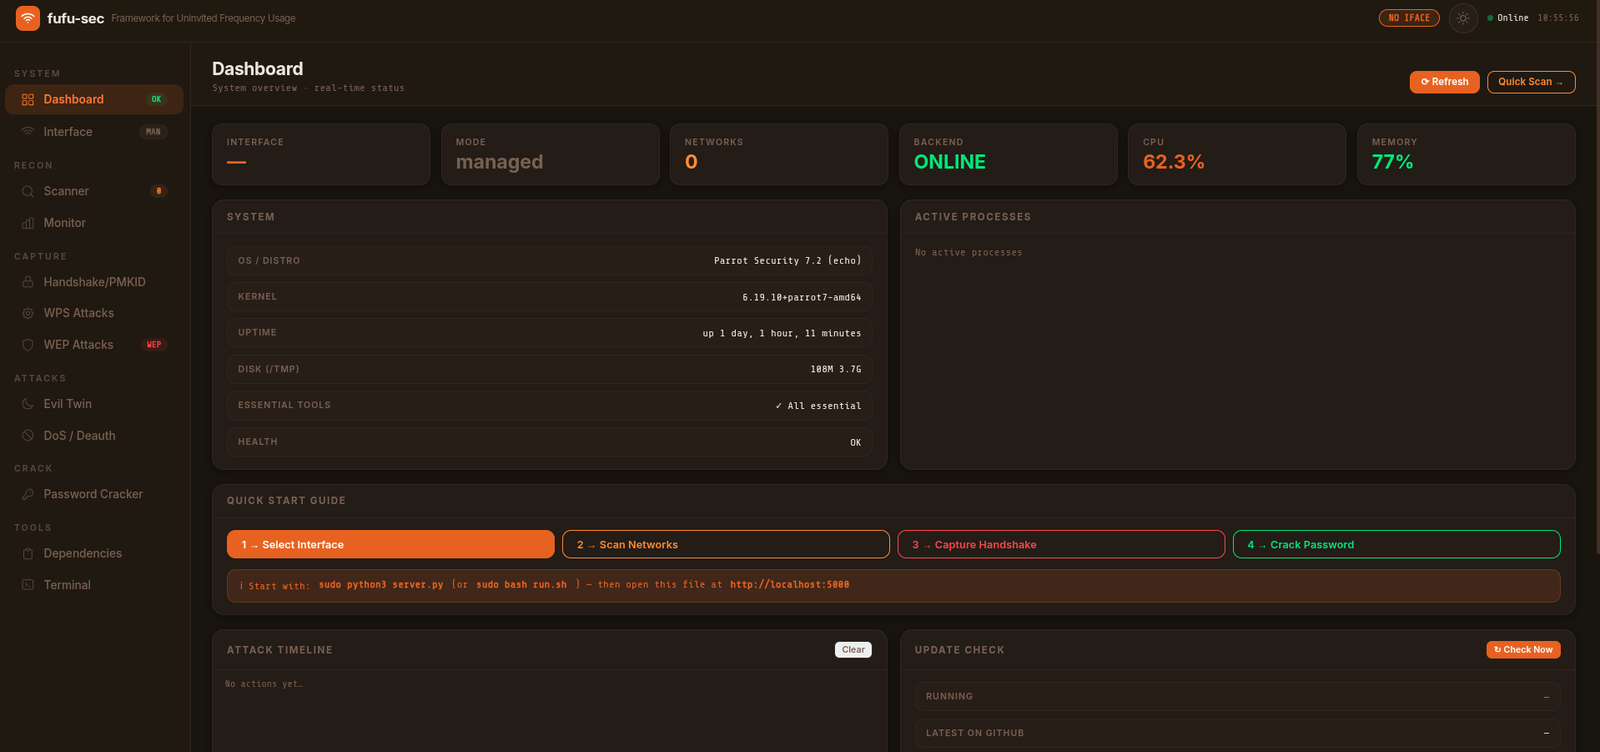 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
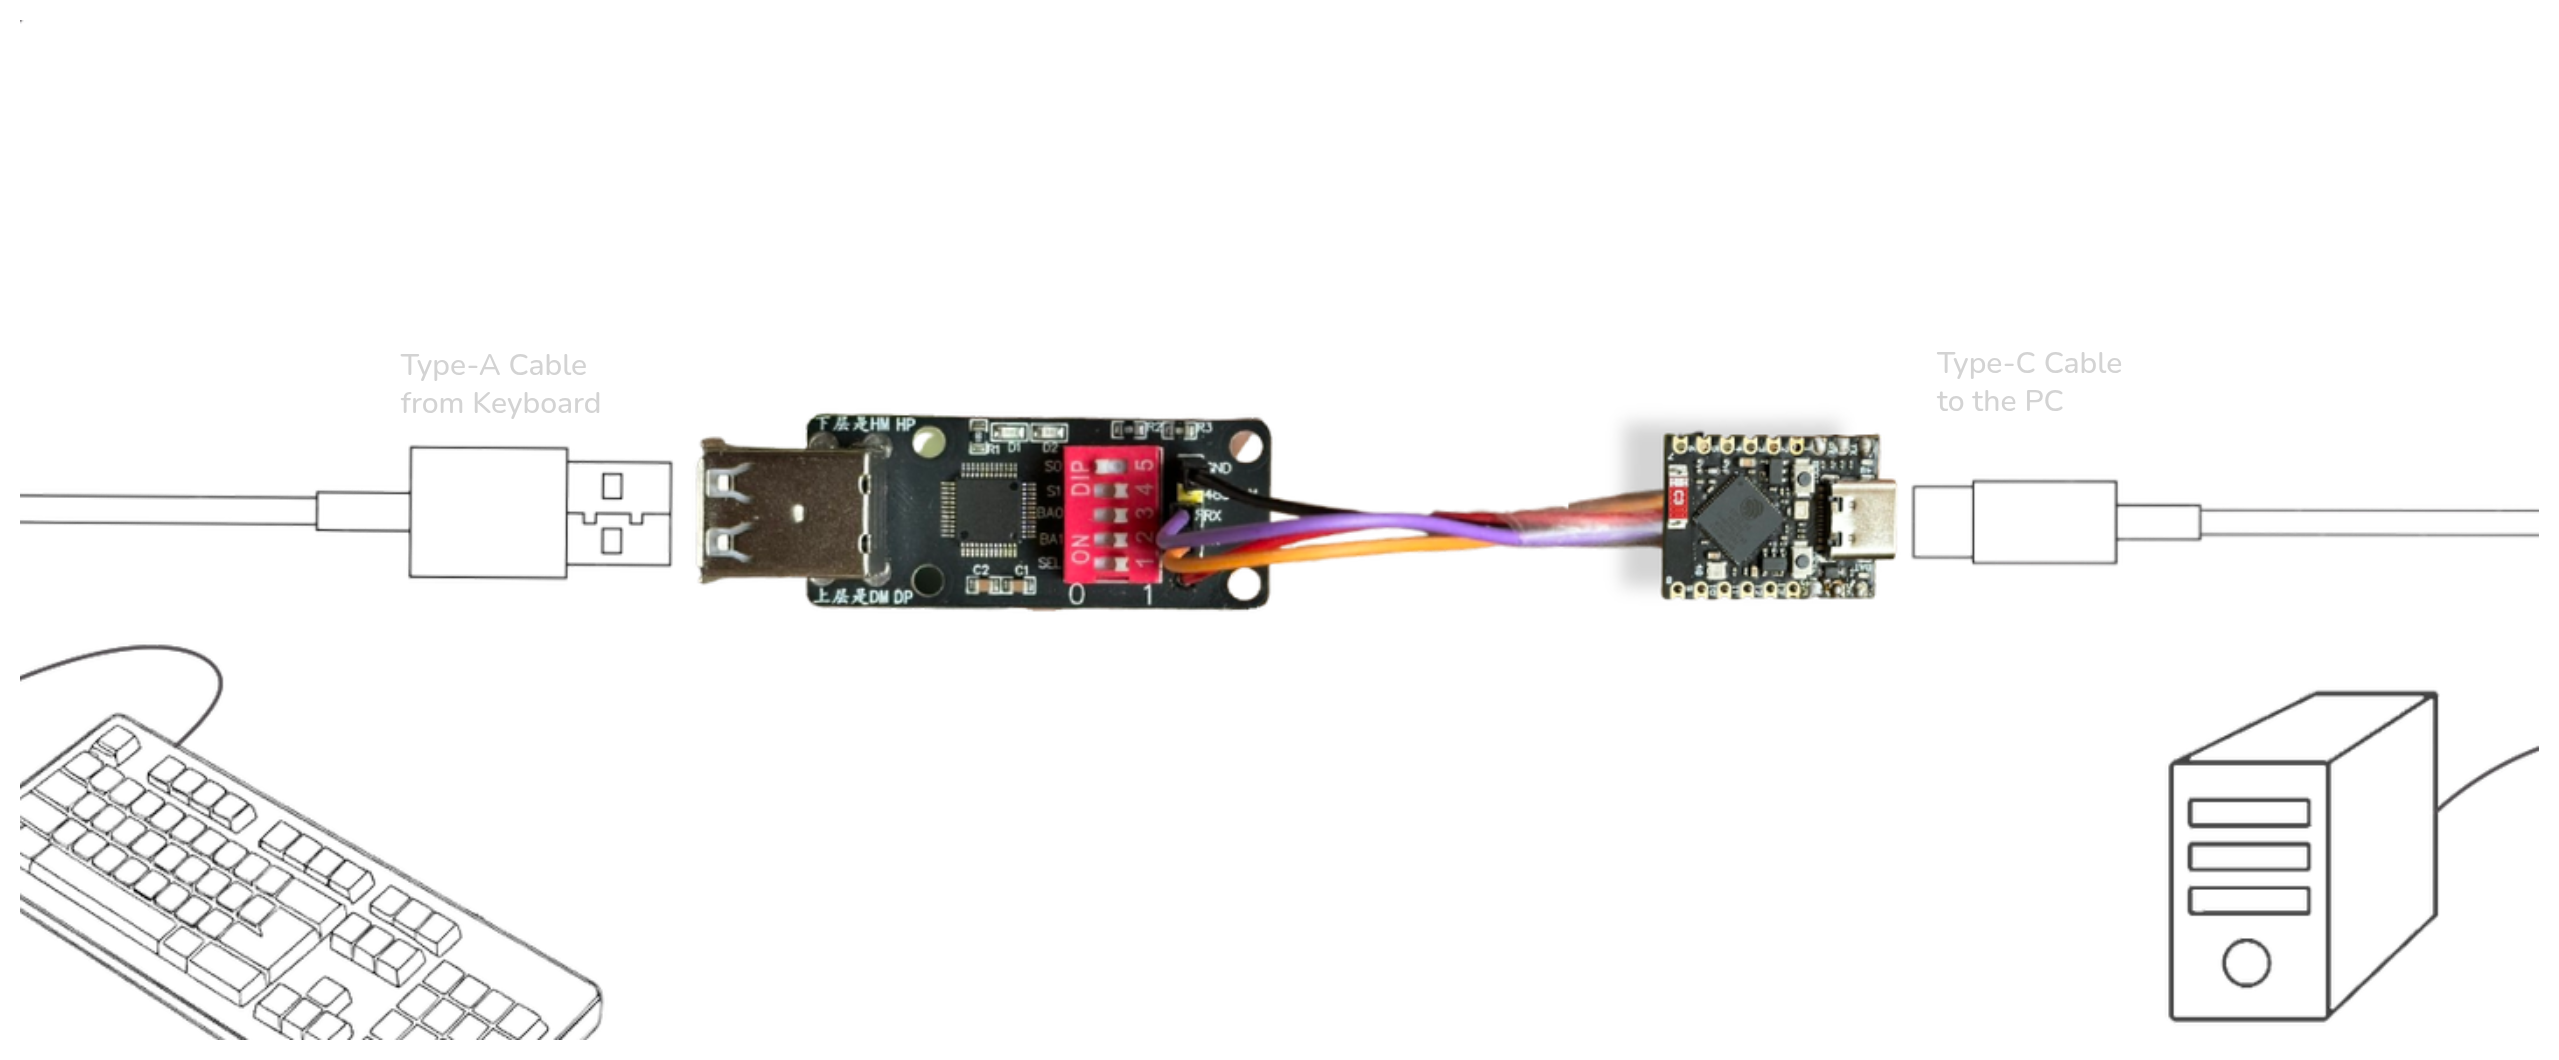 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 emenstanougat/esp32-bluejammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking