
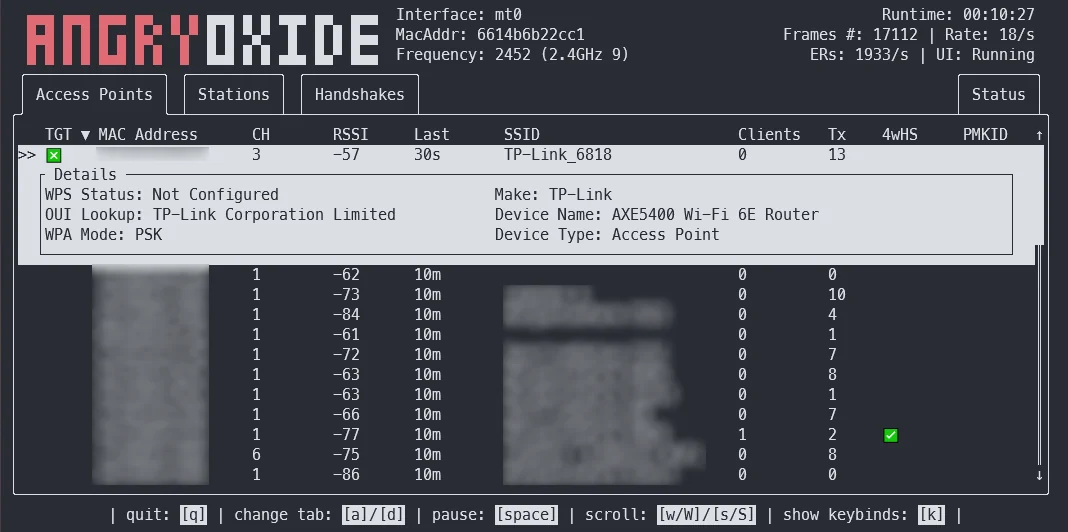
AngryOxide
 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
exploitationinformation-gatheringpacket-sniffing-analysis+5
2.0k
ragnt/angryoxideOffensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
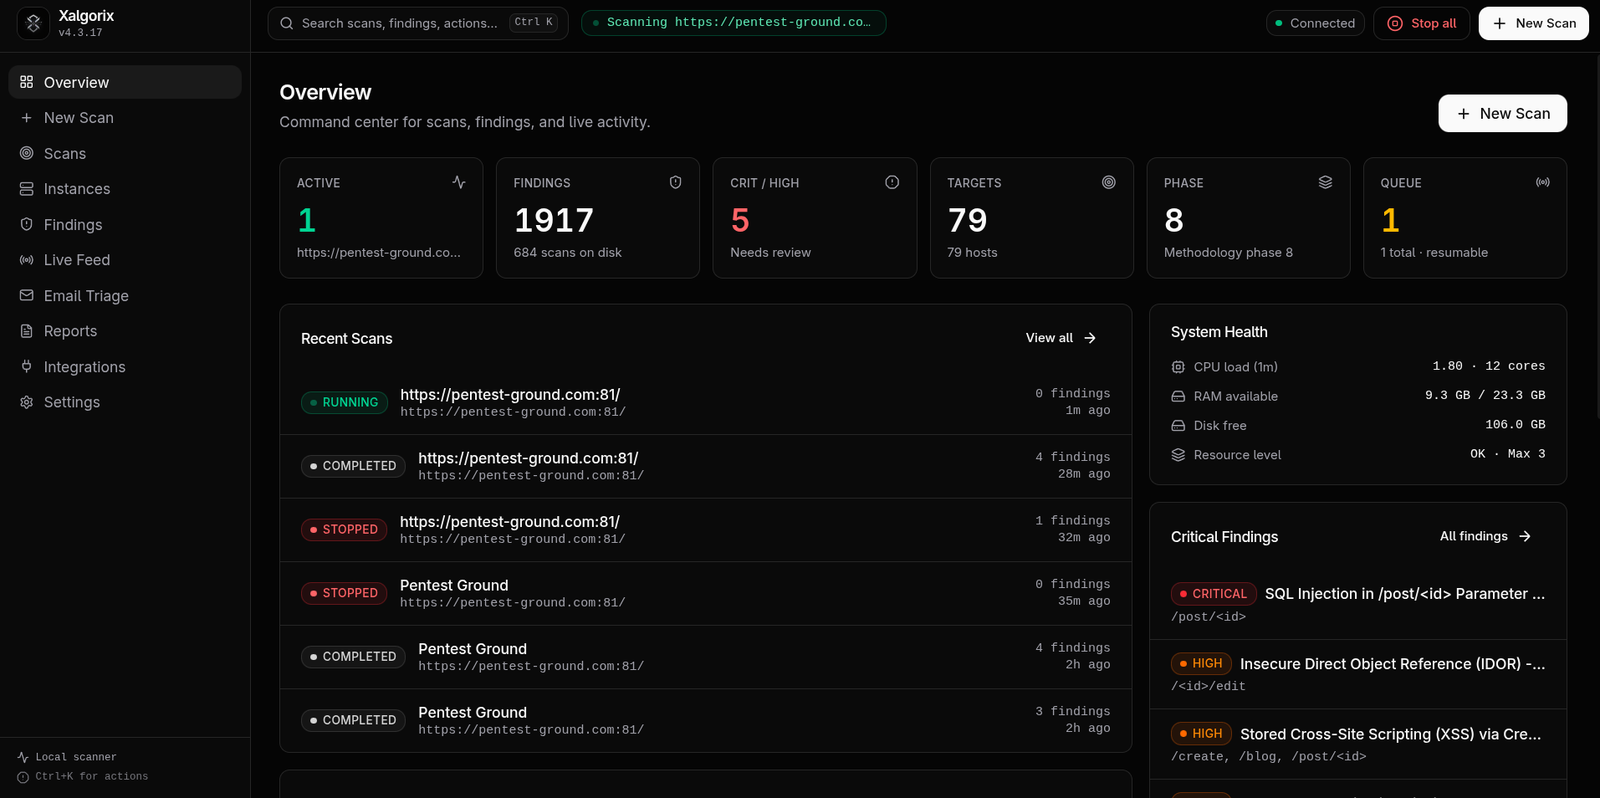 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 g0h4n/rusthound-ce
Active Directory data ingestor via LDAP(S) or ADWS protocol for BloodHound Community Edition written in Rust. 🦀
 specterops/bloodhound
Six Degrees of Domain Admin
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 specterops/nemesis
Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
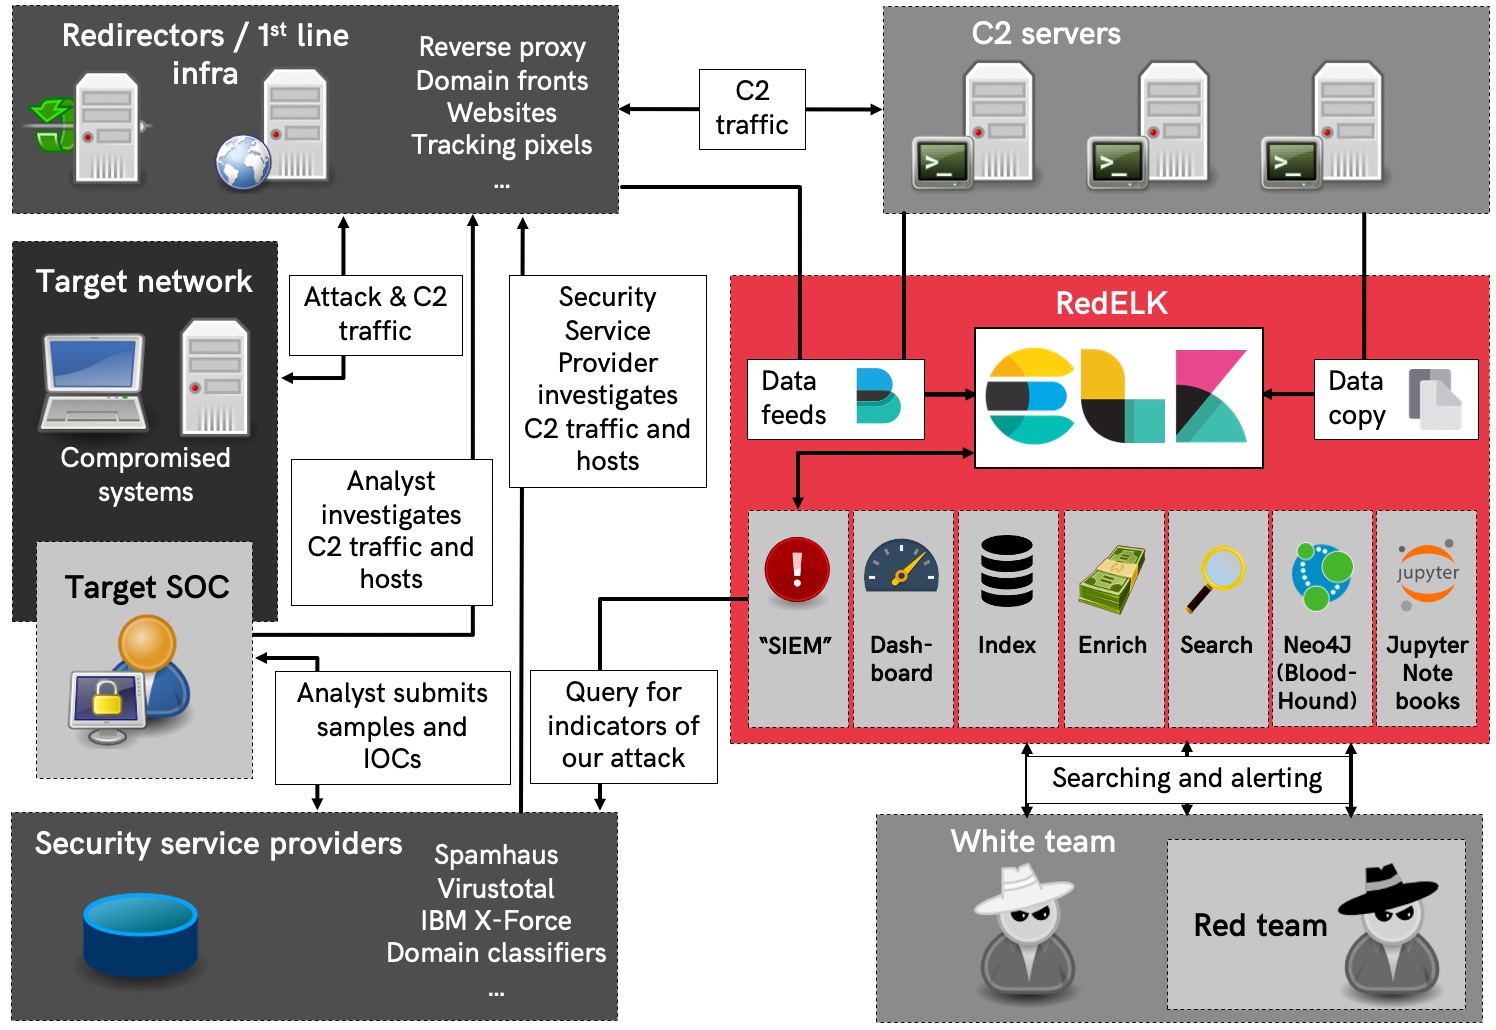 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
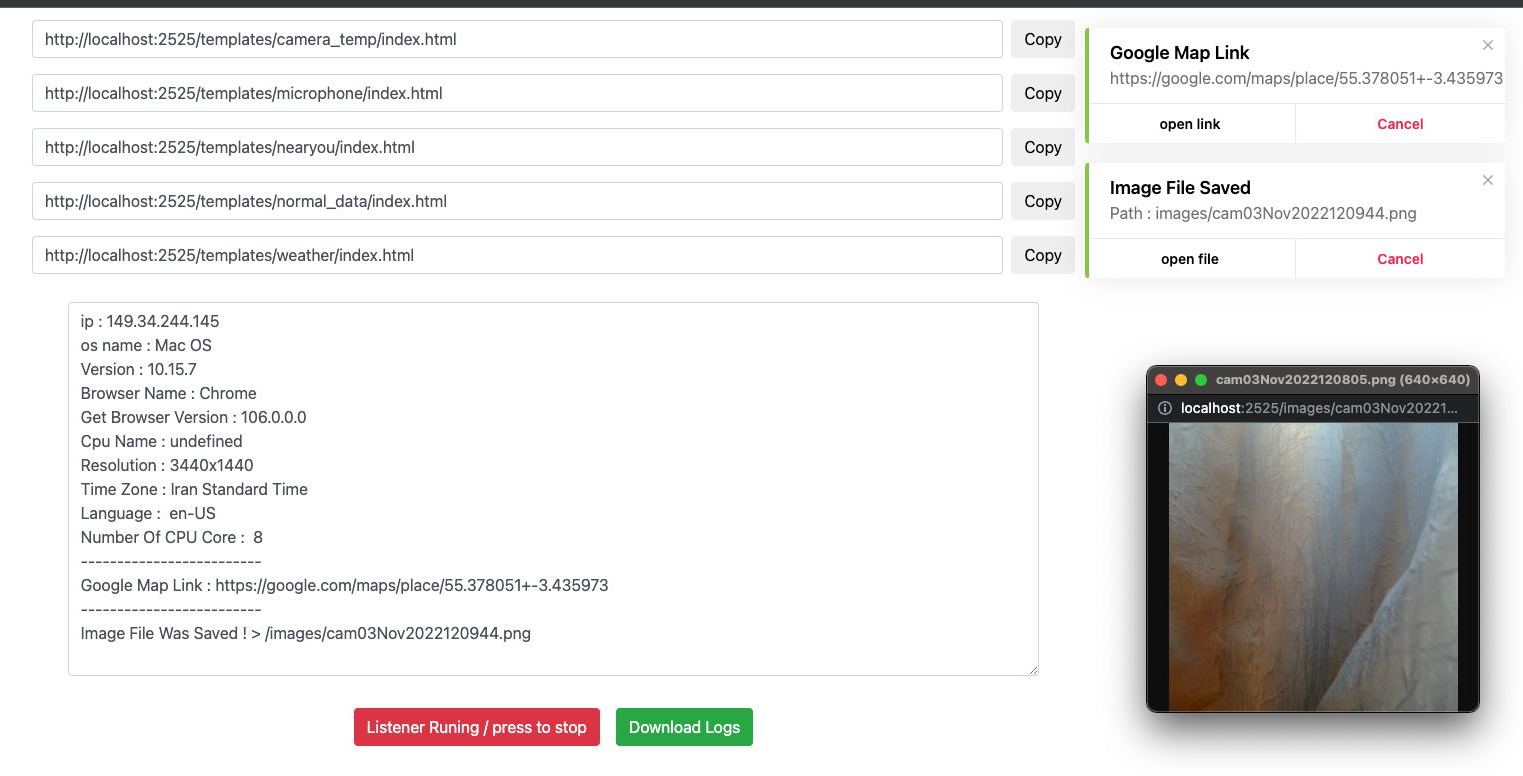 ultrasecurity/storm-breaker
Full-featured Social Engineering Framework with Page Cloning, MITM Proxy, Credential Capture, Session Extraction, and Real-time Monitoring.
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
 garrettfoster13/pre2k
A tool to query for the existence of pre-windows 2000 computer objects.
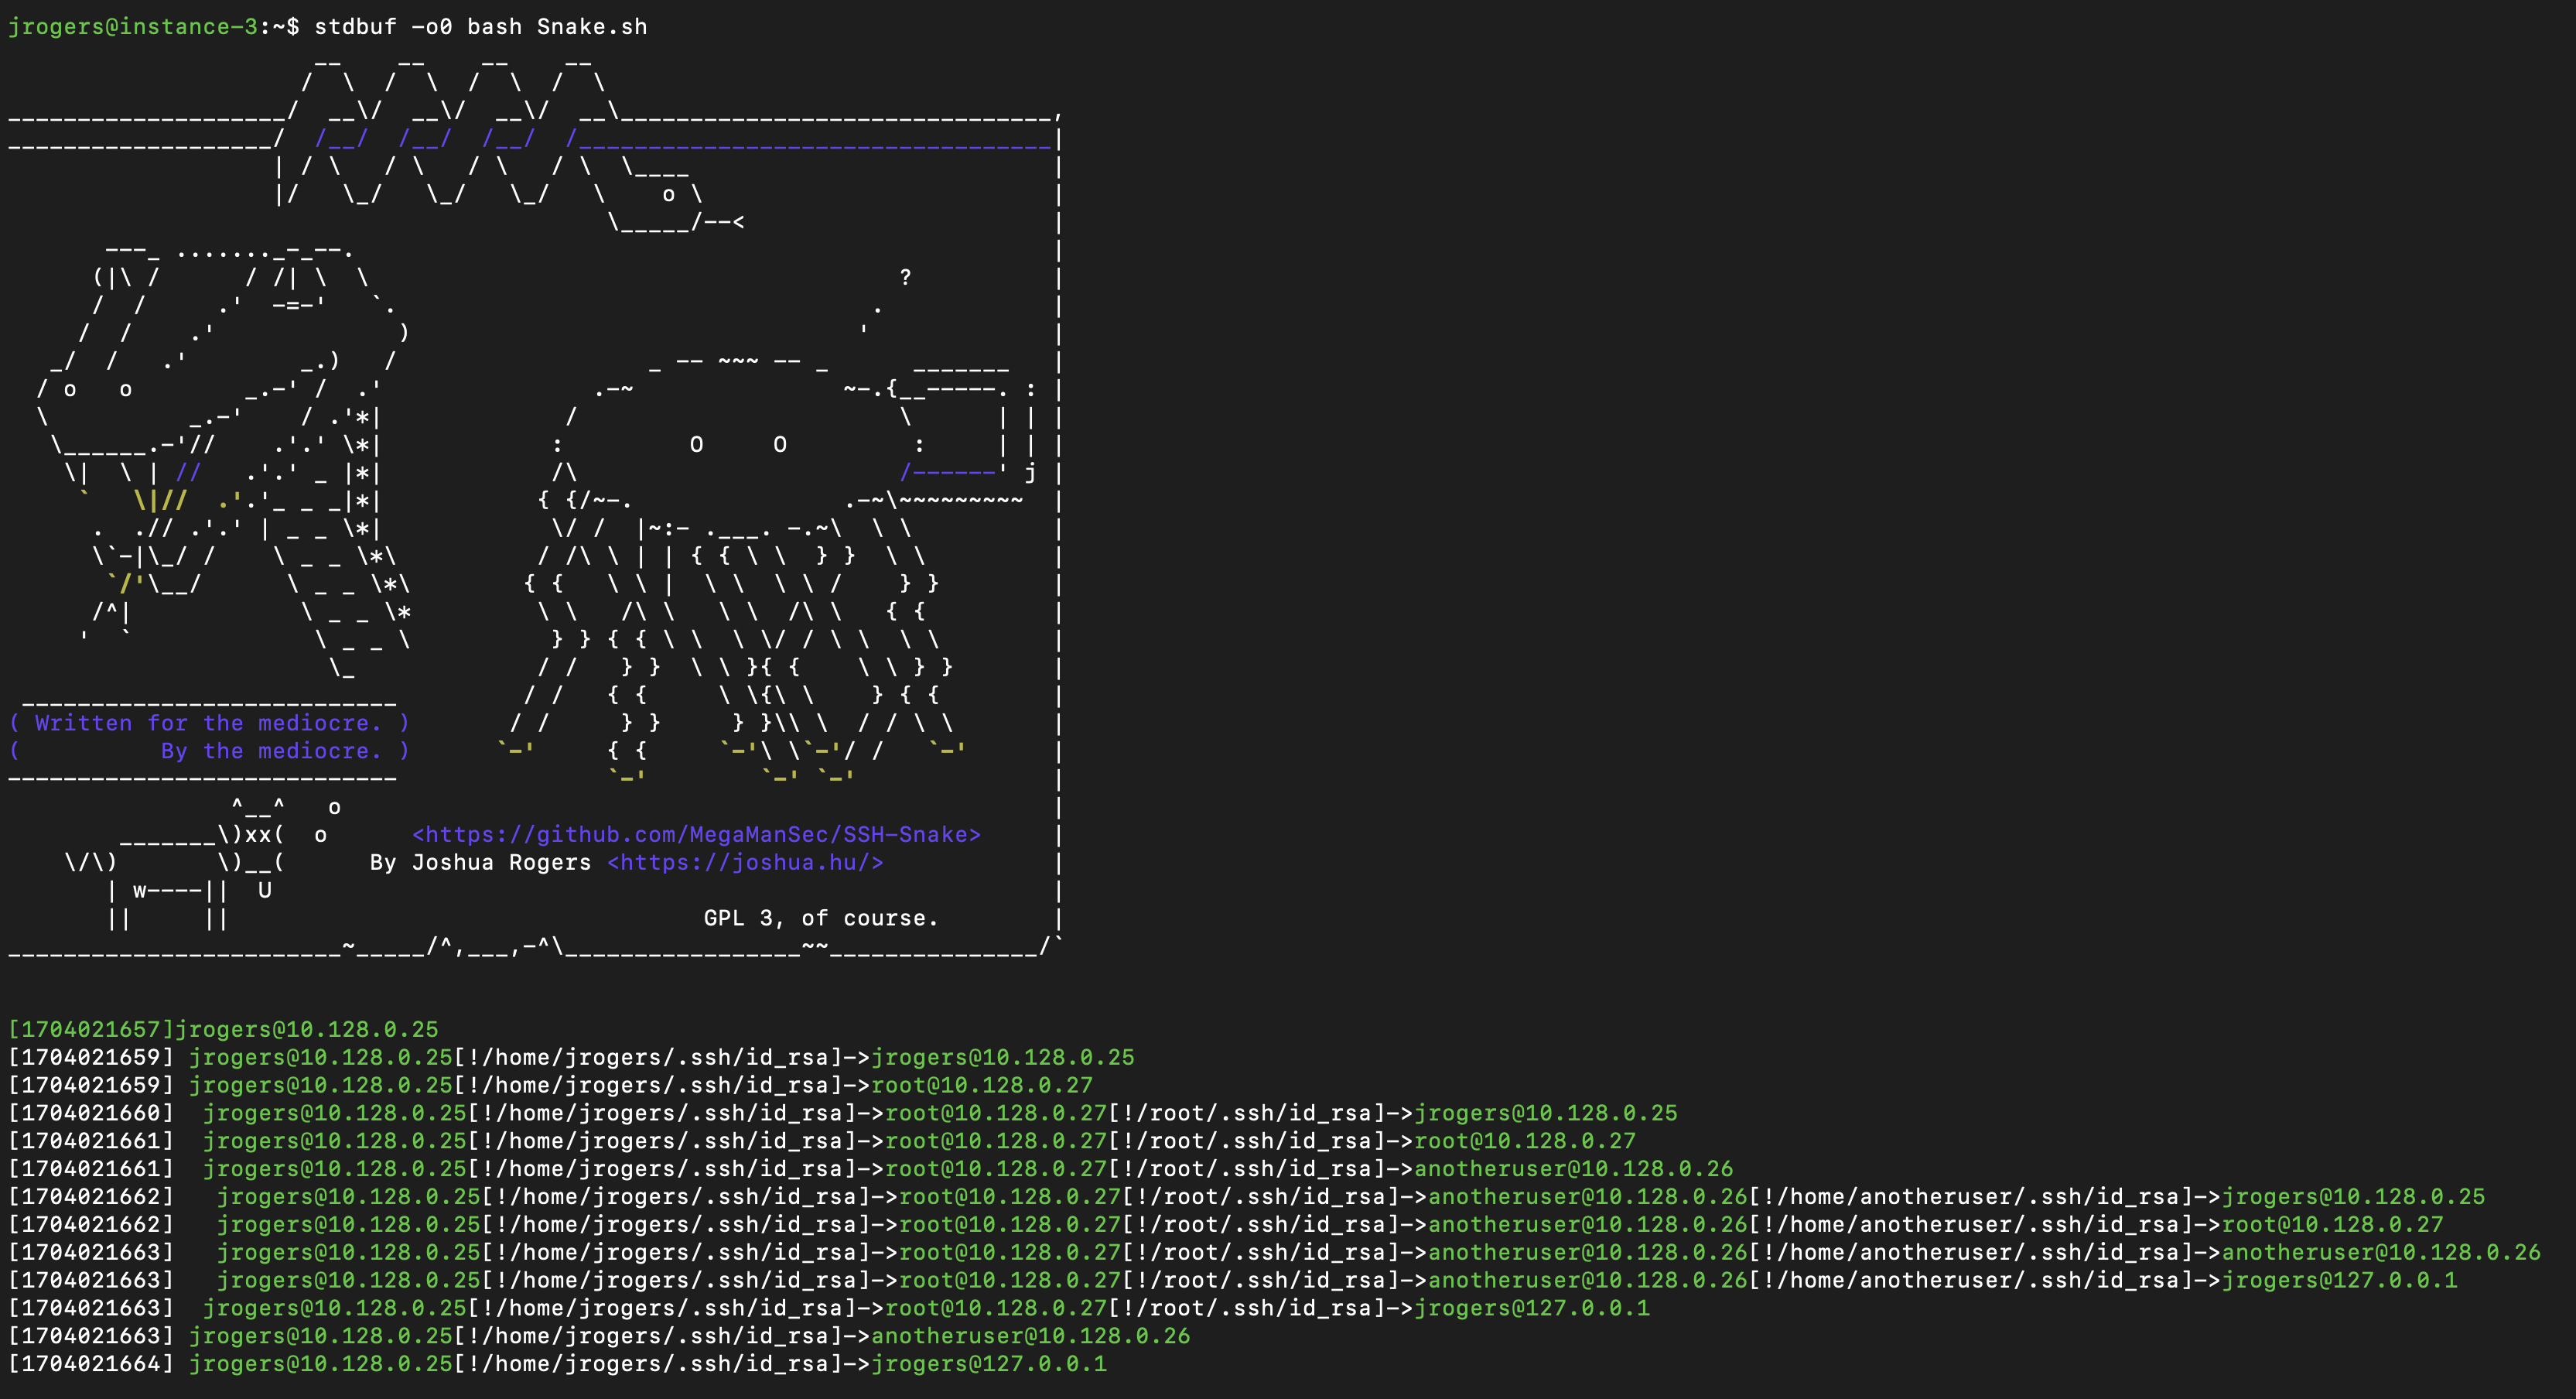 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.

 yukibtc/redknife
A Swiss Army knife for offensive security.
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 vampsecure-labs/vamp-forticheck
VampSecure Labs: FortiOS CVE scanner (CVE-2018-13379, CVE-2022-40684, CVE-2023-27997, CVE-2024-21762)
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.