
umbra
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
exploitationmemory-forensicsred-teaming+1
18
ymsniper/umbraExternal read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 robertmotr/zirconium
DLL-injectable internal game cheat for Plutonium BO2 zombies
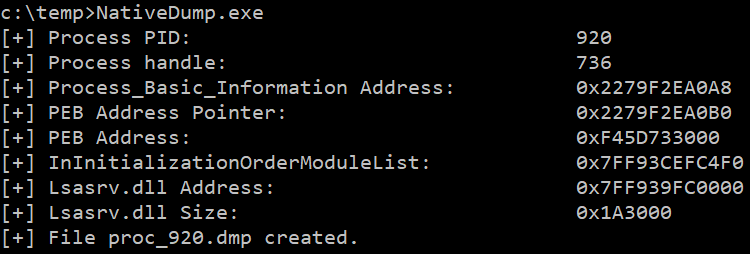 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
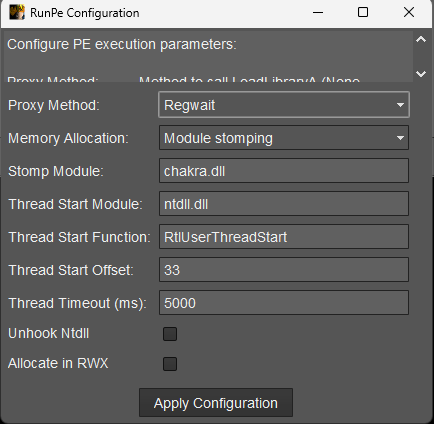 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 fortra/nanodump
The swiss army knife of LSASS dumping
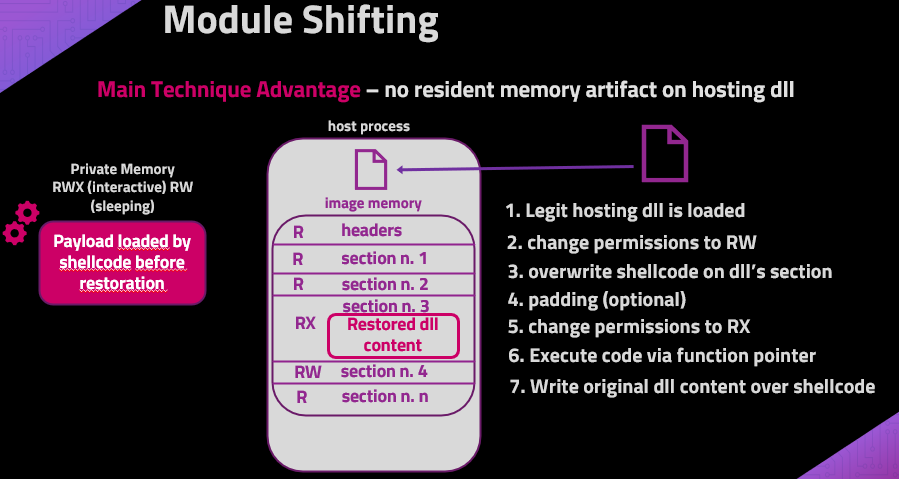 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
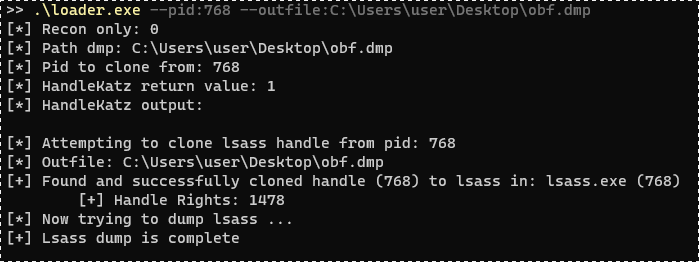 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 withsecurelabs/dotnet-gargoyle
A spiritual .NET equivalent to the Gargoyle memory scanning evasion technique
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…