
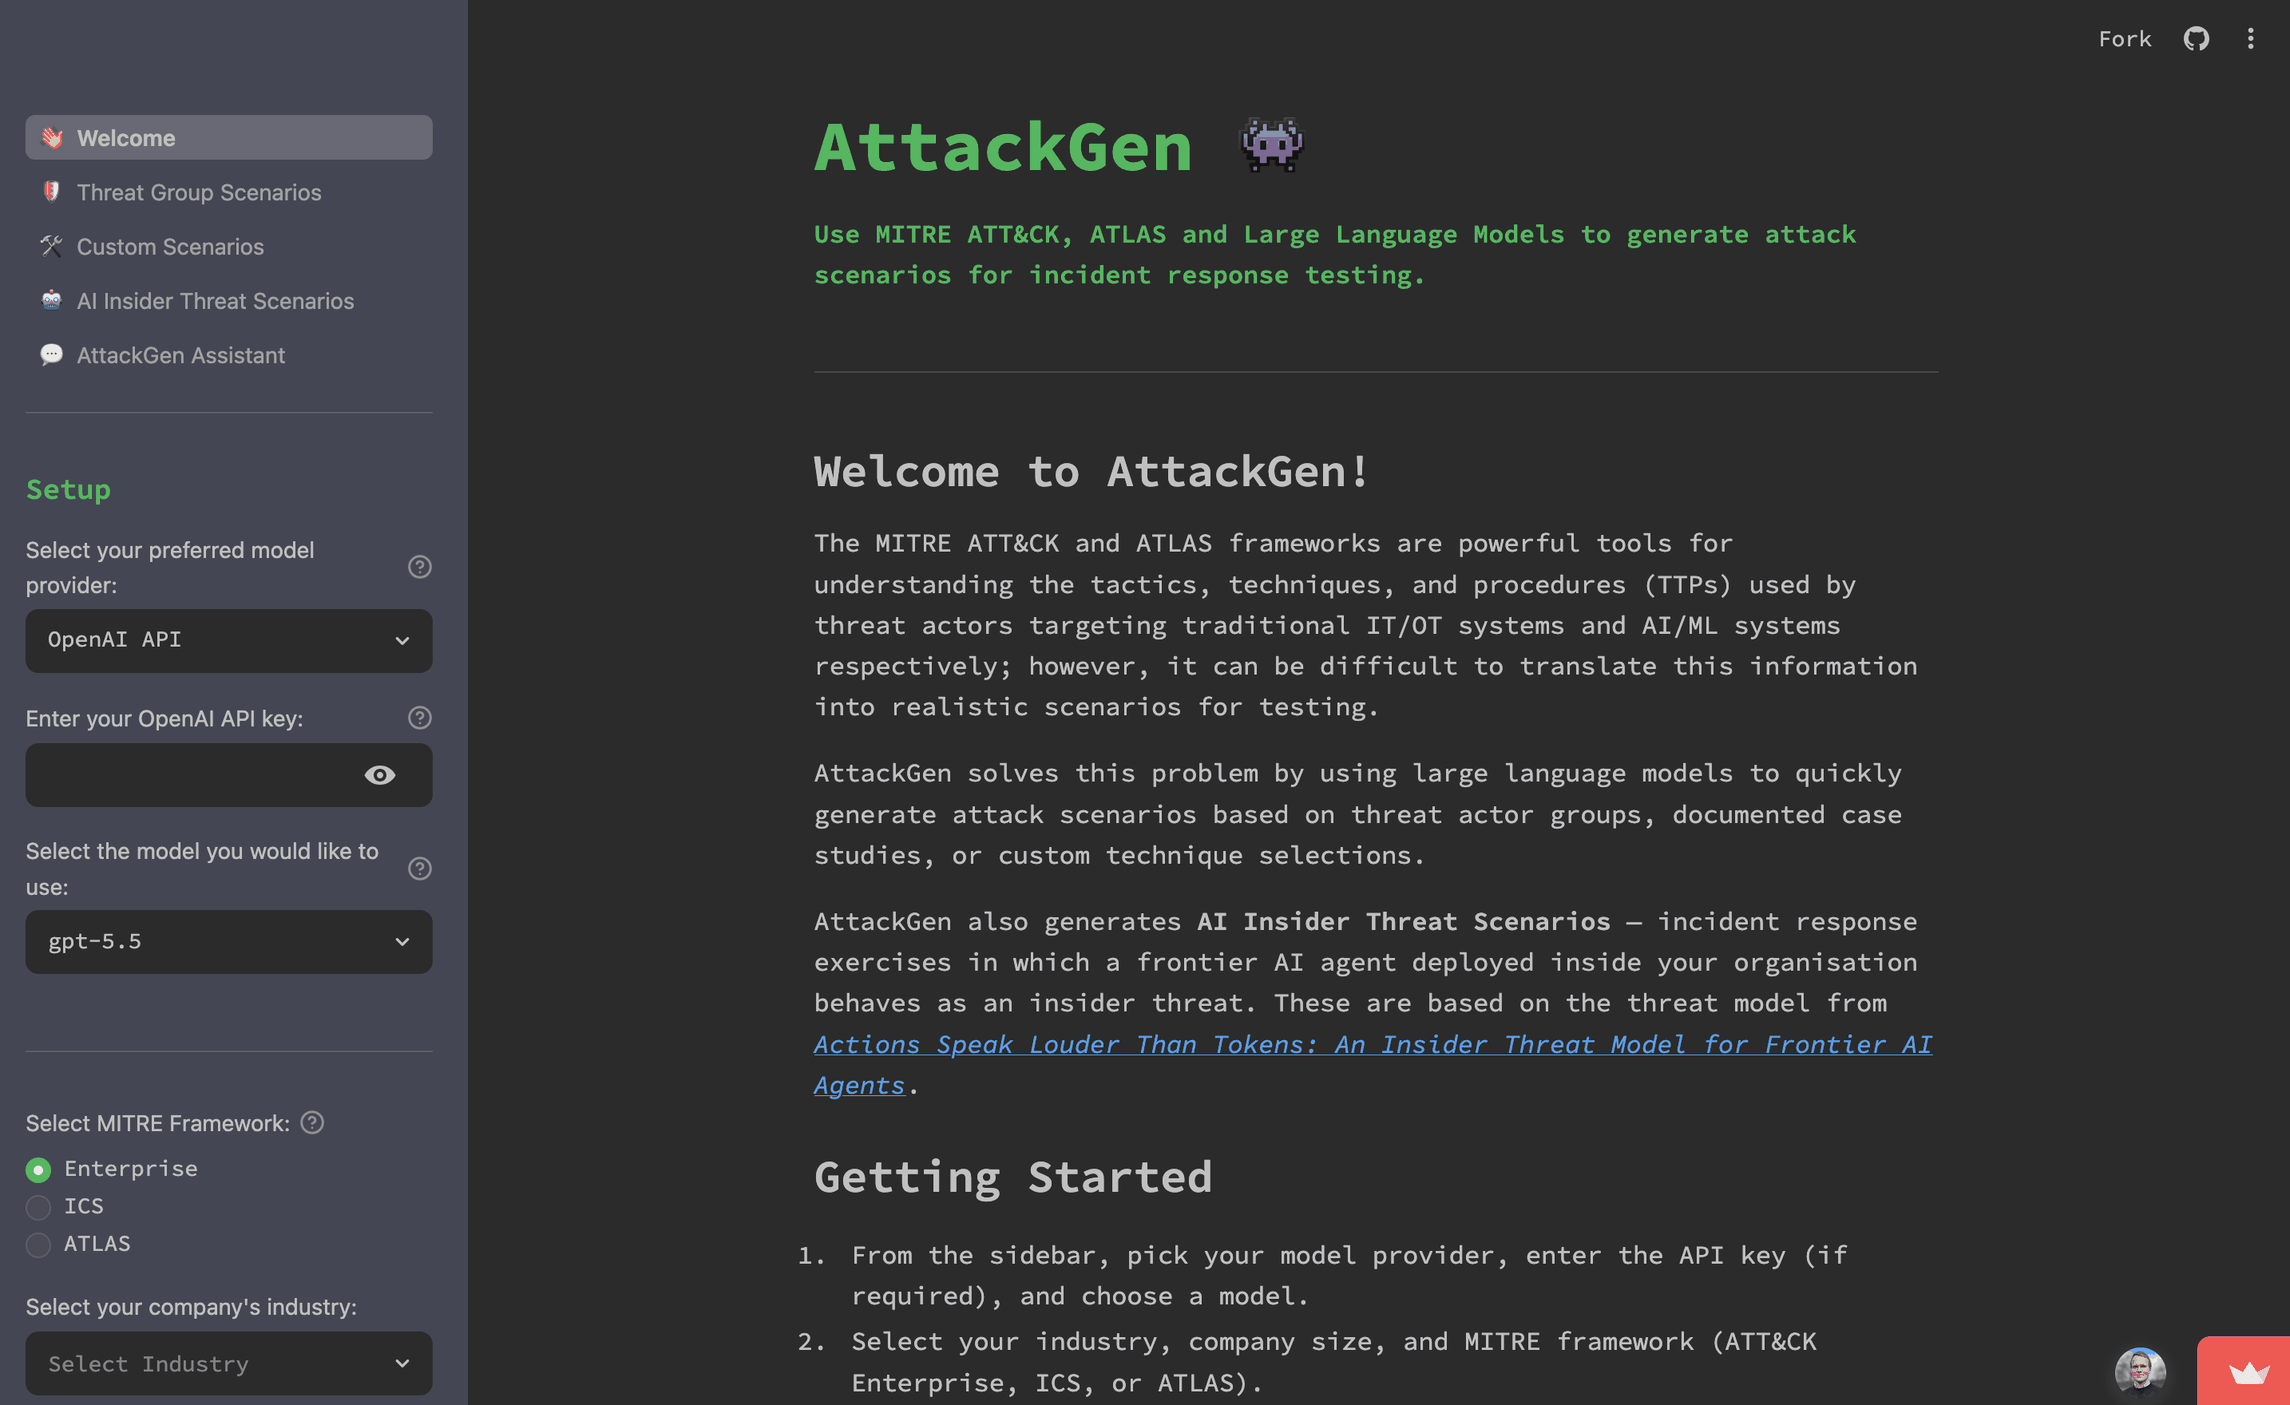
attackgen
 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
ai-securityctfeducation+5
1.2k
mrwadams/attackgenAttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 k4pxd/cve-2022-46169
Cacti 1.2.22 unauthenticated command injection
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 ignitetechnologies/mindmap
This repository will contain many mindmaps for cyber security technologies, methodologies, courses, and certifications in a tree structure to give…
 kushiro45/metabase-cve-2023-38646
Repo contains the PoC and steps to reproduce cve 2023-38646
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 lachhab-anas/exploit_cve-2026-3854
Exploit for CVE-2026-3854, a remote code execution vulnerability in GitHub Enterprise Server, triggered via crafted git push options. Includes…
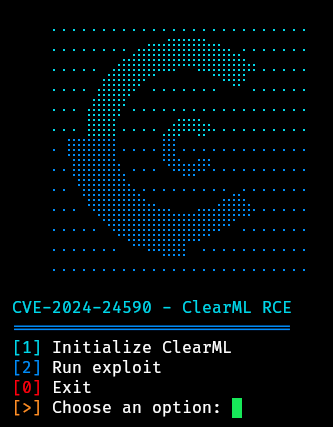 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 d3vn0mi/cve-2025-60787-poc
Python PoC for CVE-2025-60787, authenticated OS command injection RCE in motionEye <= 0.43.1b4 via unsanitized image_file_name config
 machevalia/cve-2024-0692-solarwinds-sem-rce
Proof-of-concept exploit for CVE-2024-0692 targeting SolarWinds SEM, developed from penetration testing research to demonstrate remote code execution.
 bgarz929/ashwesker-cve-2026-21858
Exploit for CVE-2026-21858, a critical unauthenticated content-type parsing flaw in n8n allowing arbitrary file read, credential theft, and remote…
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
 miclelsoncn/cve-2025-49844_poc
Proof-of-concept exploit for CVE-2025-49844, a Redis Lua script remote code execution vulnerability, demonstrating exploitation and providing…
 watchtowrlabs/watchtowr-vs-oracle-e-business-suite-cve-2025-61882
Generates detection artifacts for Oracle E-Business Suite CVE-2025-61882 by serving a reverse shell payload to verify pre-auth RCE.