
afrog
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
penetration-testingred-teamingvulnerability-scanners+1
zan8in/afrogA Security Tool for Bug Bounty, Pentest and Red Teaming.
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 berylliumsec/nebula
AI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
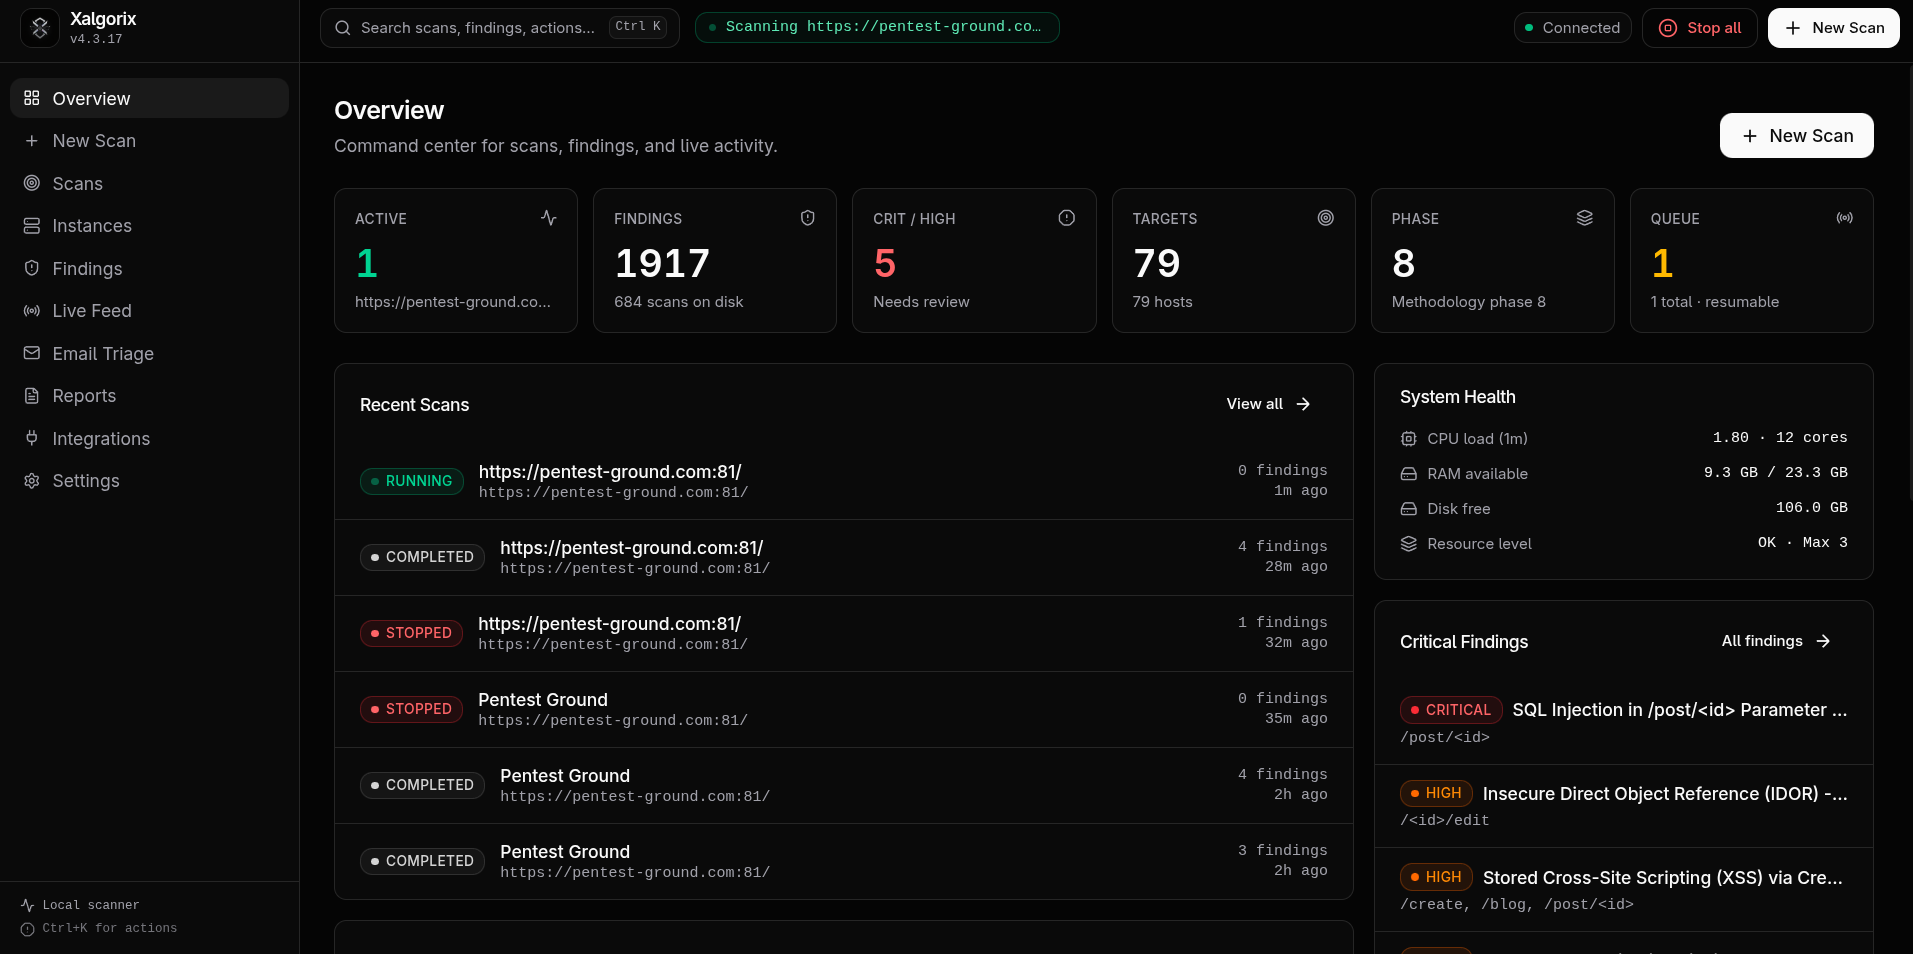 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 elementalsouls/claude-bughunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 mandiant/vulnerability-disclosures
Curated repository of vulnerability disclosures from Mandiant, including CVEs discovered through internal research, red team assessments, and wild…
 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
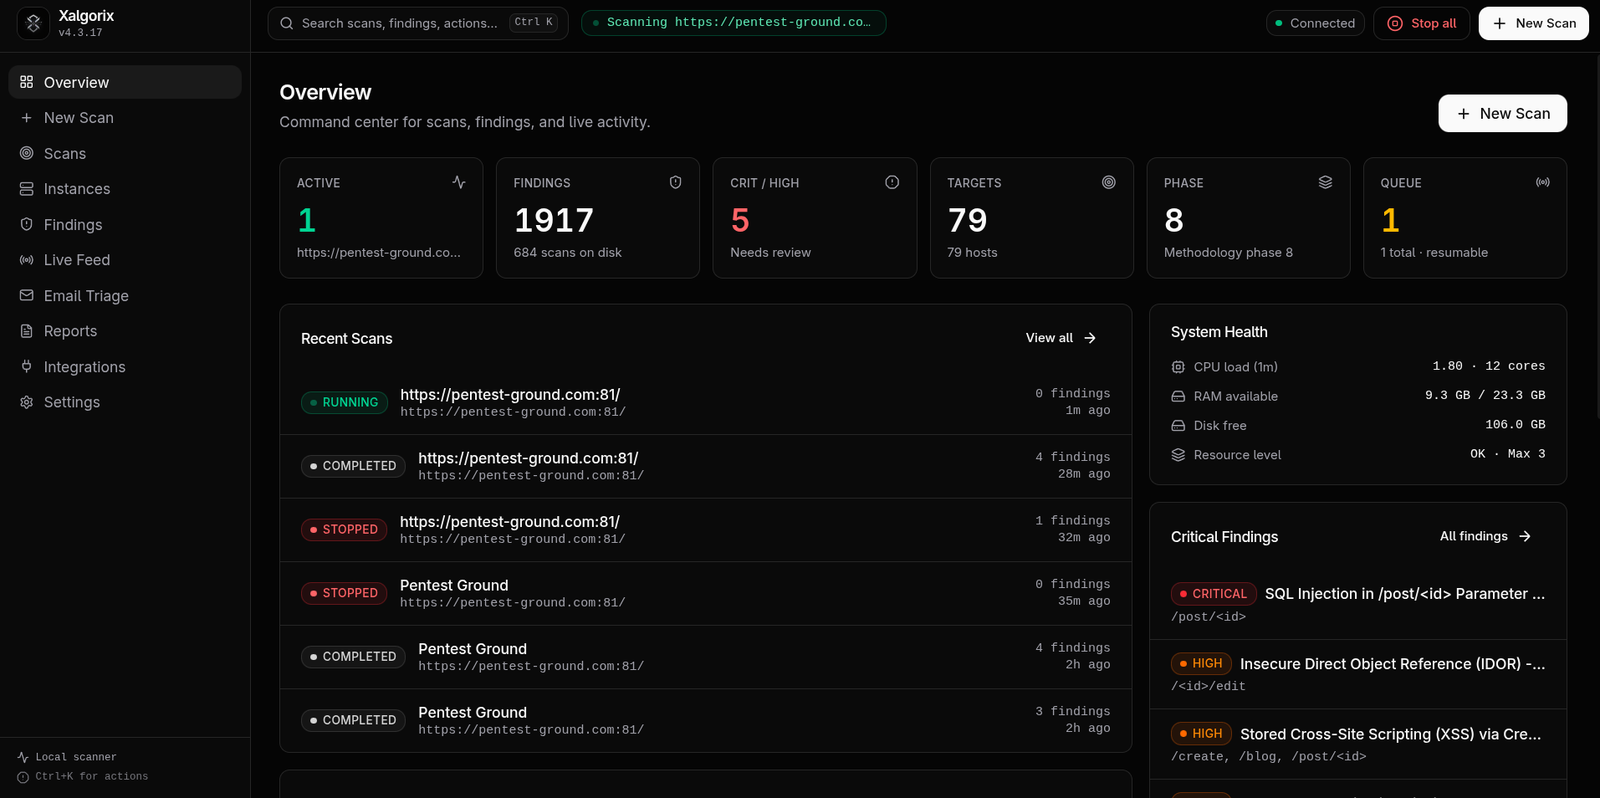 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
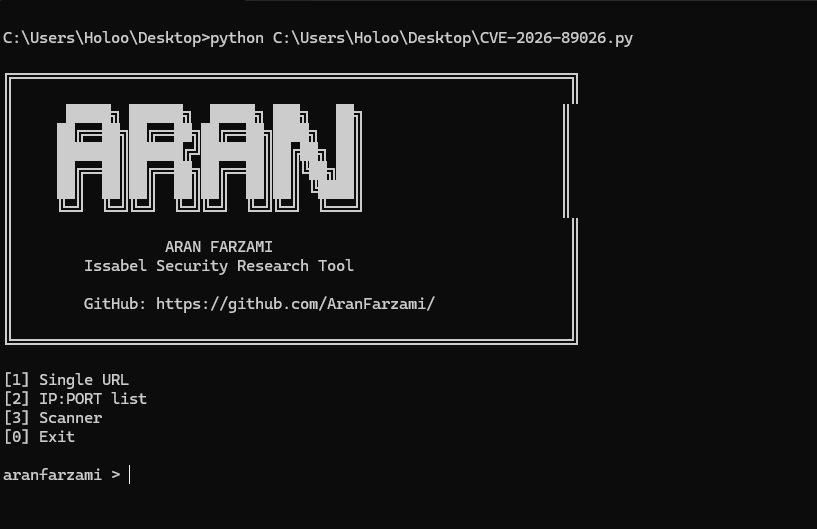 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.