

qyvora-toha3ee
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
exploitationnetwork-securityosint+9
5
qyvora/qyvora-toha3eeGo-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 kentox493/cve-2026-46300_fragnesia
Linux kernel local privilege escalation exploit with automated prerequisite audit for CVE-2026-46300, validating patch status, XFRM ESP-in-TCP…
 1xpwn/cve-2025-32463
This CVE addresses a vulnerability in sudo versions 1.9.14 to 1.9.17, enabling unauthorized local privilege escalation to root access.
 safebreach-labs/forgottenbutnotgone
proof-of-concept scripts for 2 unauthenticated RCEs in Samba (CVE-2026-4408 & CVE-2026-4480) and local privilege escalation in TelnetD…
 lsecqt/portforwarder
TCP Port Forwarding Utility on C
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 n00py/outpacket
This cheatsheet maps common impacket workflows to their modern alternatives
 ryan2929/cve-2026-31431
Public exploit for a Linux kernel zero-day (CVE-2026-31431) enabling local privilege escalation to root on distributions since 2017. Includes a…
 gtfobins/gtfobins.github.io
GTFOBins is a curated list of Unix-like executables that can be used to bypass local security restrictions in misconfigured systems.
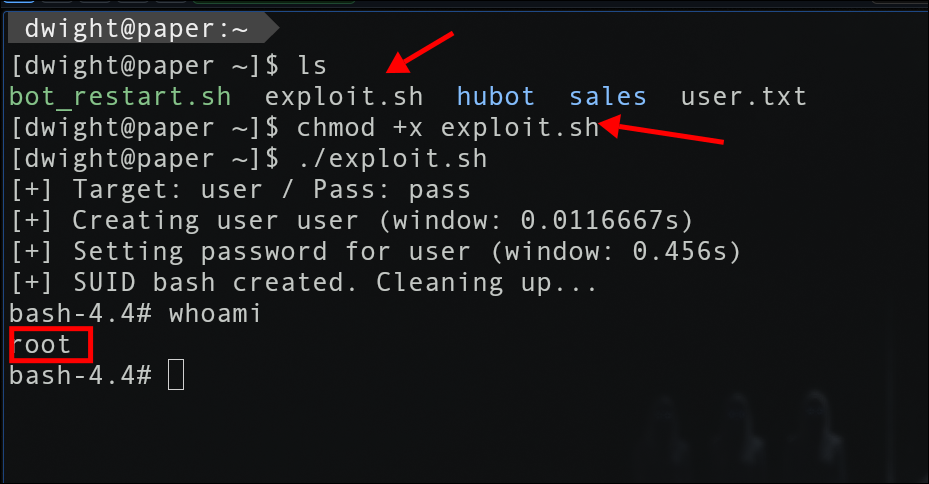 jeanback1/cve-2021-3560-exploit
CVE-2021-3560 — Polkit privilege escalation exploit via accounts-daemon D-Bus race condition
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 razvanduda/ghostshell
CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption
 mfloresdacunha/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431 in Linux kernel's algif_aead, using splice to overwrite page cache and gain root. Includes a…
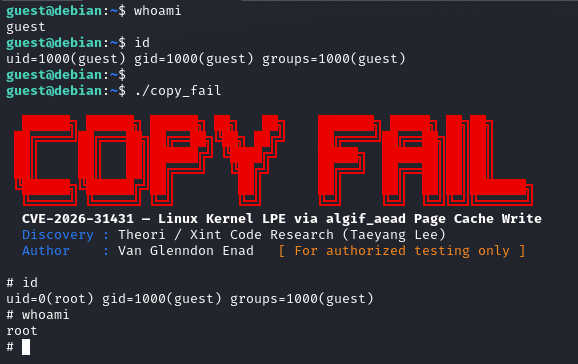 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…