SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…

Stored XSS in Nagios Log Server 2024R1.3.1

Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…

JavaScript for Automation (JXA) macOS agent

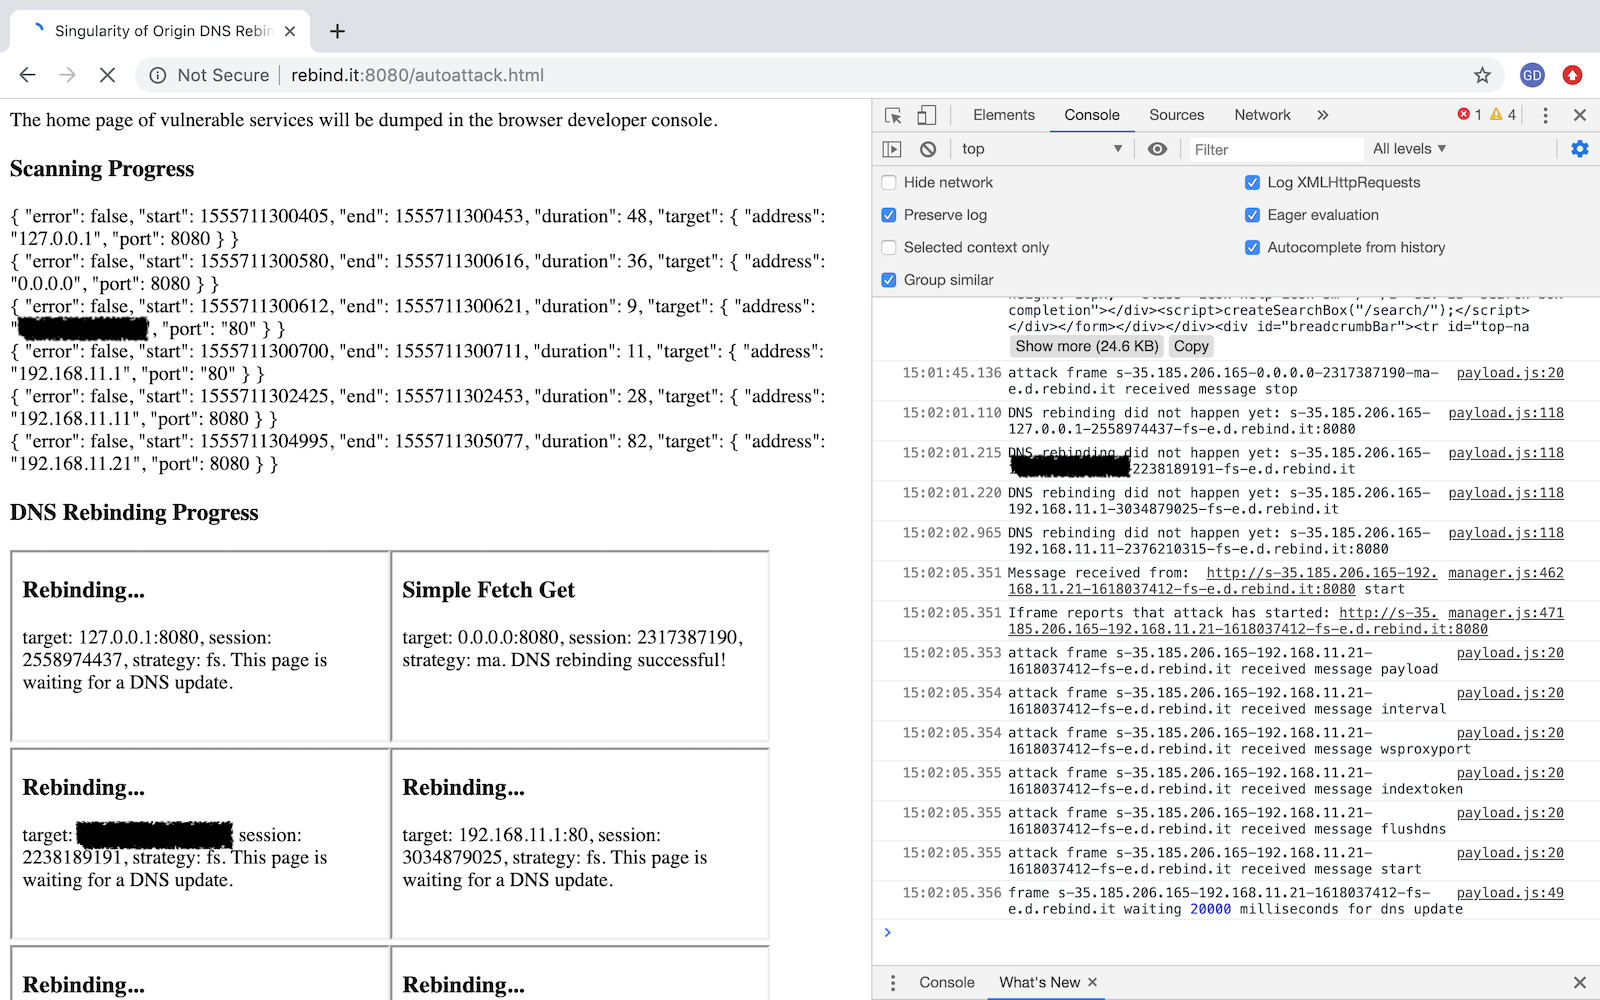
A DNS rebinding attack framework.

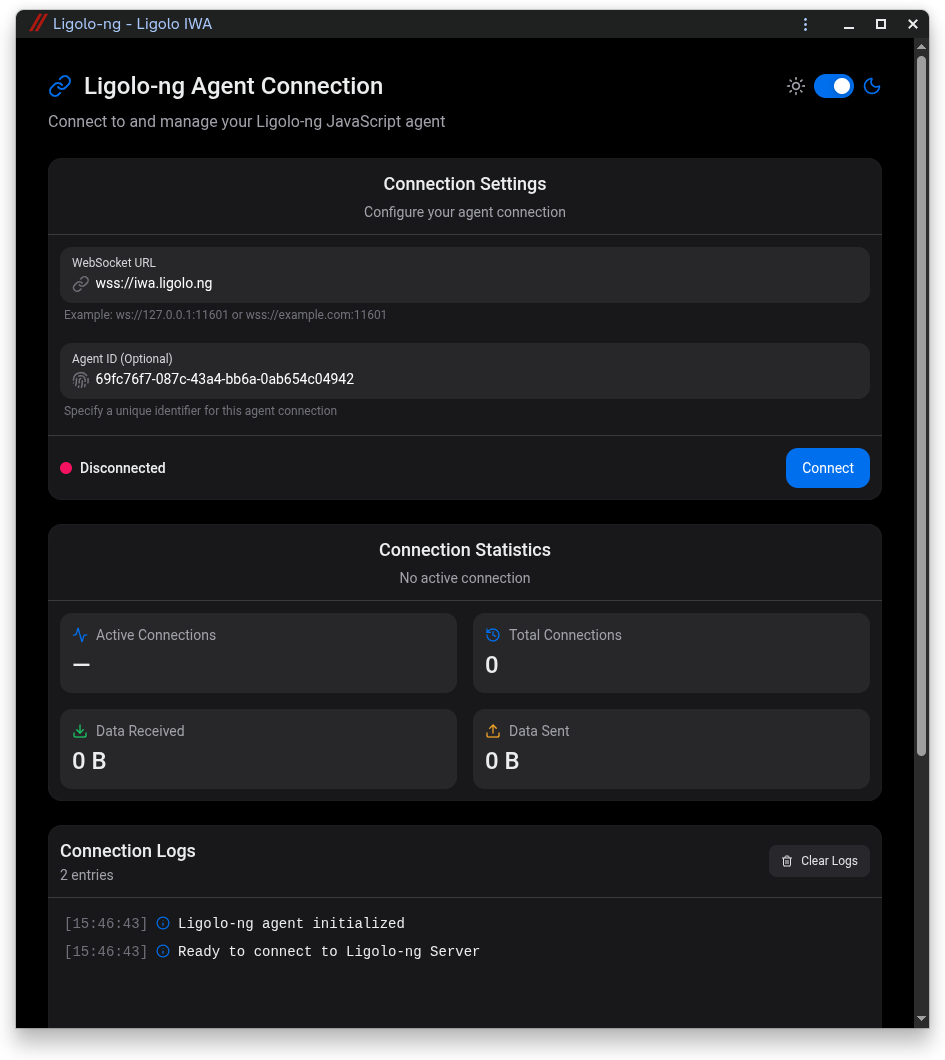
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.

Proof-of-concept exploit for CVE-2026-27574, a critical code injection in OneUptime enabling remote code execution and environment variable leakage.

Generates and delivers exploit payloads for CVE-2026-23830, a SandboxJS escape, with modes for blind OOB exfiltration and local calc PoC. Supports…

Exploit for Apache Solr CVE-2026-22444, leveraging UNC path injection and SMB server to achieve remote code execution via malicious configset and…

API, CLI, and Web App for analyzing and finding a person's profile in 1000 social media \ websites

Serverless AITM Simulation Framework for Entra ID and M365

Node.js reverse shell payload generator for penetration testing. Creates bind and reverse shells in JavaScript.

a lightweight JavaScript snippet showcasing how unauthorized password changes can be triggered on vulnerable Fortinet FortiSwitch GUI endpoints.

Exploit for CVE-2024-21683, a post-authentication remote code execution vulnerability in Atlassian Confluence Server and Data Center, allowing…

The BerqWP – Automated All-In-One PageSpeed Optimization Plugin for Core Web Vitals, Cache, CDN, Images, CSS, and JavaScript plugin for WordPress is…

CVE-2023-22621: SSTI to RCE by Exploiting Email Templates affecting Strapi Versions <=4.5.5

This script exploits a vulnerability (XSS) in the TPLink WR840N router, using a field for injecting javascript code.