CVE-2025-6325_CVE-2025-6327

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…

Unauthenticated arbitrary file upload -> RCE in WPLP Cookie Consent (gdpr-cookie-consent) <= 4.4.1 - technical write-up and PoC

Proof-of-concept for CVE-2026-78839, an arbitrary file upload vulnerability in AppNitro MachForm v30 allowing remote code execution via crafted .phar…

Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…

Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…

Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…

Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…

Python exploit for CVE-2026-21627, an unauthenticated arbitrary PHP file inclusion in Joomla's Novarain Framework, enabling file upload, delete, and…

Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…

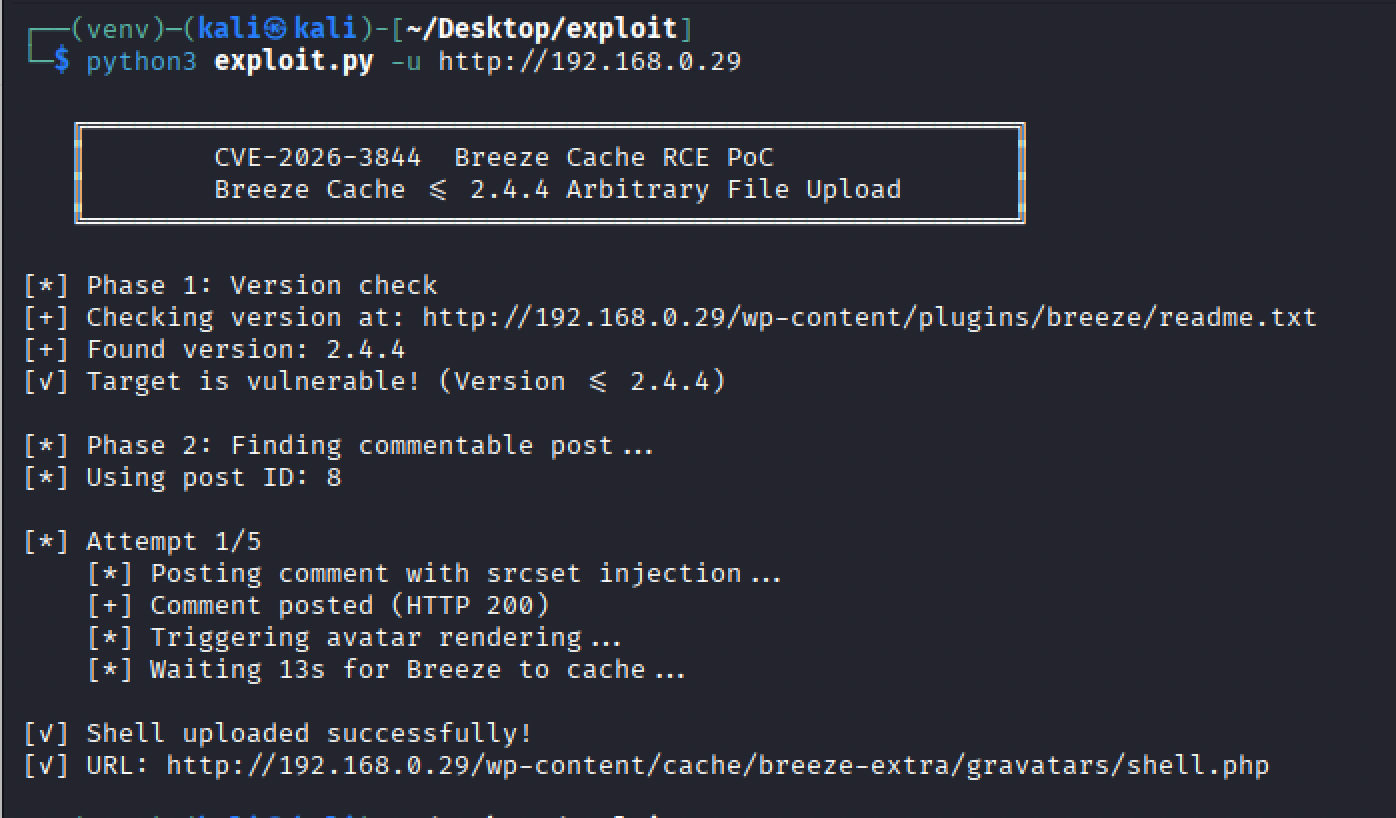
Breeze Cache WordPress <=2.4.4 allows unauthenticated file upload via fetch_gravatar_from_remote when local gravatar hosting is enabled.

Exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to RCE in Breeze Cache WordPress plugin. Includes lab setup, usage, and…

FacturaScripts RCE Exploit - Proof of Concept

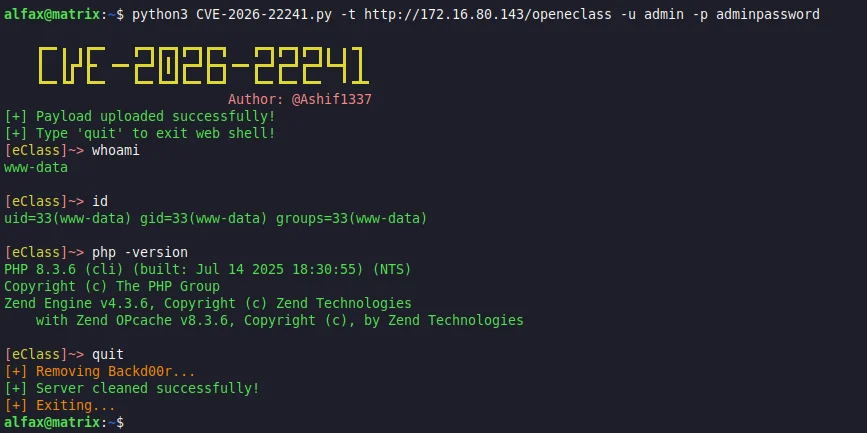
Automated exploit for CVE-2026-22241, an unrestricted file upload vulnerability in Open eClass, enabling remote code execution via a webshell with…

Forminator Forms <= 1.56.1 - Unauthenticated Arbitrary File Upload via Forged Upload Field Configuration

Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…

Unauthenticated arbitrary file upload exploit for Realtyna WPL/Organic IDX WordPress plugin, chains PHP webshell upload to RCE, with command…