

sliver-gui
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
cloud-securitycommand-and-controllateral-movement+7
181
sliverarmory/sliver-guiCross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 samybaiwir/dnslivery
Easy files and payloads delivery over DNS
 mbanyamer/cve-2026-27180-majordomo-unauthenticated-rce
Proof-of-concept exploit for CVE-2026-27180, an unauthenticated RCE in MajorDoMo via update URL poisoning, delivering a webshell to the web root.
 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 gmh5225/aether-c2-framework
🛠️ Explore custom C2 TTPs with Aether-C2-Framework, focusing on lightweight Rust implants and stealthy transport stacks to reduce forensic…
 virtualalllocex/payload-download-cradles
This are different types of download cradles which should be an inspiration to play and create new download cradles to bypass AV/EPP/EDR in context…
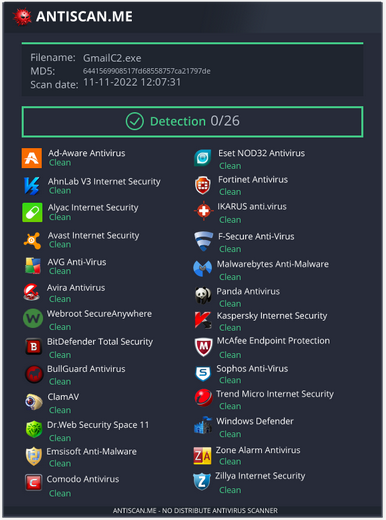 reveng007/sharpgmailc2
Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
 darksh3llru/dark-doh
Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
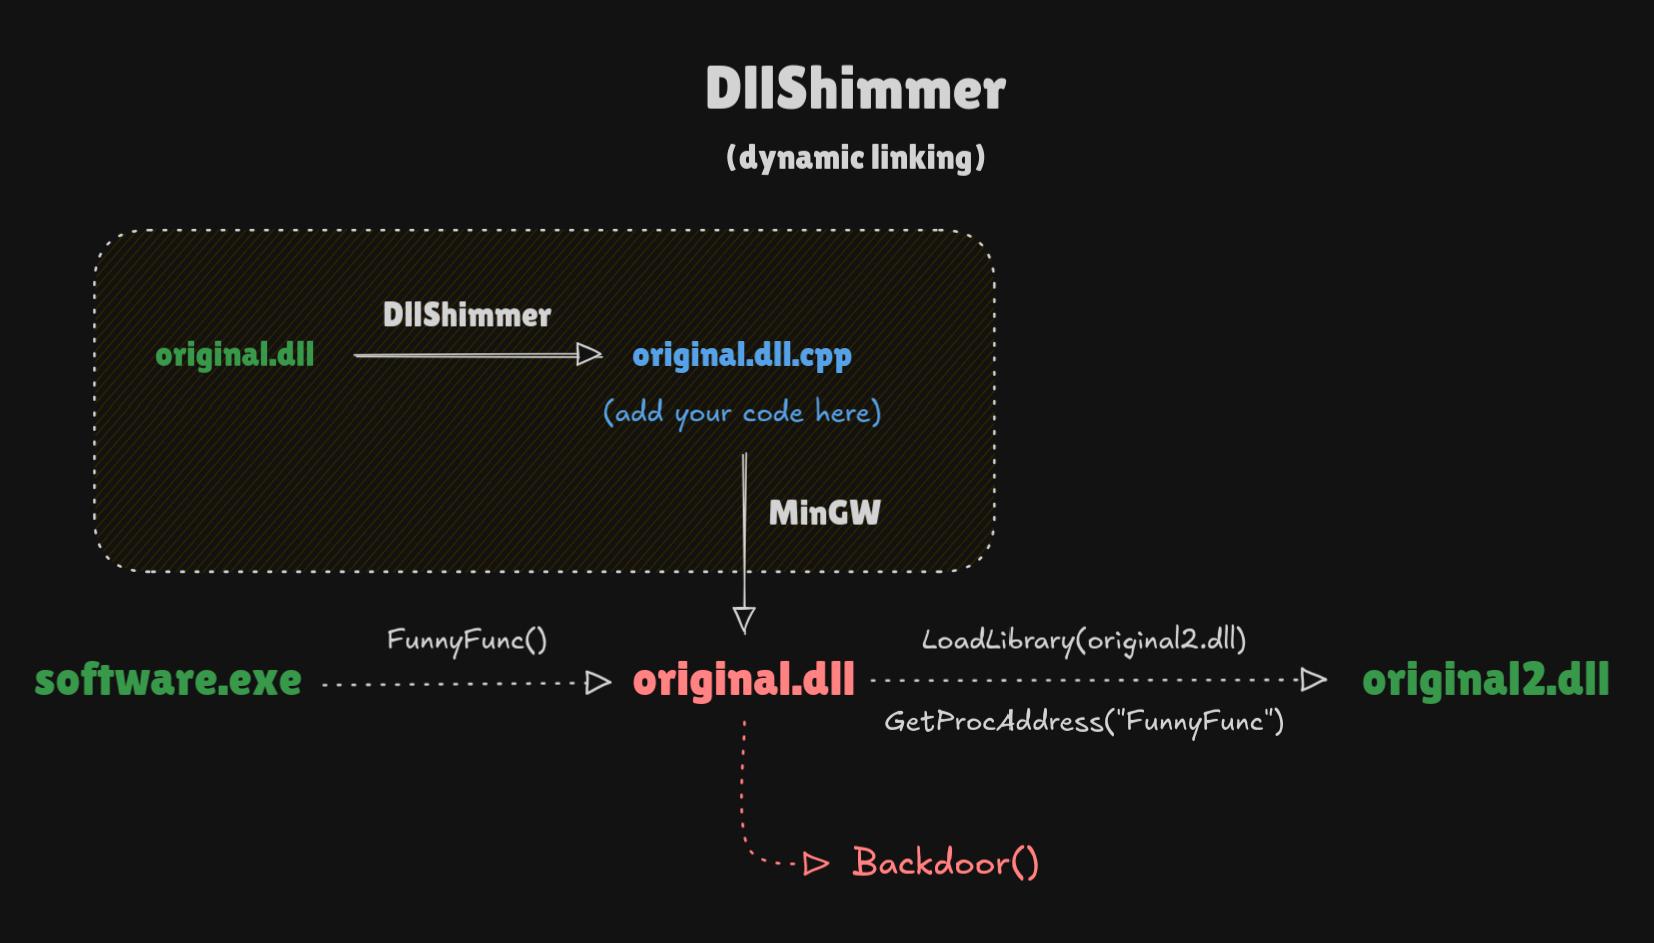 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
 freakazoidile/ms15-011-files
Repo that the MS15-011 exploit clones to get required files. Avoids having to download all files from exploit_dev.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 qusaialhaddad/f5-bigip-cve-2022-1388
Reverse Shell for CVE-2022-1388
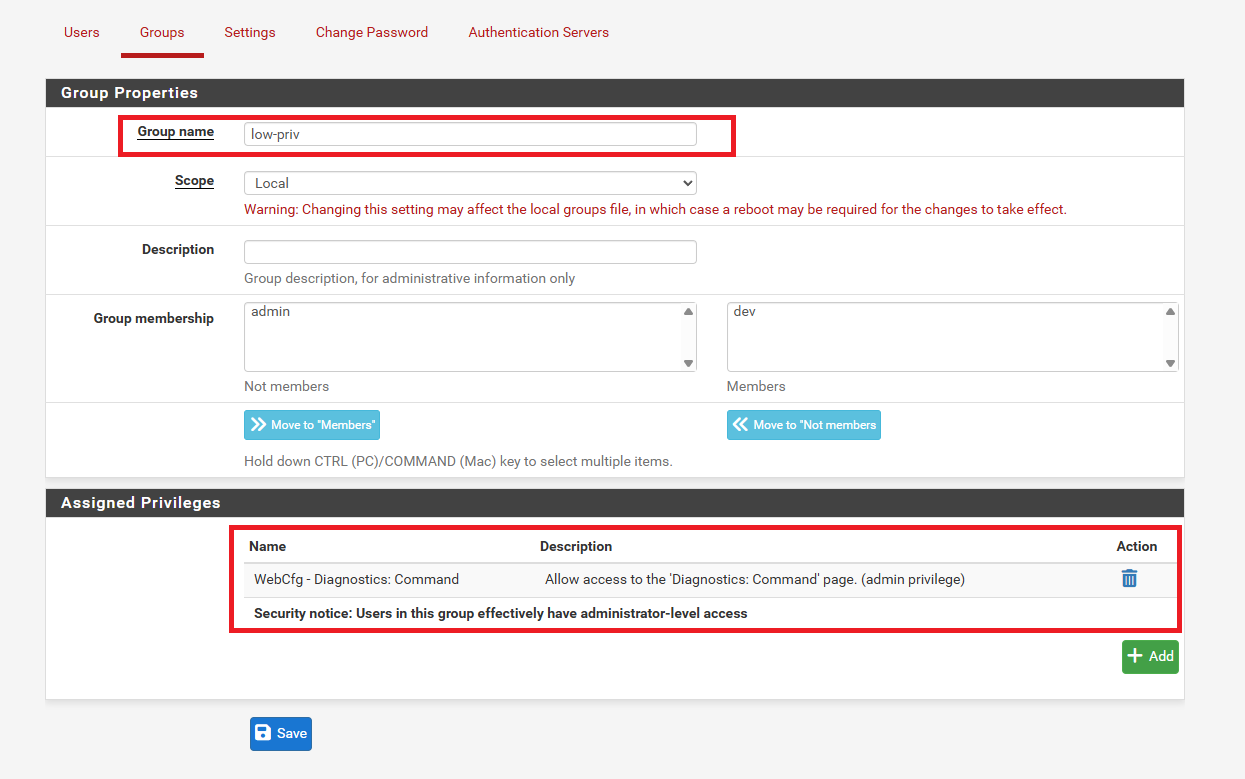 skraft9/pfsense-security-research
Authenticated Arbitrary File Read in pfSense 2.8.0 via Diagnostics Web Interface (CVE-2025-53392)
 watchtowrlabs/cve-2024-50623
Cleo Unrestricted file upload and download PoC (CVE-2024-50623)
 wa6n3r/cve-2024-3400
Multi-threaded exploit tool for CVE-2024-3400 in Palo Alto PAN-OS with automated artifact download and detailed logging for confirmed RCE.