
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
umbra preview

umbra

GitHubymsniper/umbra

External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
exploitationmemory-forensicsred-teaming+1
1825 days ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
exploitationmemory-forensicspayload-development+2
3.4k13 years ago
dotnet-gargoyle preview

dotnet-gargoyle

GitHubwithsecurelabs/dotnet-gargoyle

A spiritual .NET equivalent to the Gargoyle memory scanning evasion technique
malware-analysismemory-forensicsred-teaming
527 years ago
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

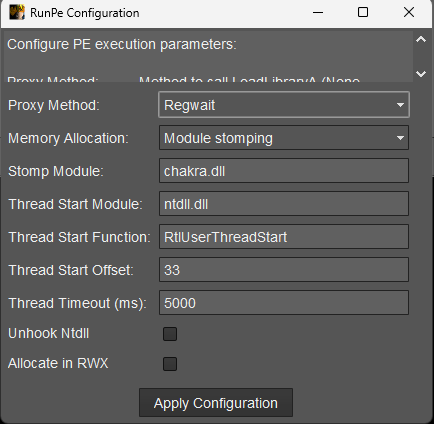
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
memory-forensicspassword-attackspost-exploitation+1
2182 years ago
BOF_RunPe preview

BOF_RunPe

GitHubntdallas/bof_runpe

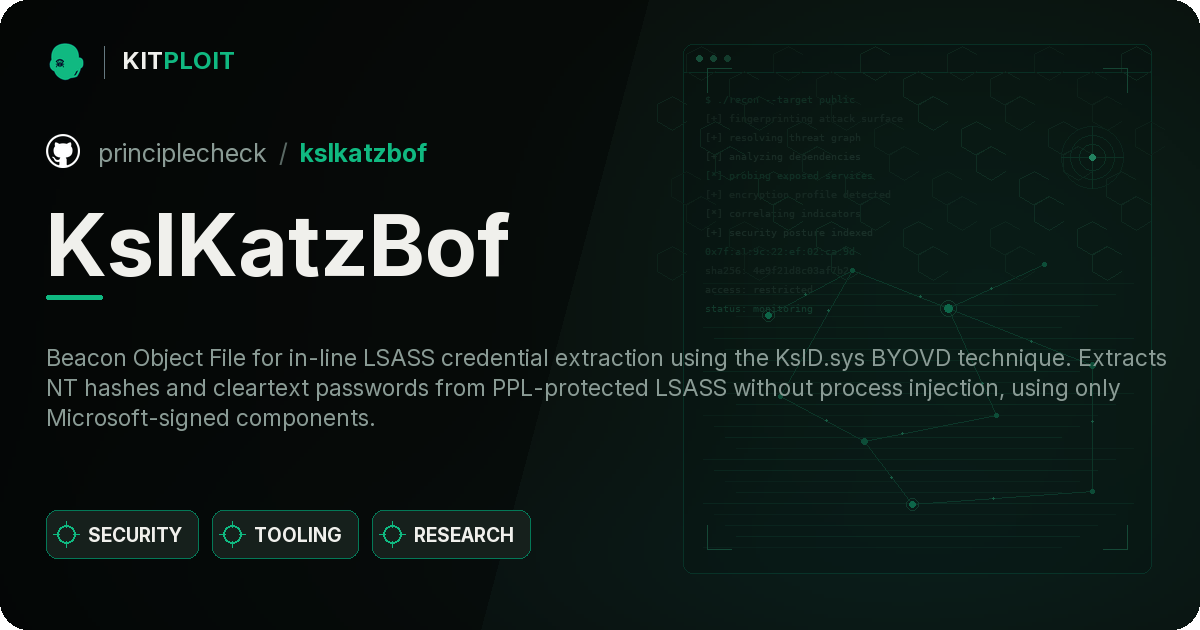
BOF to run PE in Cobalt Strike Beacon without console creation
memory-forensicspost-exploitationred-teaming+1
19811 months ago
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
exploitationmemory-forensicspayload-development+4
911 month ago
HandleKatz preview

HandleKatz

GitHubcodewhitesec/handlekatz

PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…

defensive-toolsmemory-forensicspayload-generation+3
5984 years ago
nanodump preview

nanodump

GitHubfortra/nanodump

The swiss army knife of LSASS dumping

exploitationmemory-forensicspayload-development+4
2.1k2 years ago
TrickDump preview

TrickDump

GitHubricardojoserf/trickdump

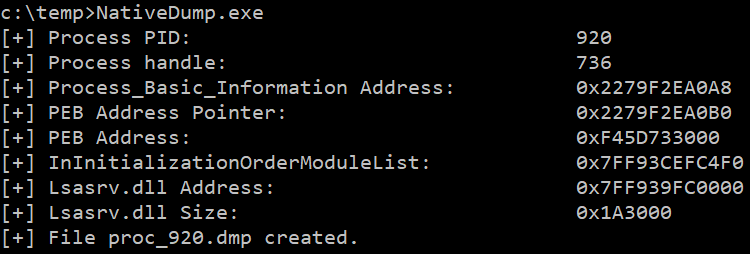
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
memory-forensicspost-exploitationred-teaming
6112 months ago
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
memory-forensicspost-exploitationred-teaming
7502 months ago
ModuleShifting preview

ModuleShifting

GitHubnaksyn/moduleshifting

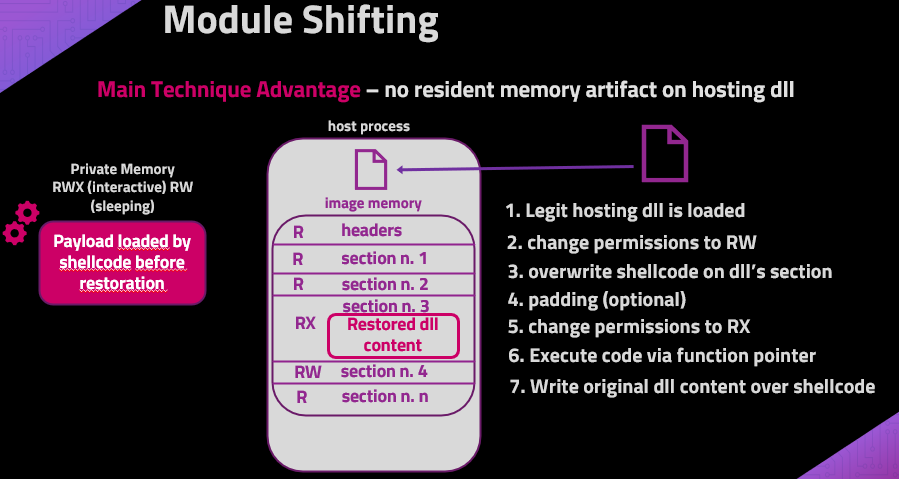
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
binary-exploitationmemory-forensicspayload-development+1
1373 years ago
zirconium preview

zirconium

GitHubrobertmotr/zirconium

DLL-injectable internal game cheat for Plutonium BO2 zombies

exploitationmemory-forensicspenetration-testing+2
132 months ago