
CVE-2010-2075
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
educationexploitationlabs-practice+7
rushikesh-a-bhujbal/cve-2010-2075UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 mourafuseti/vulneravel-cve-2018-14847---credenciais-extraidas
VULNERAVEL CVE-2018-14847 - CREDENCIAIS EXTRAIDAS MIKROTIK EM PYTHON
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
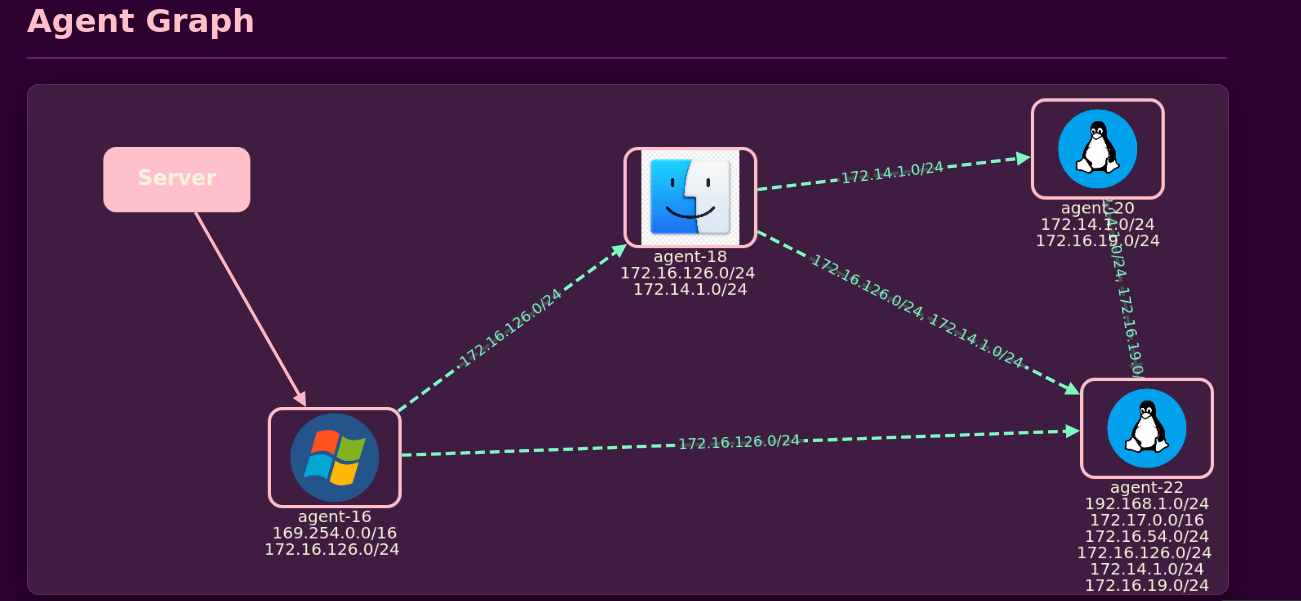 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 malwaretech/comodos
A remote denial-of-service zero day vulnerability in Comodo Internet Security firewall
 peter5he1by/cve-2023-20209
Detailed technical analysis and proof-of-concept exploit for CVE-2023-20209, a post-authentication remote code execution vulnerability in Cisco…
 scanfsec/cve-2018-15982
Aggressor Script to launch IE driveby for CVE-2018-15982.
 vakzz/tplink-cve-2017-11519
POC for TP-Link Archer C9 - Admin Password Reset and RCE (CVE-2017-11519)
 oscarakaelvis/cve-2023-51119
Improper Access Control on D-Link DIR-605L router
 papayajackal/ipeeyoupeewepee
Scanner and attack suite for hosts that forward unauthenticated packets via IPIP and GRE protocols. (CVE-2020-10136 CVE-2024-7595)
 s1lentf00thold/cve-2021-21425-rce
Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…
 fzbacon/cve-2019-18370_xiaomi_mi_wifi_rce_analysis
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 fj016/cve-2024-41992-poc
PoC for the CVE-2024-41992 (RCE on devices running WiFi-TestSuite-DUT)