
tfo-connect-bypass
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
exploitationids-ips-evasionnetwork-security+3
4n4s4zi/tfo-connect-bypassUsing TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 rudsarkar/cve-2026-42228
Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…
 al4n4n/cve-2026-25253-research
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click RCE on OpenClaw via Cross-Site WebSocket Hijacking. Includes attacker server and…
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 jelasin/cve-2026-41089
Pre-auth PoC for CVE-2026-41089 Netlogon CLDAP stack overflow via UDP/389, triggering LSASS crash/DC reboot. Includes exploit script, root-cause…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 ridhinva/ghe-push-option-rce-scanner
Scanner: CVE-2026-3854 GitHub Enterprise Server Pre-auth RCE via Push Option Injection — Python checker (CISA KEV)
 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 nccgroup/bkscan
BlueKeep scanner supporting NLA
 nccgroup/upnp-pentest-toolkit
UPnP Pentest Toolkit for Windows
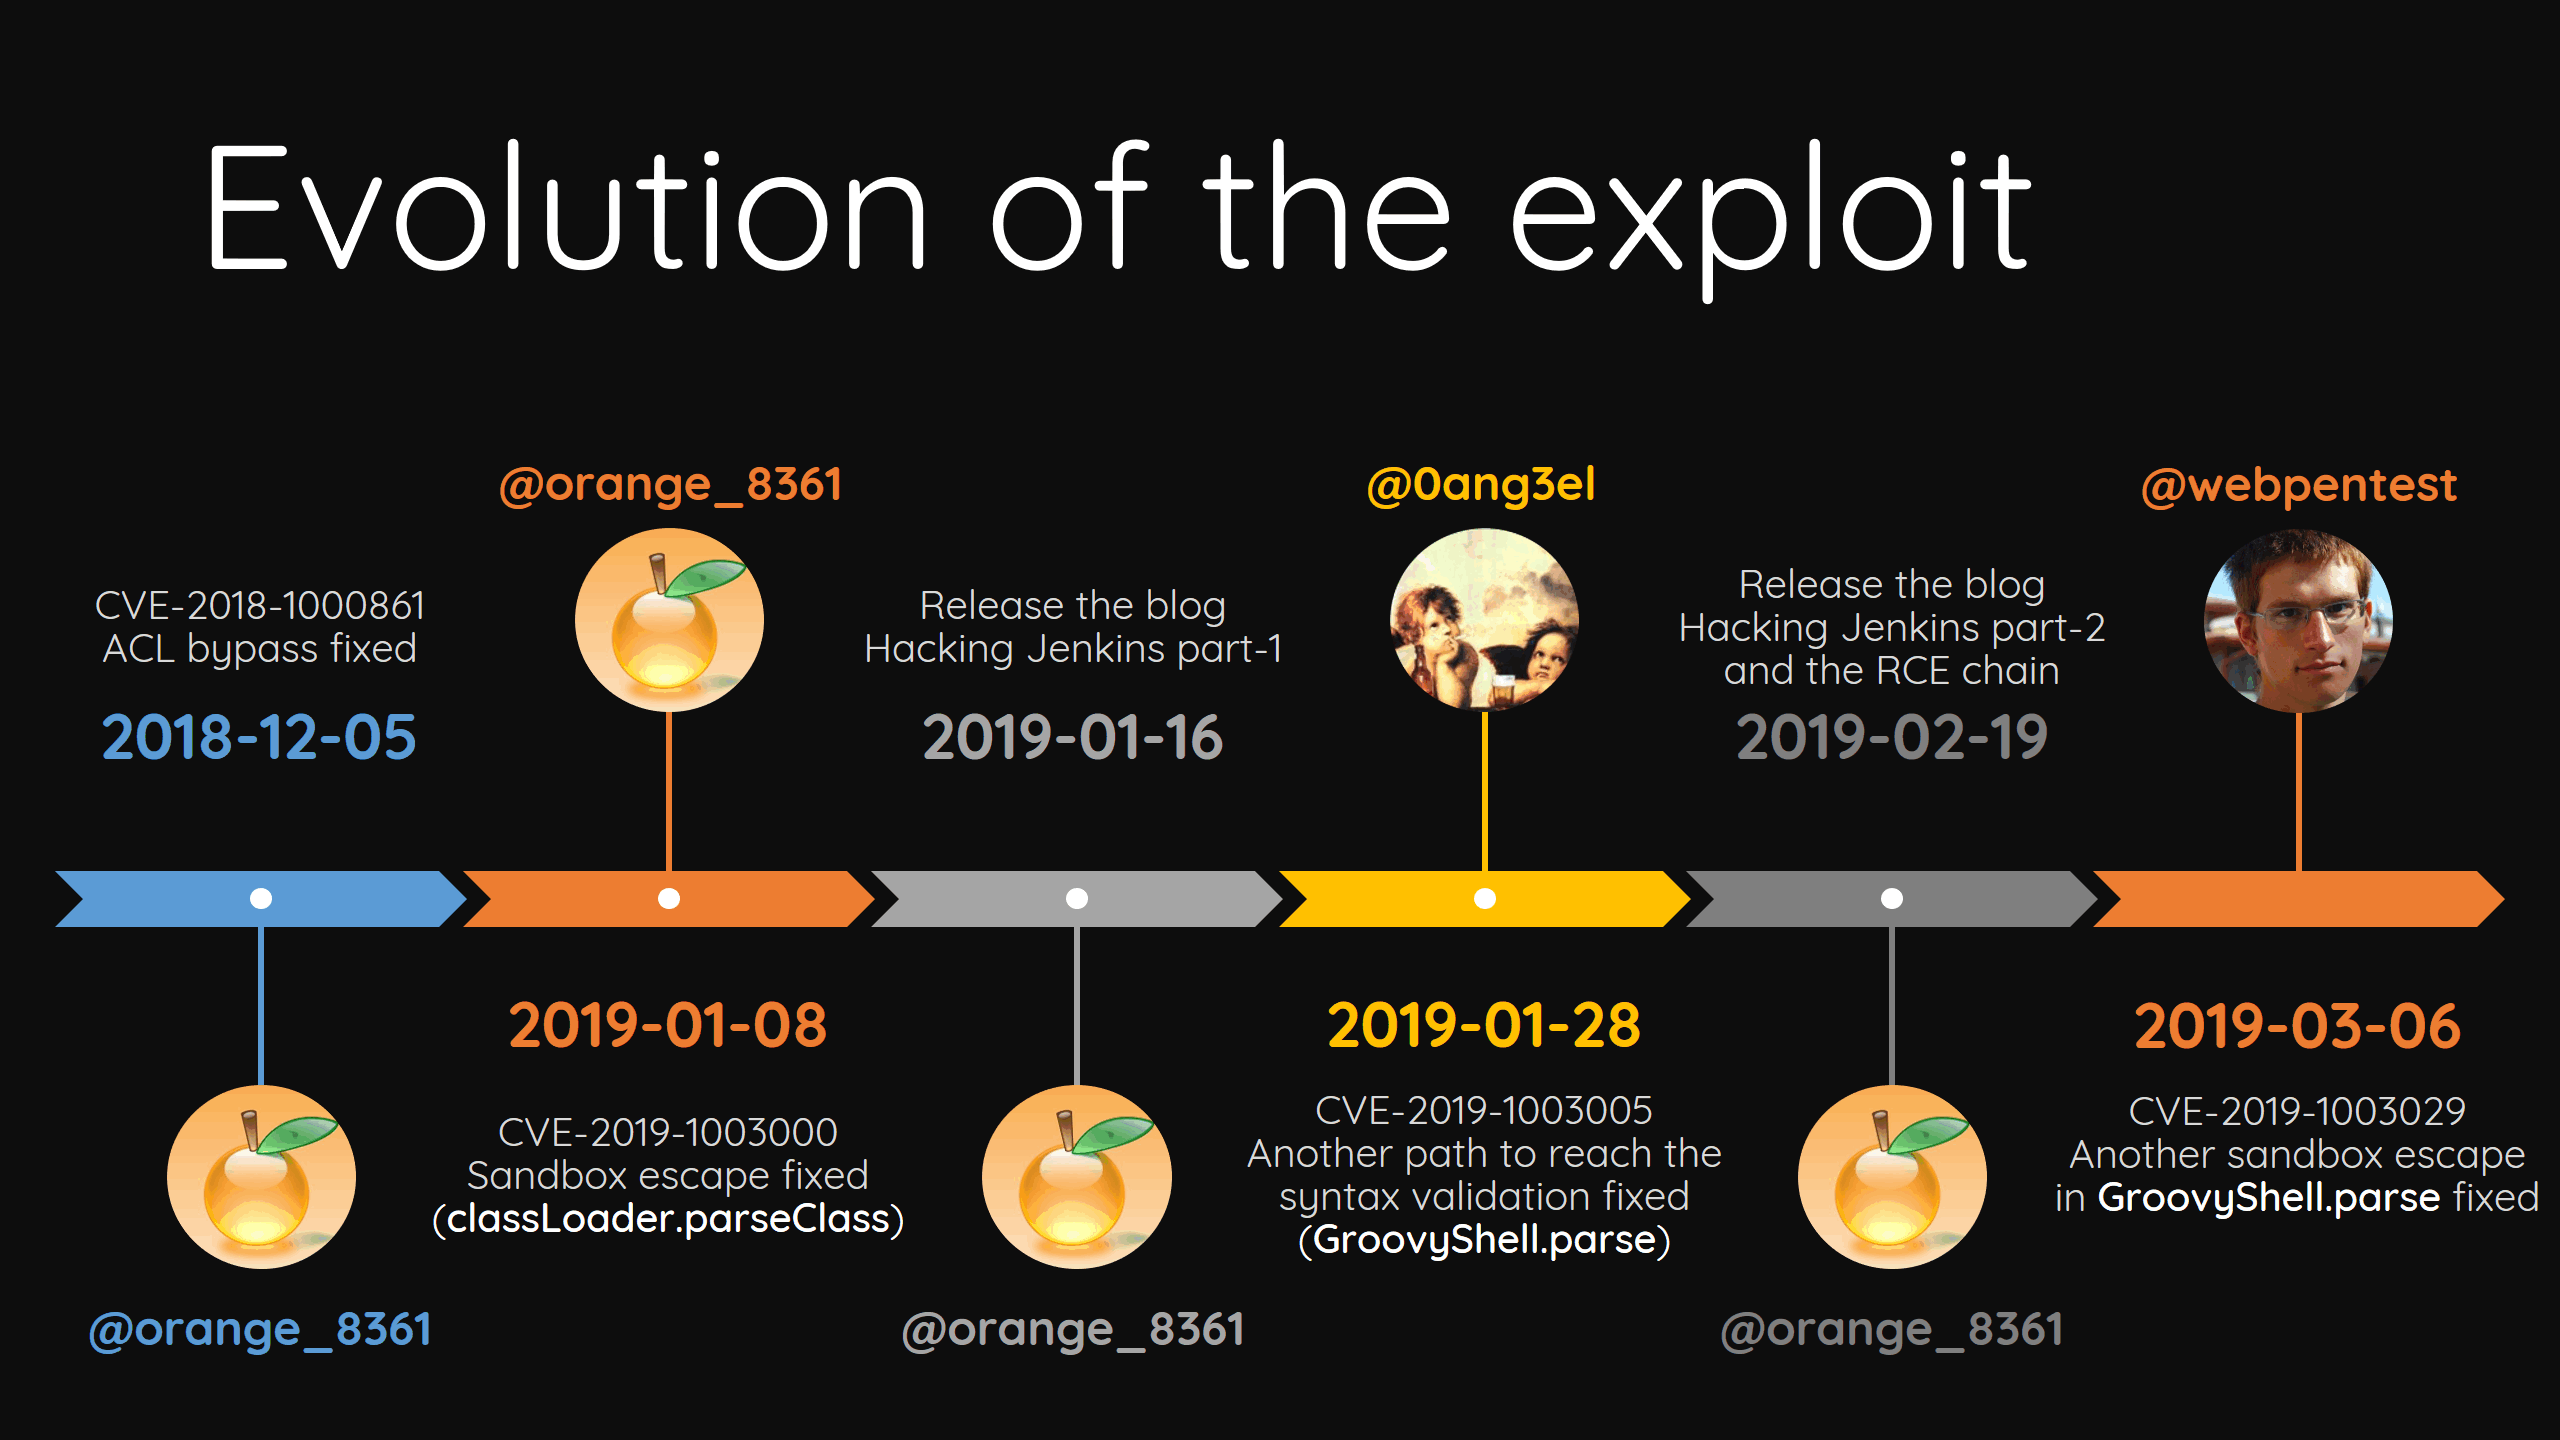 orangetw/awesome-jenkins-rce-2019
There is no pre-auth RCE in Jenkins since May 2017, but this is the one!

 husam212/mitmer
Automated man-in-the-middle attack tool.
 kevin-robertson/conveigh
Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 sherlocksecurity/vmware-cve-2022-22954
POC for VMWARE CVE-2022-22954