

Enumprotections_BOF
 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.
information-gatheringpenetration-testingpost-exploitation+4
126
octoberfest7/enumprotections_bofA BOF to enumerate system process, their protection levels, and more.
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 raikia/smbcrunch
3 tools that work together to simplify reconaissance of Windows File Shares
 javelinnetworks/honeypotbuster
PowerShell module for red teams to detect honeypots, honeytokens, and deception techniques in Active Directory environments, including fake accounts,…
 peewpw/invoke-wcmdump
PowerShell Script to Dump Windows Credentials from the Credential Manager
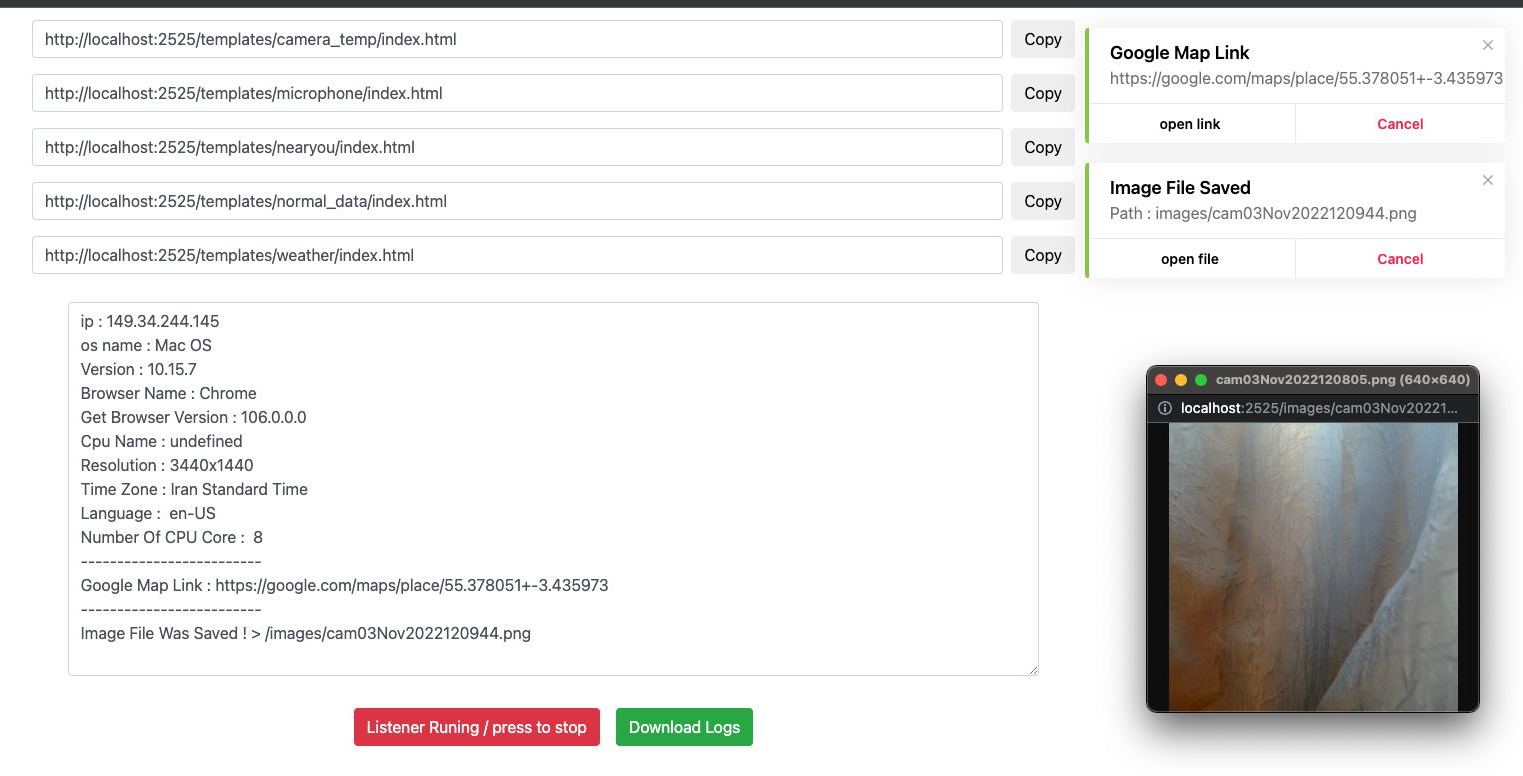 ultrasecurity/storm-breaker
Full-featured Social Engineering Framework with Page Cloning, MITM Proxy, Credential Capture, Session Extraction, and Real-time Monitoring.