
VMInjector
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
authentication-authorizationbinary-exploitationexploitation+4
hzphreak/vminjectorDLL Injection tool to unlock guest VMs
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
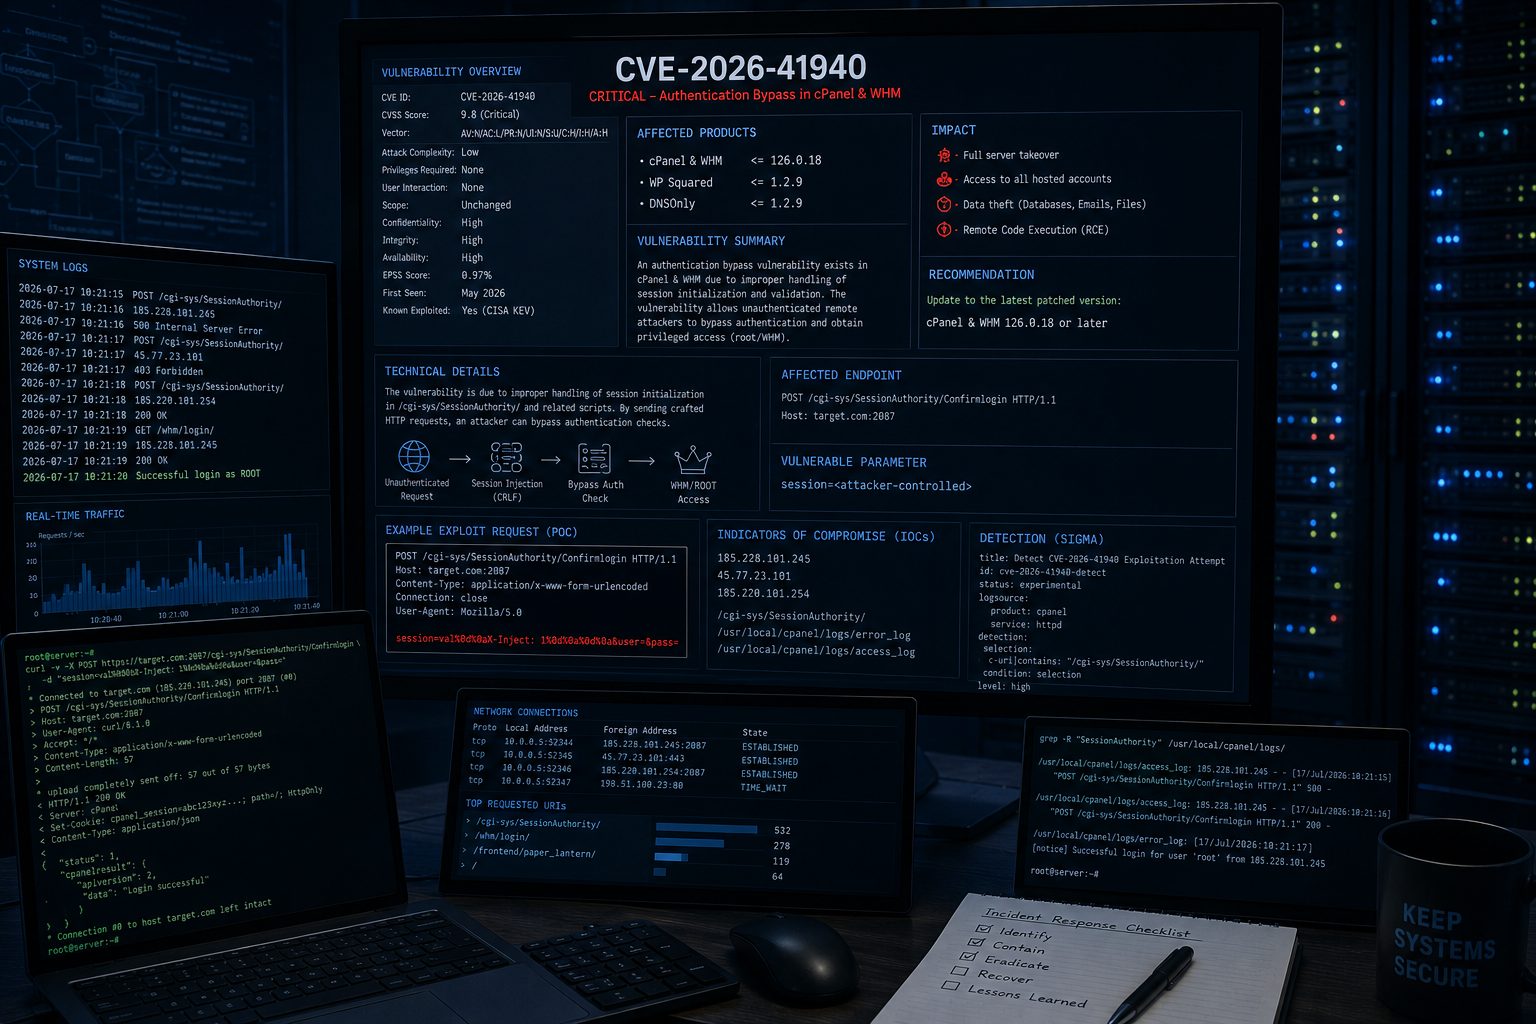 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 anach-ai/cve-2026-41940
CVE-2026-41940 — cPanel/WHM Auth Bypass By Dr.Anach, CRLF injection in `cpsrvd` Basic auth handler → unauthenticated WHM API access → RCE as root.…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…