
red-team-map
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
command-and-controlcurated-resourceseducation+7
37
kypvas/red-team-mapRed Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 bishopfox/sliver
Adversary Emulation Framework
 fatedier/frp
A fast reverse proxy to help you expose a local server behind a NAT or firewall to the internet.
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
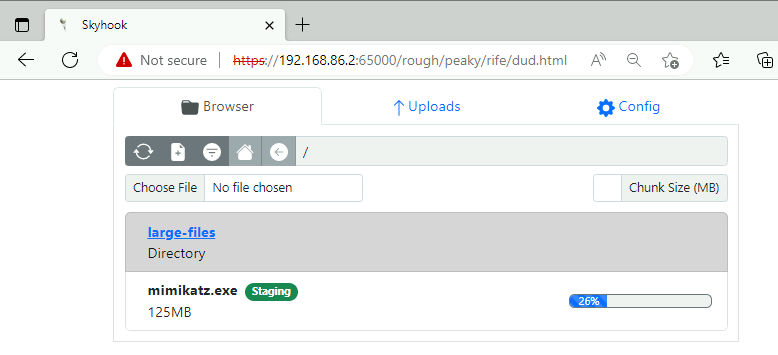 blackhillsinfosec/skyhook
A round-trip obfuscated HTTP file transfer setup built to bypass IDS detections.
 sims718718/unifiedthreathunting
Documents a structured, repeatable threat hunting methodology covering triggers, SMART hypotheses, feasibility gates, scoping, hunt plans, and…
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…