
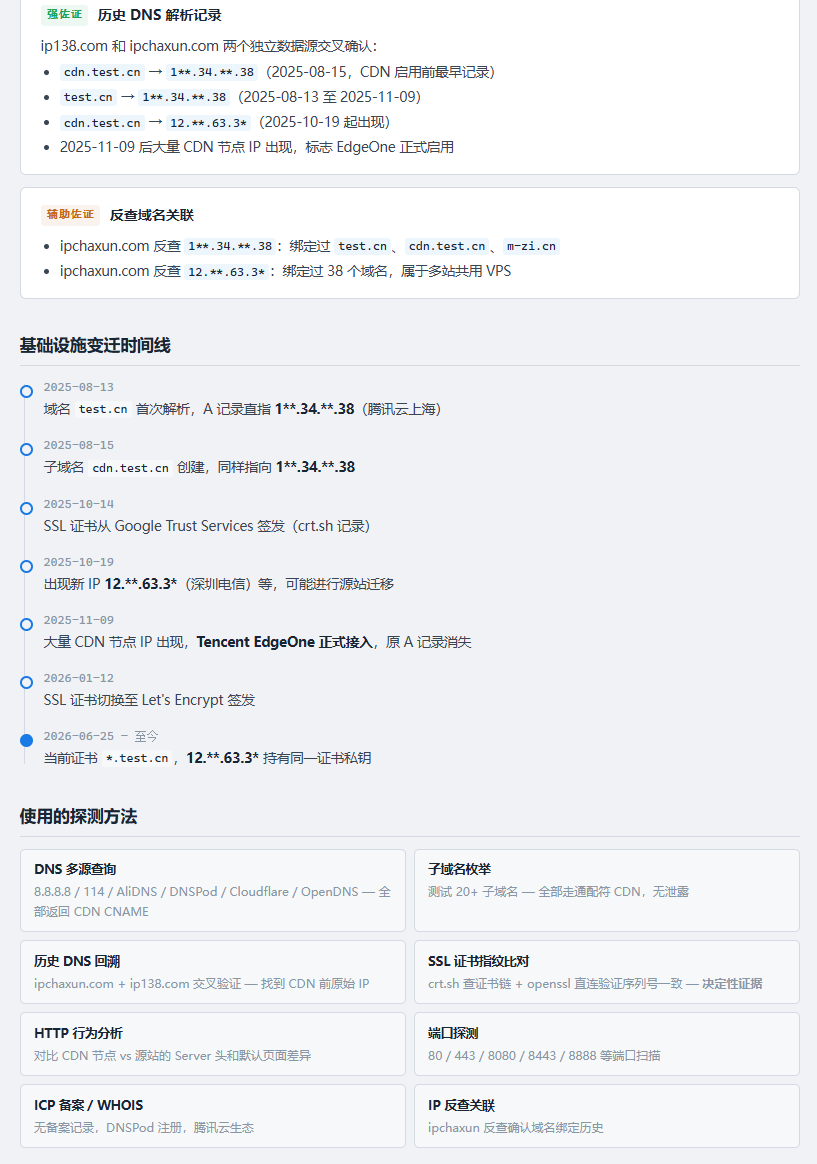
FUCK-CDN
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
dns-analysisdns-subdomain-enumerationinformation-gathering+9
159
0xshe/fuck-cdnAutomated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
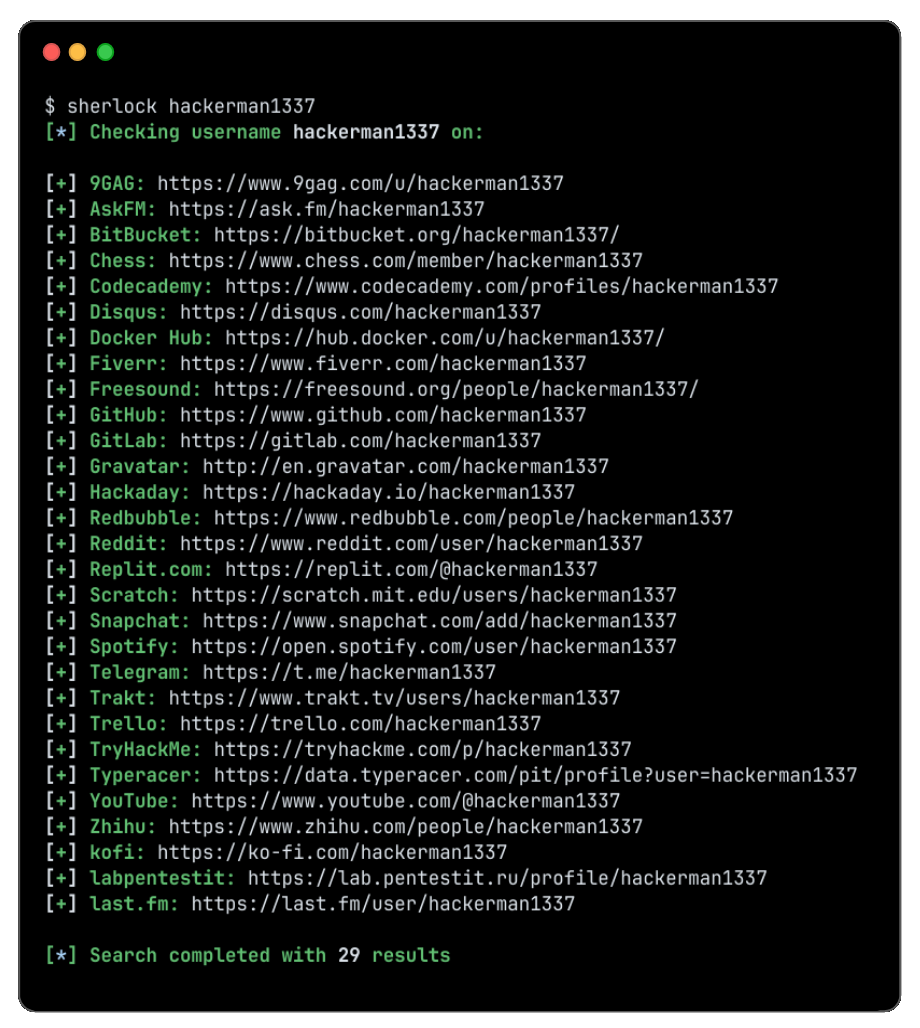 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 matrixtm/mhddos
Best DDoS Attack Script Python3, (Cyber / DDos) Attack With 56 Methods
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
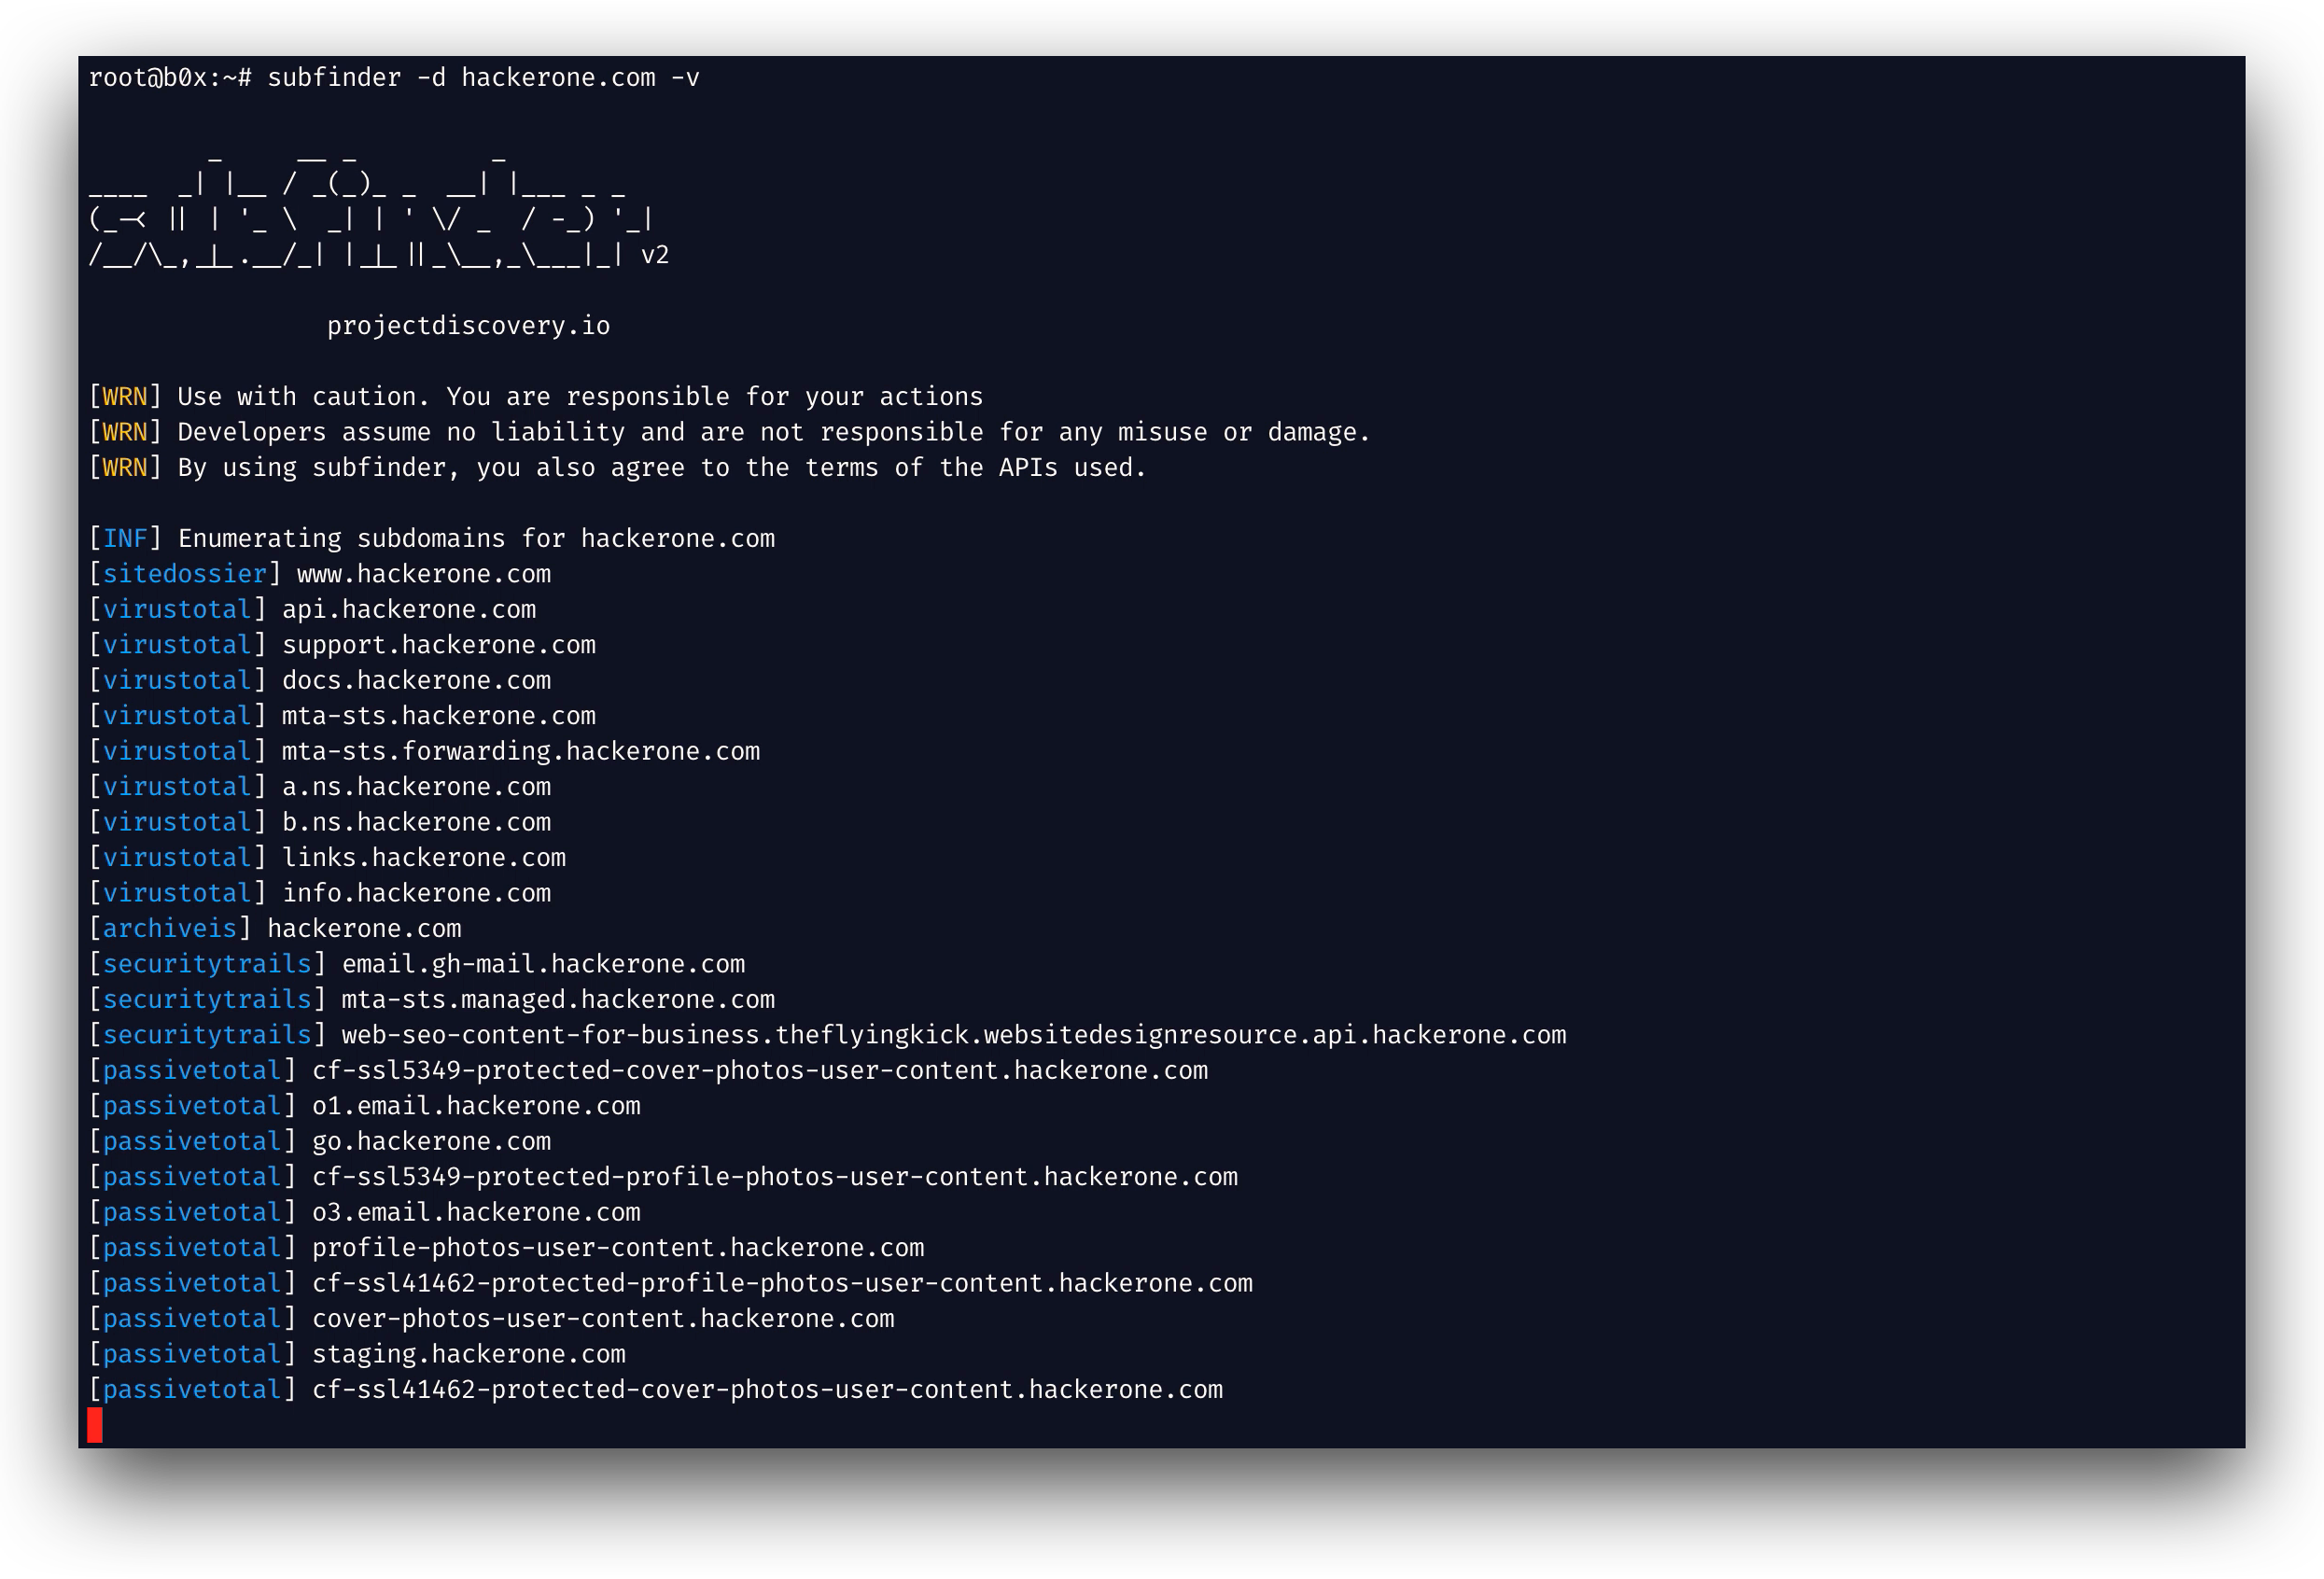 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 hackerest/pwneye
Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
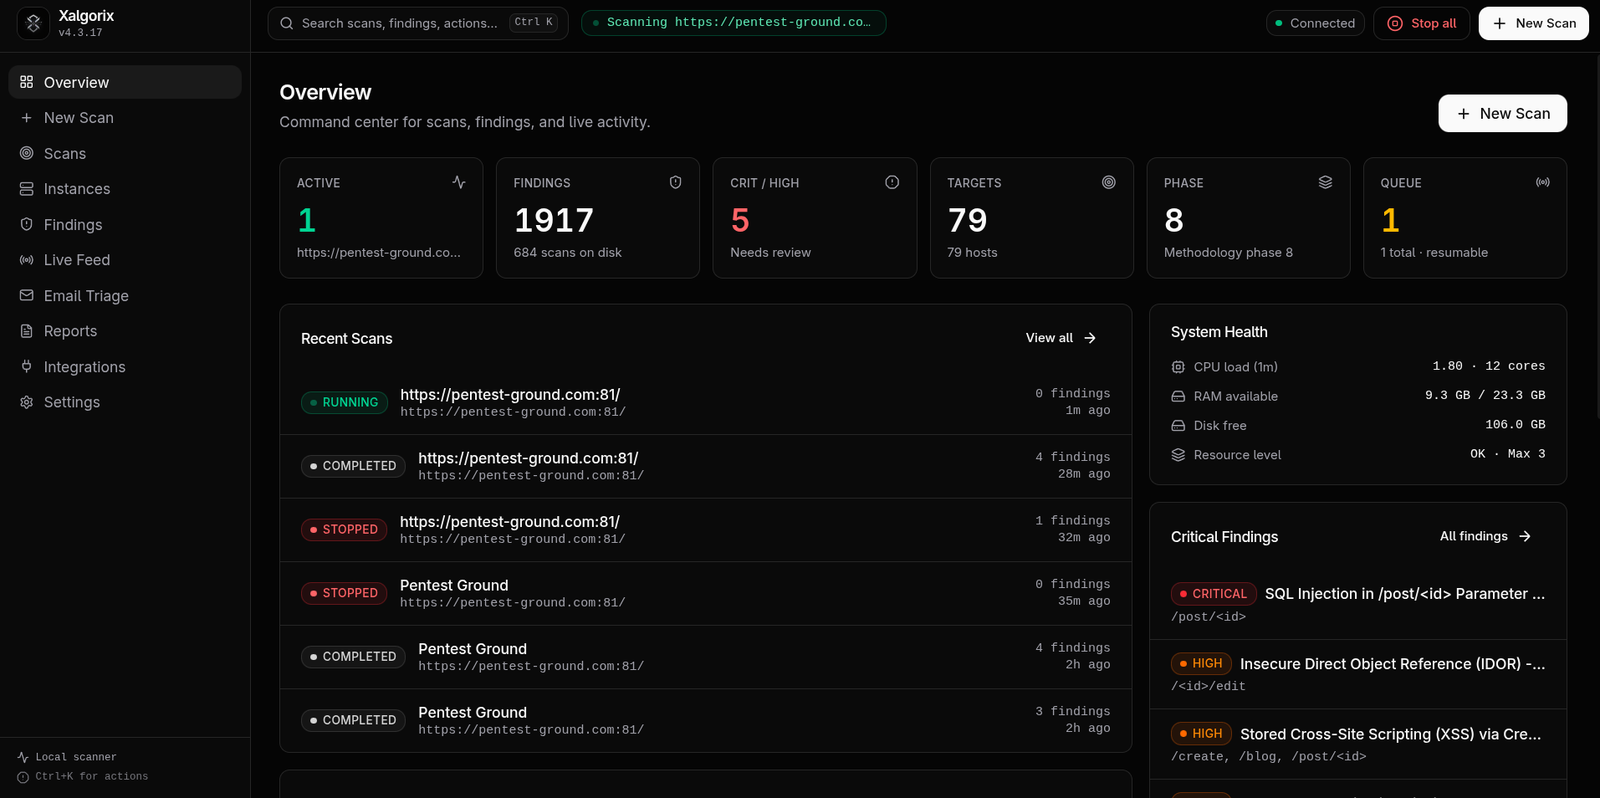 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
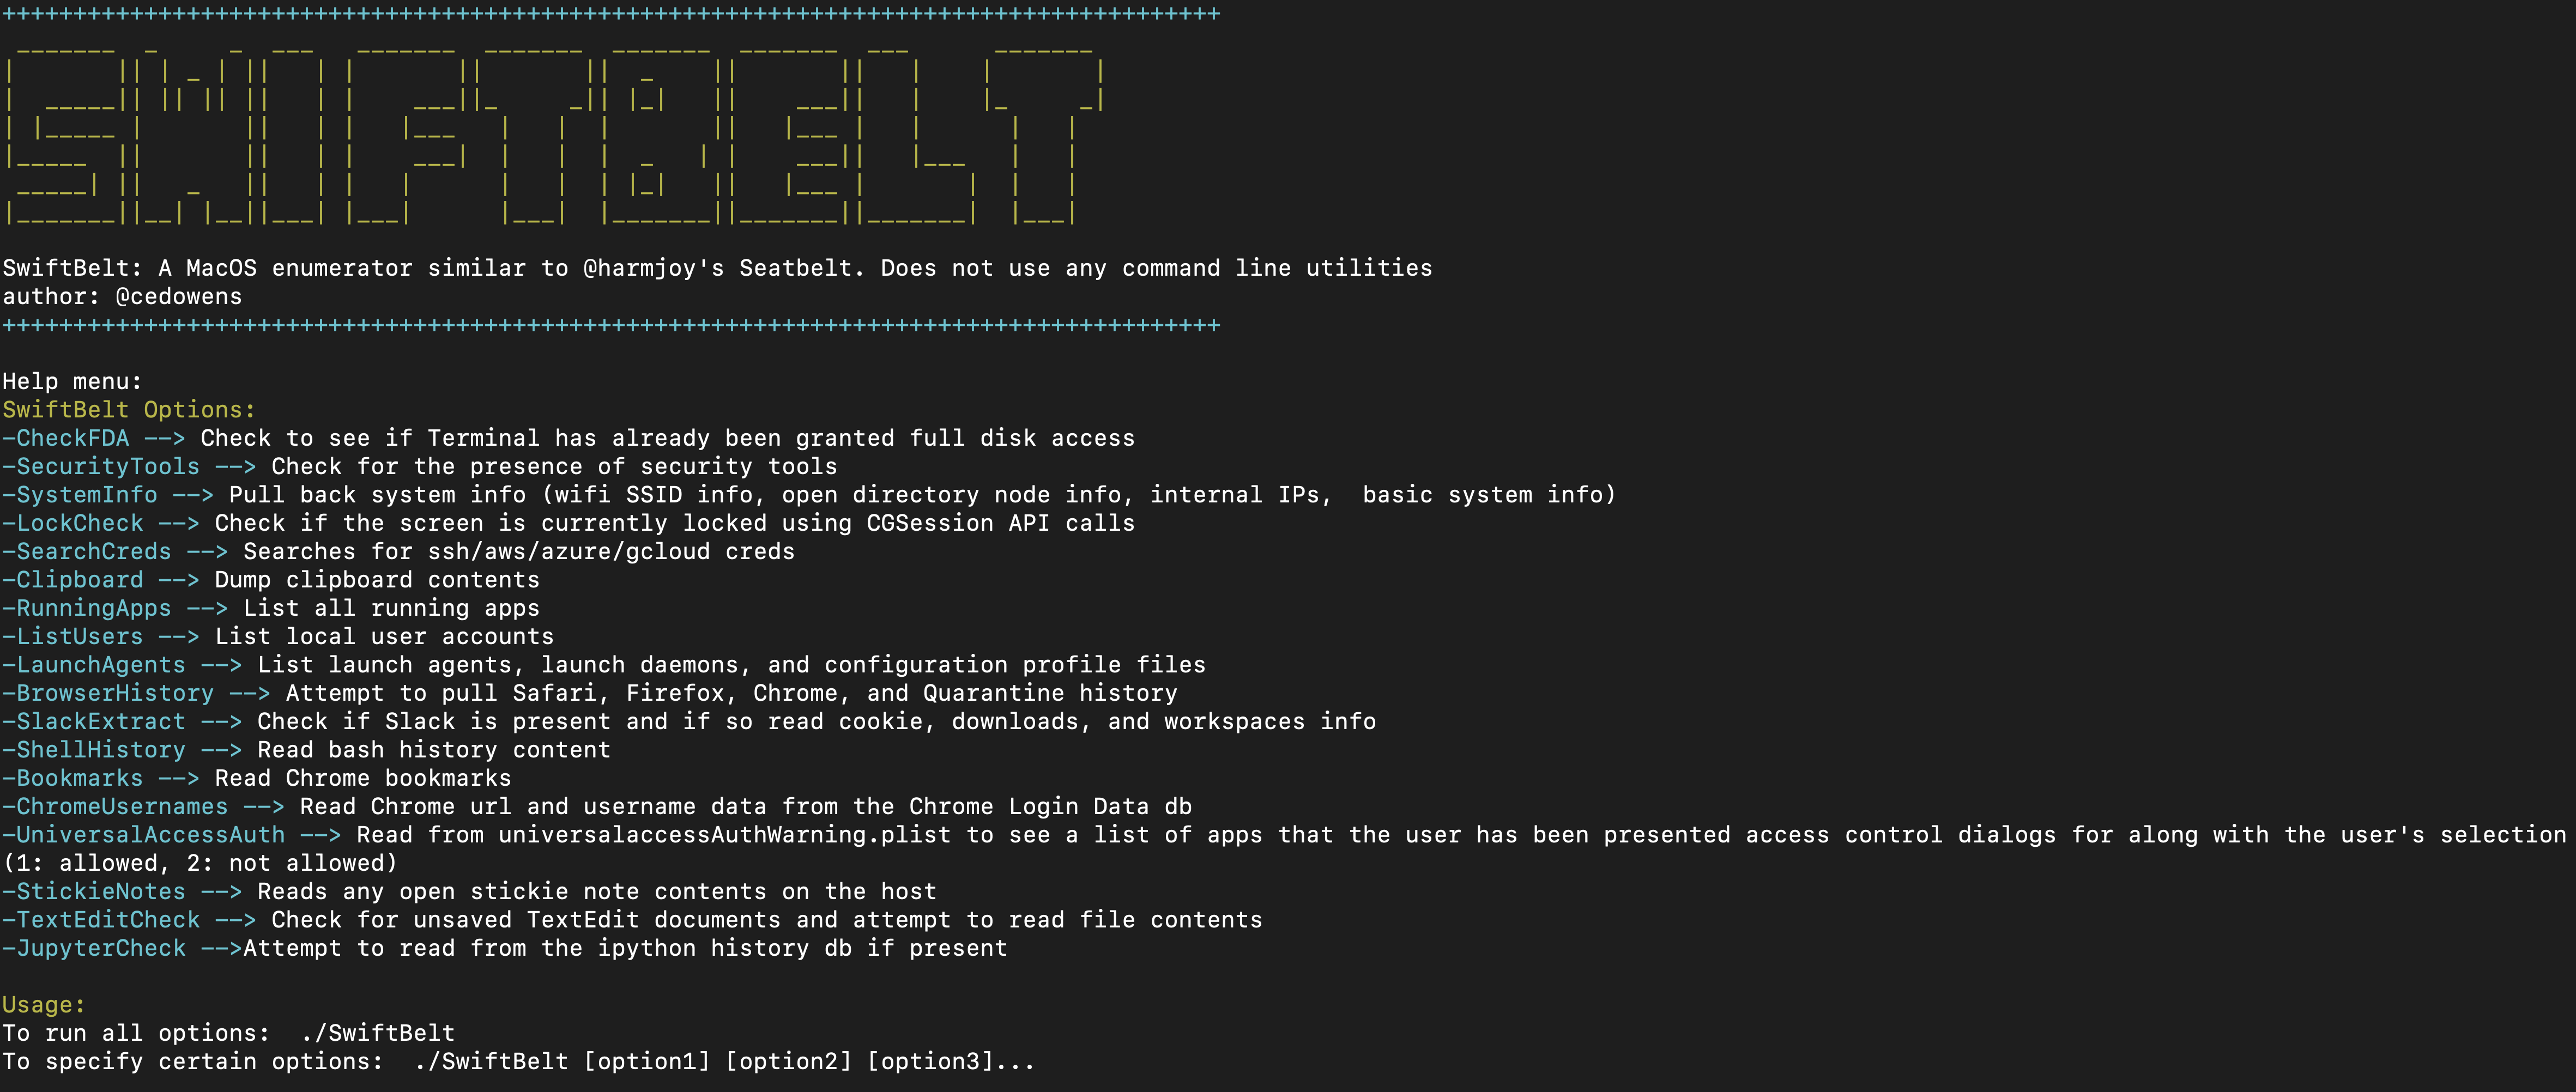 cedowens/swiftbelt
A macOS enumeration tool inspired by harmjoy's Windows-based Seatbelt enumeration tool. Author: Cedric Owens
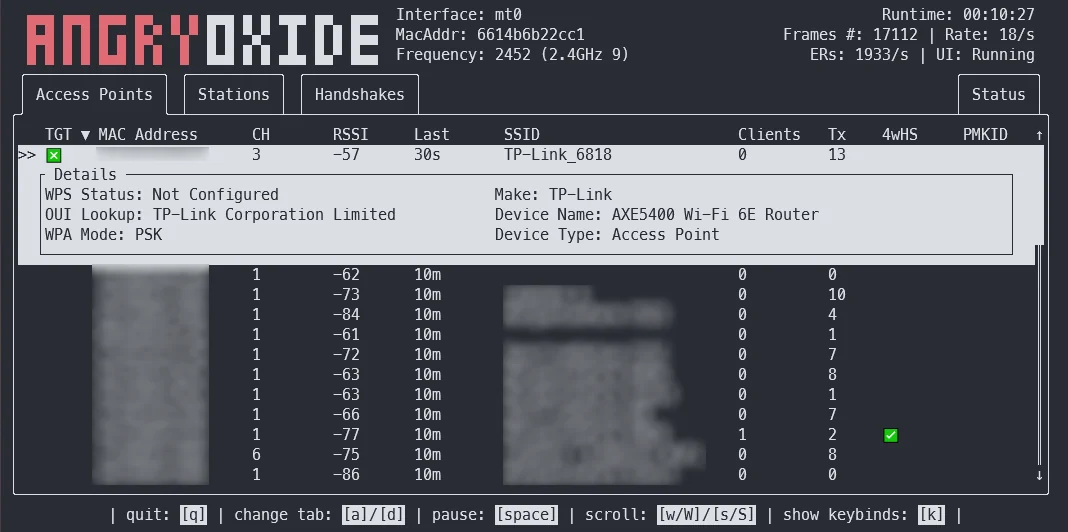 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
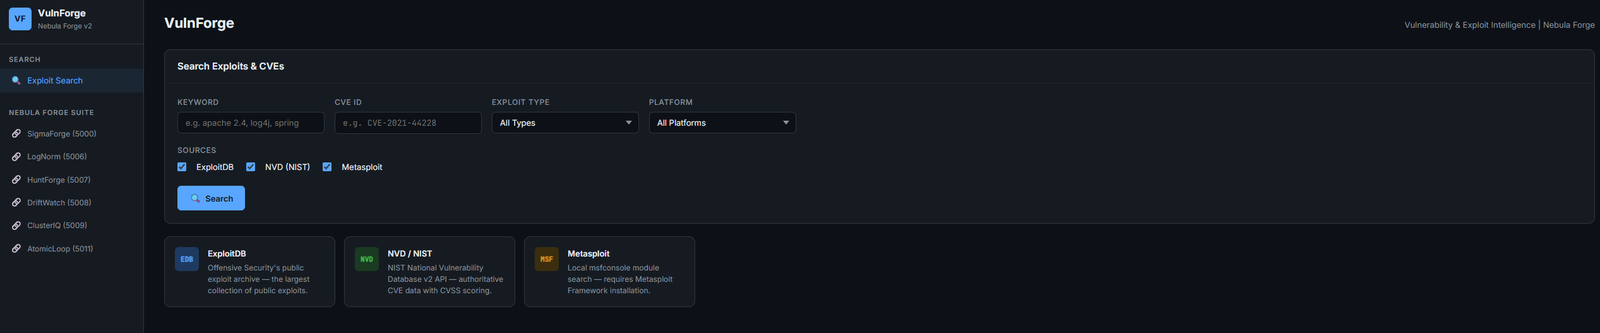 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
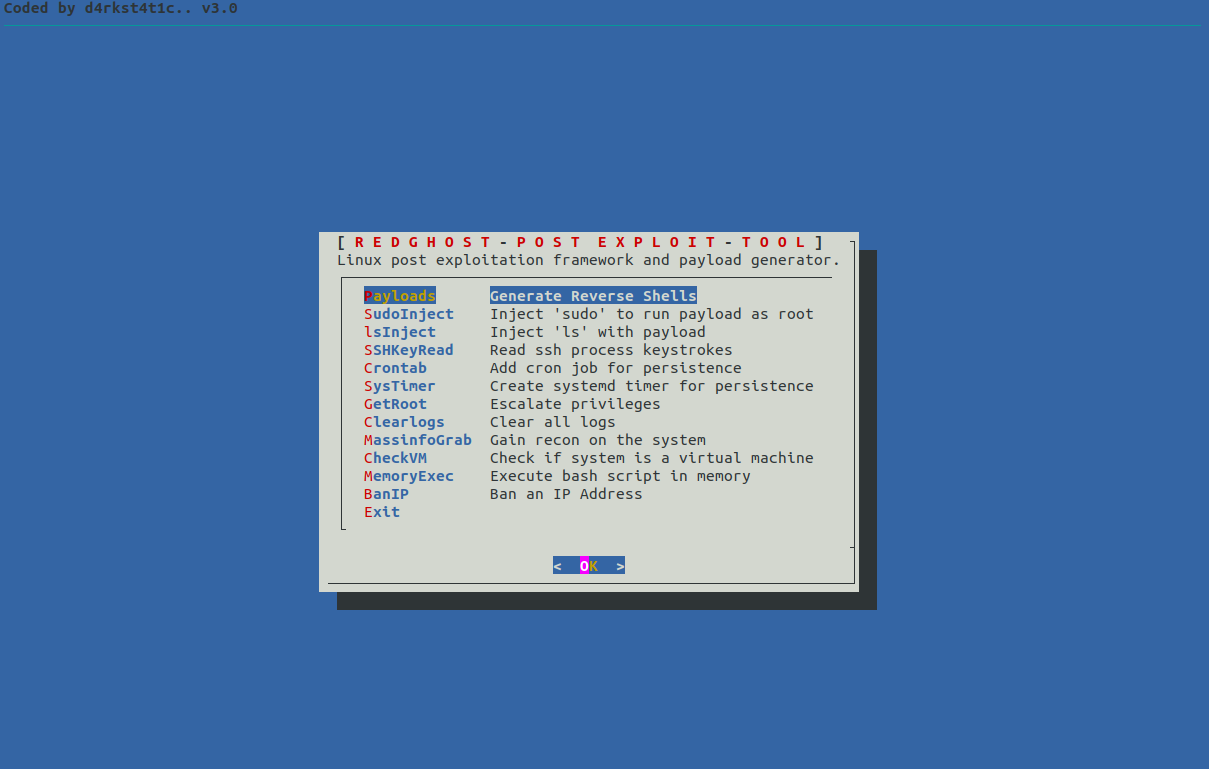 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…