
php_reverse_shell
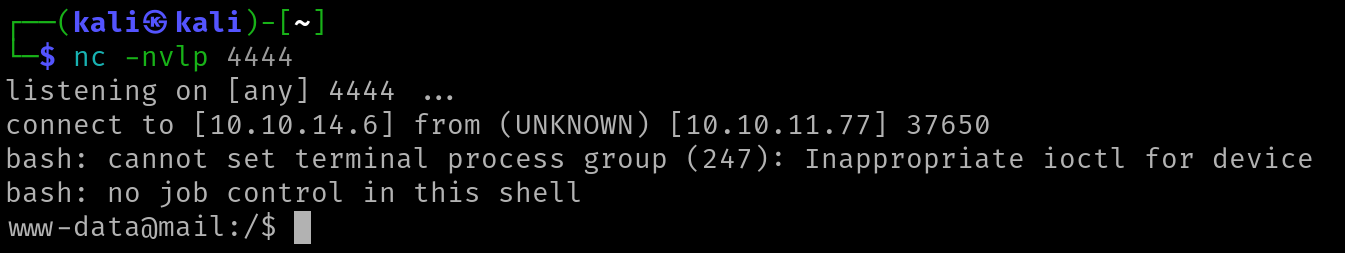
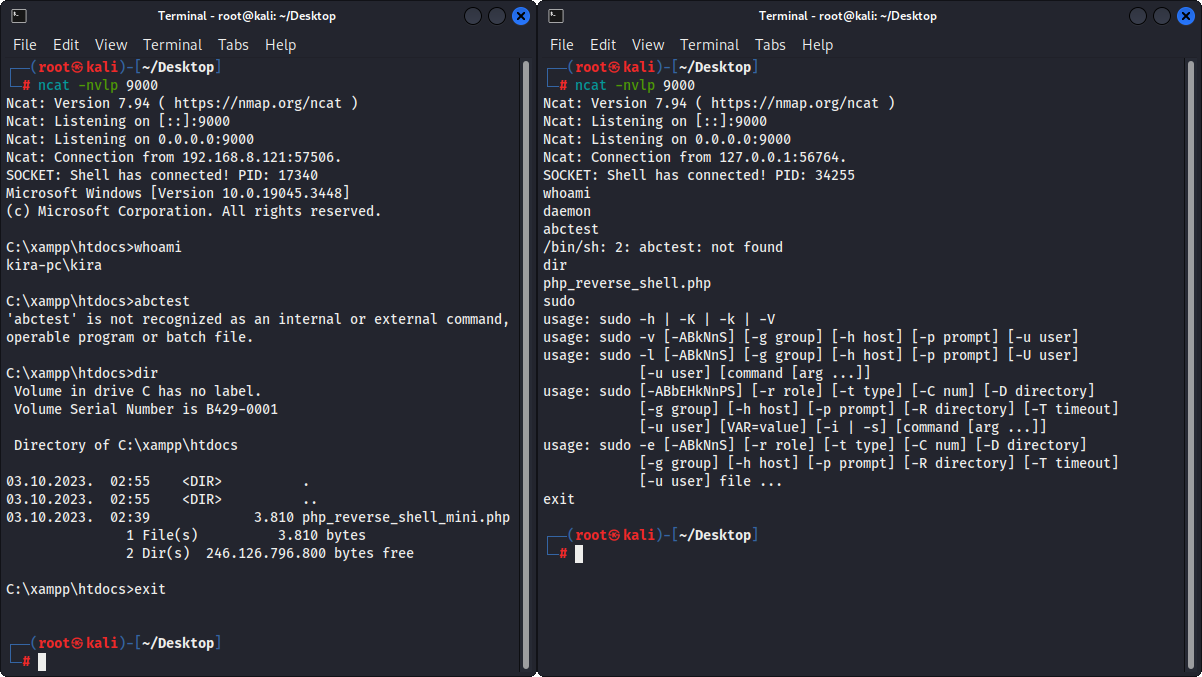
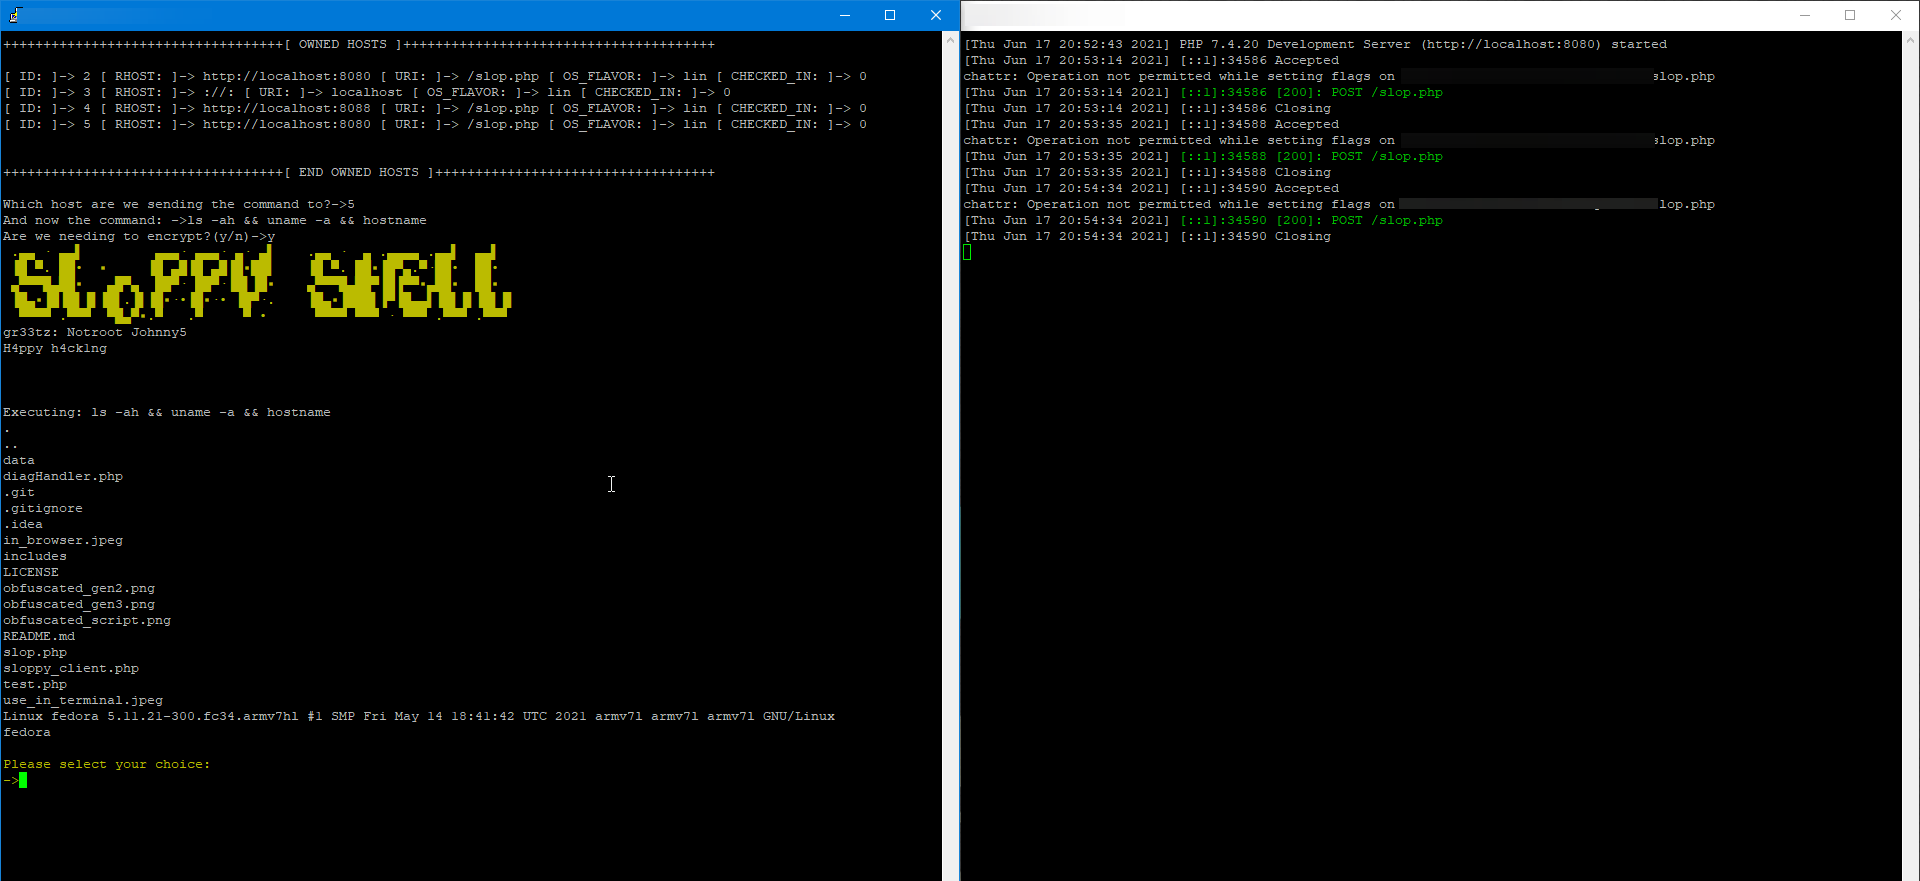
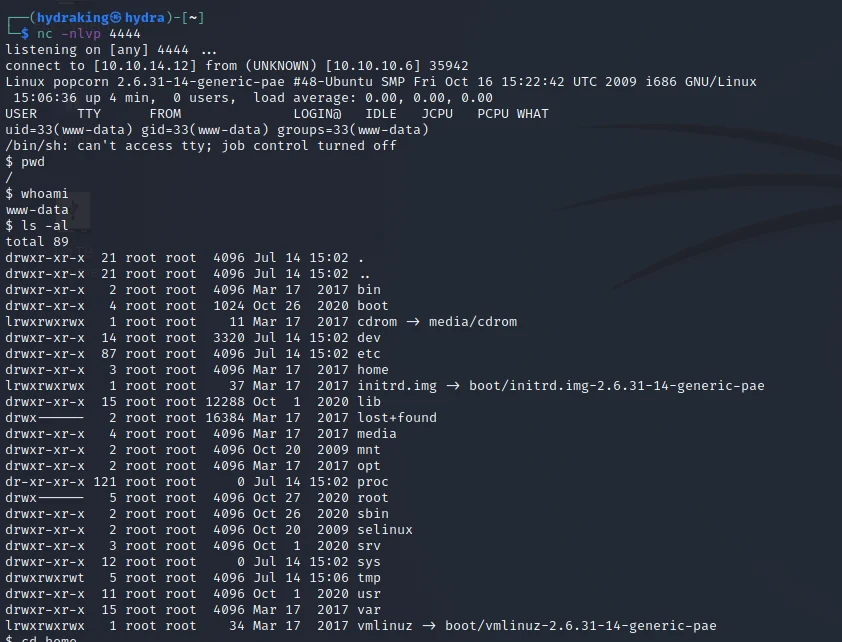
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…

A proof of concept for Joomla's CVE-2015-8562 vulnerability (Object Injection RCE)

Demo project how to bypass the disable_functions security control of PHP on Linux

Exploits CVE-2024-51793 unauthenticated arbitrary file upload in WordPress Computer Repair Shop plugin, scans target lists, uploads PHP webshells,…

Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…

Exploit for PHP CGI Argument Injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers running Apache and PHP-CGI.…

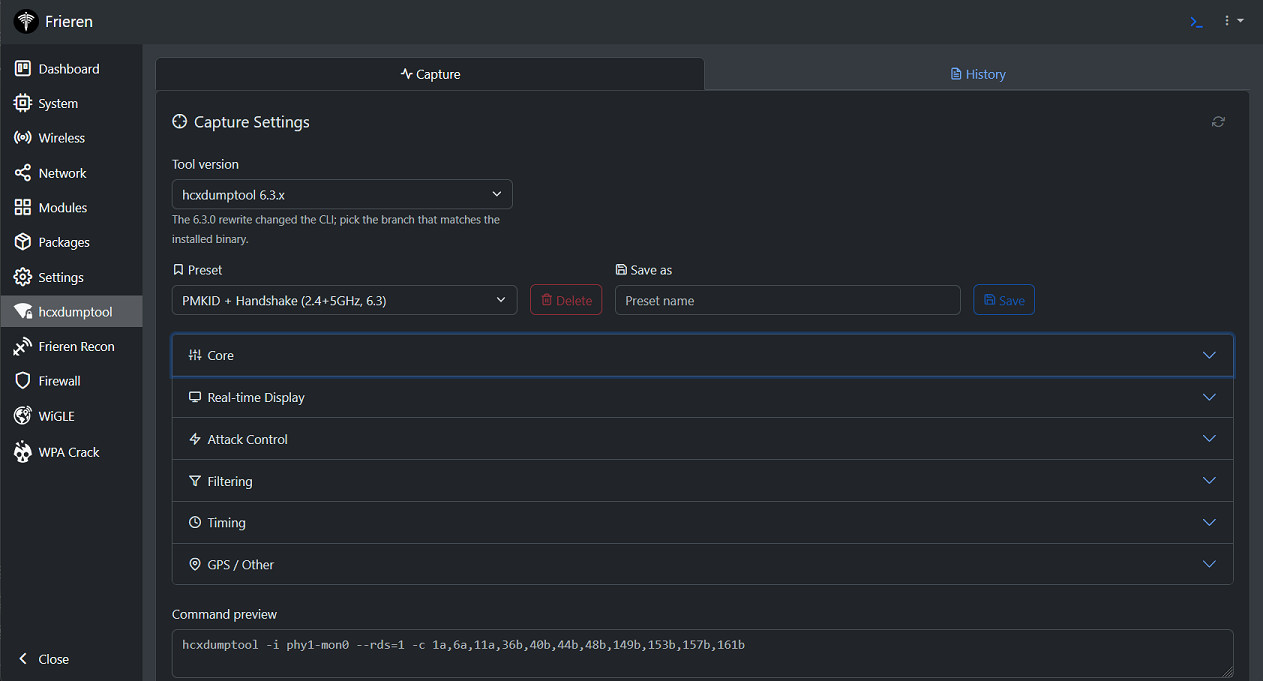
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…

This is a webshell open source project

PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.

PHP shells that work on Linux OS, macOS, and Windows OS.

GiveWP <= 4.16.7.1 Unauthenticated PHP Object Injection → RCE

A BYOSI (Bring-Your-Own-Script-Interpreter) Rapid Payload Deployment Toolkit

Proof-of-concept exploit for CVE-2026-82222, an unauthenticated PHP object injection leading to remote code execution in GiveWP WordPress plugin…

This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…


the only php webshell you need.