Chrome-App-Bound-Encryption-Decryption

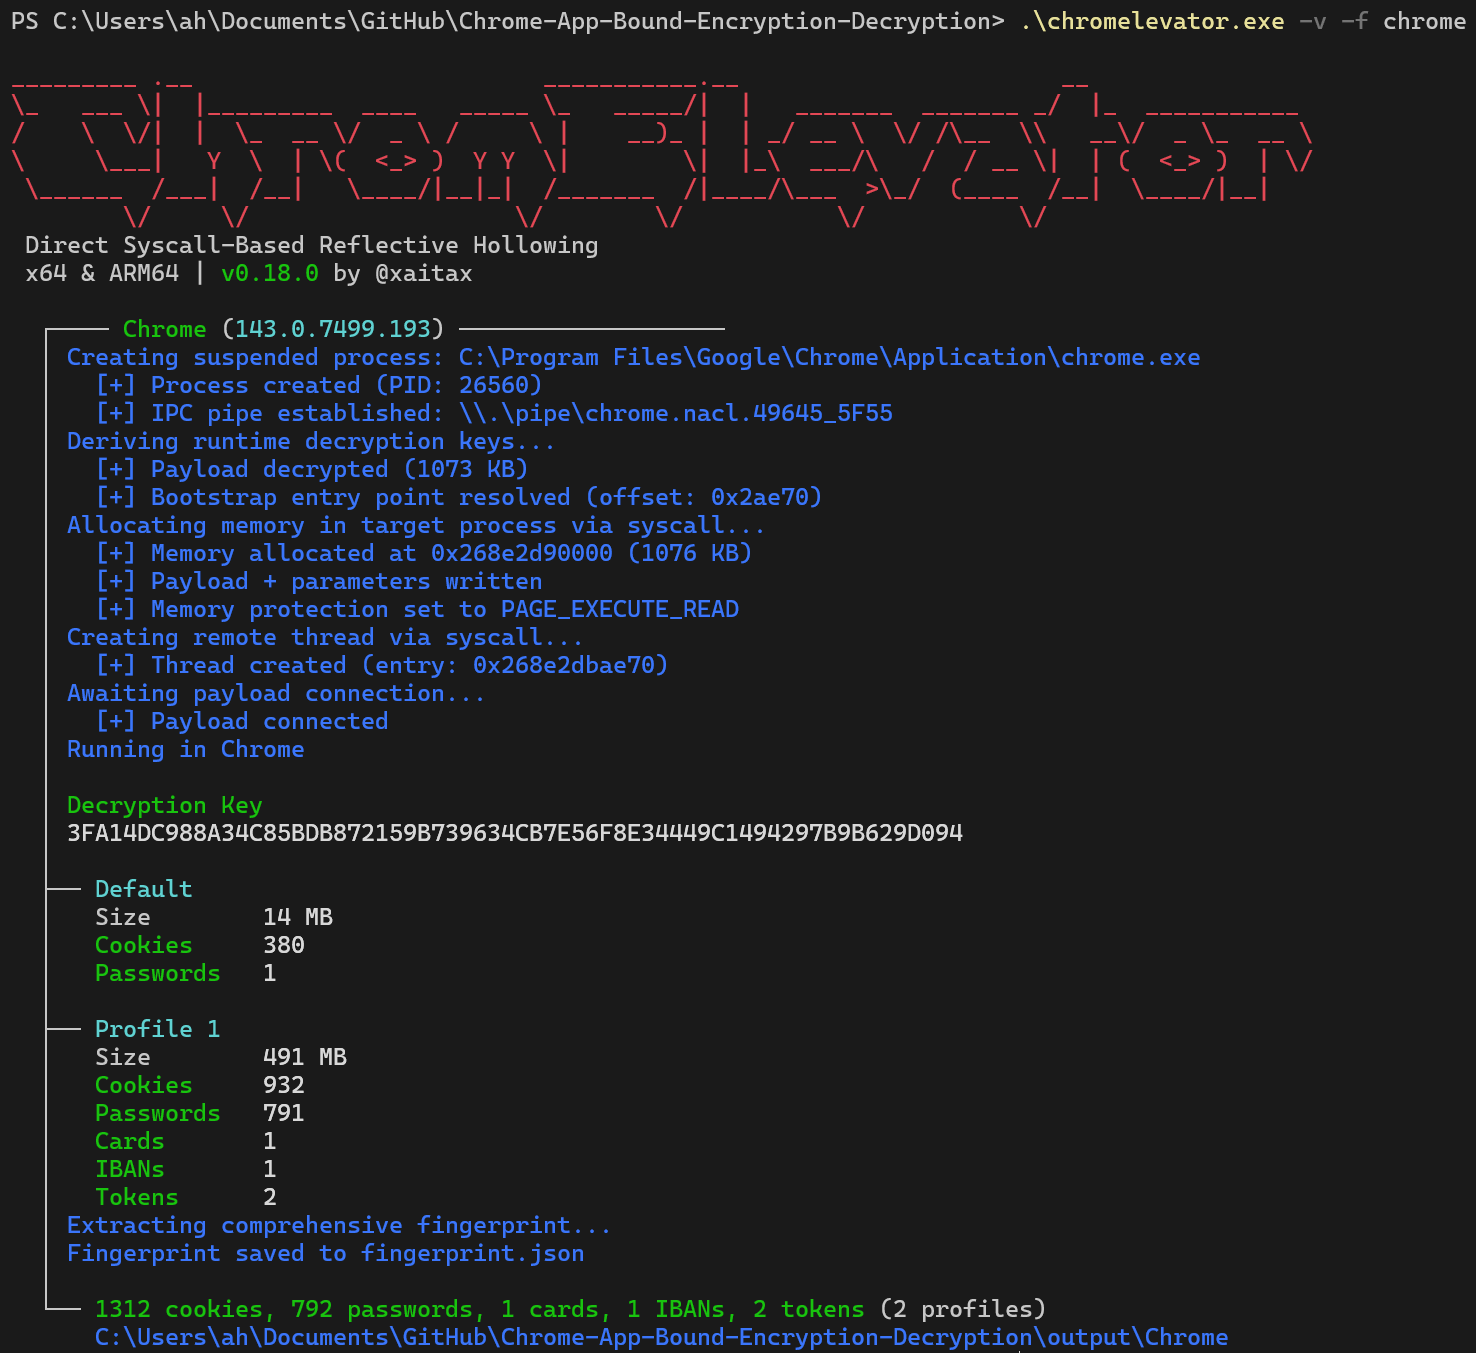
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.

The Shadow Attack Framework

RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…

CVE-2026-34197 activemq PoC

Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…

Post exploitation tool for configuration management servers.

C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…

Tool to deploy a post-exploitation prompt at any time

Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…

RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…

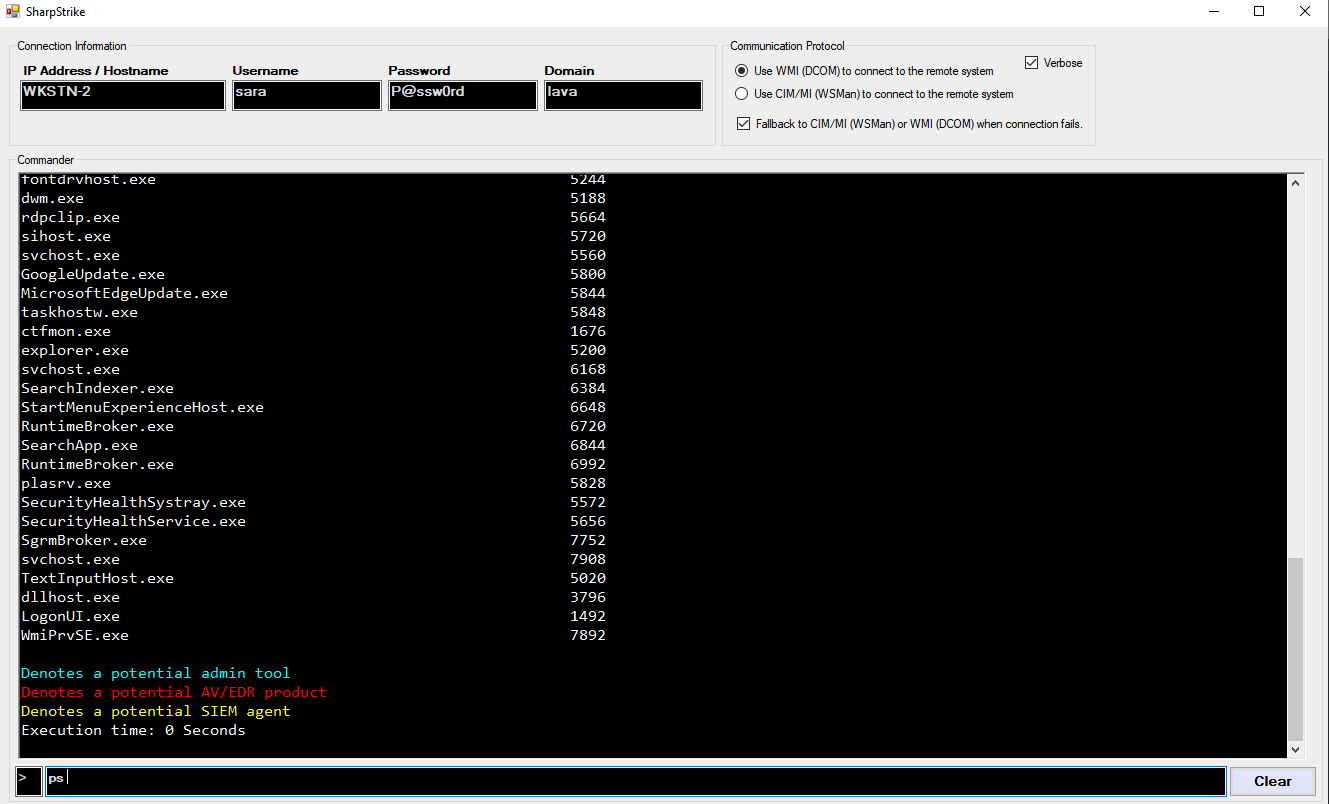
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.

Offensive tool to trigger network authentications as SYSTEM

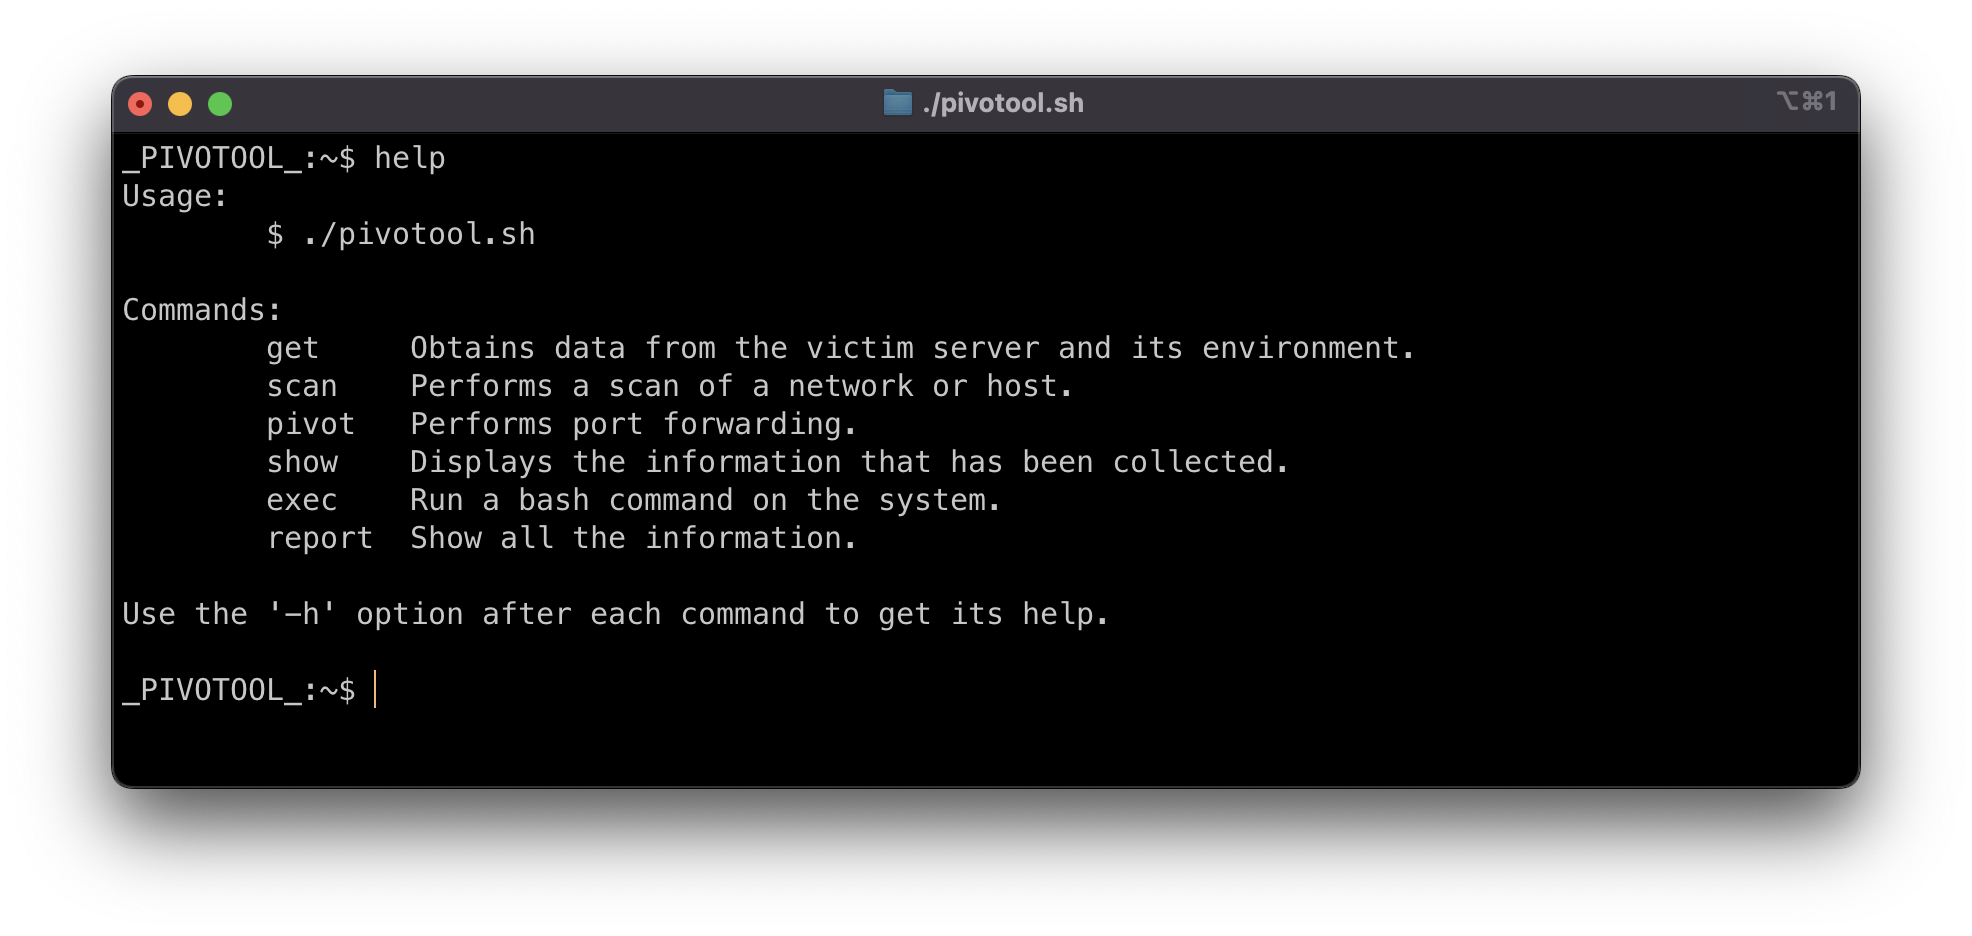
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.

Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it

Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens