
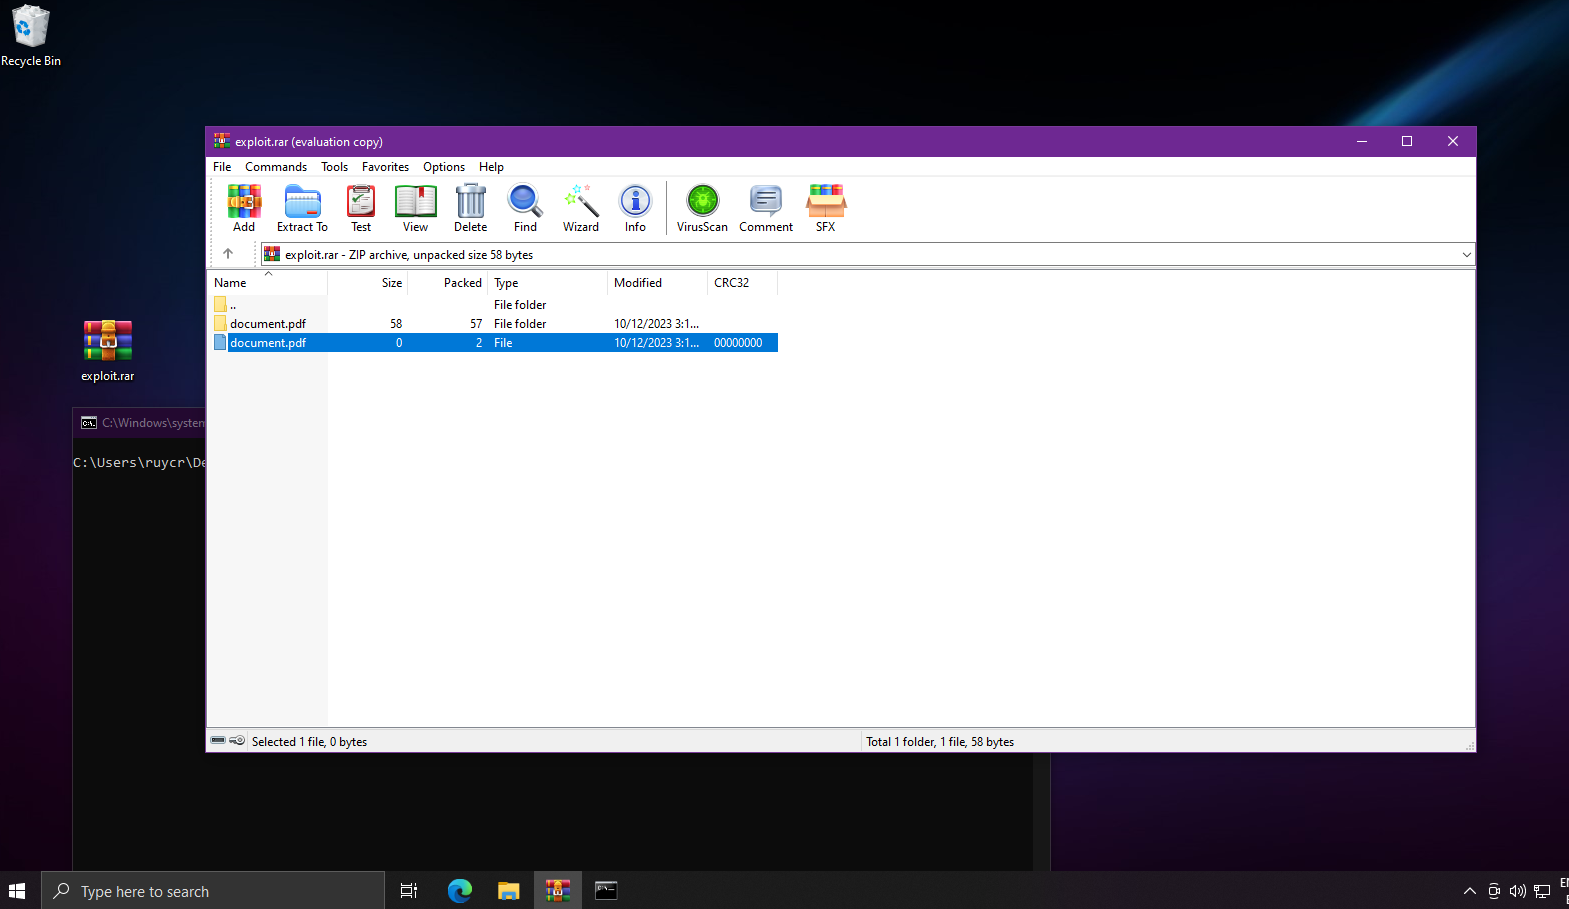
CVE-2023-38831
 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
exploitationpayload-generationpenetration-testing+3
1
ruycr4ft/cve-2023-38831Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 synacktiv/itsm-exploit
Ivanti Neurons for ITSM (On Premise) exploits
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
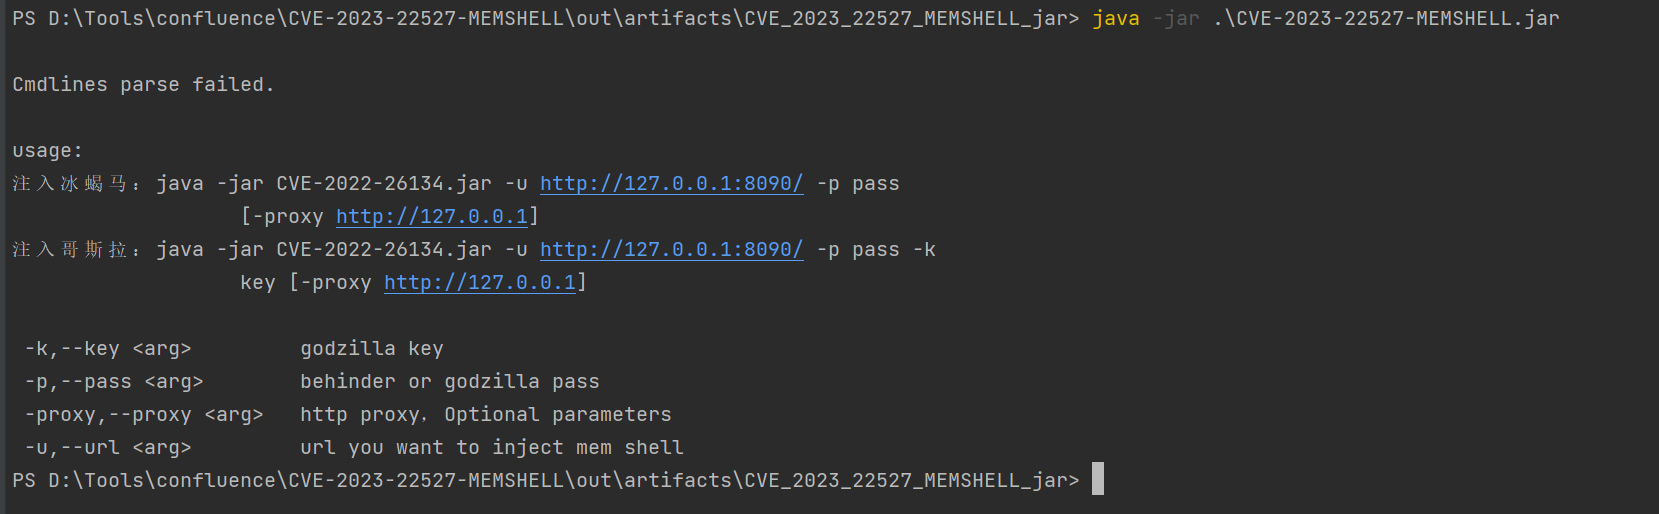 m0untainshley/cve-2023-22527-memshell
confluence CVE-2023-22527 漏洞利用工具,支持冰蝎/哥斯拉内存马注入,支持设置 http 代理
 horizon3ai/cve-2023-28324
Ivanti EPM AgentPortal RCE Vulnerability
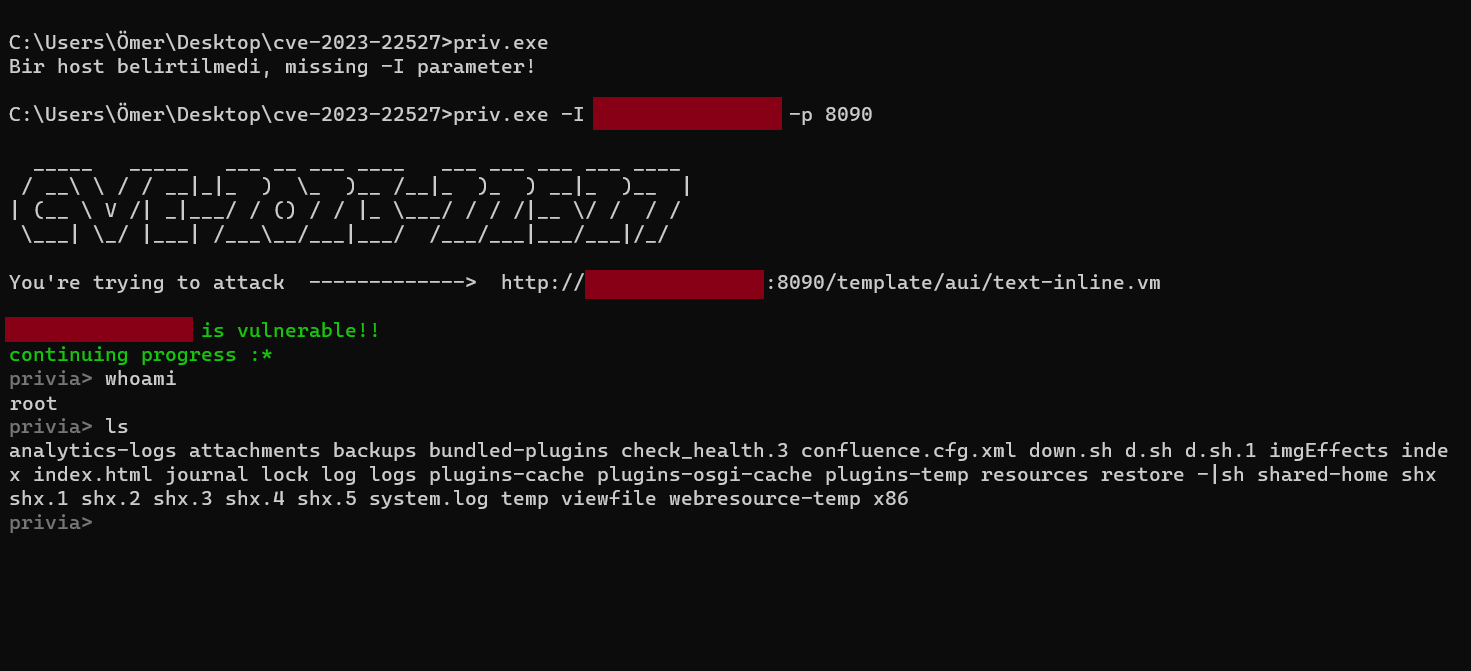 privia-security/cve-2023-22527
CVE-2023-22527
 swiftsecur/teamcity-exploit-cve-2023-42793
teamcity-exploit-cve-2023-42793
 toothless5143/cve-2023-22809
Running this exploit on a vulnerable system allows a local attacker to gain a root shell on the machine.
 okaytc/superset_auth_bypass_check
Apahce-Superset身份认证绕过漏洞(CVE-2023-27524)检测工具
 0xnehru/cve-2023-36845-juniper-vulnerability
This Python script automates the Proof of Concept (PoC) for CVE-2023-36845, a vulnerability impacting Juniper Networks Junos OS on EX and SRX Series…
 fullspectrumdev/rancidcrisco
Proof-of-concept exploit for CVE-2023-20126 targeting Cisco SPA phone adapters. Uploads malicious firmware to gain a root shell on port 23000/tcp via…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.