
chimera
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
binary-exploitationexploitationpayload-development+4
1neptune/chimeraRust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
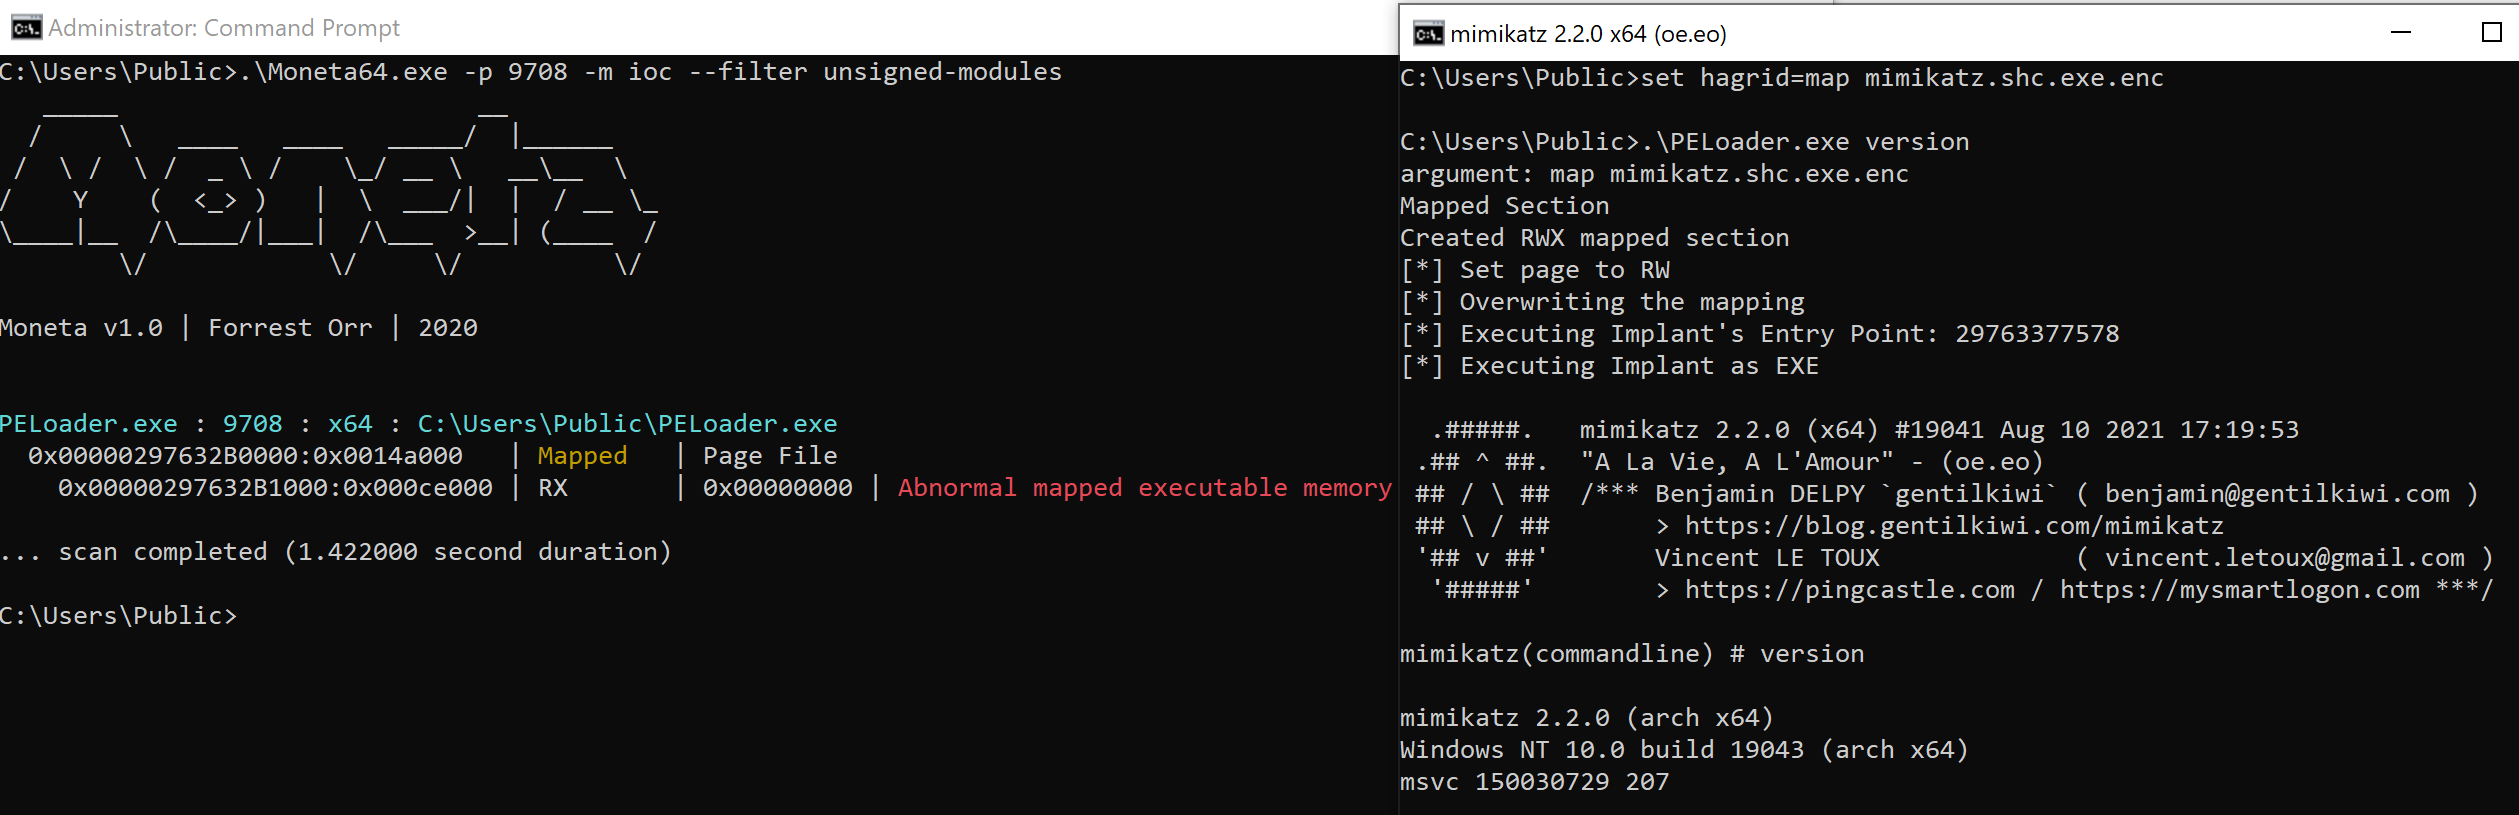 hagrid29/peloader
PE loader with various shellcode injection techniques
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…