
second-order
 mhmdiaa/second-order
Crawls web applications to detect second-order subdomain takeover vulnerabilities by collecting URLs and matching configurable rules for non-200…
crawlerreconnaissancesubdomain-enumeration+2
410
mhmdiaa/second-orderCrawls web applications to detect second-order subdomain takeover vulnerabilities by collecting URLs and matching configurable rules for non-200…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 abdullahaligun/reachability-check
Browser-based network connectivity checker for testing firewall rules, access restrictions, and corporate policy compliance. Supports HTTP Fetch and…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
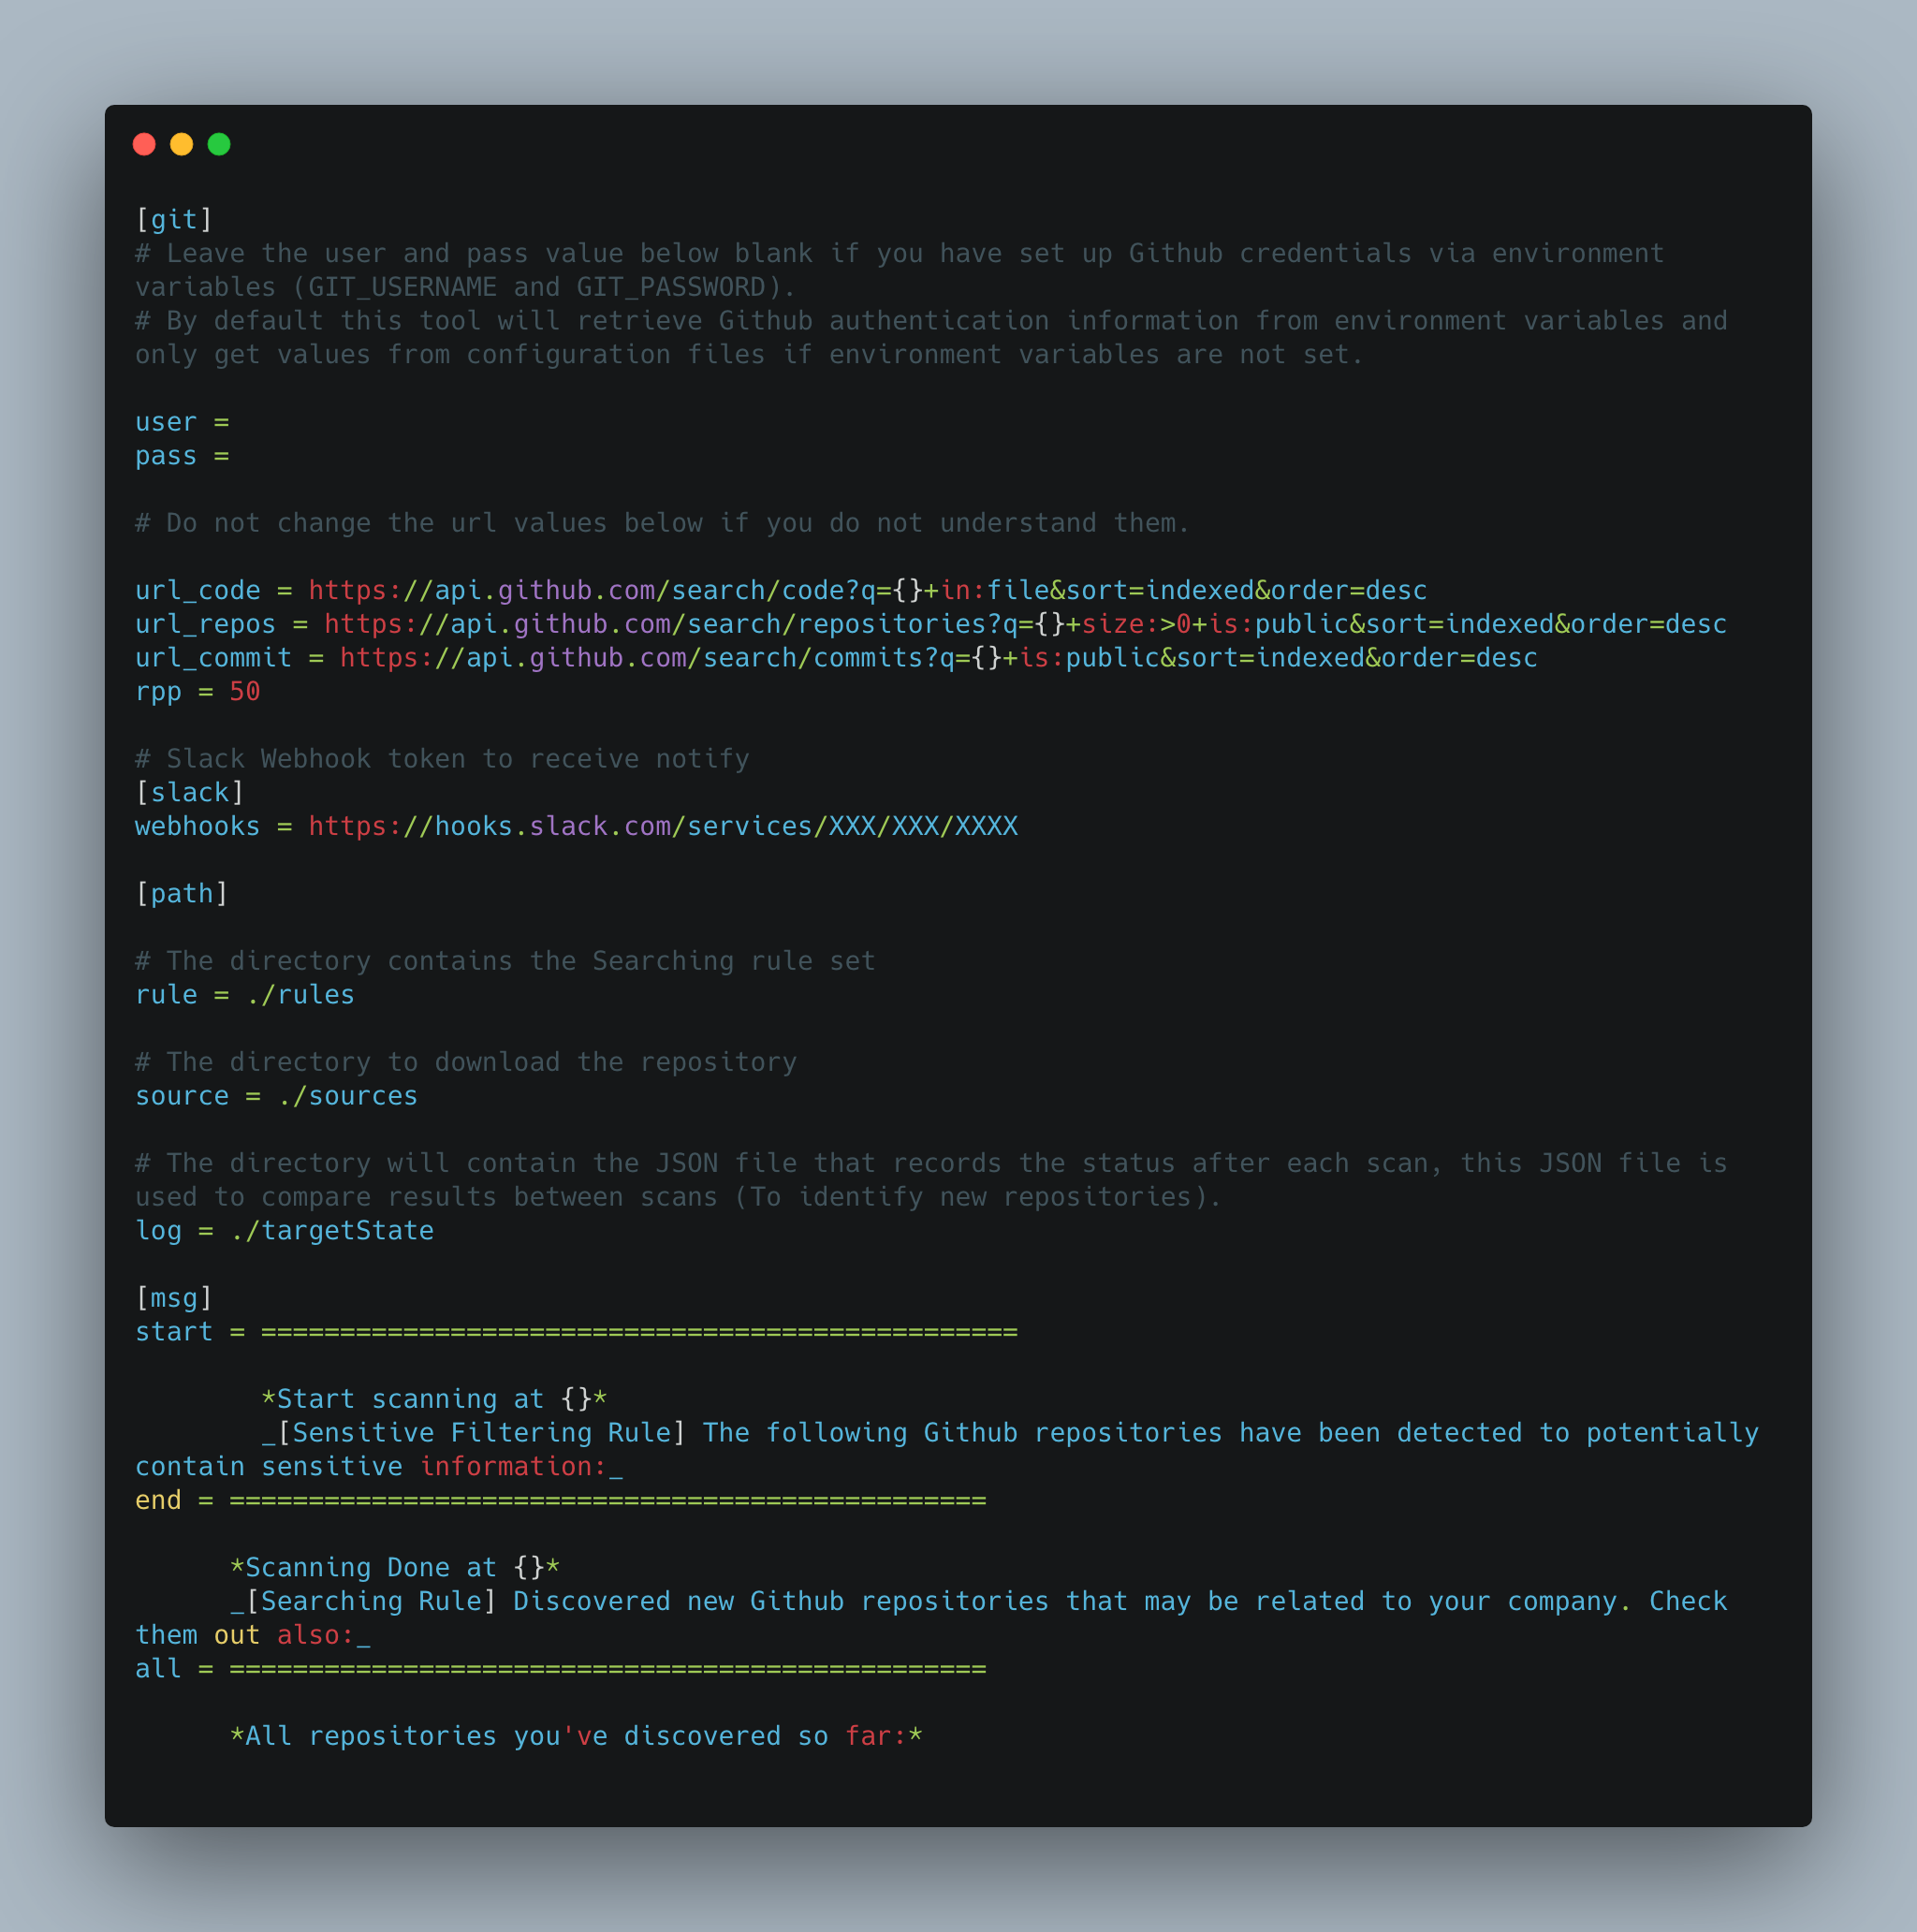 talkaboutcybersecurity/gitmonitor
One way to continuously monitor sensitive information that could be exposed on Github
 rk-000/pixel-flood-attack
PoC for CVE-2024-22393: Pixel Flood DoS in Apache Answer ≤1.2.1. Upload crafted 5KB image with fake 64Kx64K dimensions. Server allocates memory for…
 assetnote/php2shell-scanner
High fidelity scanner for php2shell (CVE-2026-109618 and CVE-2026-109619)
 jinparkmida/cve-2023-28771-demo
Proof-of-concept exploit for CVE-2023-28771, demonstrating a critical vulnerability in Zyxel devices for security testing and validation.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 cyberisltd/egresser
Client/server scripts designed to test outbound (egress) firewall rules.
 keraattin/cve-2026-39842
Critical remote code execution vulnerability in OpenRemote's Rules Engine allows authenticated users with `write:rules` role to execute arbitrary…
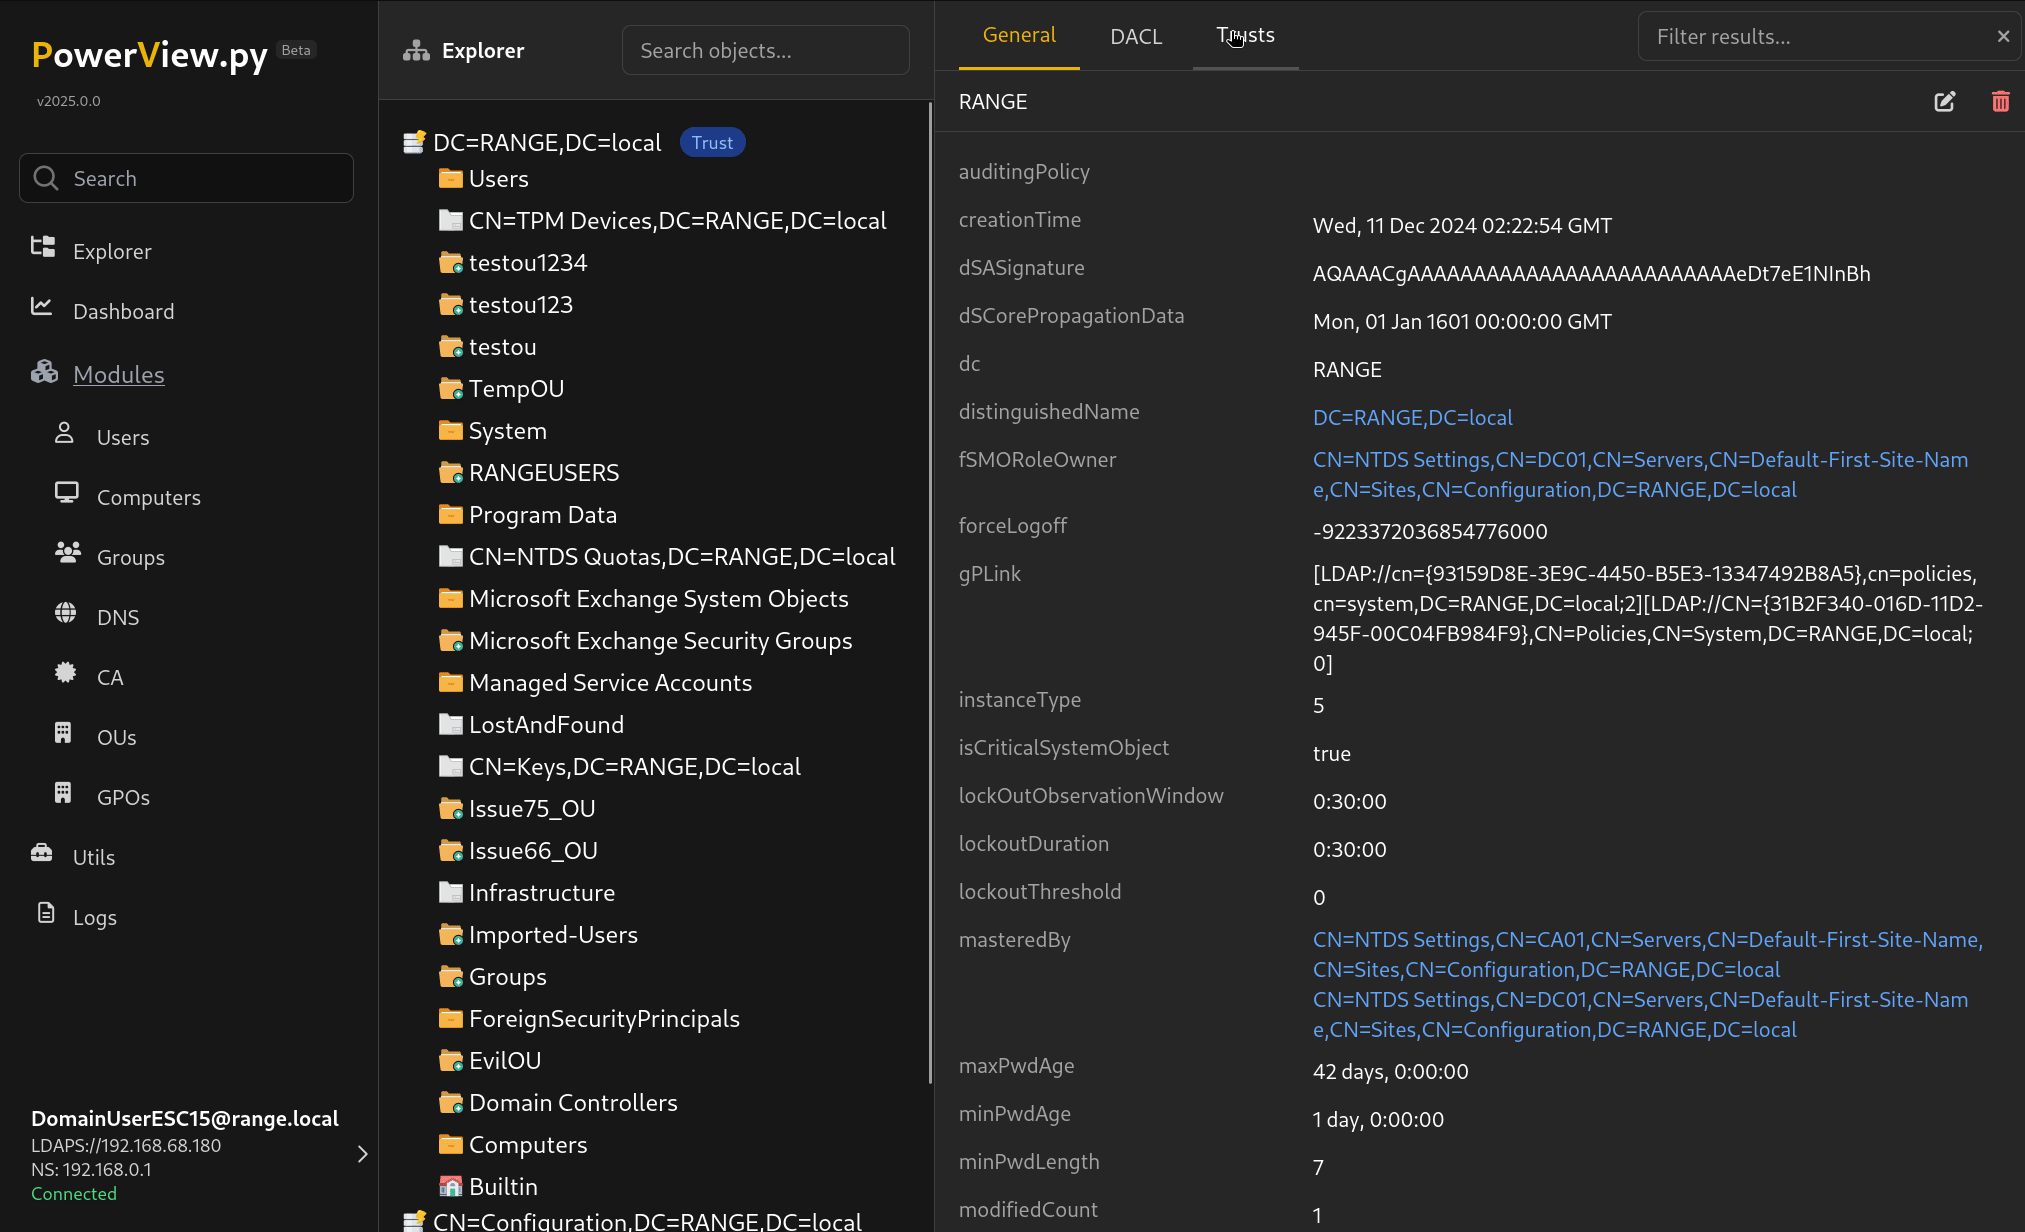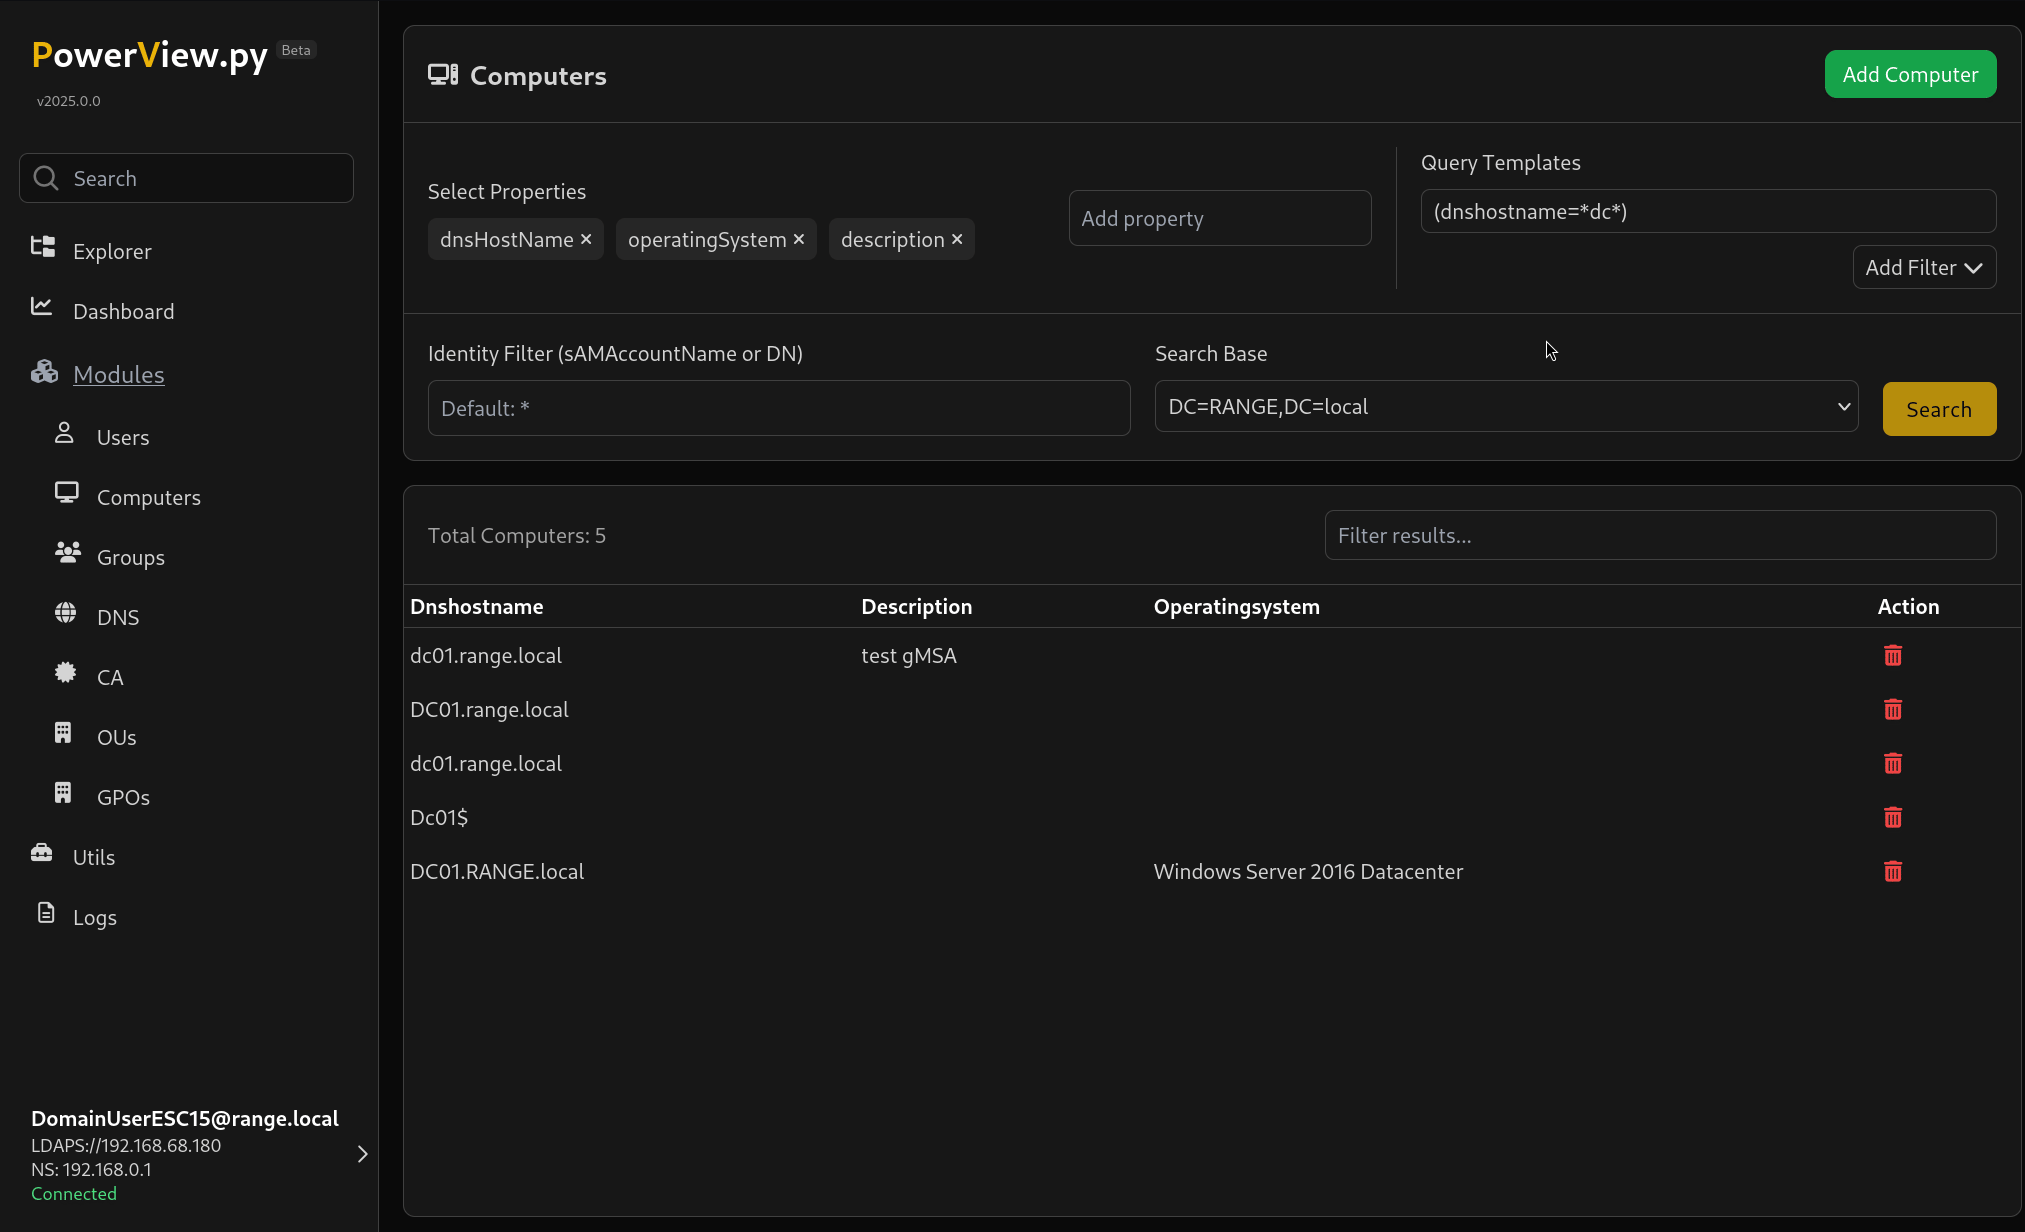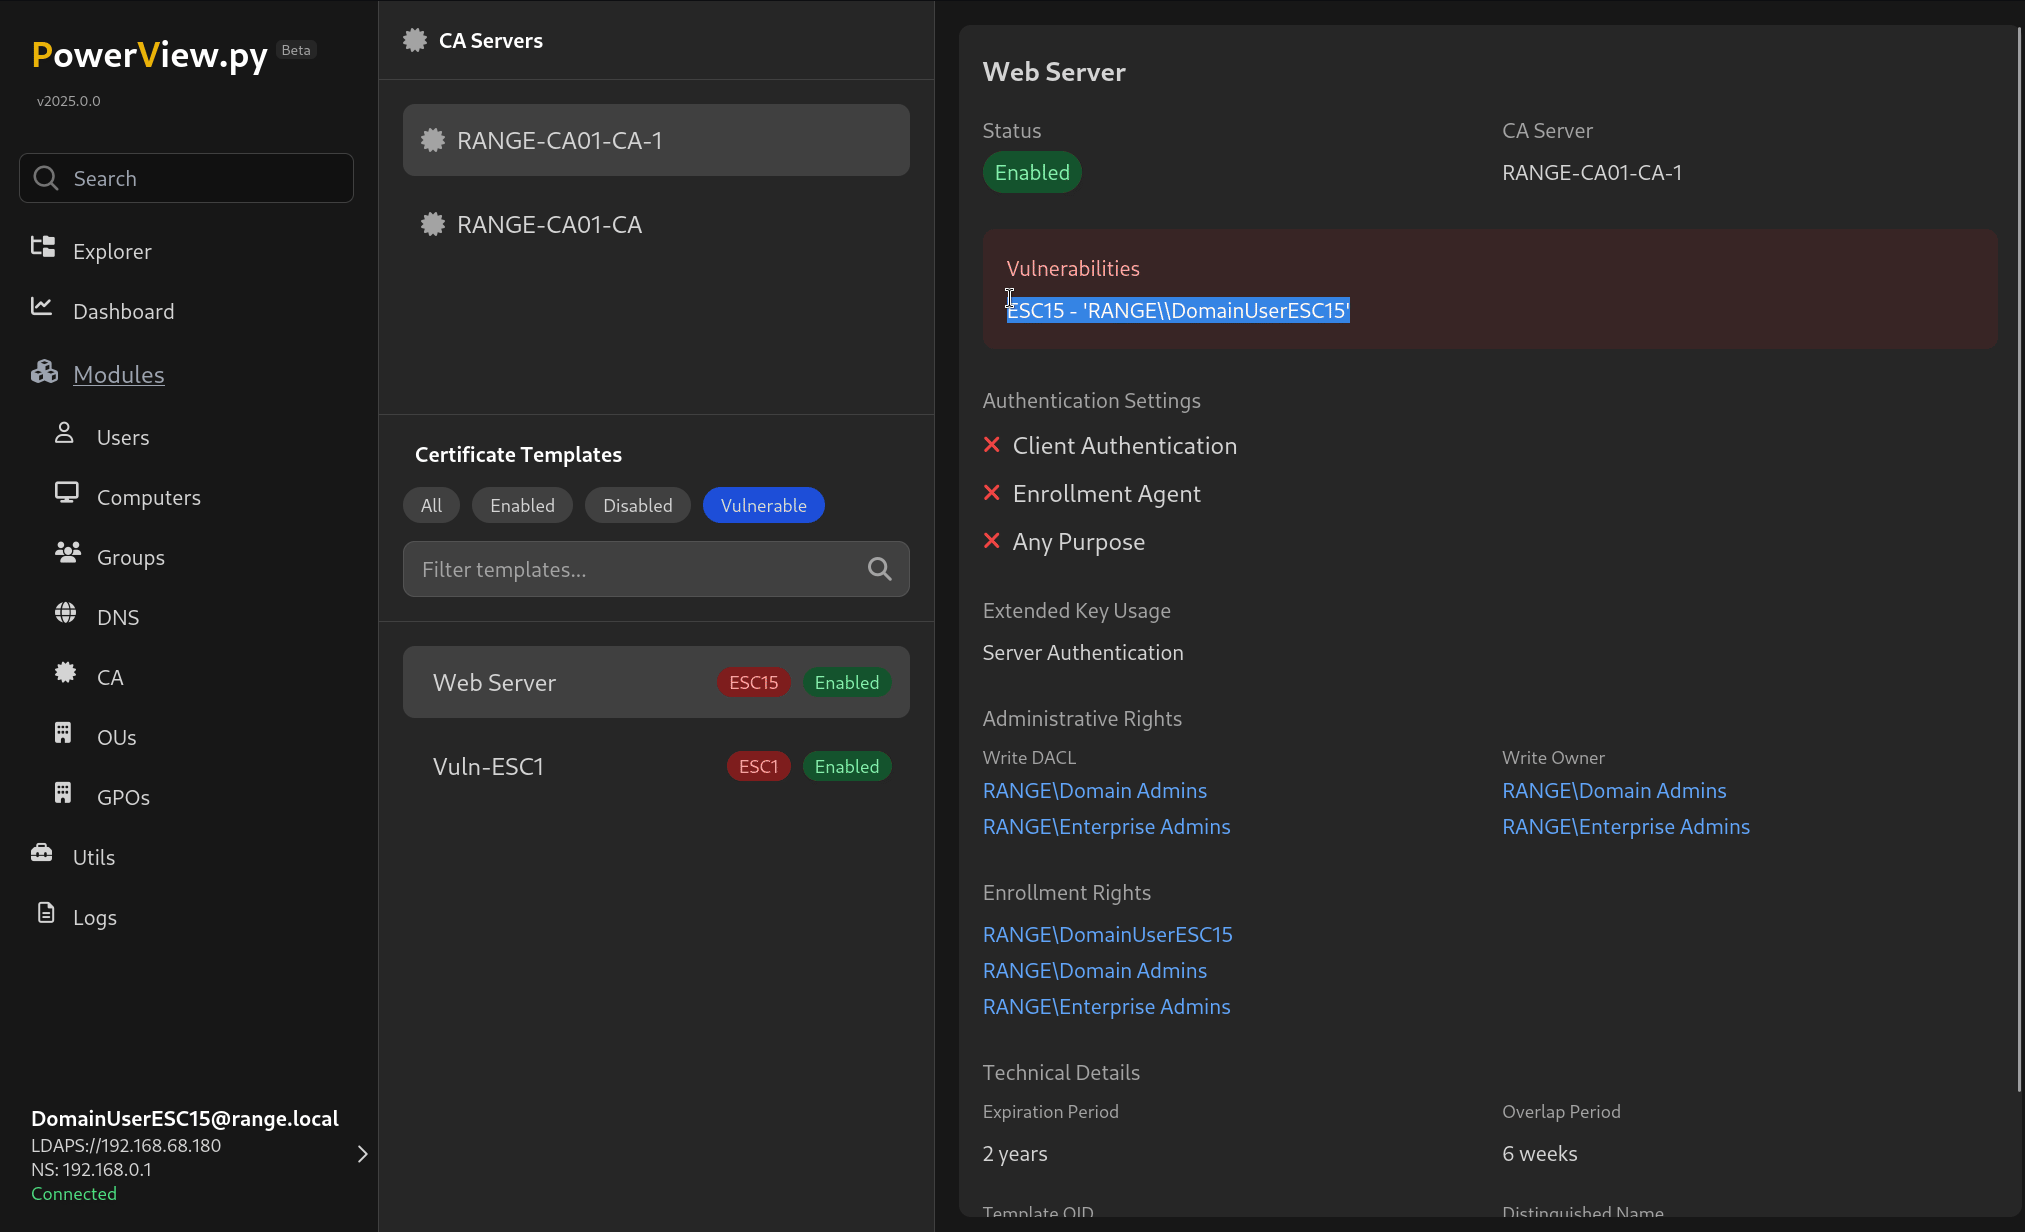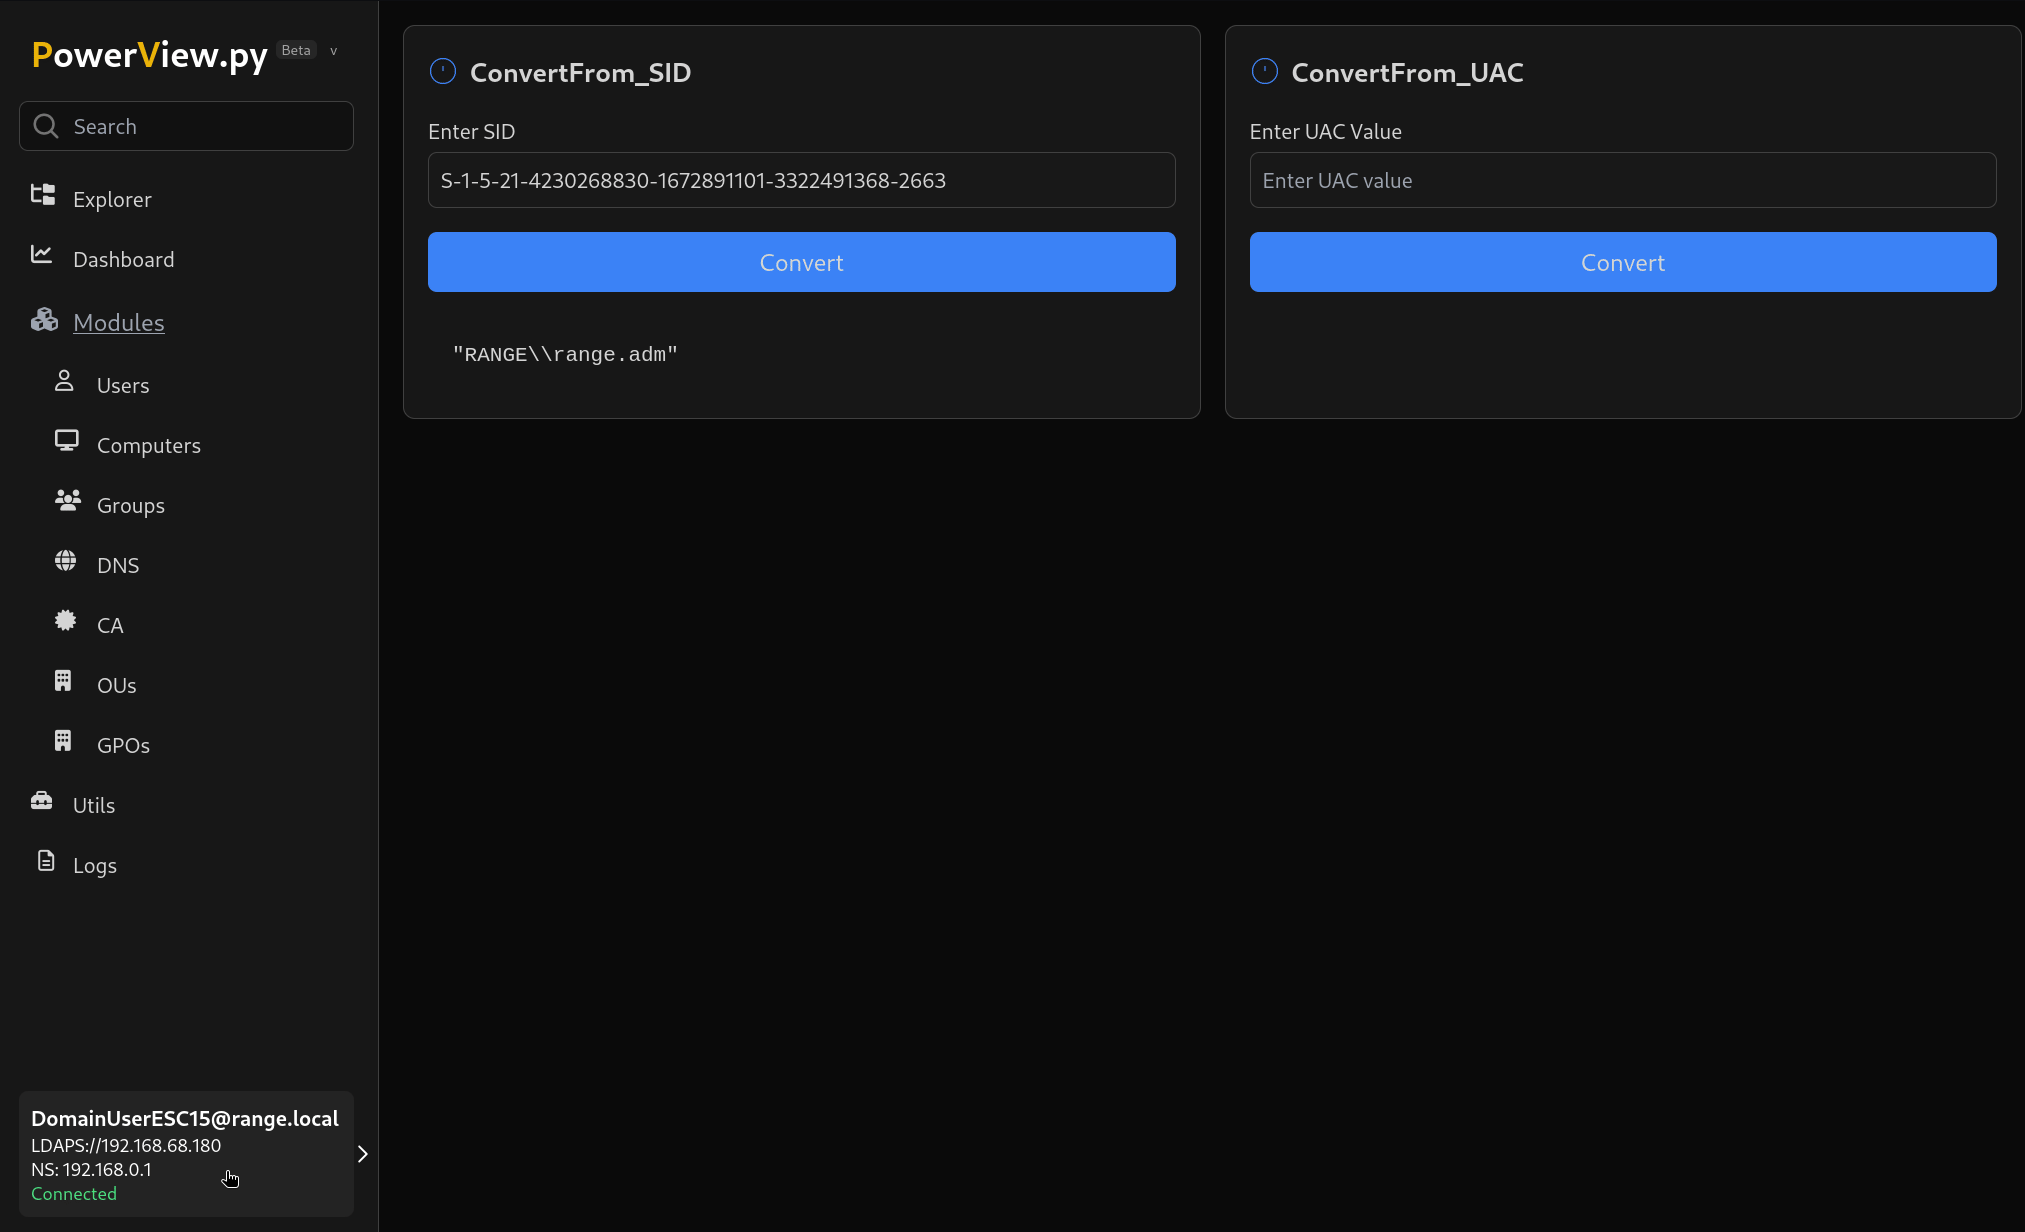 aniqfakhrul/powerview.py
Powerview on steroids
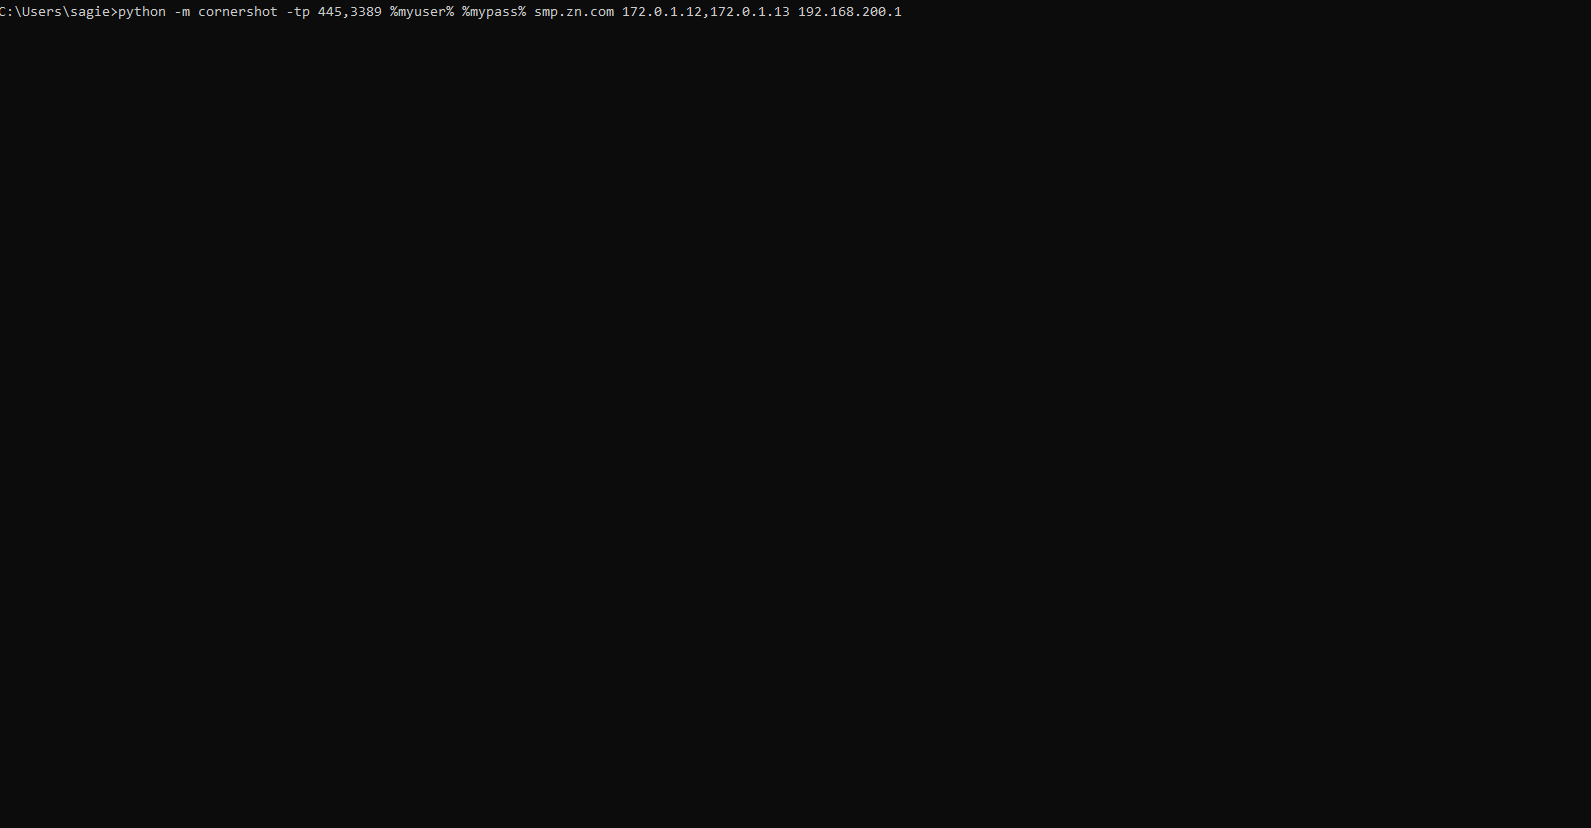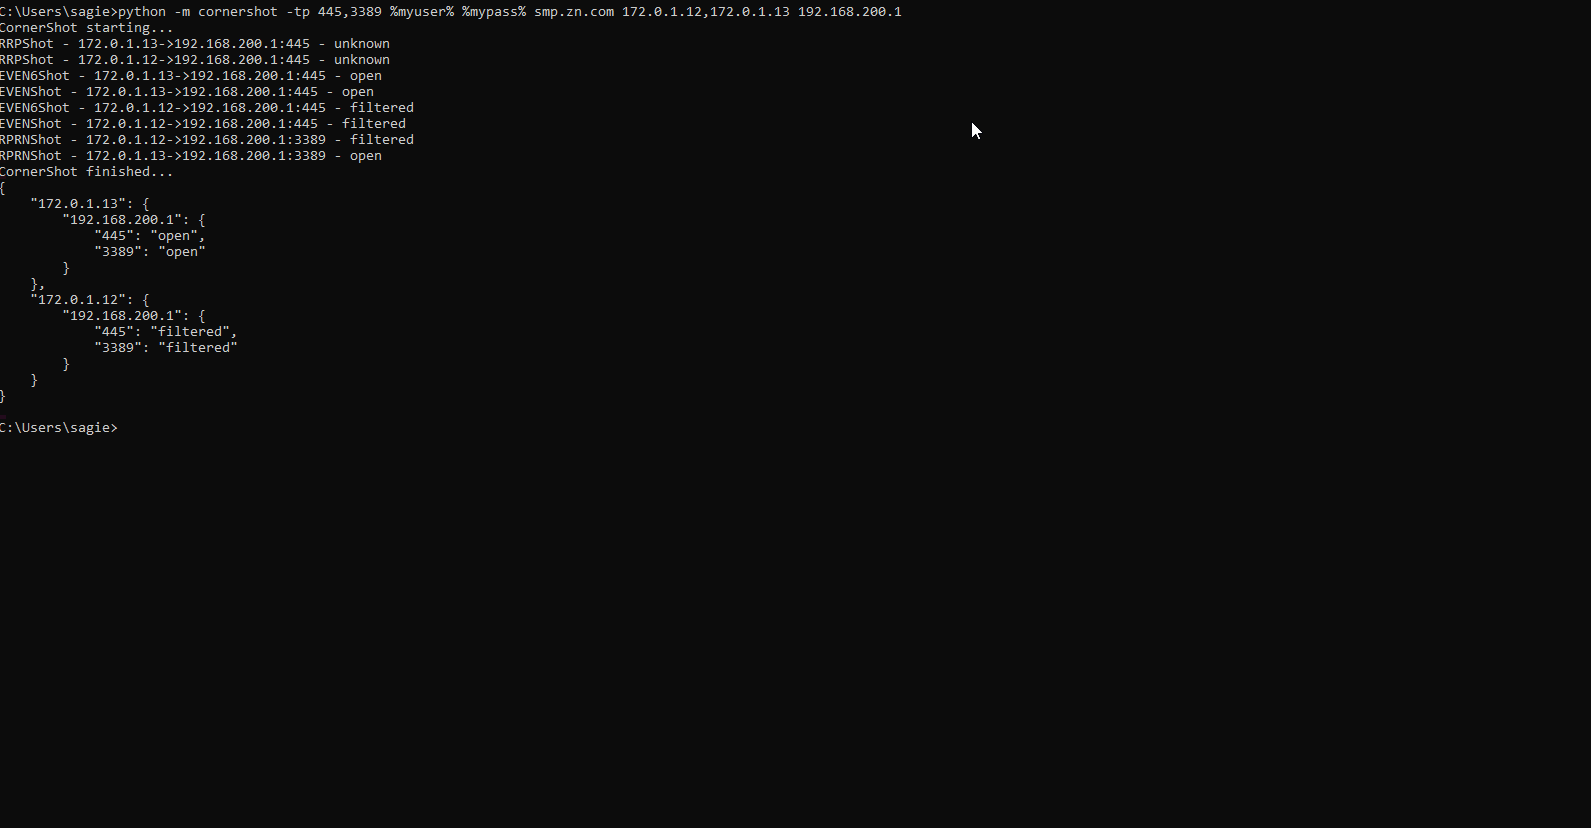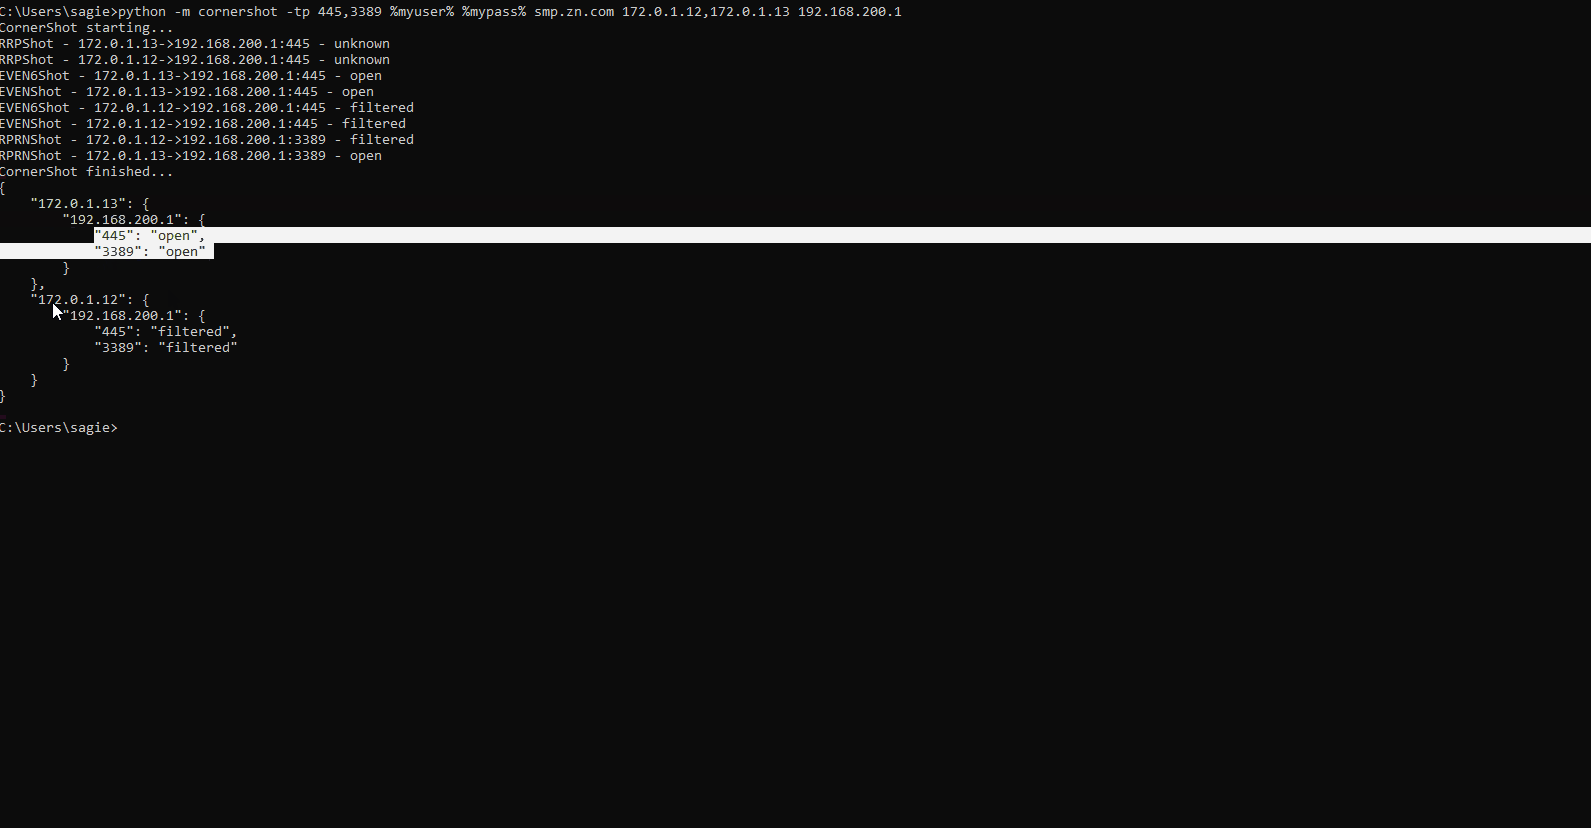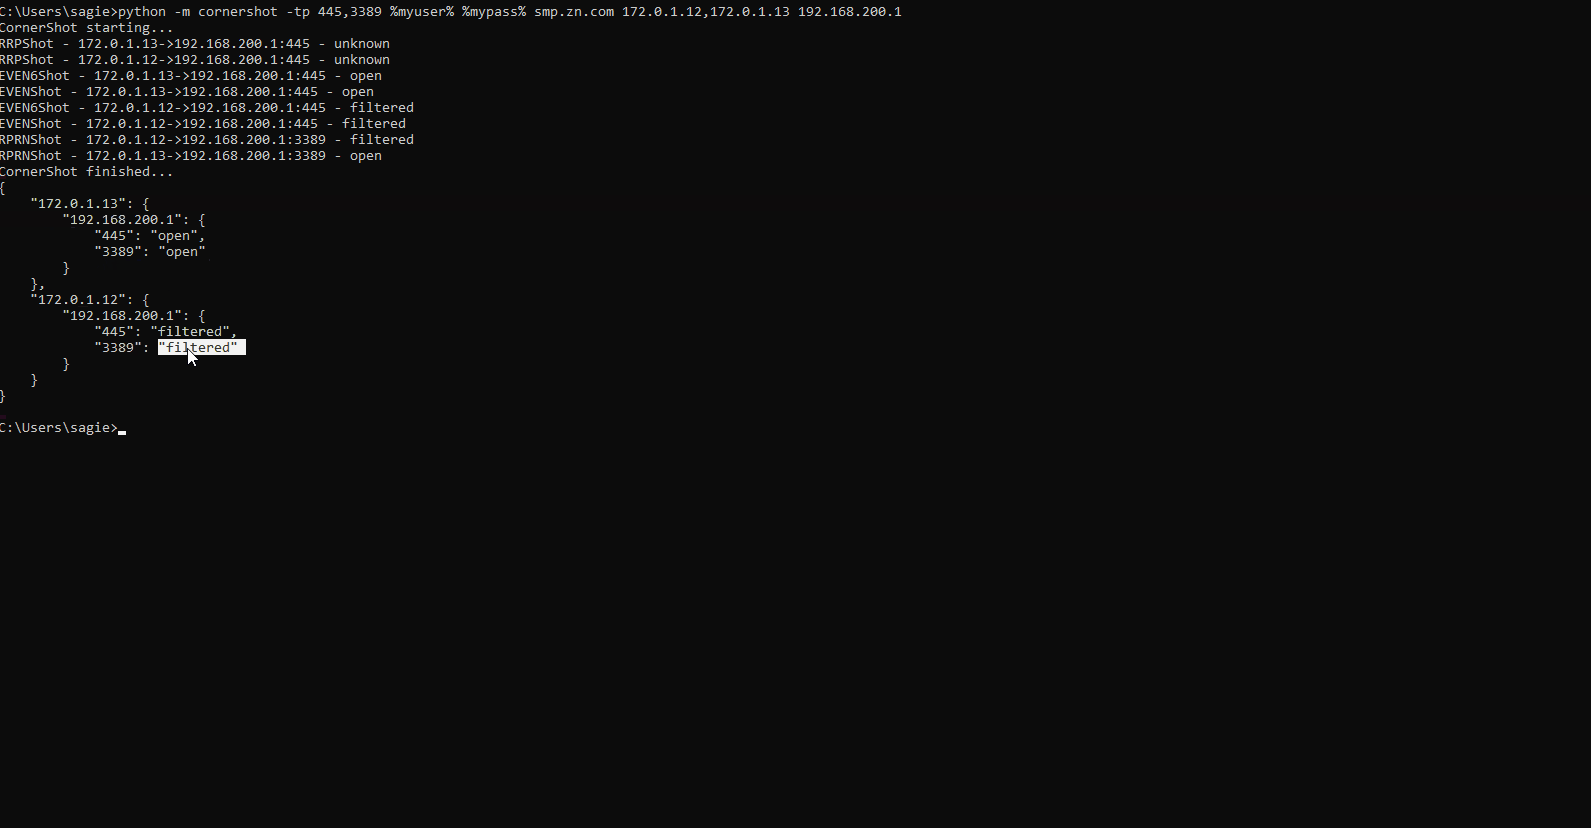 zeronetworks/cornershot
Amplify network visibility from multiple POV of other hosts