
PressVector
 vulnquest58/pressvector
PressVector - Advanced WordPress Vulnerability Scanner CVE-2026-63030 (REST batch route confusion) / CVE-2026-60137 (SQLi) Developer: Vulnquest
information-gatheringpenetration-testingreconnaissance+3
1
vulnquest58/pressvectorPressVector - Advanced WordPress Vulnerability Scanner CVE-2026-63030 (REST batch route confusion) / CVE-2026-60137 (SQLi) Developer: Vulnquest
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
 raghu66669999/wordpress-snapcreek
snapcreek_duplicator file read vulnerability https://www.cvedetails.com/cve/CVE-2020-11738/
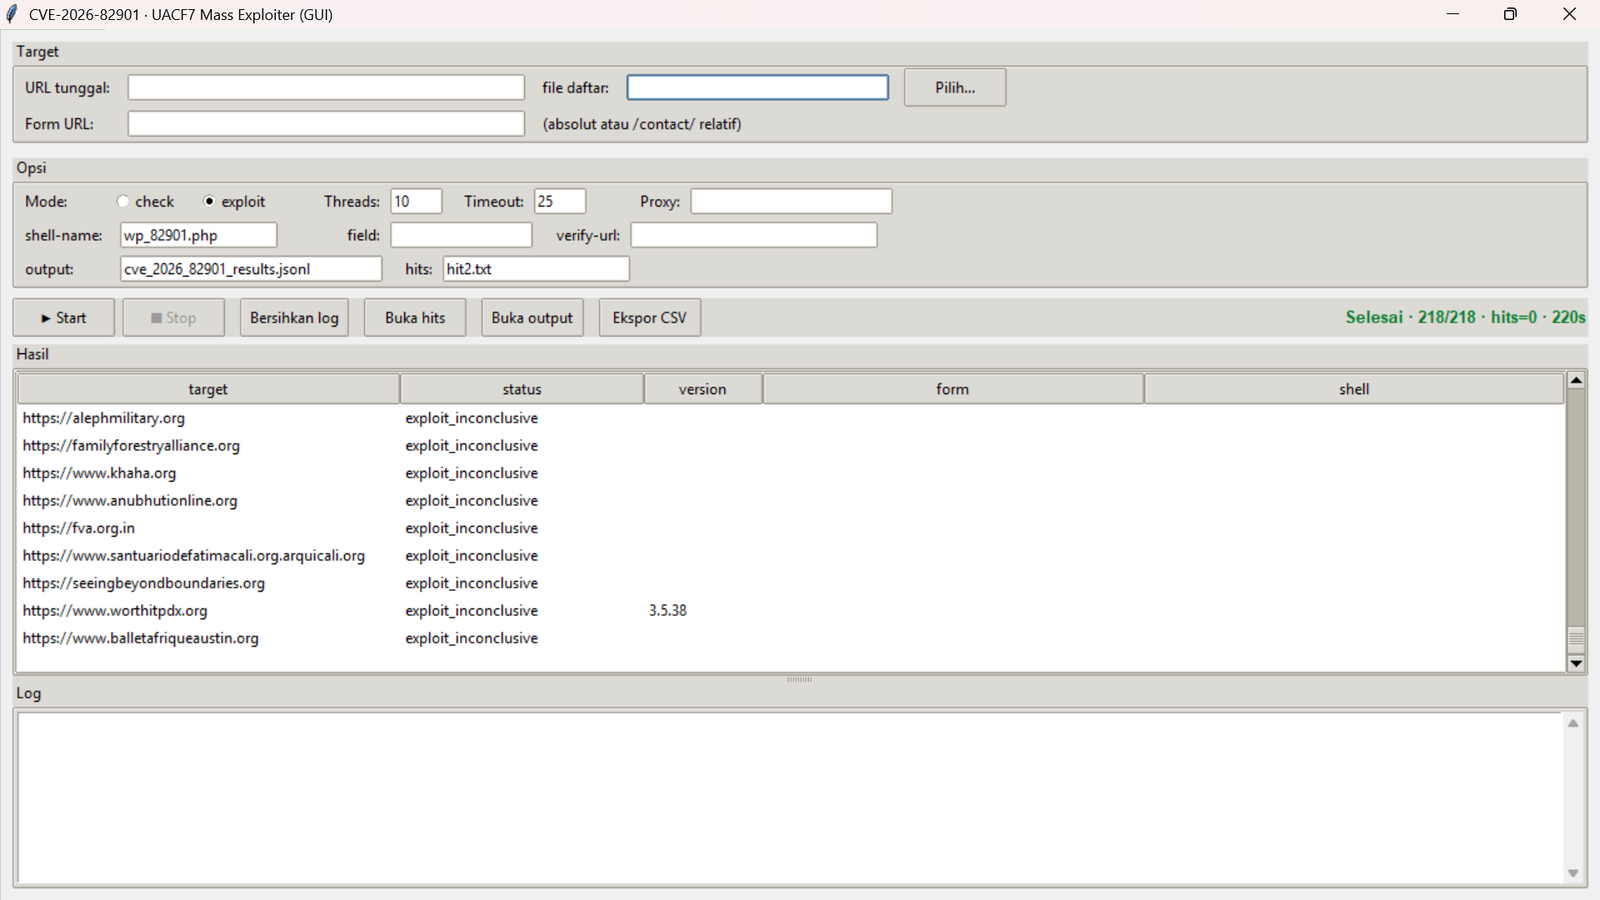 tonydelouvre/cve-2026-82901
GUI and CLI mass scanner and exploiter for CVE-2026-82901, an unauthenticated arbitrary file upload in the Ultra Addons for Contact Form 7 WordPress…
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 dzmind2312/mass-cve-2026-23550-exploit
Multi-threaded Python scanner for CVE-2026-23550, detecting unauthenticated admin takeover in WordPress Modular DS plugin with full wp-admin…
 dzmind2312/cve-2024-34444-exploit-poc
Multi-threaded mass scanner for CVE-2024-34444 (Missing Authorization) in Slider Revolution WordPress plugin. Automates nonce extraction, version…
 tuhinshubhra/wpintel
Chrome extension designed for WordPress Vulnerability Scanning and information gathering!
 bhanunamikaze/wp2shell-cve-2026-63030-poc
PoC detector & safe validator for the WP2Shell WordPress vulnerability chain: CVE-2026-63030 (REST batch-route confusion) + CVE-2026-60137…
 reneoliveirajr/wp_cve-2020-35489_checker
WordPress Sites Vulnerability Checker for CVE-2020-35489 - "Educational Use Only"
 rhbb/cve-2019-17671
Proof-of-concept exploit for CVE-2019-17671, a WordPress plugin vulnerability exploitable via crafted URL parameters to achieve unauthorized data…
 kernel364/cve-2024-2876
Proof-of-concept exploit for a critical SQL injection vulnerability in WordPress Email Subscribers plugin. Includes exploitation details, HTTP…
 anggatechi/cve-2026-63030
WordPress Core Pre-Auth RCE — Batch Route Confusion + SQL Injection
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 yucaerin/cve-2025-2539
CVE-2025-2539 - WordPress File Away <= 3.9.9.0.1 - Arbitrary File Read
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 josemour8/cve-2026-93399
Python mass exploitation scanner for CVE-2026-93399 in the Bookly WordPress plugin: version detection, unauthenticated IDOR order-token enumeration,…