
CVE-2023-25157
 0x2458bughunt/cve-2023-25157
Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…
exploitationinformation-gatheringreconnaissance+2
10
0x2458bughunt/cve-2023-25157Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
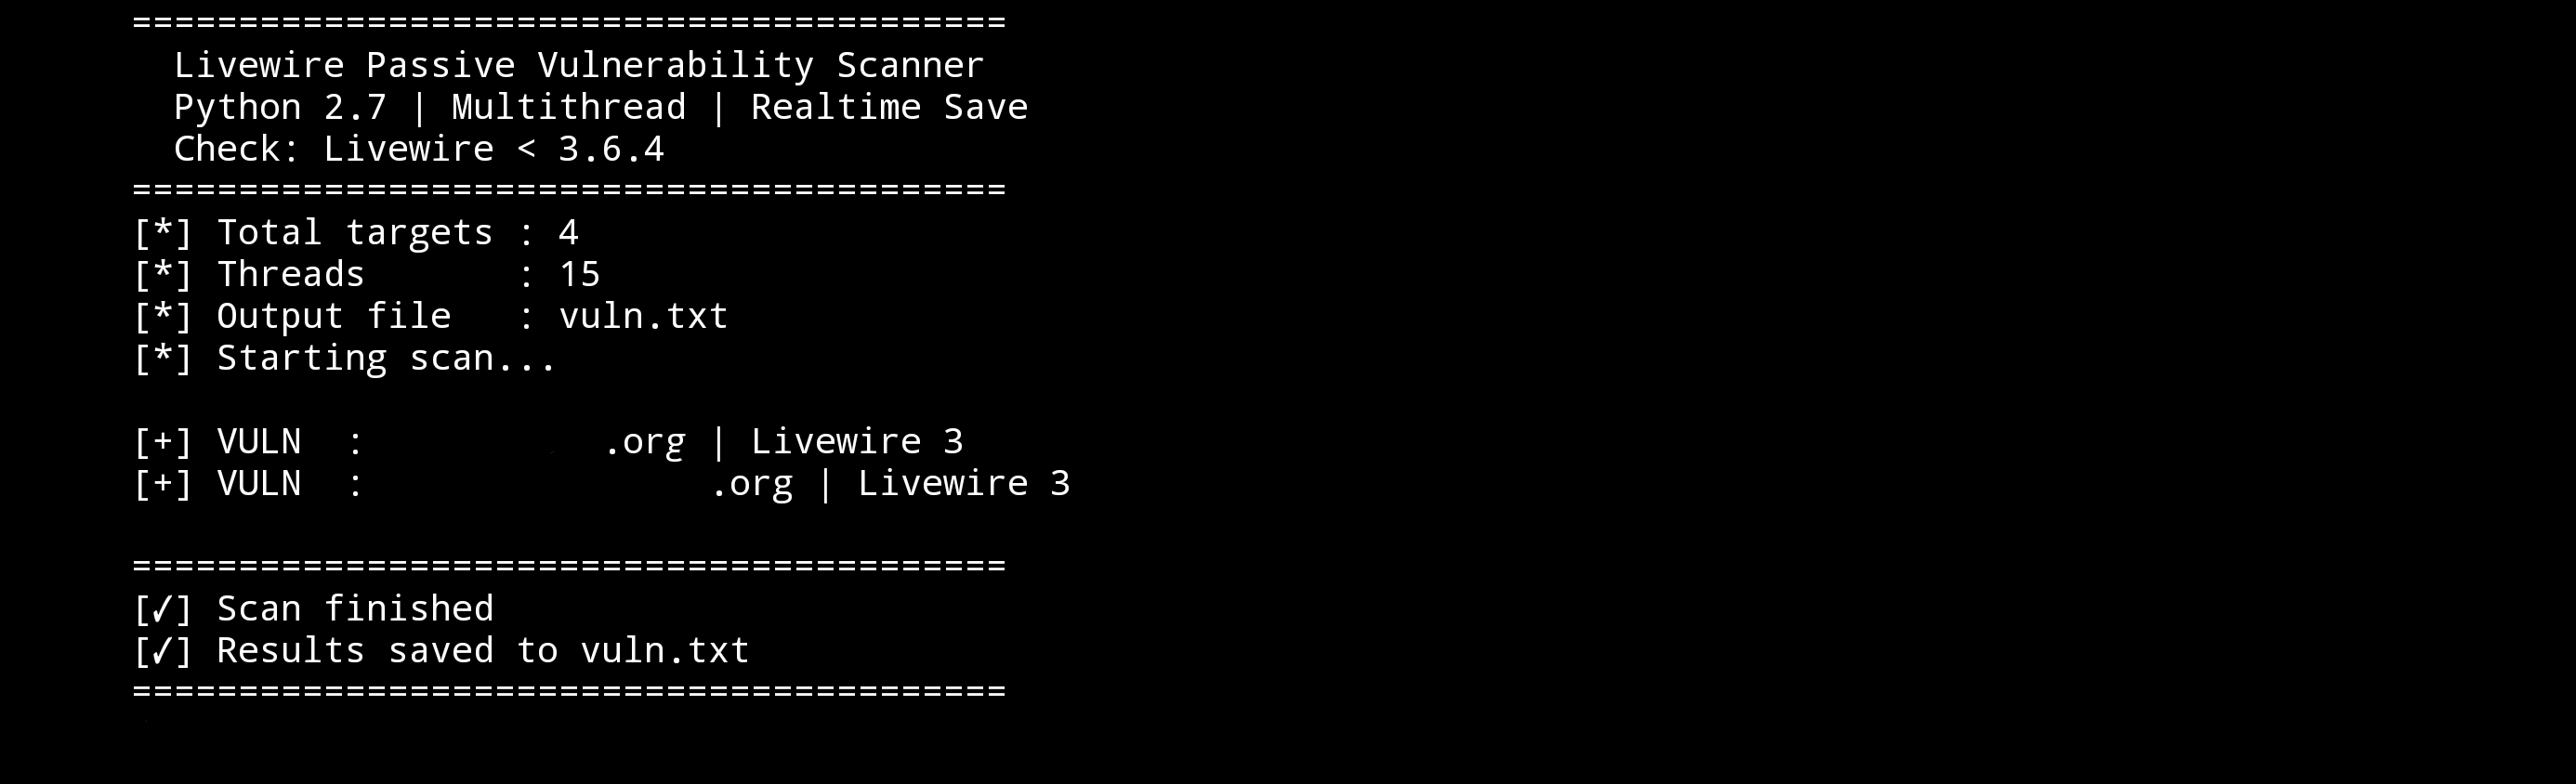 jenderal92/livewire-vuln-scanner
Simple scanner to detect vulnerable Livewire installations.
 feralthedogg/cve-2025-24132-scanner
mDNS-based AirPlay device discovery tool that scans local networks and tests for CVE-2025-24132 zero-click HTTP RCE vulnerability with a simple GUI…
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 infosec4fun/cve-2020-13158
CVE-2020-13158 - Artica Proxy before 4.30.000000 Community Edition allows Directory Traversal
 xdev05/cve-2020-3452-poc
Automates downloading and running an Nmap NSE script to scan hosts for CVE-2020-3452 vulnerability, using a list of target hosts.
 brianwrf/joomla3.7-sqli-cve-2017-8917
Joomla 3.7 SQL injection (CVE-2017-8917)
 r00tpgp/http-vuln-cve-2019-16759
Nmap NSE Script to Detect vBulletin pre-auth 5.x RCE CVE-2019-16759
 zack0x01/cve-2025-55182-advanced-scanner-
Command-line scanner for detecting and exploiting CVE-2025-55182 (React Server Components RCE) in Next.js applications. Supports custom command…
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 kal1gh0st/mylog4shell
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading
 nxploited/cve-2025-53580
WordPress Simple Business Directory Pro Plugin < 15.6.9 is vulnerable to a high priority Privilege Escalation
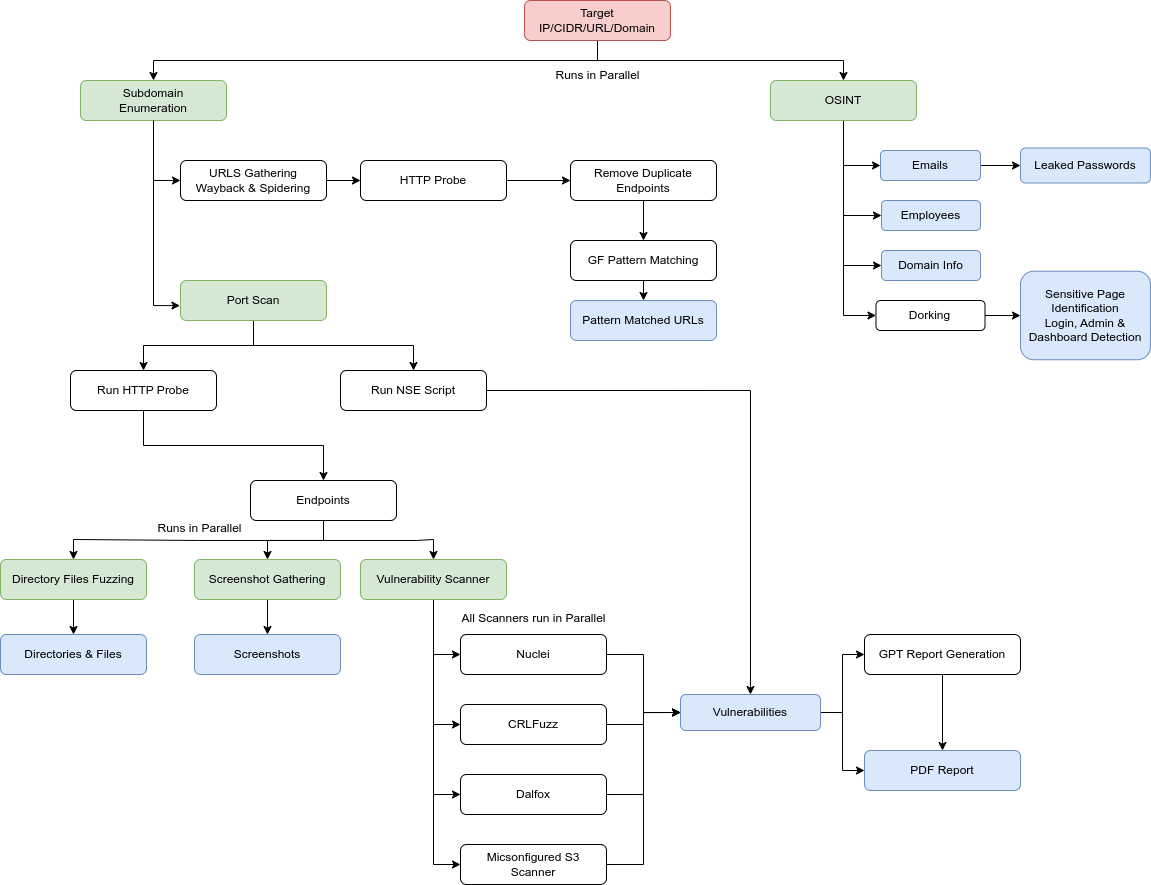 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 thecyberviking/cve-2020-5902-vuln-checker
Simple Vulnerability Checker Wrote by me "@TheCyberViking" and A fellow Researcher who wanted to be left Nameless... you know who you are you…
 asbawy/automation-for-juniper-cve-2023-36845
Simple Automation script for juniper cve-2023-36845