

Rock-ON
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
crawlerdns-subdomain-enumerationinformation-gathering+5
290
silverpoision/rock-onRock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 fricciolosa-red-team/evildork
Automated Google dorking tool for extracting leaked secrets, personal information, and subdomains from a target domain or individual, outputting…
 makefu/dnsmap
fork of http://code.google.com/p/dnsmap/source/checkout
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 viralmaniar/smwyg-show-me-what-you-got
This tool allows you to perform OSINT and reconnaissance on an organisation or an individual. It allows one to search 1.4 Billion clear text…
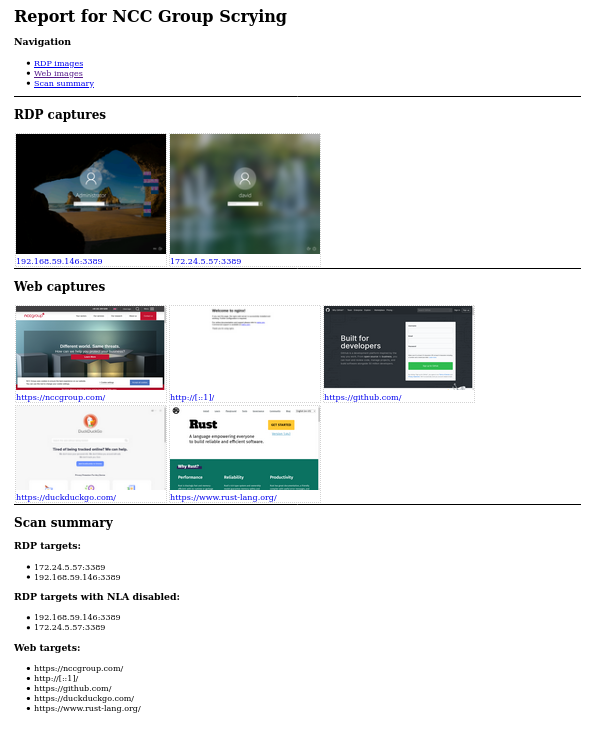 nccgroup/scrying
A tool for collecting RDP, web and VNC screenshots all in one place
 talkaboutcybersecurity/gitmonitor
One way to continuously monitor sensitive information that could be exposed on Github
 jenderal92/reverse-ip-new-api
This tool is used to perform reverse IP lookups— searching for all domains hosted on one IP address.
 thoughtfuldev/eagleeye
Stalk your Friends. Find their Instagram, FB and Twitter Profiles using Image Recognition and Reverse Image Search.
 s0md3v/parth
Heuristic Vulnerable Parameter Scanner
 raikia/smbcrunch
3 tools that work together to simplify reconaissance of Windows File Shares
 molly/gh-dork
Automated GitHub dorking tool that searches user, organization, and repository code for exposed secrets, credentials, and security misconfigurations…
 p0dalirius/rdwatool
A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application
 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.