
Rabbit Hole
 hostile.node/rabbithole
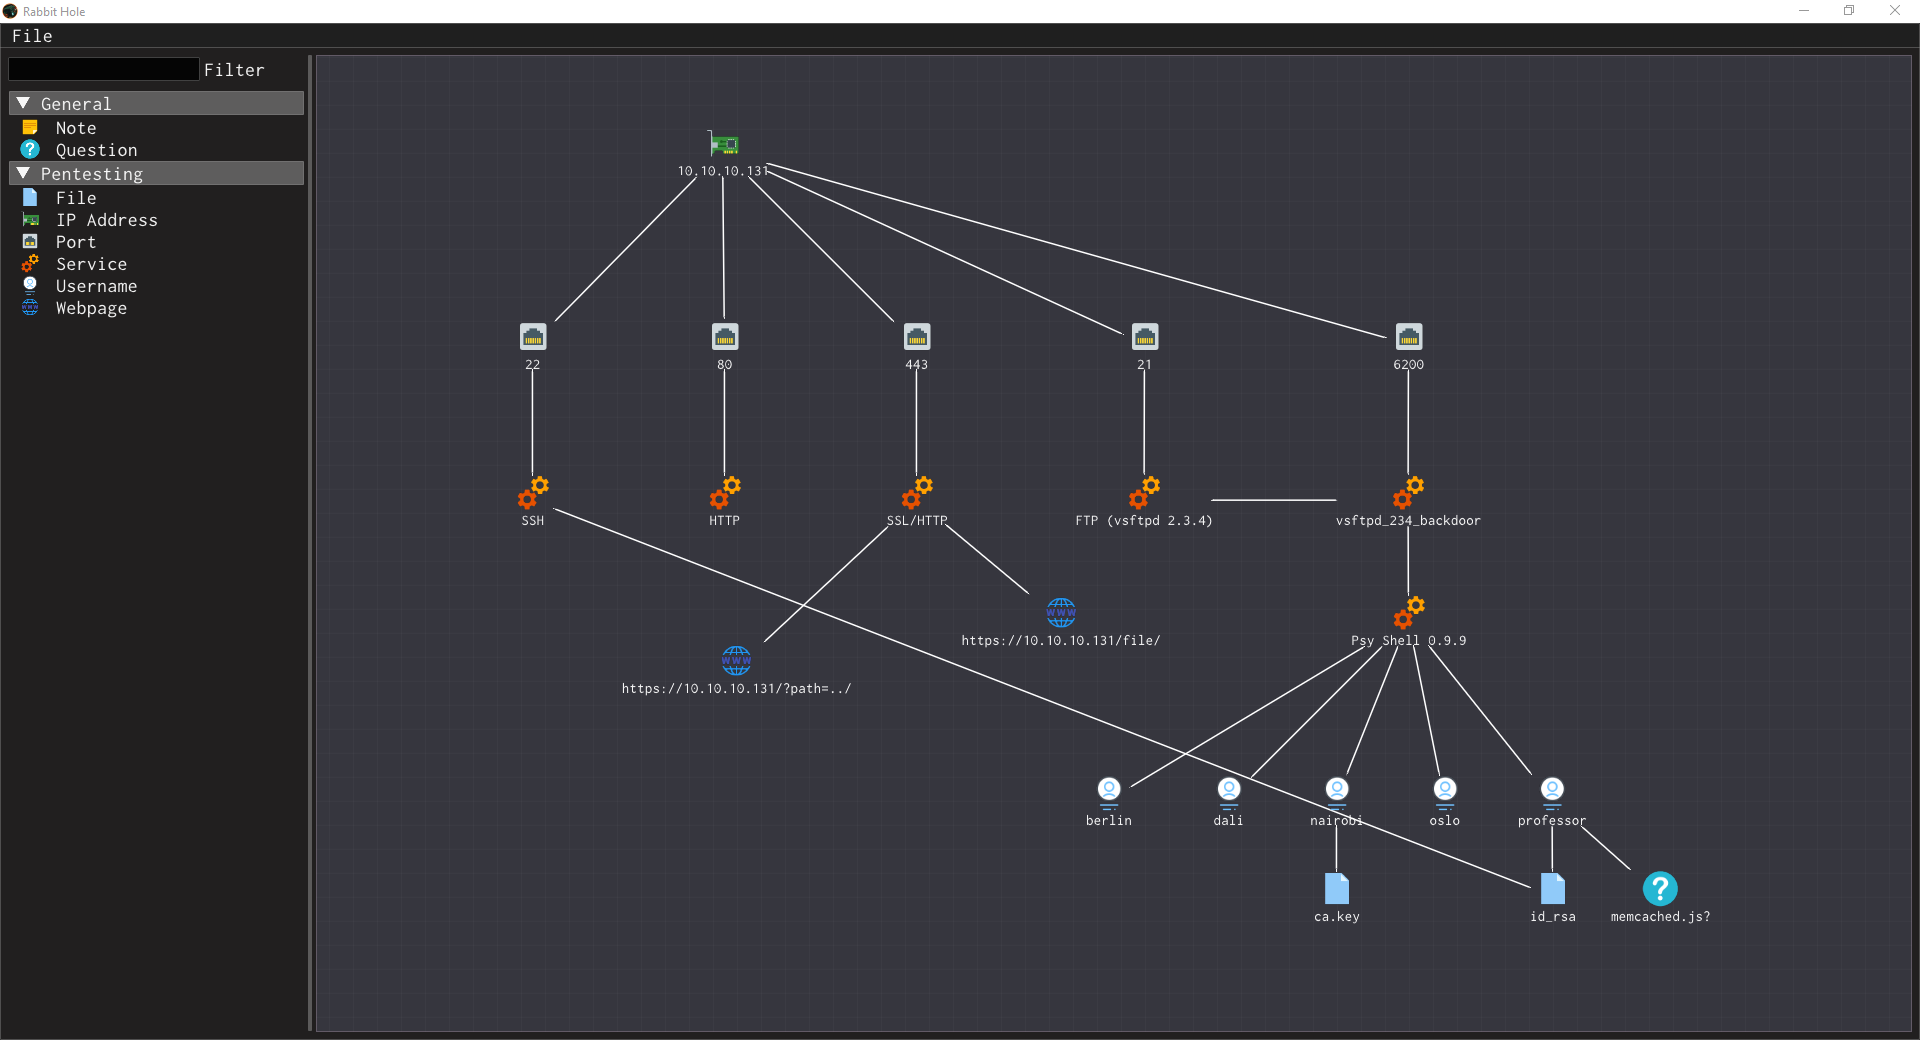
Lightweight graph-based tool for organizing penetration testing data into visual node-link diagrams of IPs, ports, services, and findings, inspired…
information-gatheringpenetration-testingreconnaissance
hostile.node/rabbitholeLightweight graph-based tool for organizing penetration testing data into visual node-link diagrams of IPs, ports, services, and findings, inspired…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 powershellempire/powertools
Collection of offensive PowerShell projects for reconnaissance, privilege escalation, and post-exploitation during penetration testing engagements.
 mistymntncop/cve-2025-5419
Proof-of-concept exploit for CVE-2025-5419, demonstrating a critical vulnerability with a JavaScript-based implementation for security testing and…
 shellkraft/anvil
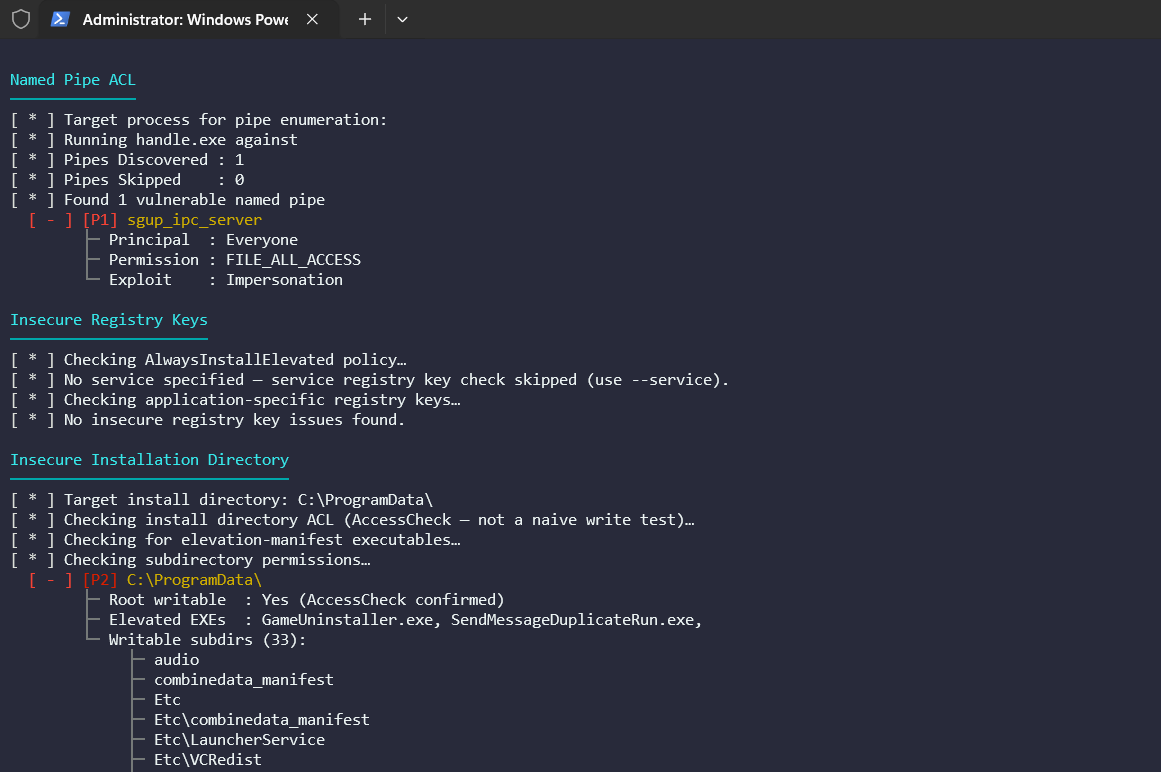
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 bigherocenter/cve-2024-7029-exploit
Exploit code for CVE-2024-7029, a web application vulnerability, providing proof-of-concept implementation for security testing and research.
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 mekoko/cve-2020-4276
Proof-of-concept exploit for CVE-2020-4276, targeting a specific vulnerability in affected software for security testing and validation.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 gibran-abdillah/cve-2023-32315
Automated exploit tool for CVE-2023-32315 authentication bypass vulnerability. Scans single or bulk targets with multiprocessing and automatic login…
 itsgiddd/cve-2023-41991
Proof-of-concept exploit for CVE-2023-41991, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 chrisbarack/cve-2025-55182
Technical penetration testing writeup demonstrating exploitation of CVE-2025-55182 in Next.js, credential harvesting from SQLite, and privilege…
 byte16384/cve-2026-49492-poc
Proof-of-concept exploit for CVE-2026-49492, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 amibhai/credential-attacks-toolkit
Complete credential attack suite for authorized security testing — SSH, FTP, Web Login, Bruteforce, Dictionary attacks
 ghxstsec/cve-2026-39987
Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…
 davidfortytwo/bluekeep
Python-based checker and exploit for BlueKeep (CVE-2019-0708) RDP vulnerability. Scans multiple IPs to identify unpatched Windows systems and enables…
 5rgj5ach5ocq5yw9/cve-2023-32315exp
Proof-of-concept exploit for CVE-2023-32315, providing a demonstration of the vulnerability for security testing.
 iknowjason/spb
Scripts for testing Shortest Path Bridging (SPB-Mac) vulnerabilities, including CVE-2016-2783 enumeration on Avaya VOSS Ethernet switches during…