

 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC
 nccgroup/autopwn
Specify targets and run sets of tools against them
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 nox-project/nox-framework
High-performance OSINT/CTI framework for automated identity pivoting and risk analysis across 120+ sources.
 projectdiscovery/katana
A next-generation crawling and spidering framework.
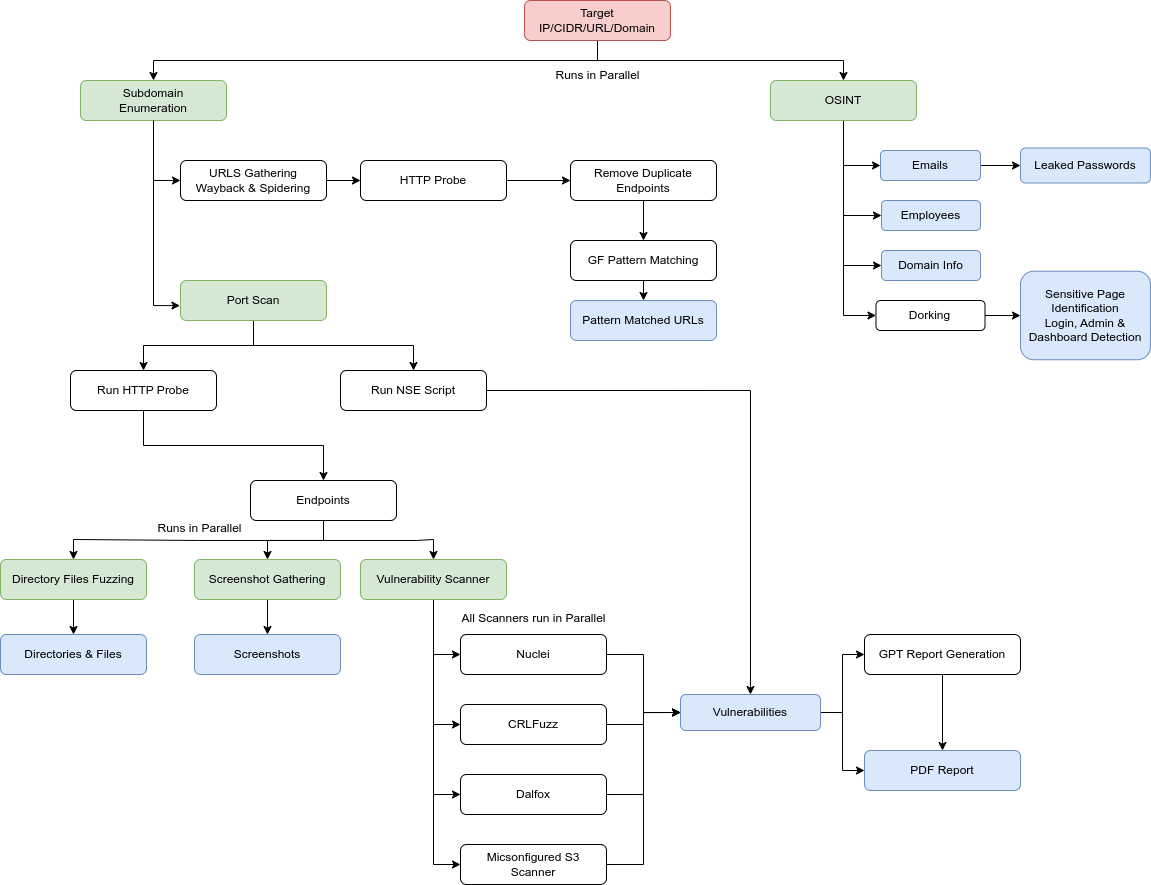 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 hausec/powerzure
PowerShell framework to assess Azure security
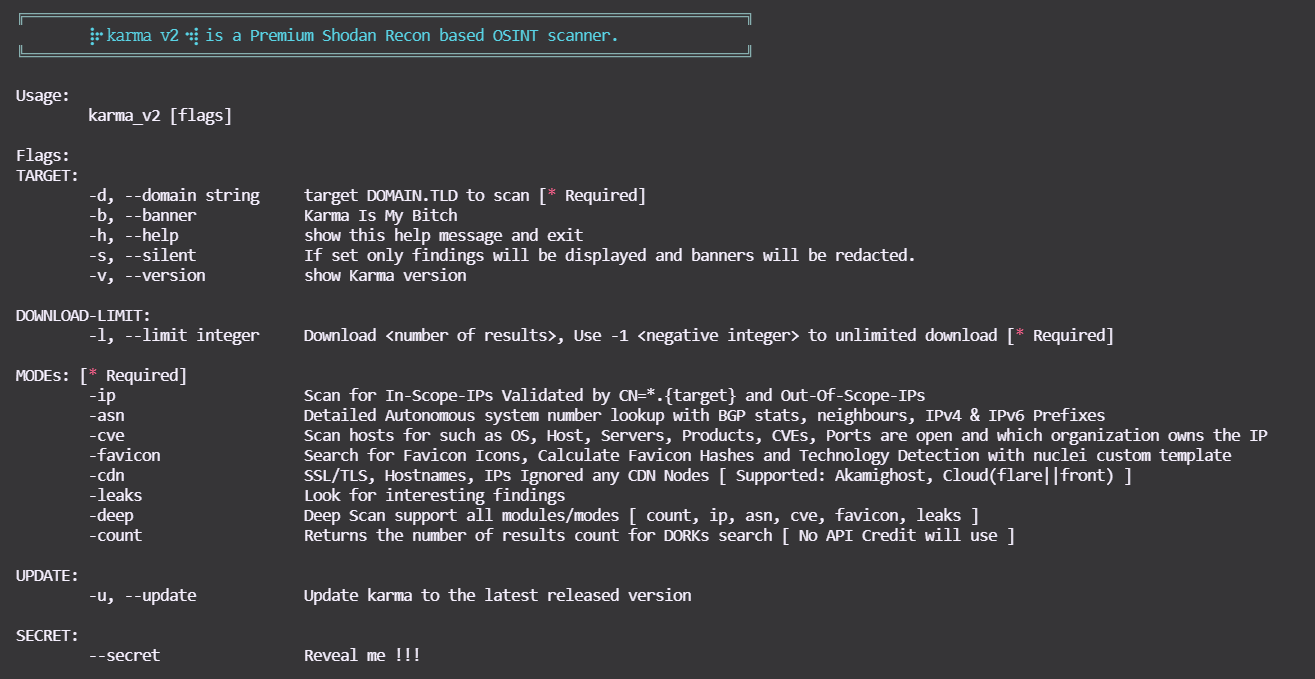 dheerajmadhukar/karma_v2
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.