
nmap-spring4shell
Nmap NSE script for detecting and exploiting Spring4Shell (CVE-2022-22965) RCE vulnerability in HTTP services with configurable payload injection and…

Nmap NSE script for detecting and exploiting Spring4Shell (CVE-2022-22965) RCE vulnerability in HTTP services with configurable payload injection and…

Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…

Self-hosted SSRF redirect, payload, callback, and DNS workbench

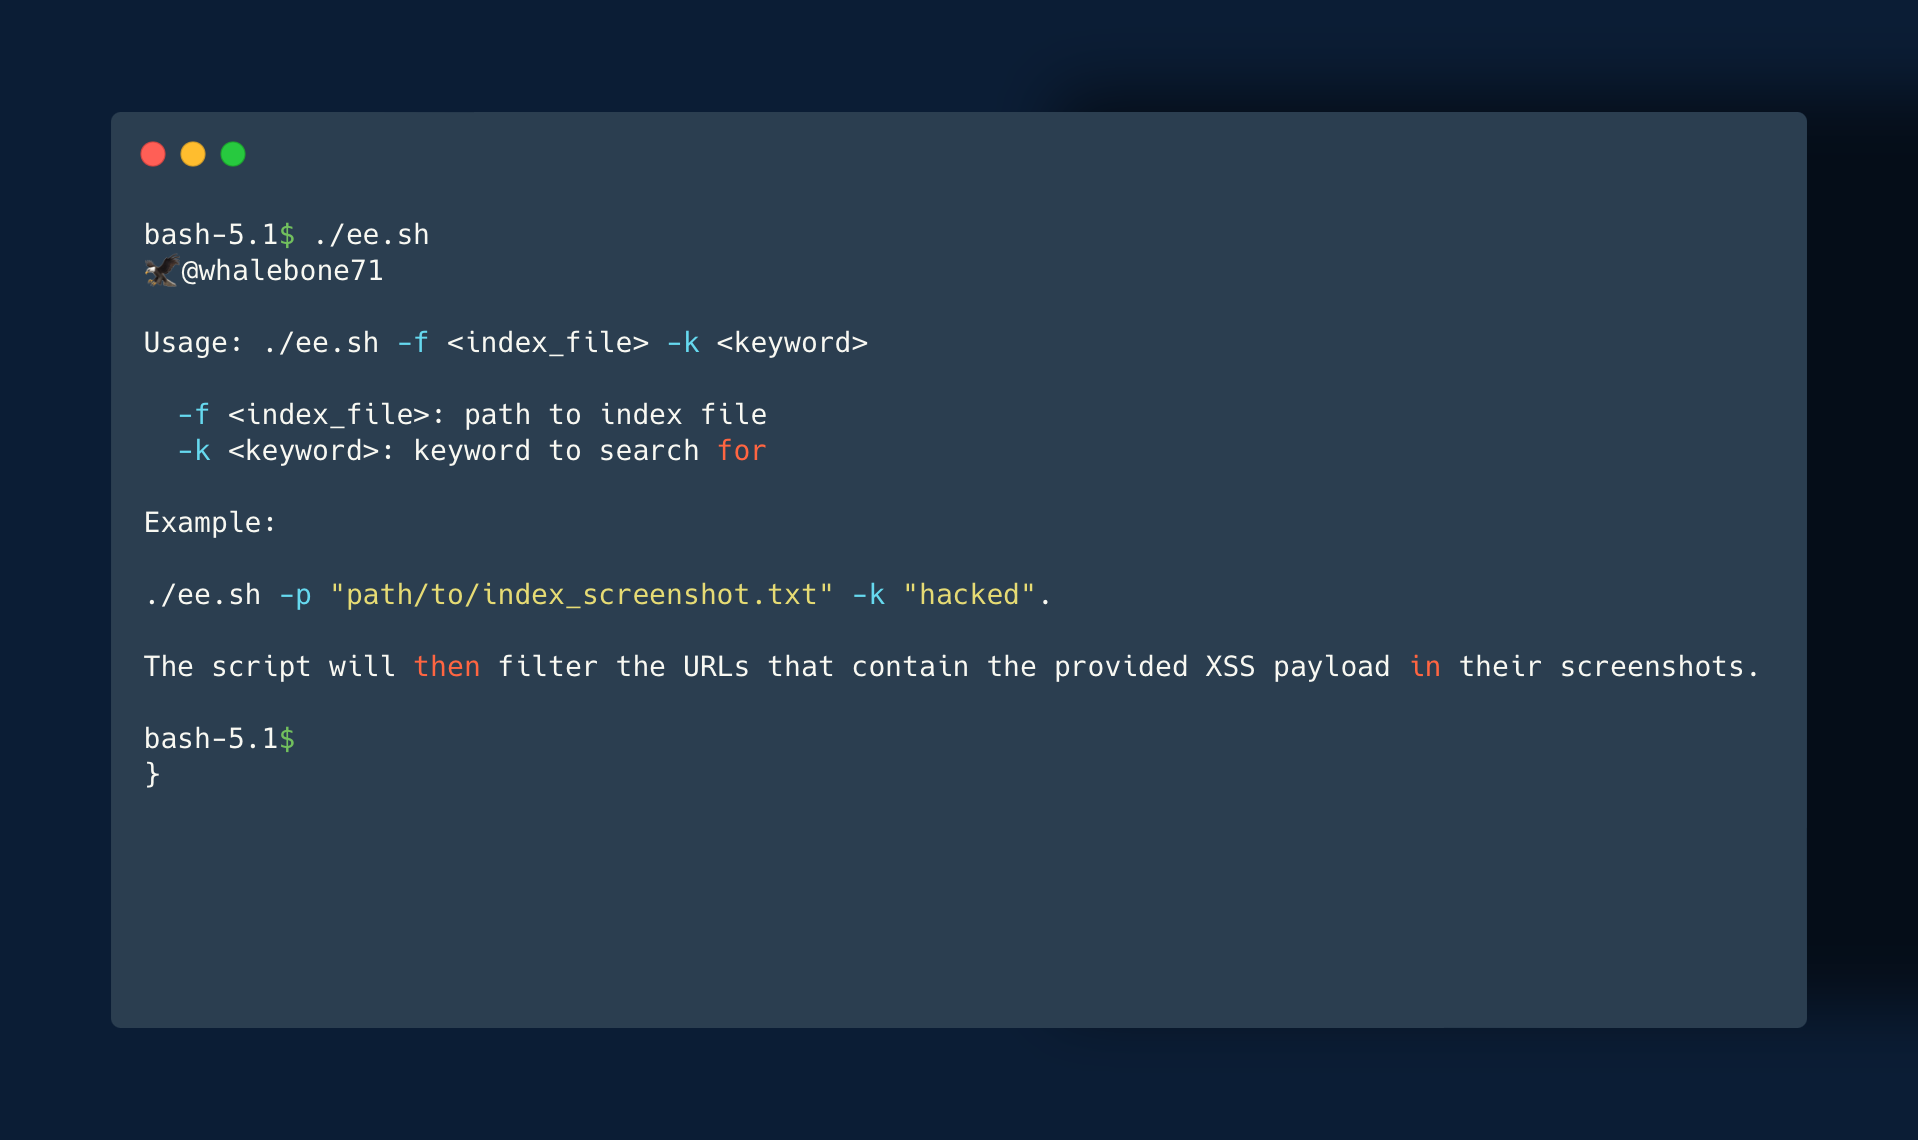
To filter the actual vulnerable URLs from the screenshots, you can use the ee.sh script. Simply run ./ee.sh -f "path/to/index_screenshot.txt" -k…

Proof-of-concept exploit toolkit for SharePoint ToolPane RCE (CVE-2025-53770) with scanner, payload analysis, and multiple exploitation methods for…

Proof-of-concept exploit for CVE-2020-28653 in ManageEngine OpManager. Detects deserialization vulnerabilities via out-of-band DNS callback using a…

Proof-of-concept exploit for CVE-2022-40881 targeting SolarView Compact devices. Uses fofa query for reconnaissance and payload delivery for…

This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…

Proof-of-concept exploit for CVE-2022-30075, demonstrating a remote code execution vulnerability in a web application. Includes Python-based payload…

Proof-of-concept exploit for CVE-2025-11627 targeting a WordPress plugin AJAX handler with nonce extraction and payload delivery for security testing.

Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…

SMBv3 vulnerability scanner for CVE-2020-0796 (SMBGhost) that checks SMB dialect 3.1.1 and compression capability via negotiate requests, with fixed…

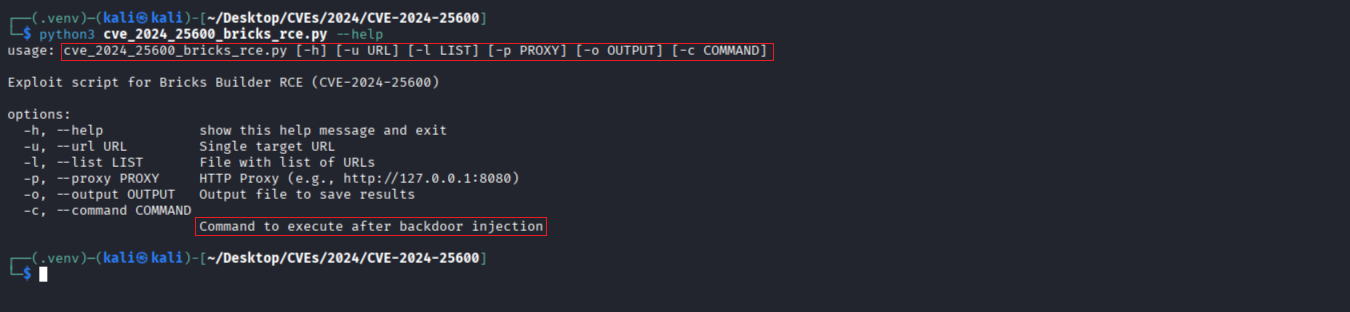
Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…

Proof-of-concept exploit for CVE-2020-24186, providing a targeted payload to demonstrate and test the vulnerability in affected systems.

Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…

Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…

Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) targeting Windows 10/Server SMBv3.1.1. Includes Nmap reconnaissance, vulnerability scanning,…

Spring Framework RCE (CVE-2022-22965) Nmap (NSE) Checker (Non-Intrusive)